
New Ransomware: LooCipher
|by Alpha Team
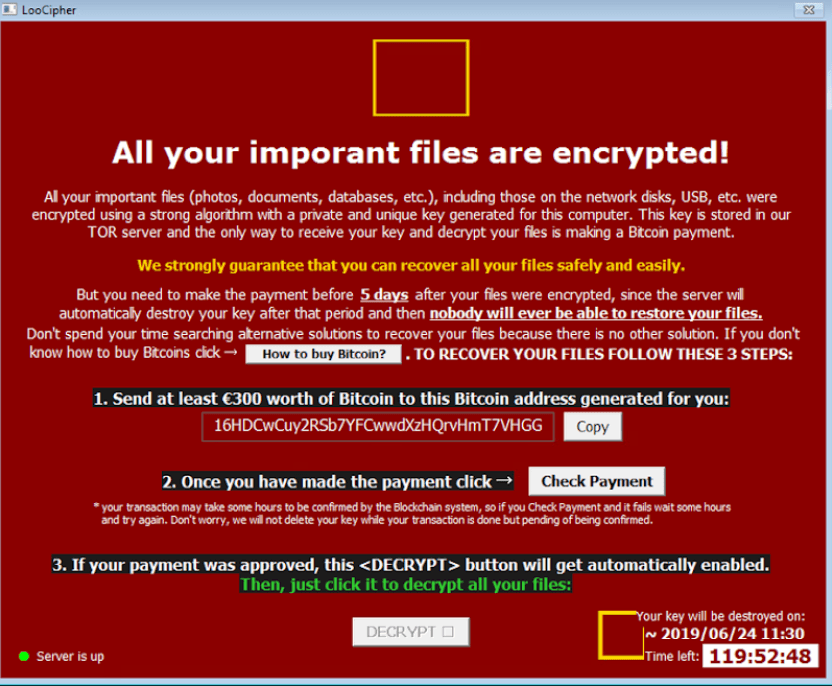
A new strain of ransomware has been discovered, and dubbed LooCipher. This ransomware has been seen to be dropped by malicious Office documents, that use macros to download the binary from an onion site. As usual, this ransomware encrypts a victim's files and demands a bitcoin payment to decrypt them.
Recommendations
- Maintain and frequently update offline backups of all critical information.
- Ensure defensive systems are updated with the latest detection.
- Consider enabling the Cyber Chatter rule in order to monitor activity related to this malware family.
Details
Researchers at Yoroi have identified a new strain of ransomware. This new malware family has been dubbed LooCipher, an allusion to Lucifer. The malicious binary responsible for encrypting a victim's files is dropped using a simplistic malicious Microsoft Office document. The document contains a single text line, requesting that the viewer enable macros to view the file. The macro embedded in these Office documents retrieves the ransomware from an onion site. The ransomware then encrypts files on a victim machine, appending the extension ".lcphr." Rather than deleting the original files as is generally the case with ransomware, this malware forces a 0-byte size and removes the contents of the file. All command and control network traffic is done using onion addresses, so the malware makes use of various services that act as proxies between the dark and clear webs. As is the norm, this ramsomware demands a payment of bitcoins to decrypt affected files.
Tags: malware, all industries, global