
Crypto Scam Potentially Targeting Retail, Media, Sports, and Government for Account Takeover
|by Alpha Team
The ZeroFOX Alpha Team has investigated a crypto-related money-flipping scam, and initial analysis indicates verified retail, media, sports, and government-related accounts, especially if Western or Japanese, may be at particular risk for Twitter account takeover as part of this scam. As of mid-November 2018, a crypto-related money-flipping scam is making the rounds on Twitter, with the attackers making use of hacked, verified accounts to solicit Bitcoin donations. The latest victims of this scam include Target and Google G Suite, whose verified accounts were taken over and used to post the Bitcoin scam on Tuesday, November 13. This scam has been ongoing since at least November 5, with possibly renewed efforts as of this week with the Target and G Suite takeovers and other account takeovers.
Details
The attackers follow a series of steps to not only post the original scam but also increase its legitimacy and distribution. First, the attackers take over a verified account, and, except for the Target and G Suite cases, change the Twitter display name and photo to impersonate Tesla CEO Elon Musk. The attackers then use that account to post the scam, which advertises a crypto giveaway and asks followers to follow a link to provide a certain amount of bitcoin to a wallet address in exchange for a larger Bitcoin return. Although the tweets advertise “giveaways,” this scam is considered money-flipping because of the claim that participants can “flip” a small Bitcoin donation into a larger payout.
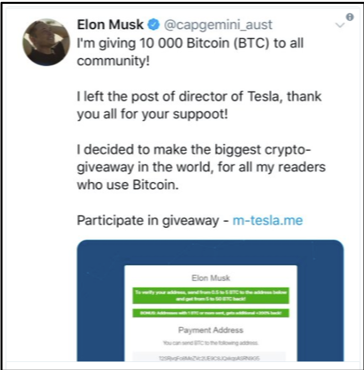
Figure 1: Example of a Hacked Account Impersonating Elon Musk and Advertising Bitcoin Money-Flipping Scam
The attackers take several additional steps on social media to increase the likelihood that followers will partake in the scam. First, they use a network of other hacked, verified accounts to reply back to the initial scam post and post comments legitimizing the scam, such as stating the followers have indeed received the larger Bitcoin payout or indicating thanks for a Bitcoin payout. The need for and use of multiple hacked, verified accounts increases the risk of verified accounts being subject to account takeover for this scam. Second, the attackers reportedly purchase ads through Twitter to promote the initial scam tweets to more users.
Potential Targets
ZeroFOX Alpha Team conducted an initial analysis of 22 verified Twitter accounts that have reportedly been affected so far by this scam, including accounts that actually posted the scam and accounts that replied back to scams. Accounts that were reportedly taken over include those related to retail, beauty products, publishing, film, music, sports and athletic leagues, and several official accounts related to national or international governing bodies. Many of the accounts analyzed were for brands or organizations based in the United States, United Kingdom, Canada, Australia, and Japan. ZeroFOX Alpha Team assesses that verified retail, media, and sports-related business accounts, as well as official government-related accounts, may be at particular risk of account takeovers in order to carry out this scam. Western and Japanese brands and organizations may be at a higher risk as well.
The accounts analyzed were not necessarily internationally recognizable organizations or businesses, particularly in the case of those replying back to scam posts. In addition, the number of followers as of November 13 ranged from as low as 59 to as high as over one million in the case of Target, with a median follower count of 7,620. This suggests that the attackers are more interested in targeting verified accounts than accounts with high follower counts.
Domain Analysis
The ZeroFOX Alpha Team investigated the variety of links and domains included in the scam tweets that the attackers use to actually receive Bitcoin. The links included in the tweets lead to a webpage with a wallet address and QR code to provide the bitcoin. At the bottom of the webpage is a list of supposed recent transactions between the scammers’ Bitcoin wallet and other wallet addresses, with the scammers paying out more Bitcoin than they receive, furthering the illusion of greater payout in exchange for a small amount of Bitcoin.
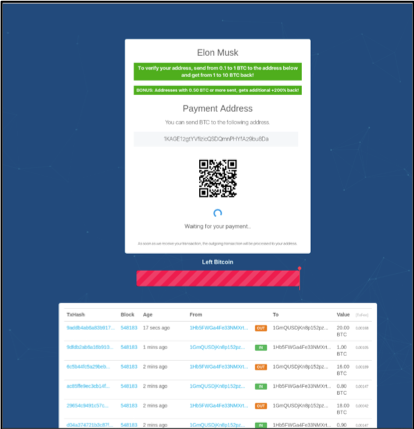
Figure 2: Example of Crypto-Scam Domain Linked in Tweets
ZeroFOX investigated eight domains reported to have been included in scam tweets. One domain has been put up for sale, likely since November 12. The other seven domains are no longer live, with five of them going down likely since November 12-13. Although the domains all had masked registration information, many of the domains had similarities in IP addresses or other characteristics to suggest they are all operated by the same attackers. Through our analysis, we identified at least two additional domains, live as of November 14, that are part of the scam but may not have yet been used by the attackers. The use of multiple domains and the switch between domains indicates the attackers are quickly setting up these webpages in anticipation of them being reported or taken down.
Recommendations
- Customers at risk should enable the Risky Image Change and Risky Name Change rules in their platforms for vulnerable entities or contact [email protected] for assistance. Since the attackers tend to change the Twitter display name and image to impersonate Elon Musk, these rules will alert on any such change and, combined with our Hacked Account rule, provide indications of possible account takeover
- If not already enabled, turn on two-factor authentication for all social media accounts
- Be alert for Twitter display names that do not appear to match their handle
- Be wary of crypto-related advertisements that seem “too good to be true”
Select Social Indicators of Compromise
Elonmusk[dot]id
Musk[dot]plus
Trump-official[dot]com
M-tesla[dot]me
M-crypto[dot]me
Spacex[dot]plus
Musk[dot]fund
Spacex[dot]to
Btc-gift[dot]net
M-tesla[dot]pw
12SRjvqFo8MeZVc2UE9C8JQxkqsASRN9G5
1KAGE12gtUVfizicQSDQmnPHYfA29bu8Da
1NCj5V2a8Yp7Wu6wsEWoRZu6twogKccgDYz
18cUM3a3JSZbaJFAF9BCSzEG14ShxzwmxX
Sources
- URLscan.io
- https://www.usatoday.com/story/money/2018/11/13/twitter-bitcoin-scam-elon-musk-target/1986017002/
- https://www.theverge.com/2018/11/13/18092656/google-g-suite-twitter-account-hacked-bitcoin-scam
- https://www.zdnet.com/article/why-are-fake-elon-musk-bitcoin-scams-running-rife-on-twitter-right-now/
- https://www.cnet.com/news/twitter-grapples-with-fake-elon-musk-accounts-promoting-bitcoin-scams/
- https://techcrunch.com/2018/11/12/twitter-those-verified-bitcoin-pushing-pillocks-are-pissing-everyone-off/
Tags: retail/cpg, apac, government, phishing & fraud, media/entertainment, us/canada