
Breach Disclosure: Pixlr
|by Alpha Team
Breach Disclosure: Pixlr
On 20 January 2021, BleepingComputer published an article detailing the breach of free online photo editing application, Pixlr. The breach contains 1.9 million rows of names, e-mail addresses, social media profiles, the user's country and SHA-512 password hashes. This is 1 of the many breaches leaked by ShinyHunters in January.
Recommendations
- Enable 2-factor authentication for all of your organizational accounts to help mitigate phishing and credential stuffing attacks
- If not already enabled, turn on the compromised credentials rule for all relevant entities and ensure relevant emails are entered for those entities, or reach out to [email protected] for assistance
- If one of your entities receives an alert, ZeroFOX recommends immediate password changes for the affected account
Details
ShinyHunters posted the breach data for free in a thread on RaidForums on 16 January, 2021. As of the writing of this advisory, Pixlr has not acknowledged the breach. According to the post by ShinyHunters, the company was breached at the same time as 123RF. Both companies are owned by Inmagine, a company that owns a number of subsidiaries that are rooted in design and media.
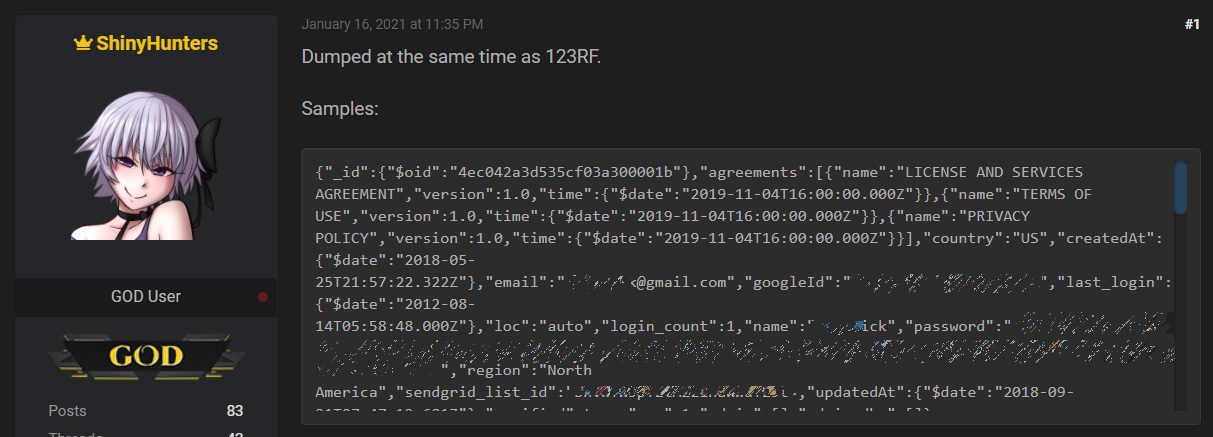
Figure 1: ShinyHunters post. Source: BleepingComputer
Tags: technology, data breach, global