
Threat Intelligence Bulletin: 08/26/2022 - 09/01/2022
|by Alpha Team
Breach disclosure: Chainlink
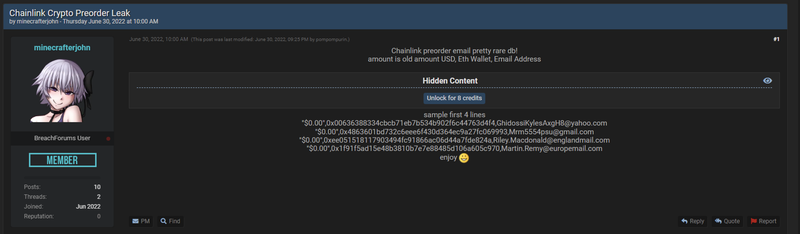
On June 30, 2022, threat actor "minecrafterjohn" from the BreachForums posted a data breach package targeting Chainlink (chain[.]link), a US-based organization providing framework for writing hybrid smart contracts by blockchain developers which connect non-blockchain enterprises with blockchain platforms. From this package, ZeroFox extracted 6,023 email addresses.
Standing Intelligence Requirements

For the most up to date list of ZeroFox Threat Research’s Intelligence Requirements, please visit:
https://cloud.zerofox.com/alpha_team/advisories/14956
Details
On June 30, 2022, a recently registered threat actor "minecrafterjohn" from the BreachForums posted a data breach package targeting Chainlink (chain[.]link), a US-based organization providing framework for writing hybrid smart contracts by blockchain developers which connect non-blockchain enterprises with blockchain platforms. From this package, ZeroFox extracted 6,023 email addresses. No passwords were found in this breach.
Recommendations
- If not already enabled, turn on the compromised credentials rule for all relevant entities and ensure relevant emails are entered for those entities, or reach out to [email protected] for assistance
- If one of your entities receives an alert, ZeroFox recommends immediate password changes for the affected account
- Enable 2-factor authentication for all of your organizational accounts to help mitigate phishing and credential stuffing attacks
Breach disclosure: BG Look
On May 5, 2022, a reputed threat actor "louisthomas82" from the BreachForums posted a data breach package targeting BG Look, an online and offline store for clothes, shoes and gifts operating from Bulgaria. From the package published in BreachForums, ZeroFox extracted 3,308 email addresses and hashed passwords.
Standing Intelligence Requirements
For the most up to date list of ZeroFox Threat Research’s Intelligence Requirements, please visit:
https://cloud.zerofox.com/alpha_team/advisories/14956
Details
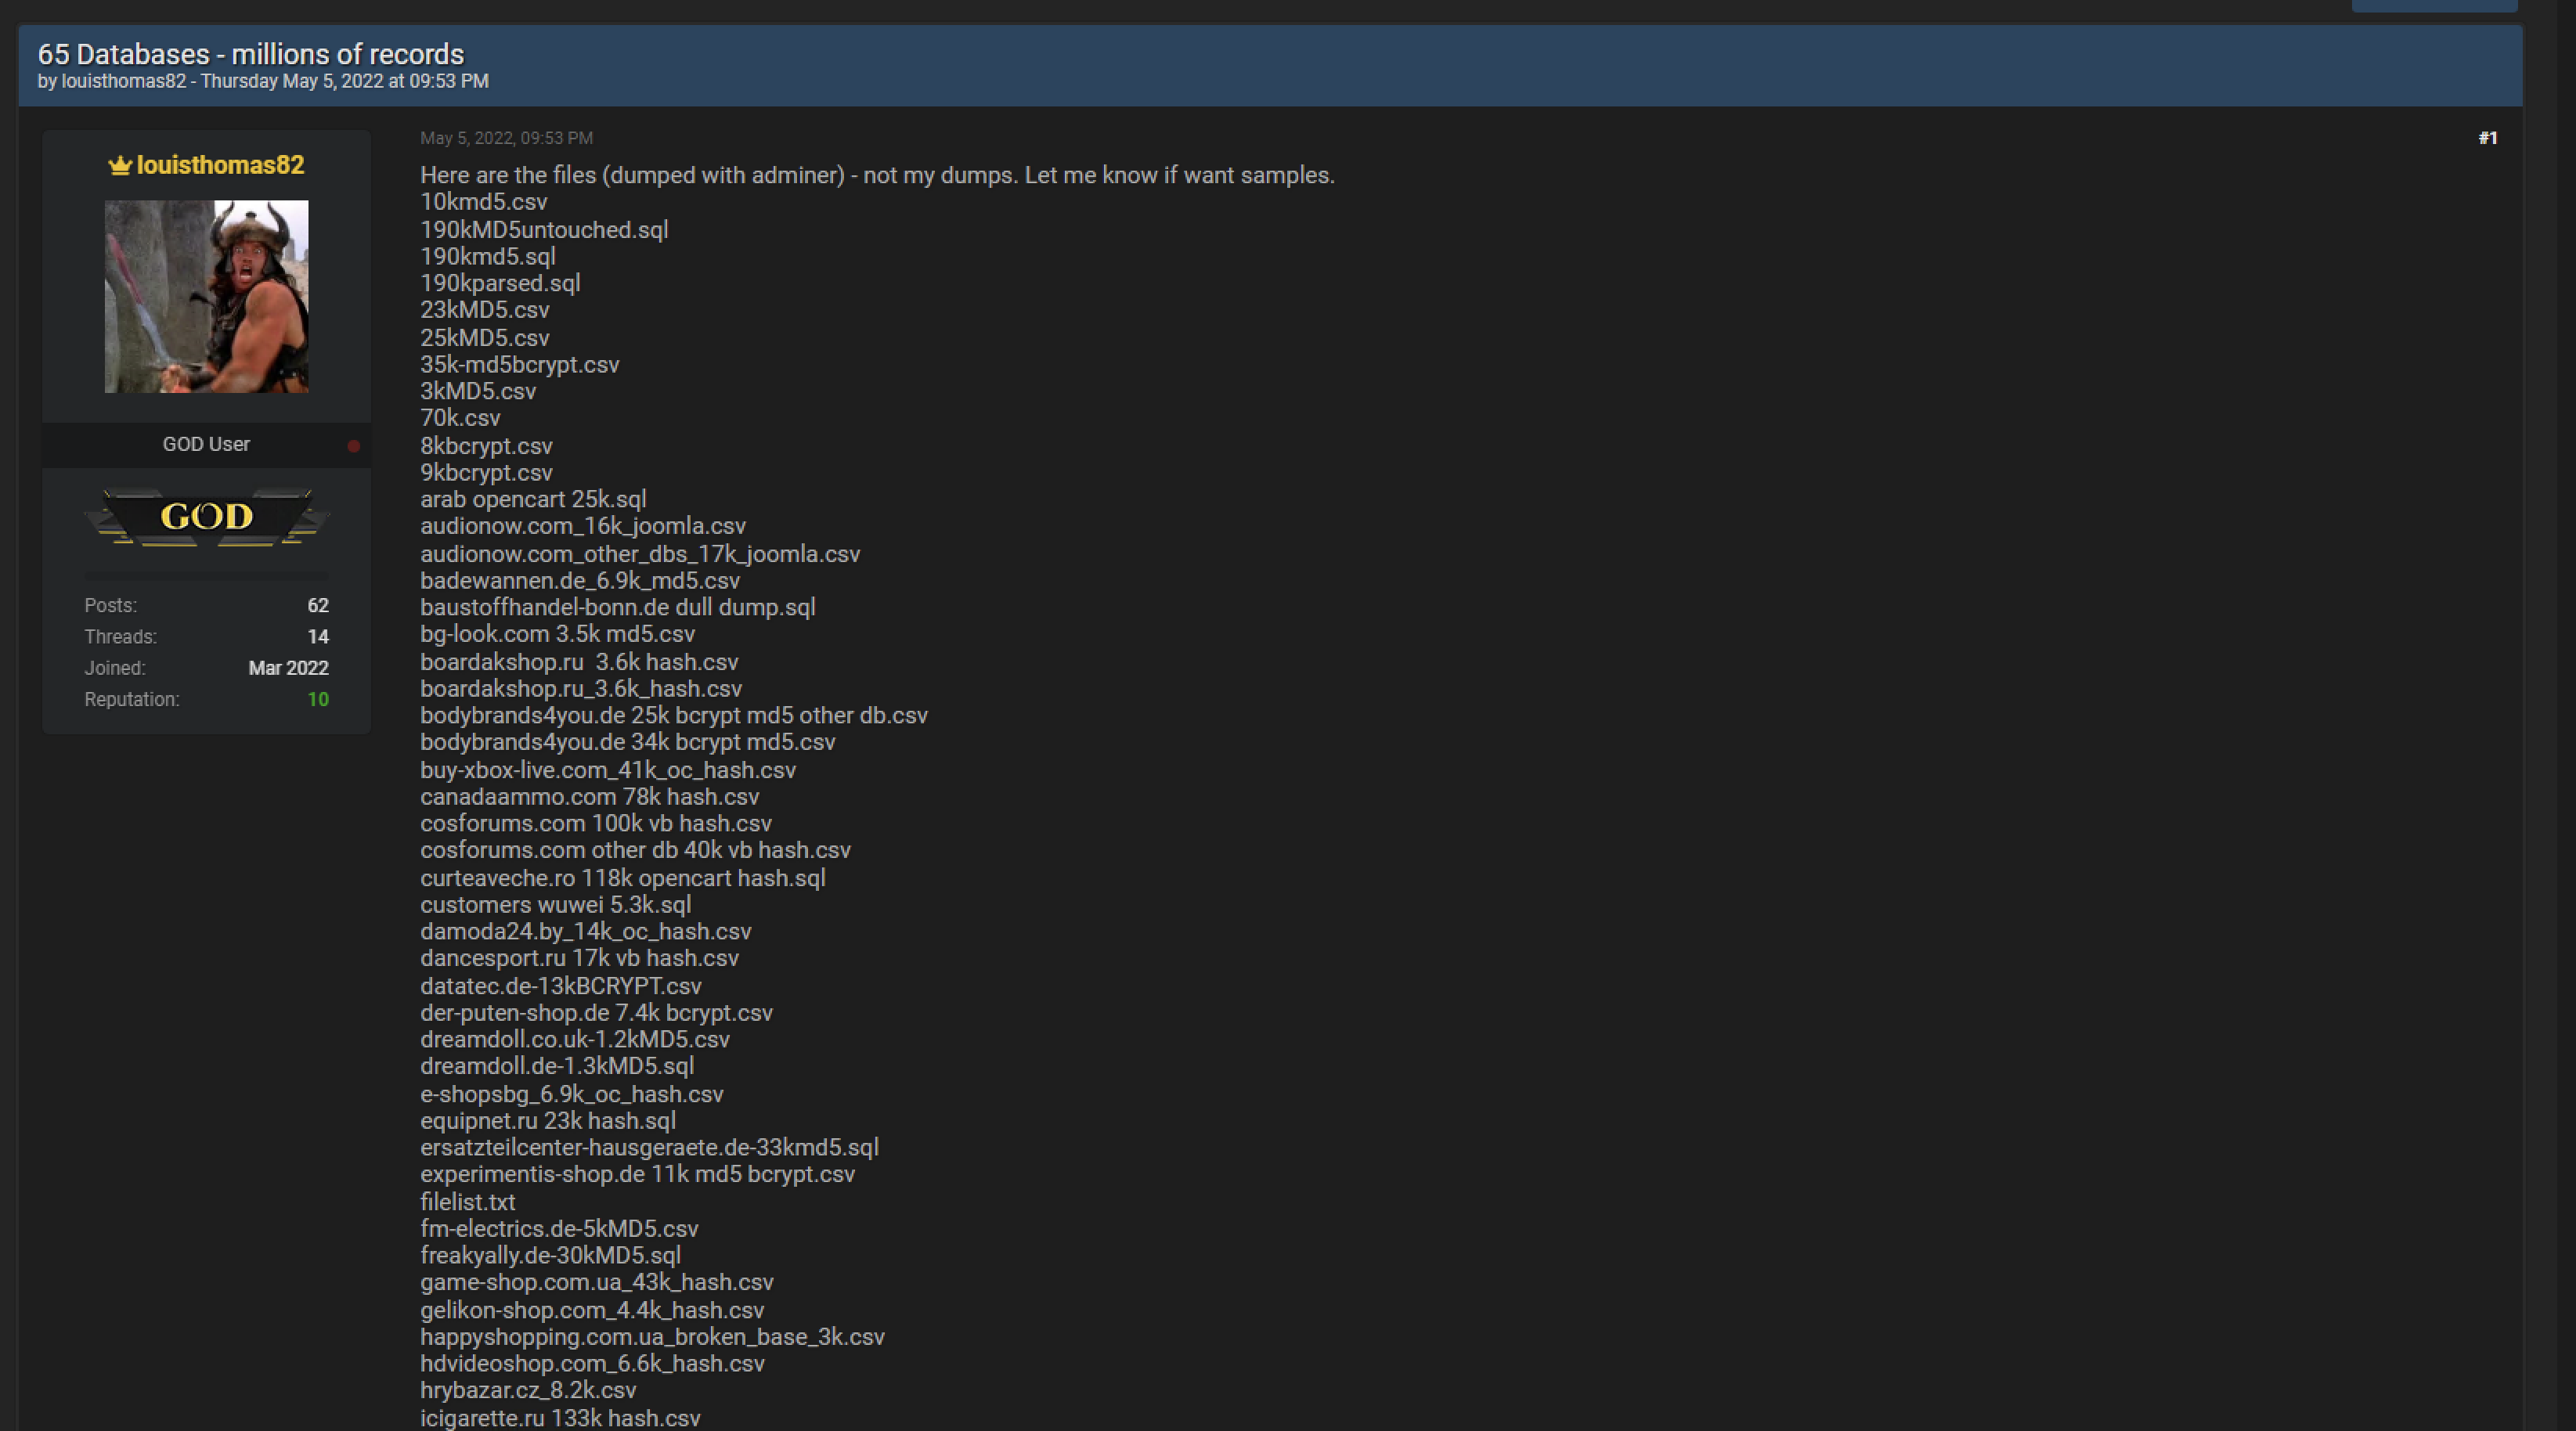
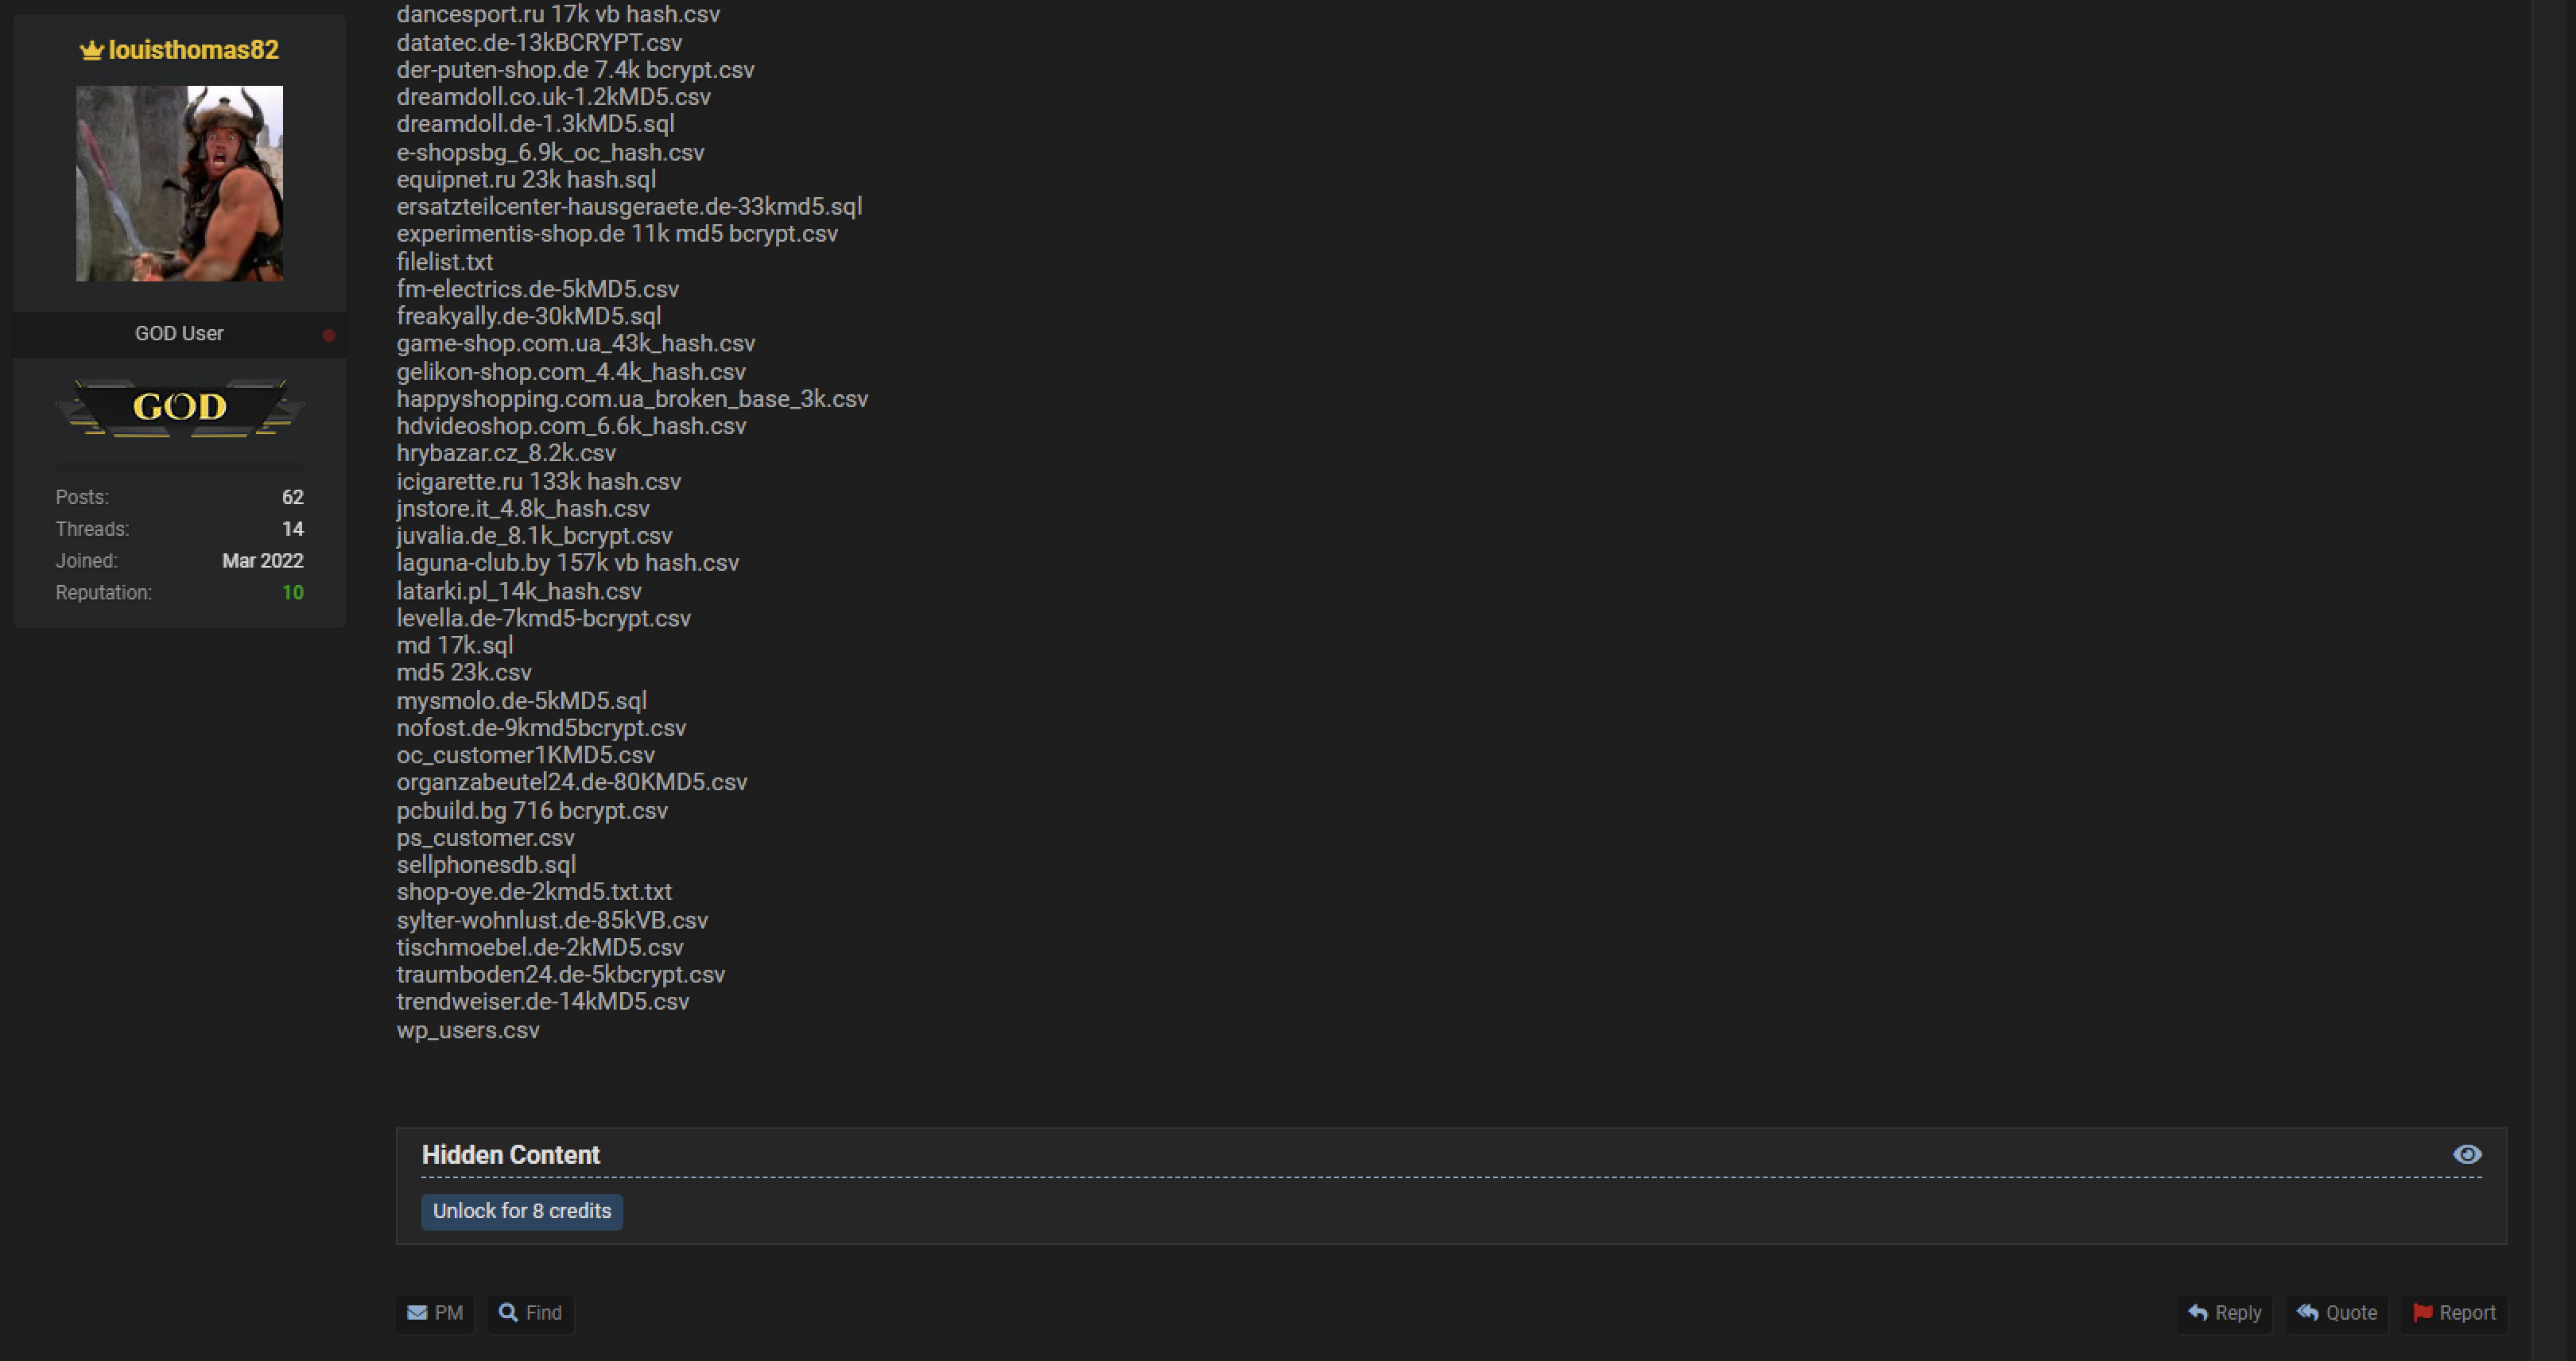
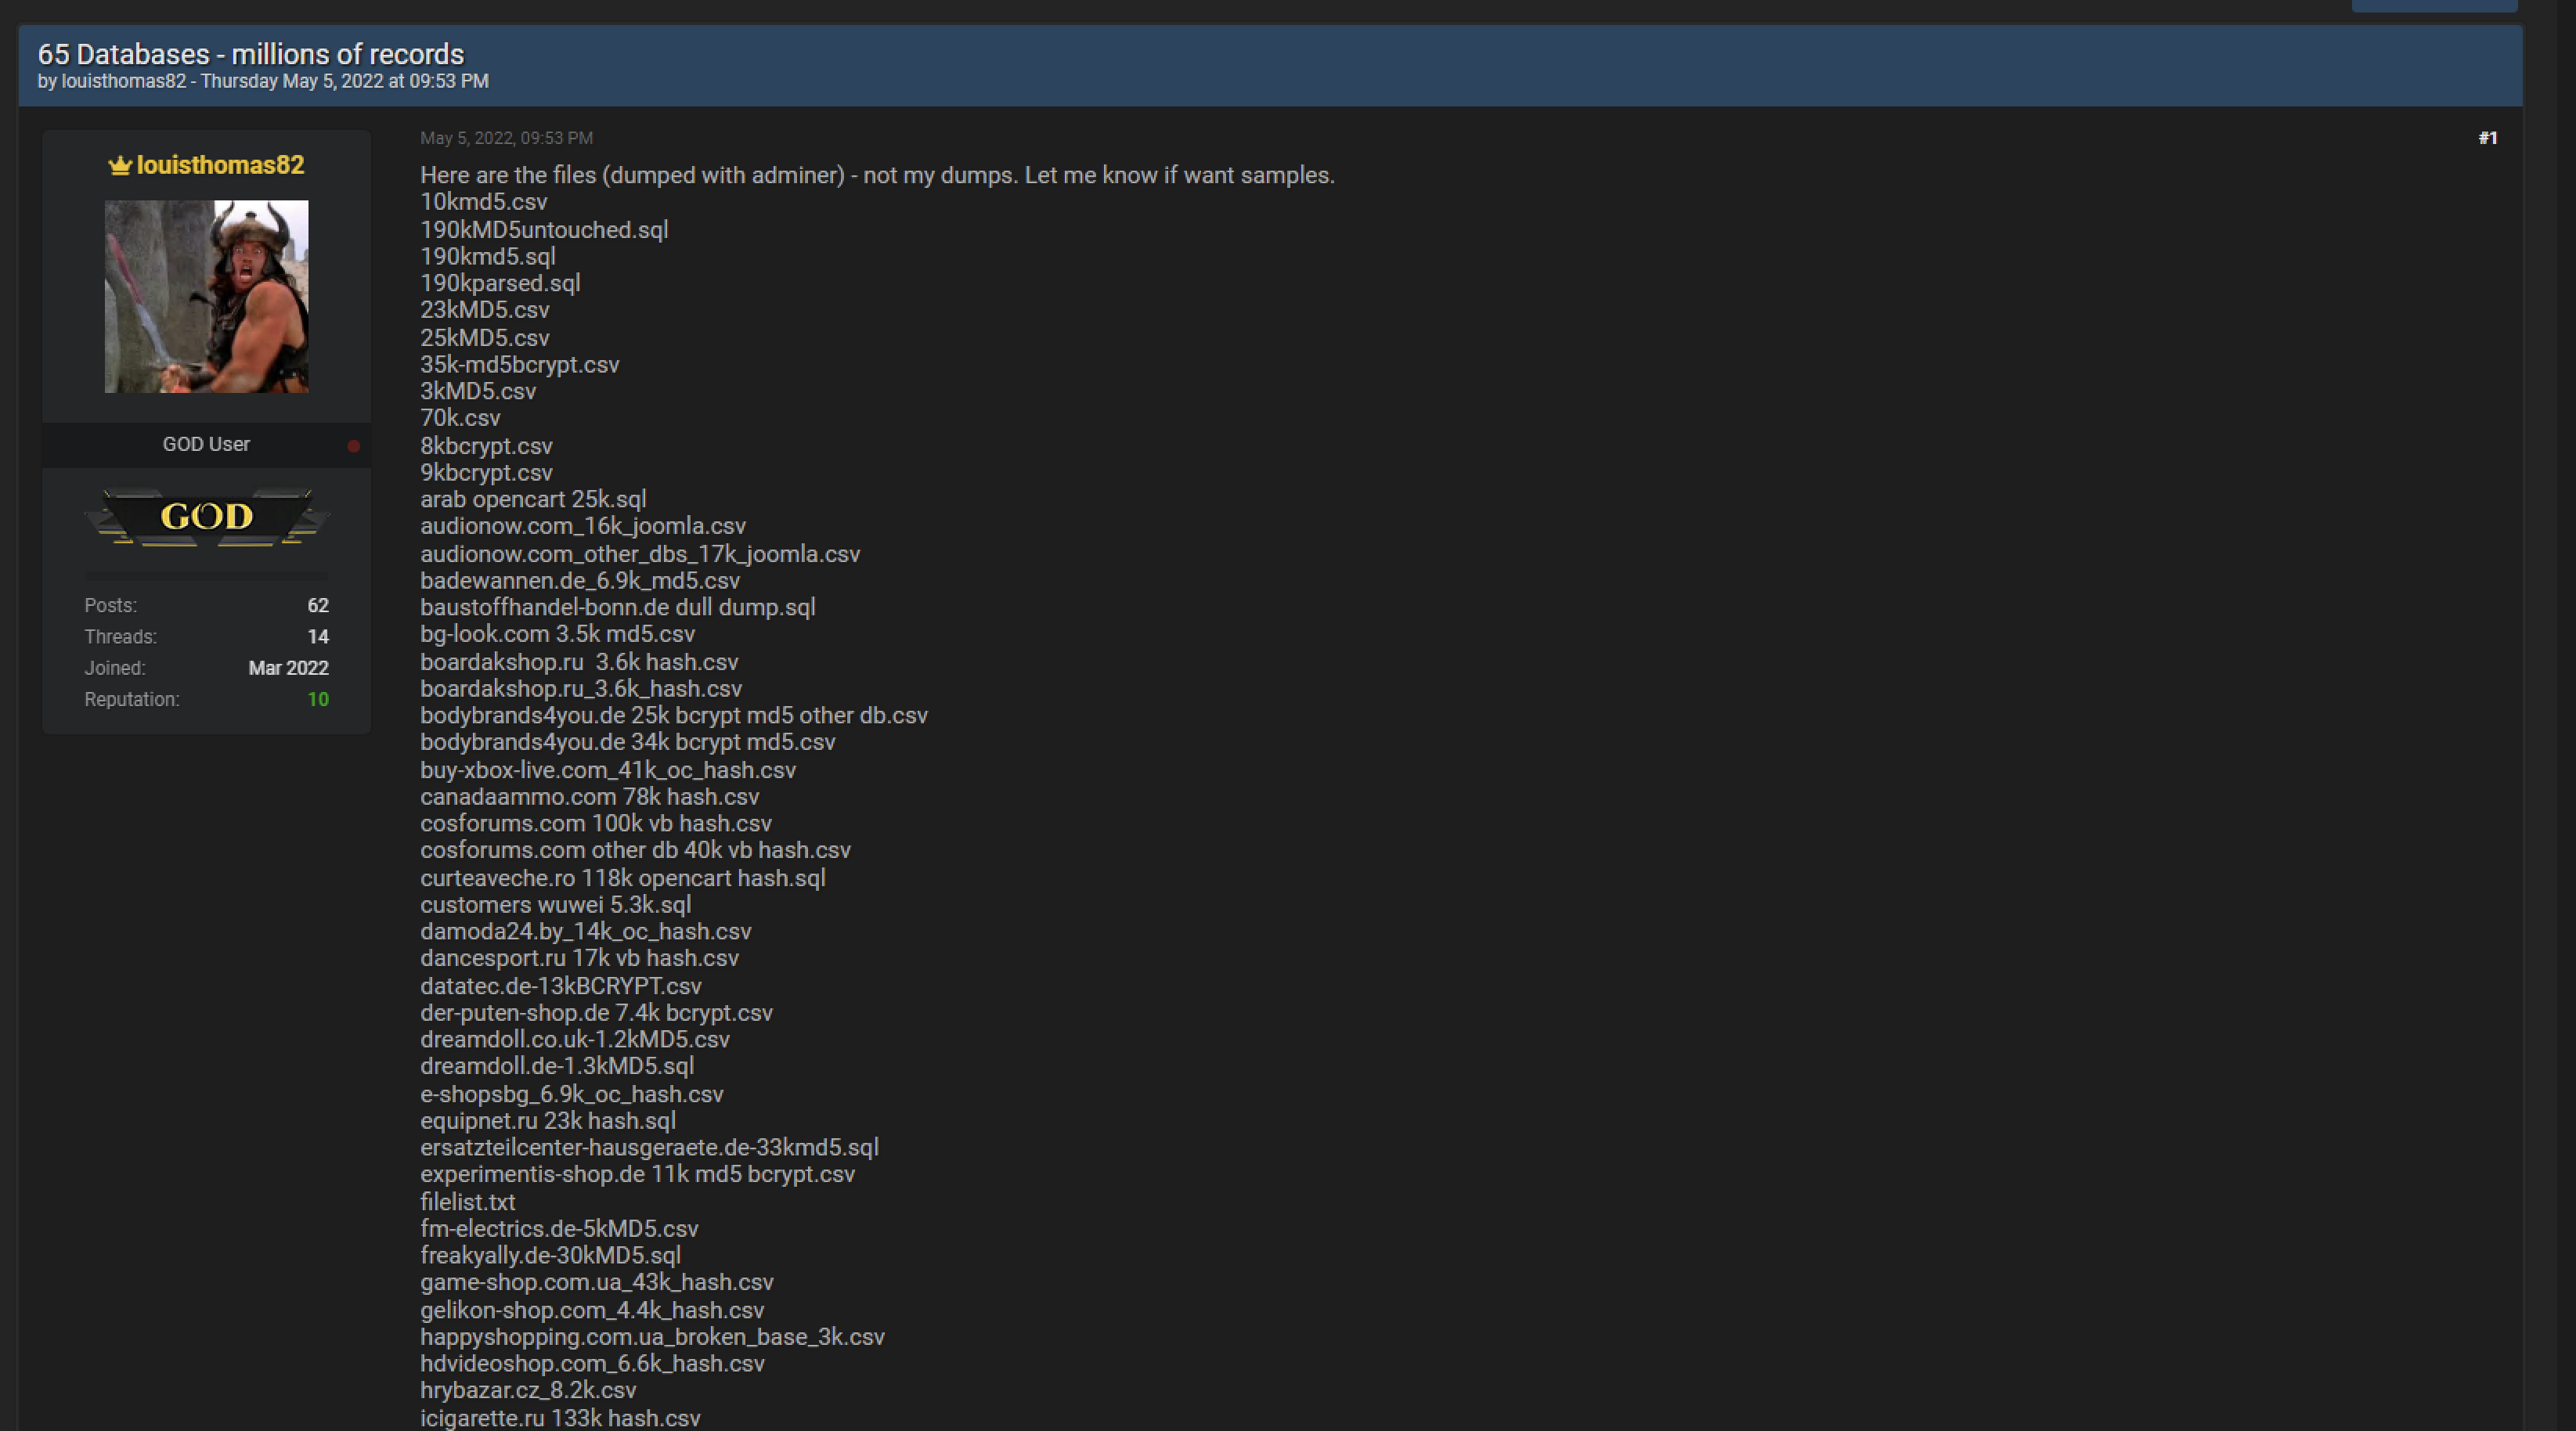
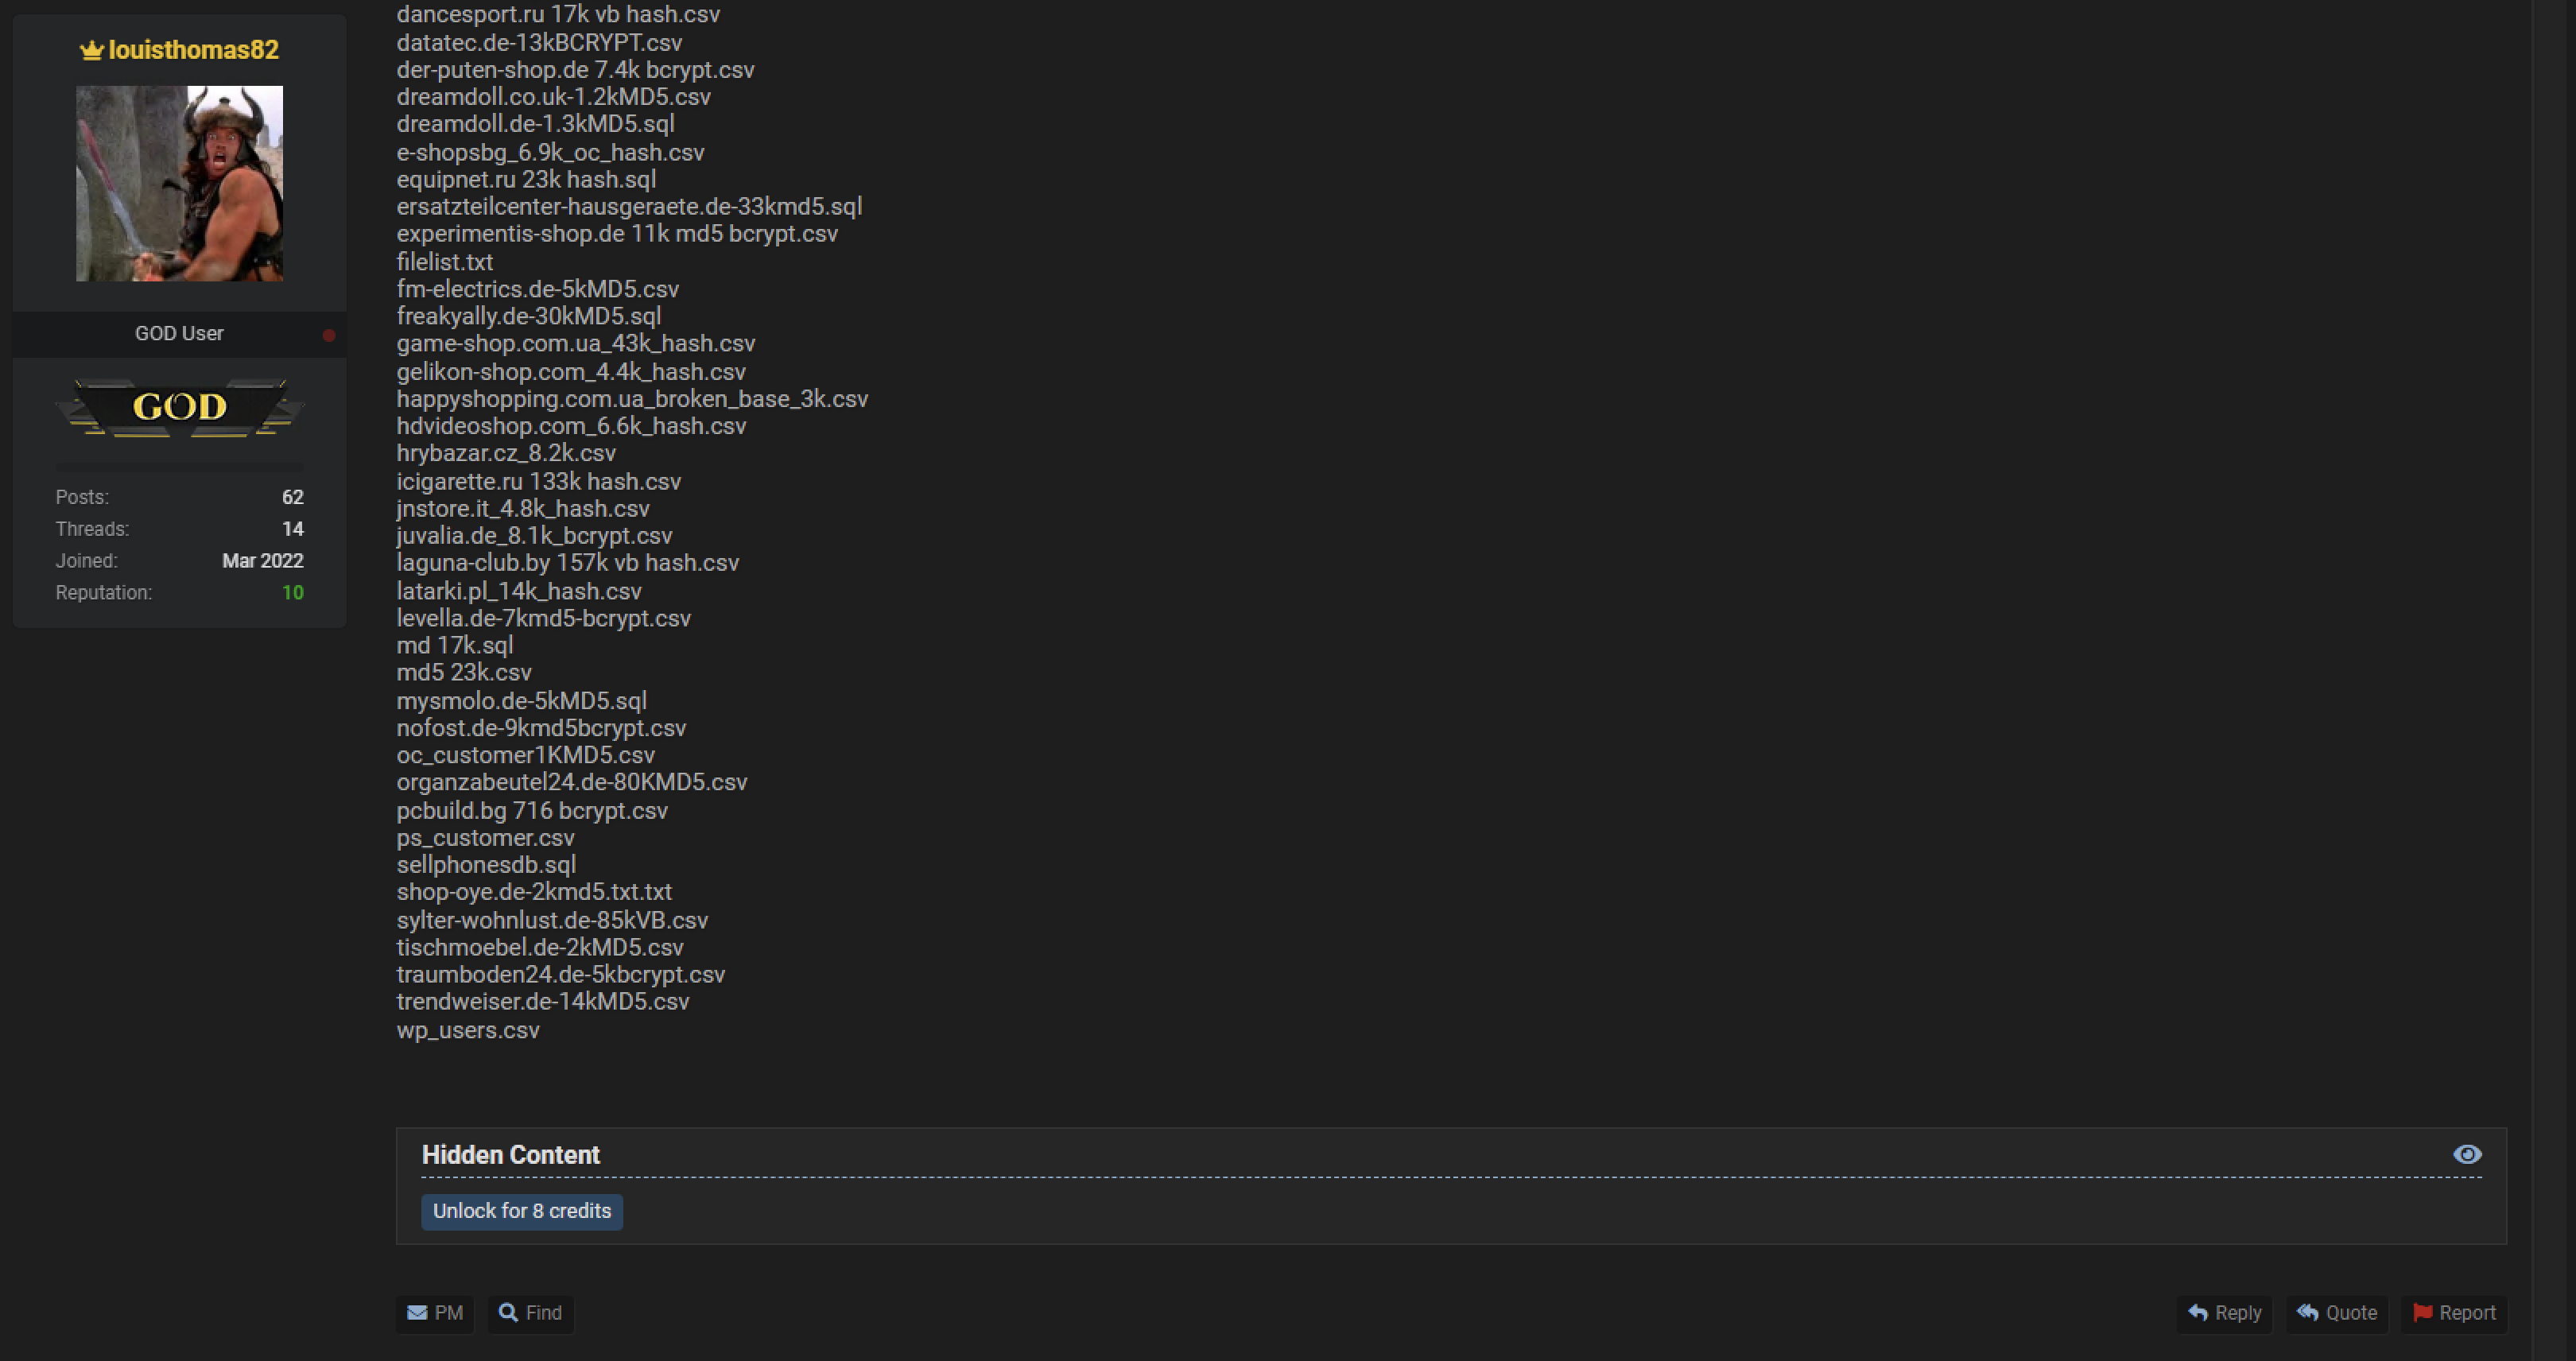
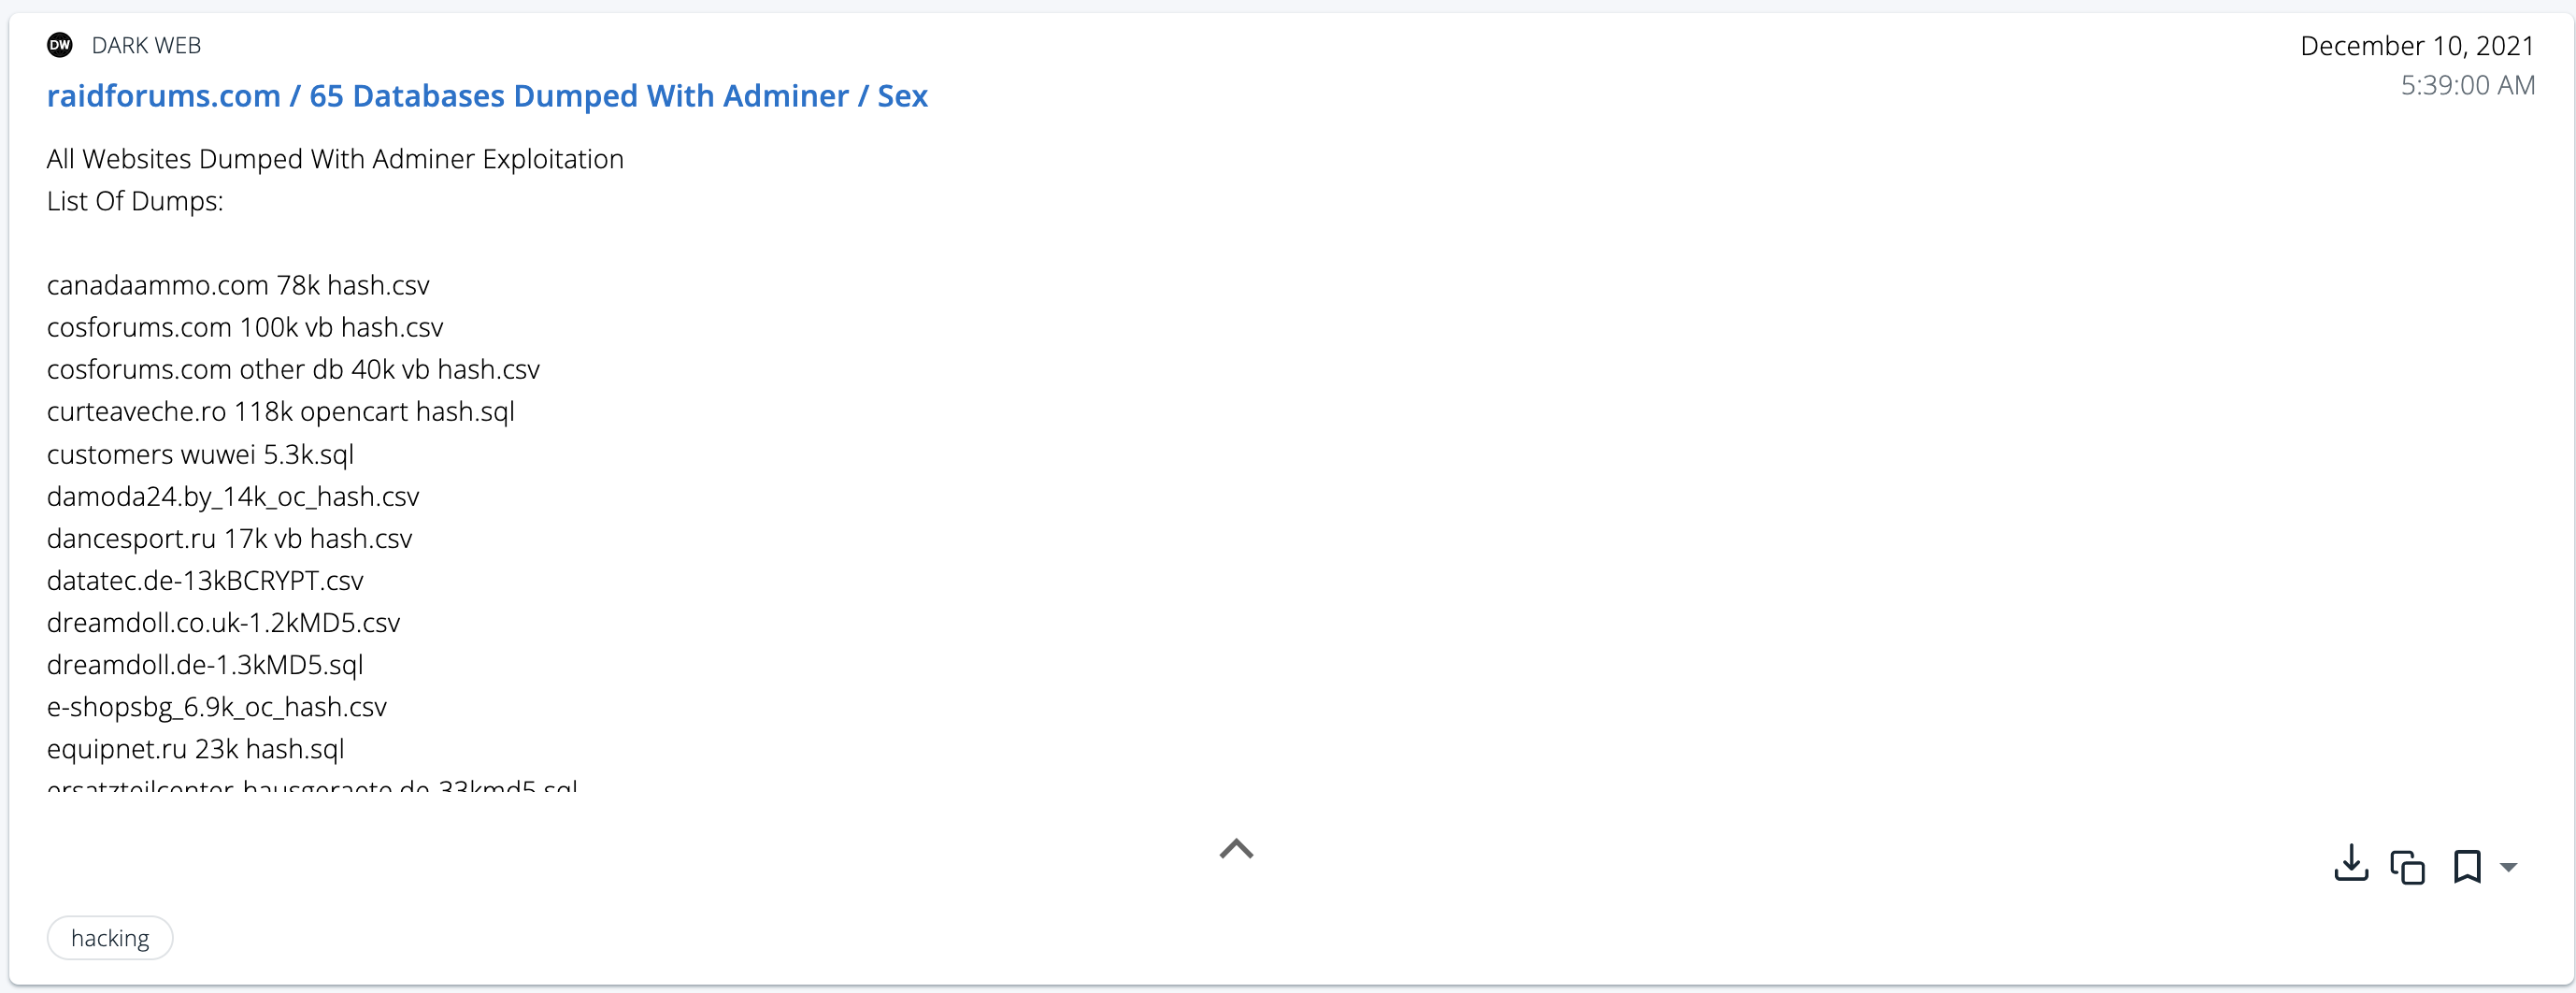
On May 5, 2022, a reputed threat actor "louisthomas82" from the BreachForums posted a data breach package targeting BG Look, an online and offline store for clothes, shoes and gifts operating from Bulgaria. The threat actor noted that the data breach package includes 65 databases with millions of records. The database for BG Look is a part of that 65 databases. The data dump was also circulated in Raid Forums on December 10, 2021 by the threat actor "Sex". From the package published in BreachForums, ZeroFox extracted 3,308 email addresses and hashed passwords.
Recommendations
- If not already enabled, turn on the compromised credentials rule for all relevant entities and ensure relevant emails are entered for those entities, or reach out to [email protected] for assistance
- If one of your entities receives an alert, ZeroFox recommends immediate password changes for the affected account
- Enable 2-factor authentication for all of your organizational accounts to help mitigate phishing and credential stuffing attacks
Breach Disclosure: BOARDak Boardshop
On May 5, 2022, a reputed threat actor "louisthomas82" from the BreachForums posted a data breach package targeting BOARDak Boardshop, an online and offline store for skateboard and snowboard brands operating from Rostov-on-Don, Russia. The threat actor noted that the data breach package includes 65 databases with millions of records. From the package published in BreachForums, ZeroFox extracted 3,616 email addresses and hashed passwords.
Standing Intelligence Requirements
For the most up to date list of ZeroFox Threat Research’s Intelligence Requirements, please visit:
https://cloud.zerofox.com/alpha_team/advisories/14956
Details
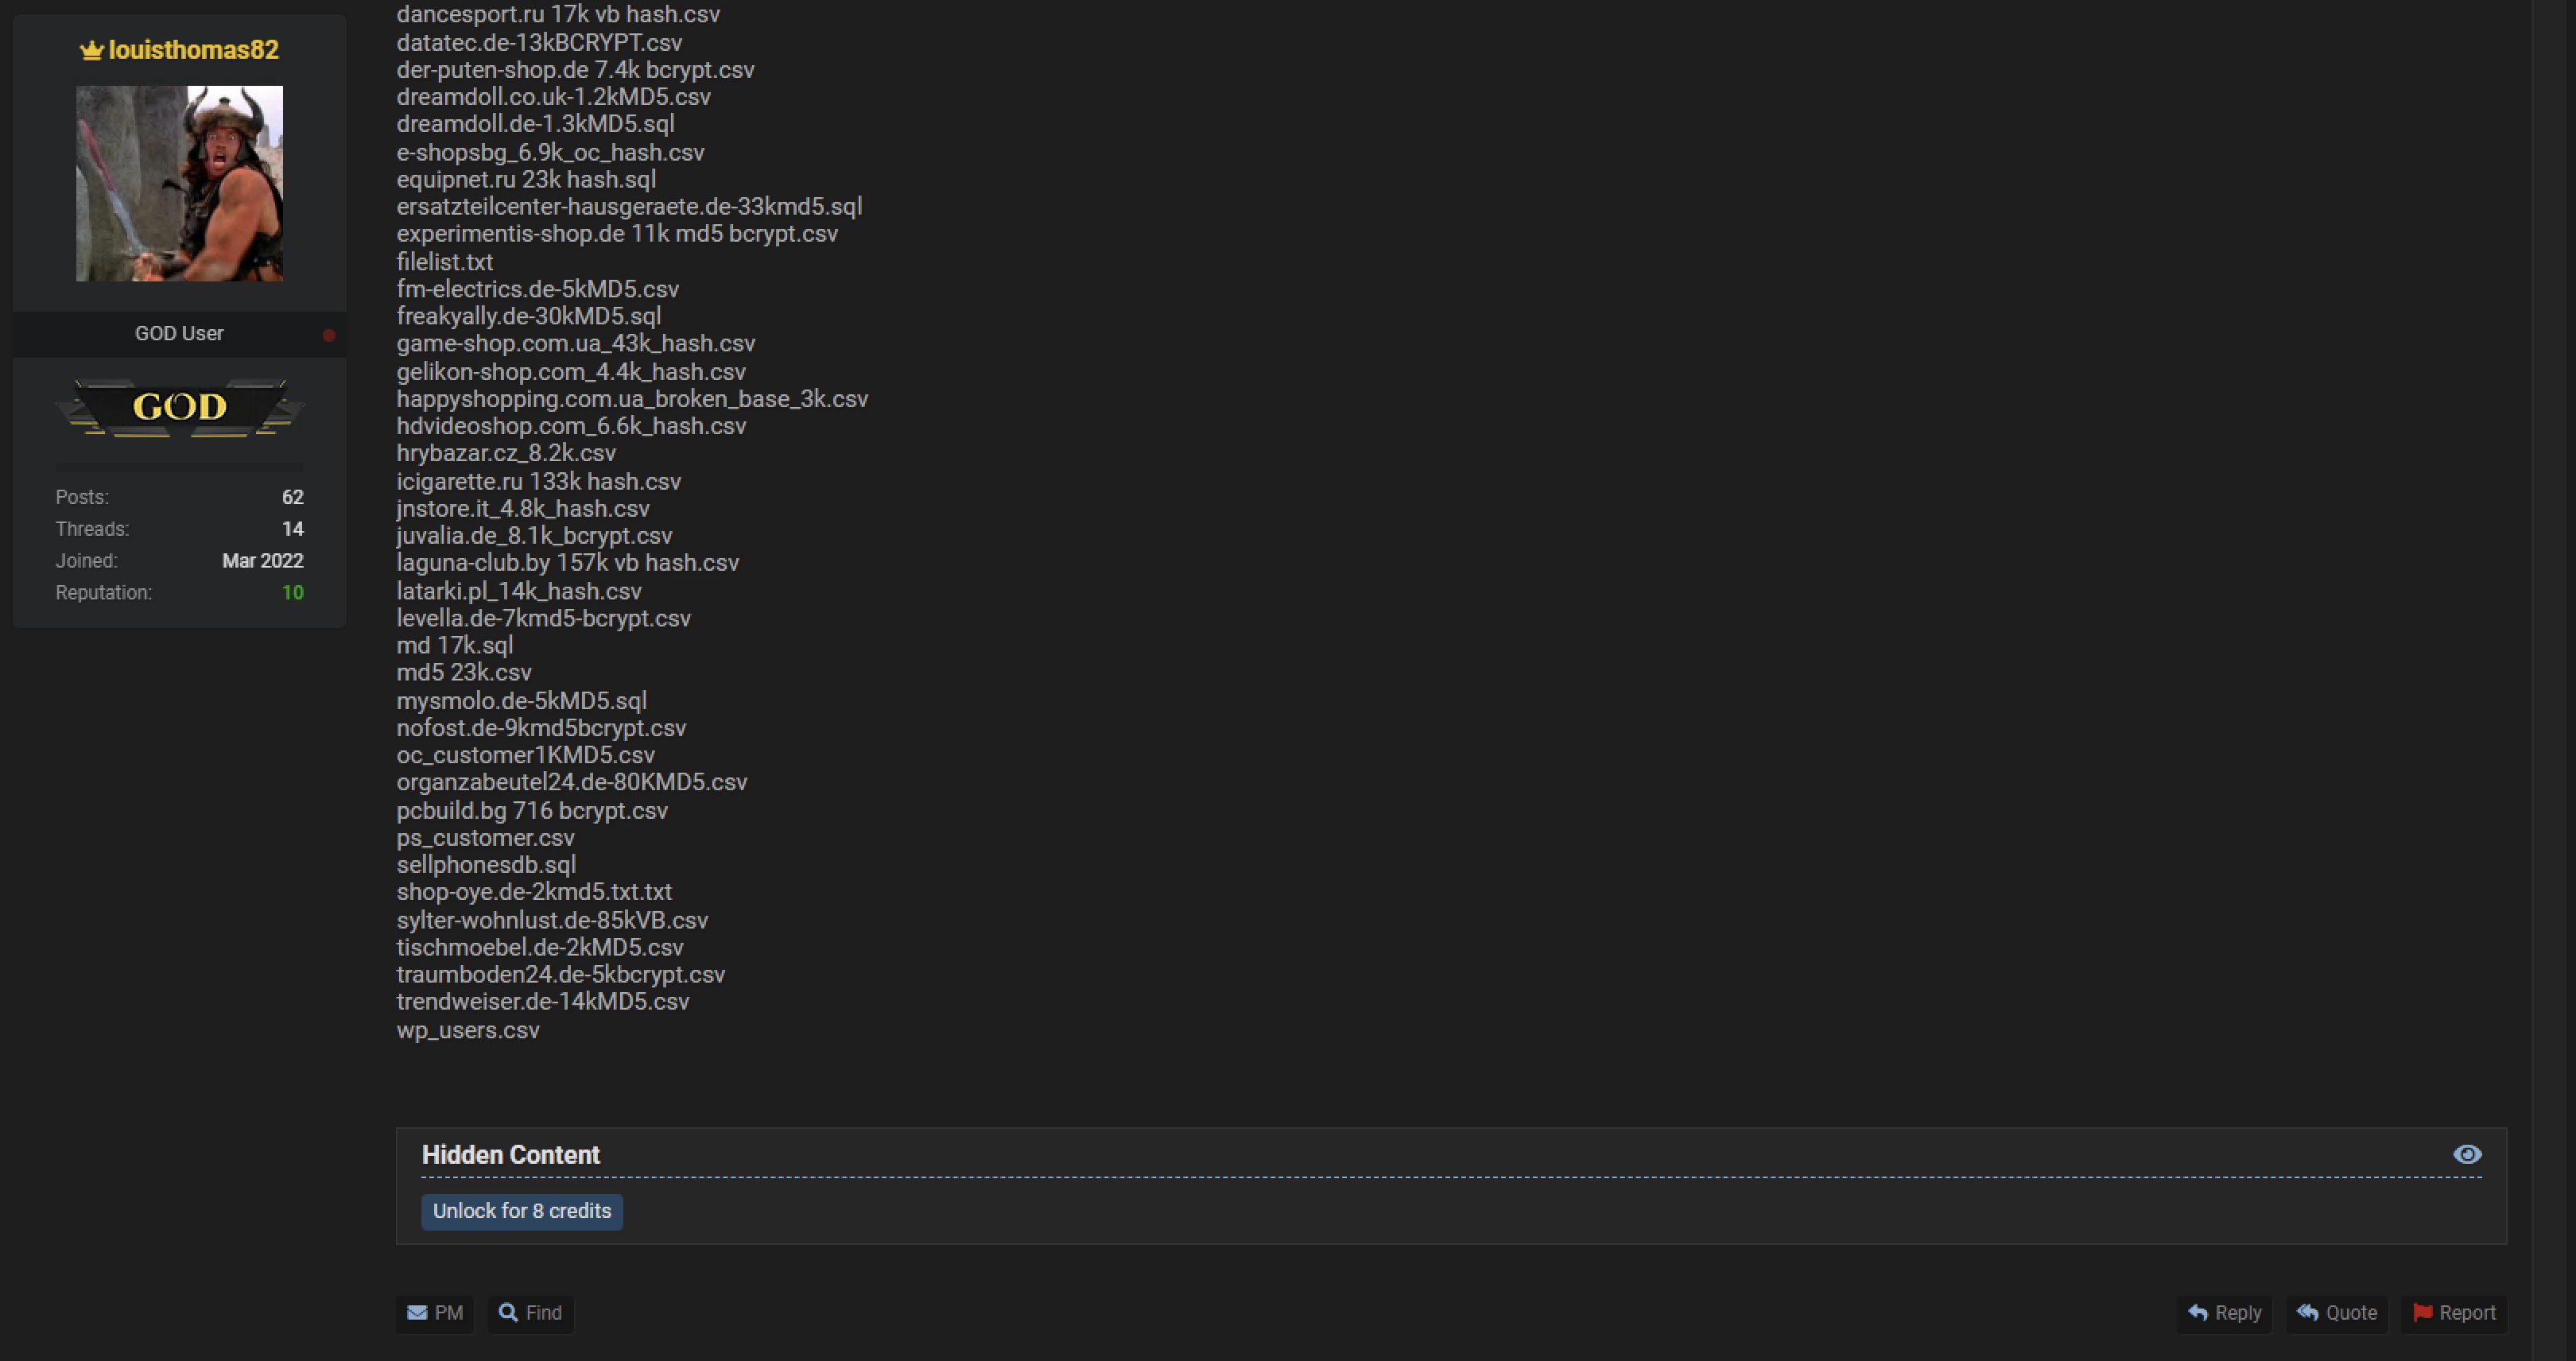
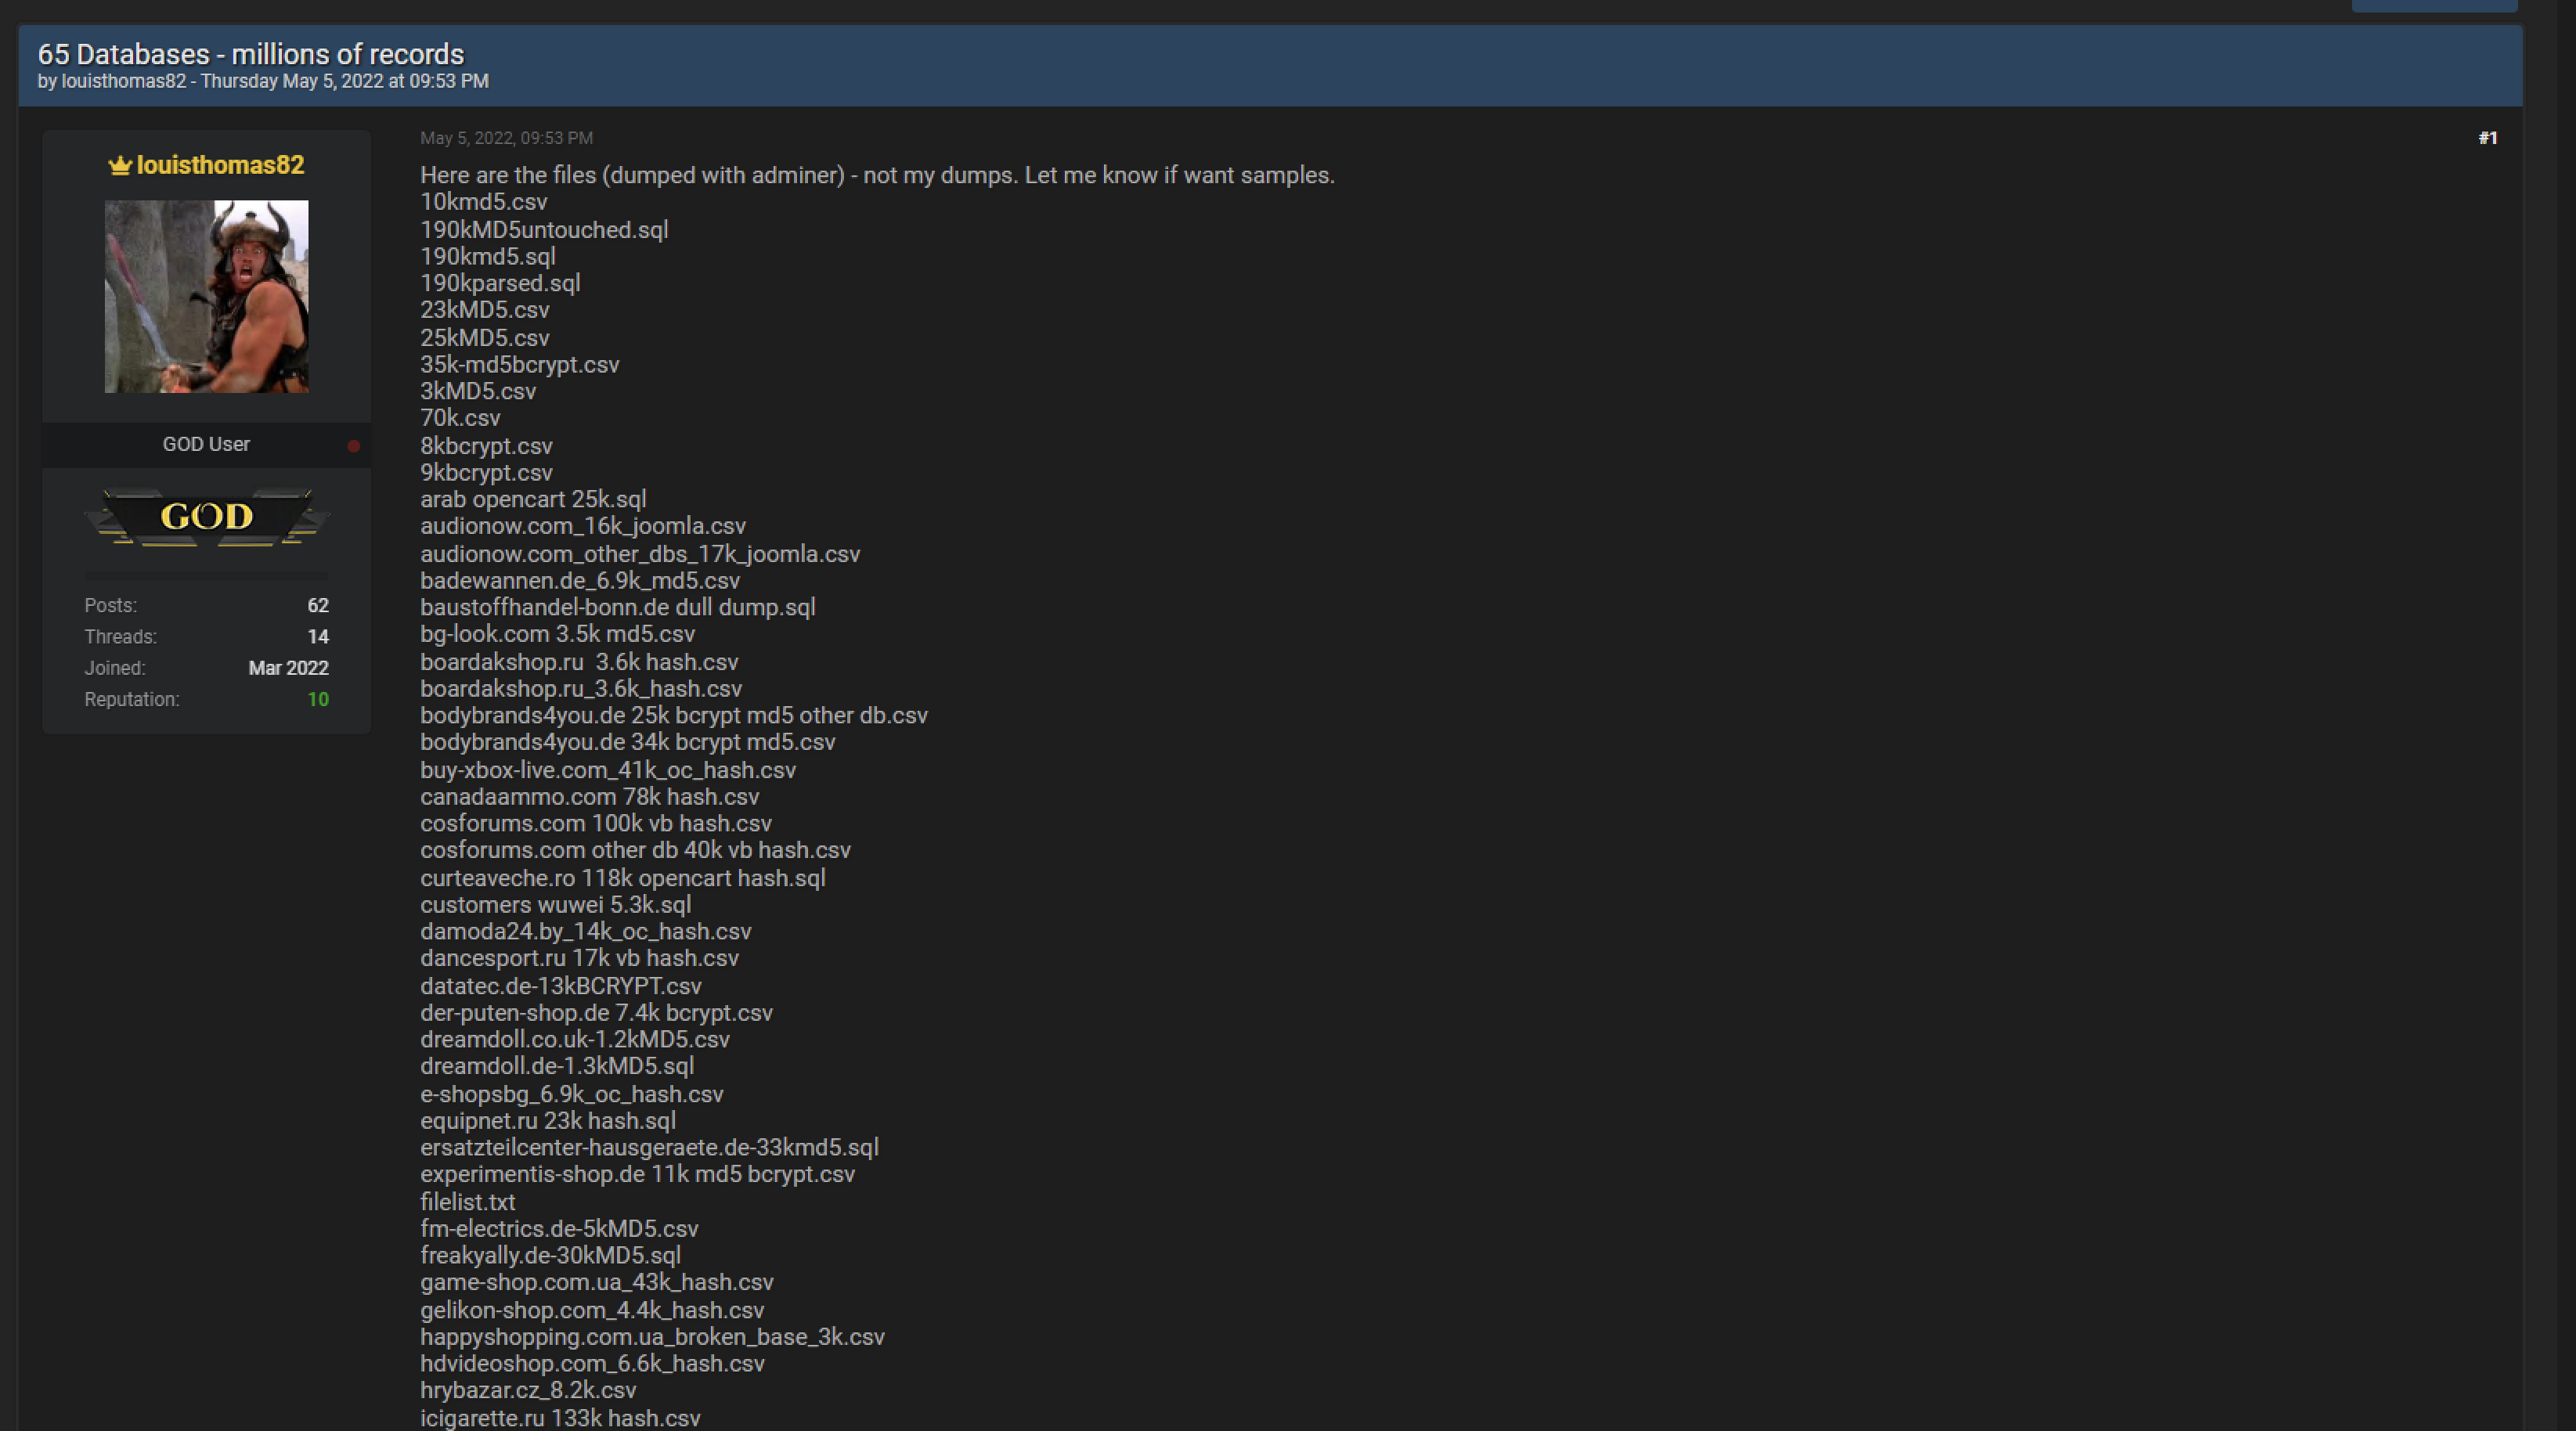
On May 5, 2022, a reputed threat actor "louisthomas82" from the BreachForums posted a data breach package targeting BOARDak Boardshop, an online and offline store for skateboard and snowboard brands operating from Rostov-on-Don, Russia. The threat actor noted that the data breach package includes 65 databases with millions of records. The database for BOARDak Boardshop is a part of that 65 databases. The data dump was also circulated in Raid Forums on December 10, 2021 by the threat actor "Sex". From the package published in BreachForums, ZeroFox extracted 3,616 email addresses and hashed passwords.
Recommendations
- If not already enabled, turn on the compromised credentials rule for all relevant entities and ensure relevant emails are entered for those entities, or reach out to [email protected] for assistance
- If one of your entities receives an alert, ZeroFox recommends immediate password changes for the affected account
- Enable 2-factor authentication for all of your organizational accounts to help mitigate phishing and credential stuffing attacks
Breach Disclosure: sofrip.com
On May 22, 2022, the Telegram Channel "ARVIN" (hxxps[:]//t[.]me/arvin_club) posted a data breach package targeting the Sofrip (sofrip[.]com), a textile recycling industry specialized in used clothing, shoes, wiping rags and fraying operating from Tunisia, North Africa. From the package published in Telegram Channel "ARVIN", ZeroFox extracted 7,491 email addresses.
Standing Intelligence Requirements
For the most up to date list of ZeroFox Threat Research’s Intelligence Requirements, please visit:
https://cloud.zerofox.com/alpha_team/advisories/14956
Details
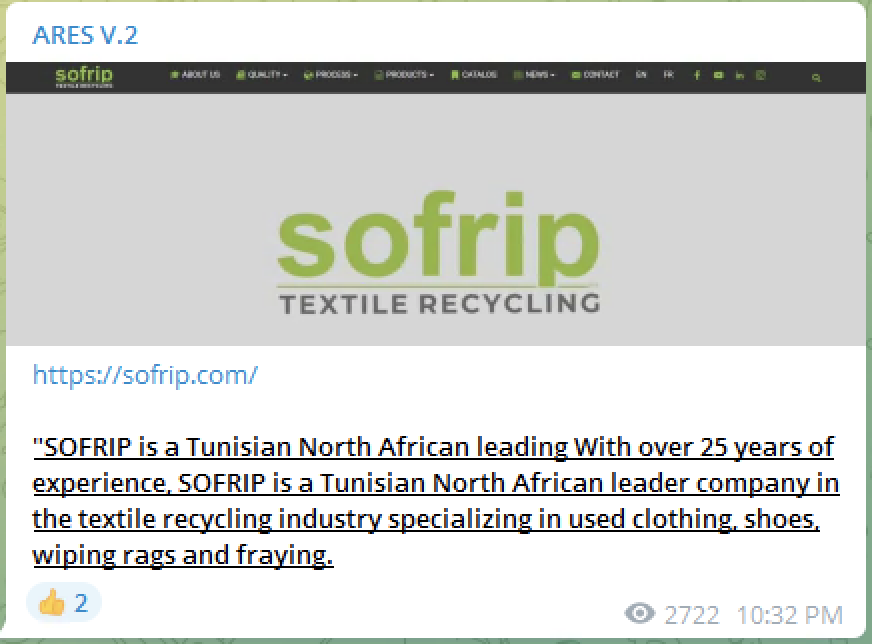
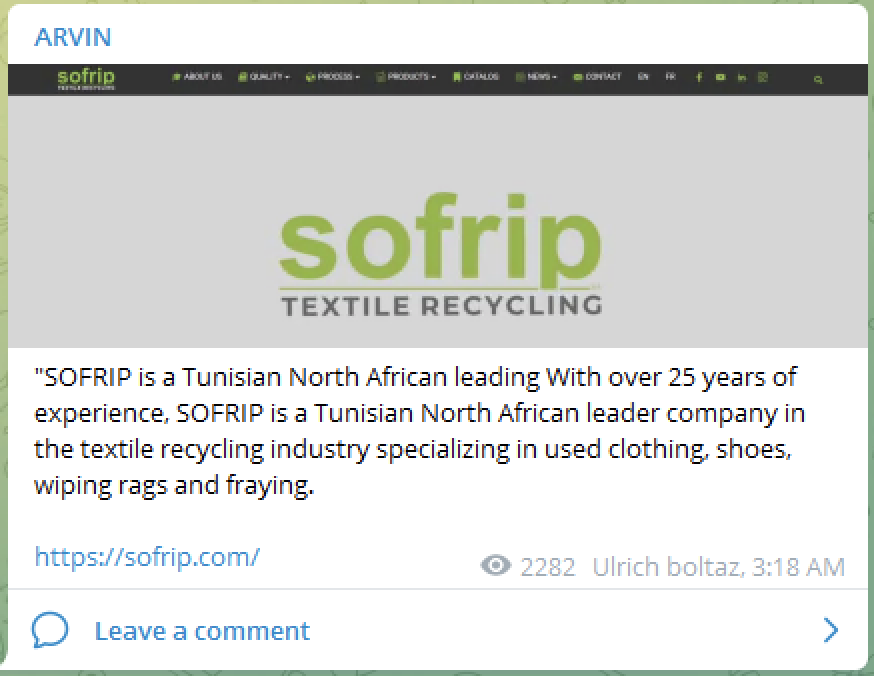
On May 22, 2022, the Telegram Channel "ARVIN" posted a data breach package targeting the Sofrip, a textile recycling industry specialized in used clothing, shoes, wiping rags and fraying operating from Tunisia, North Africa. The data dump was also circulated in a Telegram channel "ARES V.2" (hxxps[:]//t[.]me/aresfreedatav2/458) on May 22, 2022. From the package published in Telegram Channel "ARVIN", ZeroFox extracted 7,491 email addresses. Of this total, an assessed 298 records contained hashed passwords.
Recommendations
- If not already enabled, turn on the compromised credentials rule for all relevant entities and ensure relevant emails are entered for those entities, or reach out to [email protected] for assistance
- If one of your entities receives an alert, ZeroFox recommends immediate password changes for the affected account
- Enable 2-factor authentication for all of your organizational accounts to help mitigate phishing and credential stuffing attacks
Breach Disclosure: Grand Vegas Casino
On July 5, 2022, a reputed threat actor "Topazzz" from the Russian language deep web forum XSS posted a data breach package targeting Grand Vegas Casino, an online casino gaming website operating from United States. From this package, ZeroFox extracted 235,801 email addresses.
Standing Intelligence Requirements
For the most up to date list of ZeroFox Threat Research’s Intelligence Requirements, please visit:
https://cloud.zerofox.com/alpha_team/advisories/14956
Details
On July 5, 2022, a reputed threat actor "Topazzz" from the Russian language deep web forum XSS posted a data breach package targeting Grand Vegas Casino, an online casino gaming website operating from United States. From this package, ZeroFox extracted 235,801 email addresses. No passwords were found in this breach.
Recommendations
- If not already enabled, turn on the compromised credentials rule for all relevant entities and ensure relevant emails are entered for those entities, or reach out to [email protected] for assistance
- If one of your entities receives an alert, ZeroFox recommends immediate password changes for the affected account
- Enable 2-factor authentication for all of your organizational accounts to help mitigate phishing and credential stuffing attacks
Breach Disclosure: TNS Energo Group
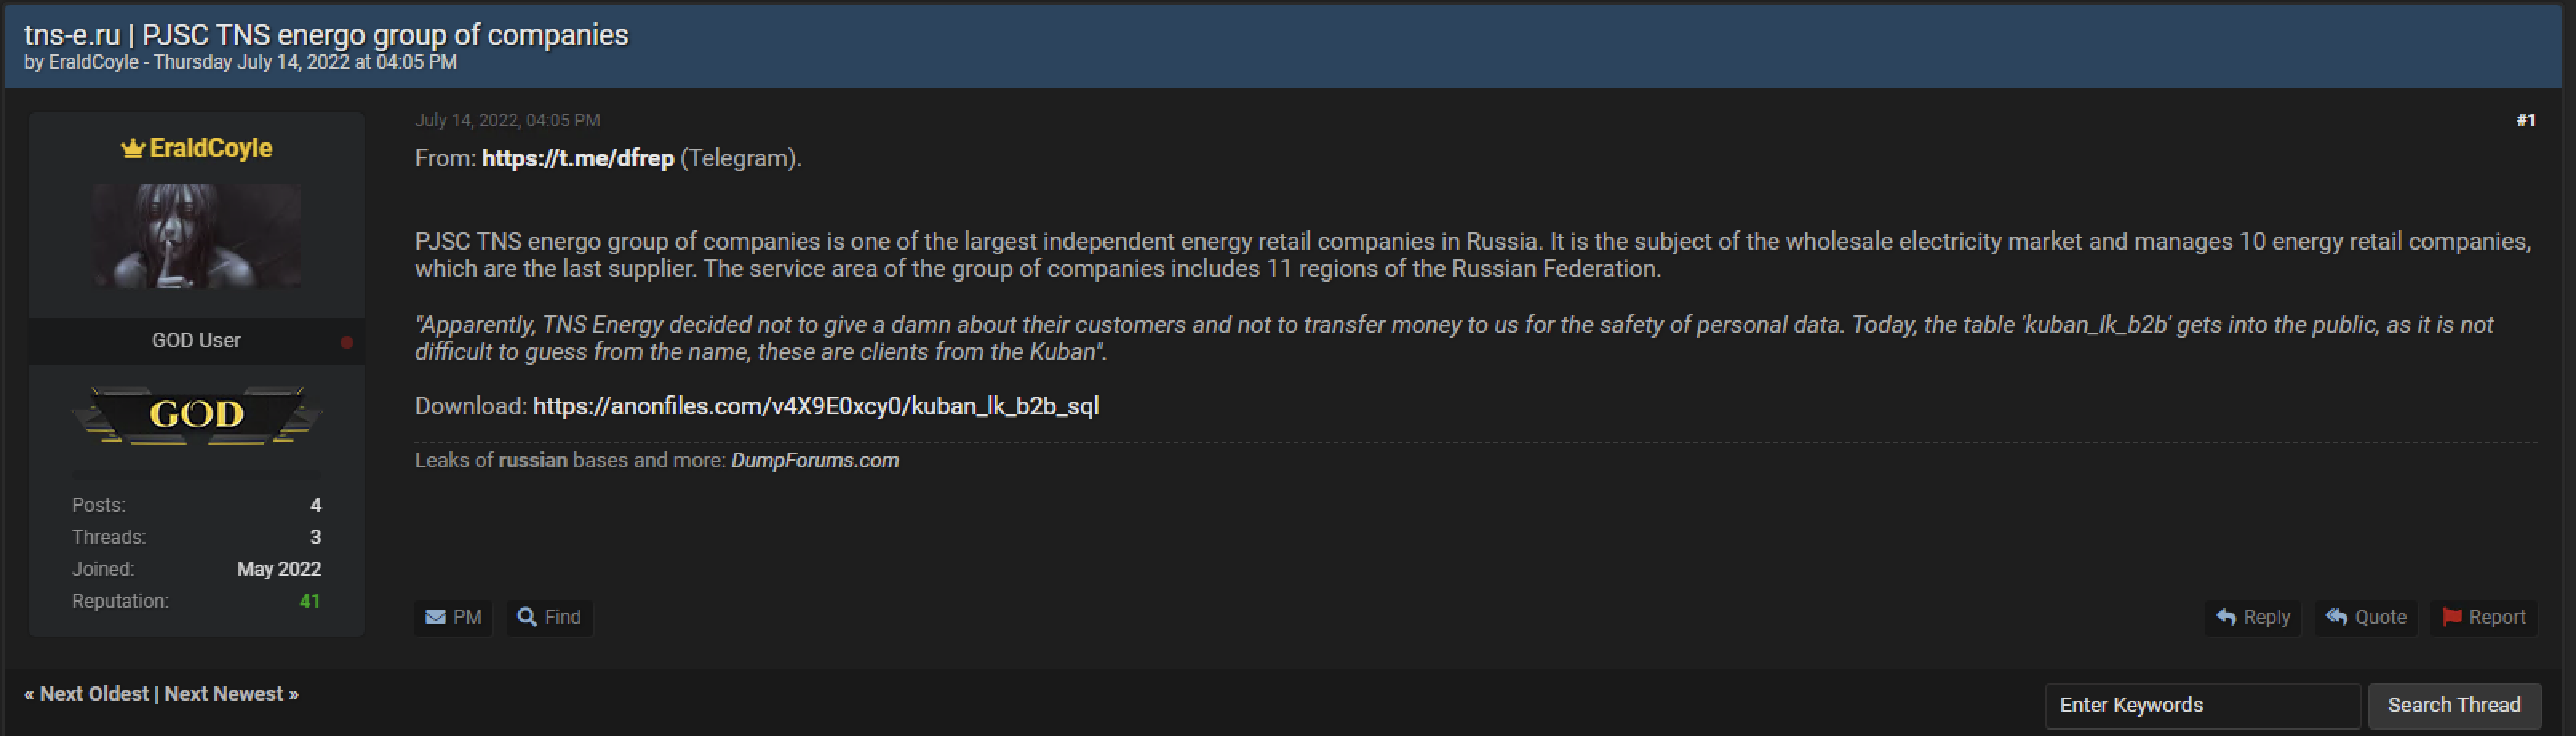
On July 14, 2022, a reputed threat actor "EraldCoyle" from the BreachForums posted a data breach package targeting TNS Energo Group, a company that provides electrical energy supply, operating from Russia. From this package, ZeroFox extracted 38,699 usernames and/or email addresses.
Standing Intelligence Requirements
For the most up to date list of ZeroFox Threat Research’s Intelligence Requirements, please visit:
https://cloud.zerofox.com/alpha_team/advisories/14956
Details
On July 14, 2022, a reputed threat actor "EraldCoyle" from the BreachForums posted a data breach package targeting TNS Energo Group (tns-e[.]ru), a company that provides electrical energy supply, operating from Russia. From this package, ZeroFox extracted 38,699 usernames and/or email addresses. Of this total, an assessed 36,721 records contained hashed passwords.
Recommendations
- If not already enabled, turn on the compromised credentials rule for all relevant entities and ensure relevant emails are entered for those entities, or reach out to [email protected] for assistance
- If one of your entities receives an alert, ZeroFox recommends immediate password changes for the affected account
- Enable 2-factor authentication for all of your organizational accounts to help mitigate phishing and credential stuffing attacks
Breach Disclosure: Pornminded
On July 11, 2022, a threat actor "Grafxxl" from the deep web forum BreachForums posted a data breach package targeting Pornminded, an escort services site operating from Sweden. From the package on BreachForums, ZeroFox extracted 28,439 email addresses and plain-text passwords.
Standing Intelligence Requirements
For the most up to date list of ZeroFox Threat Research’s Intelligence Requirements, please visit:
https://cloud.zerofox.com/alpha_team/advisories/14956
Details
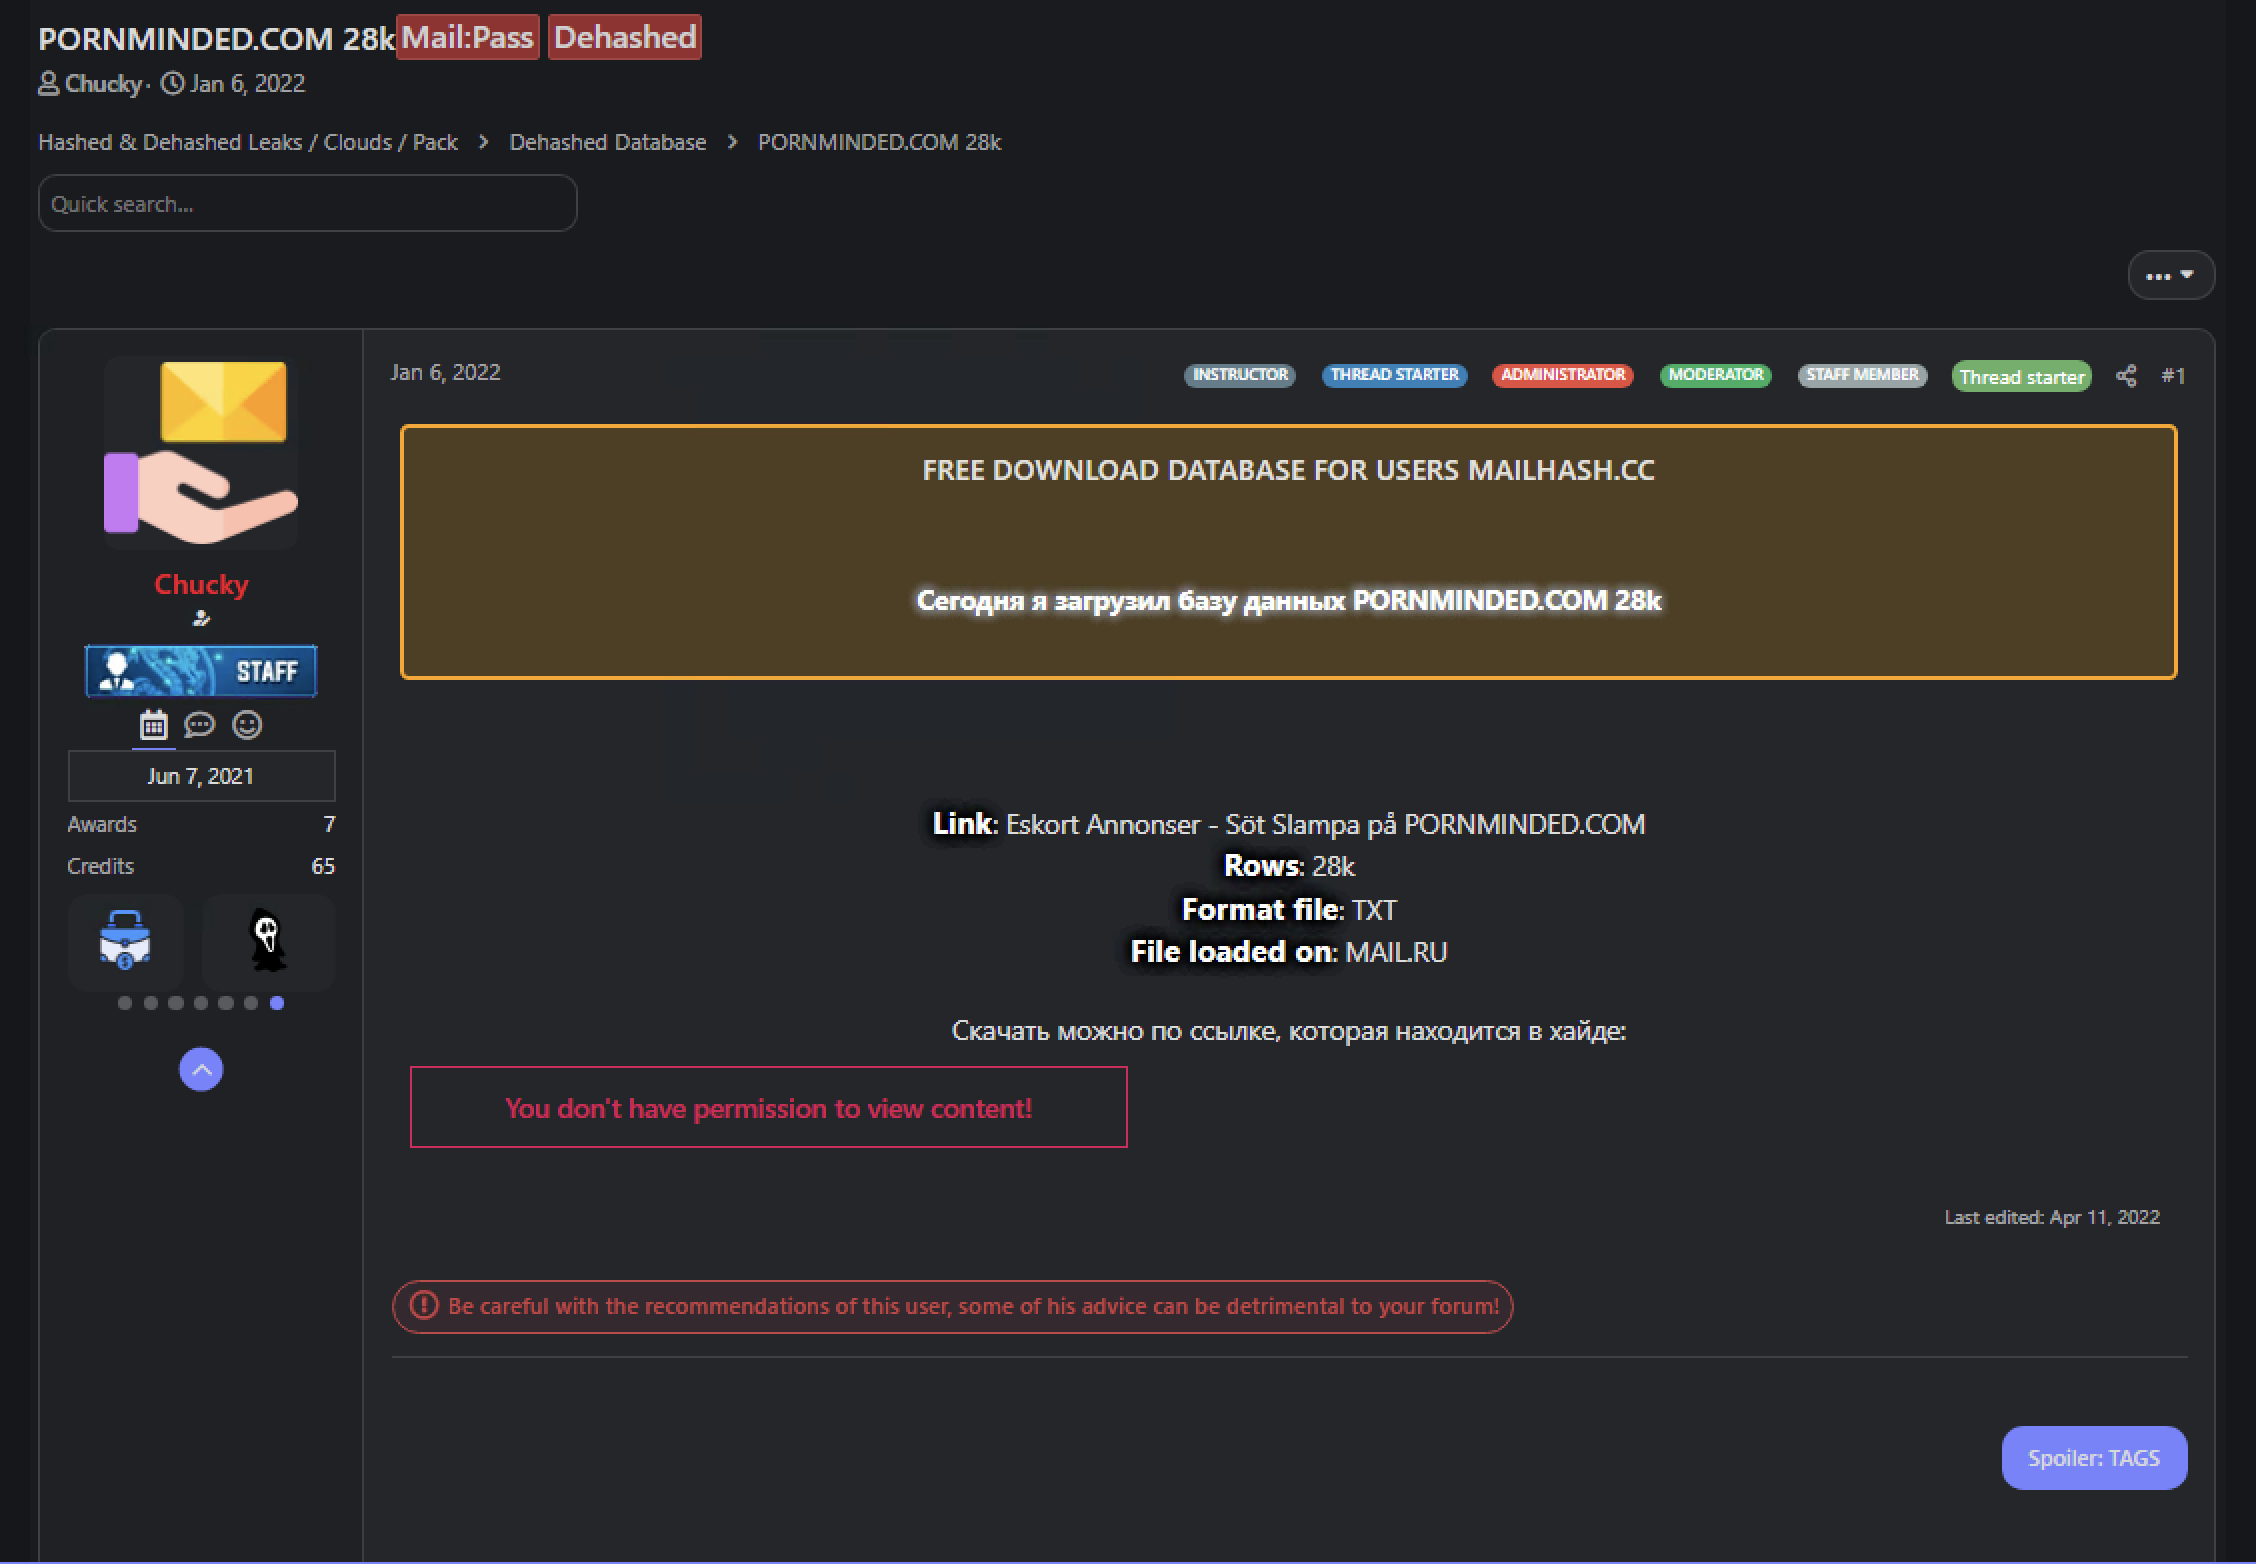
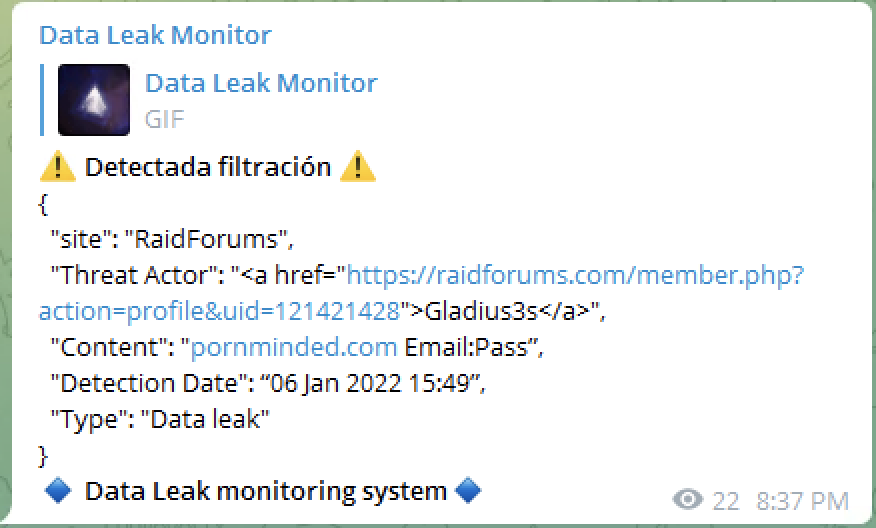
On July 11, 2022, a threat actor "Grafxxl" from the deep web forum BreachForums posted a data breach package targeting Pornminded, an escort services site operating from Sweden. The threat actor noted that the data dump includes 28K users' information. The data dump was also circulated in the deep web forums like Raid Forums on January 9, 2022 by the threat actor "johnhana", in Leakbase on January 6, 2022 by the threat actor "Chucky" and in a Telegram channel "Data Leak Monitor" on January 6, 2022. From the package on BreachForums, ZeroFox extracted 28,439 email addresses and plain-text passwords.
Recommendations
- If not already enabled, turn on the compromised credentials rule for all relevant entities and ensure relevant emails are entered for those entities, or reach out to [email protected] for assistance
- If one of your entities receives an alert, ZeroFox recommends immediate password changes for the affected account
- Enable 2-factor authentication for all of your organizational accounts to help mitigate phishing and credential stuffing attacks
Breach Disclosure: US Insurance Agents
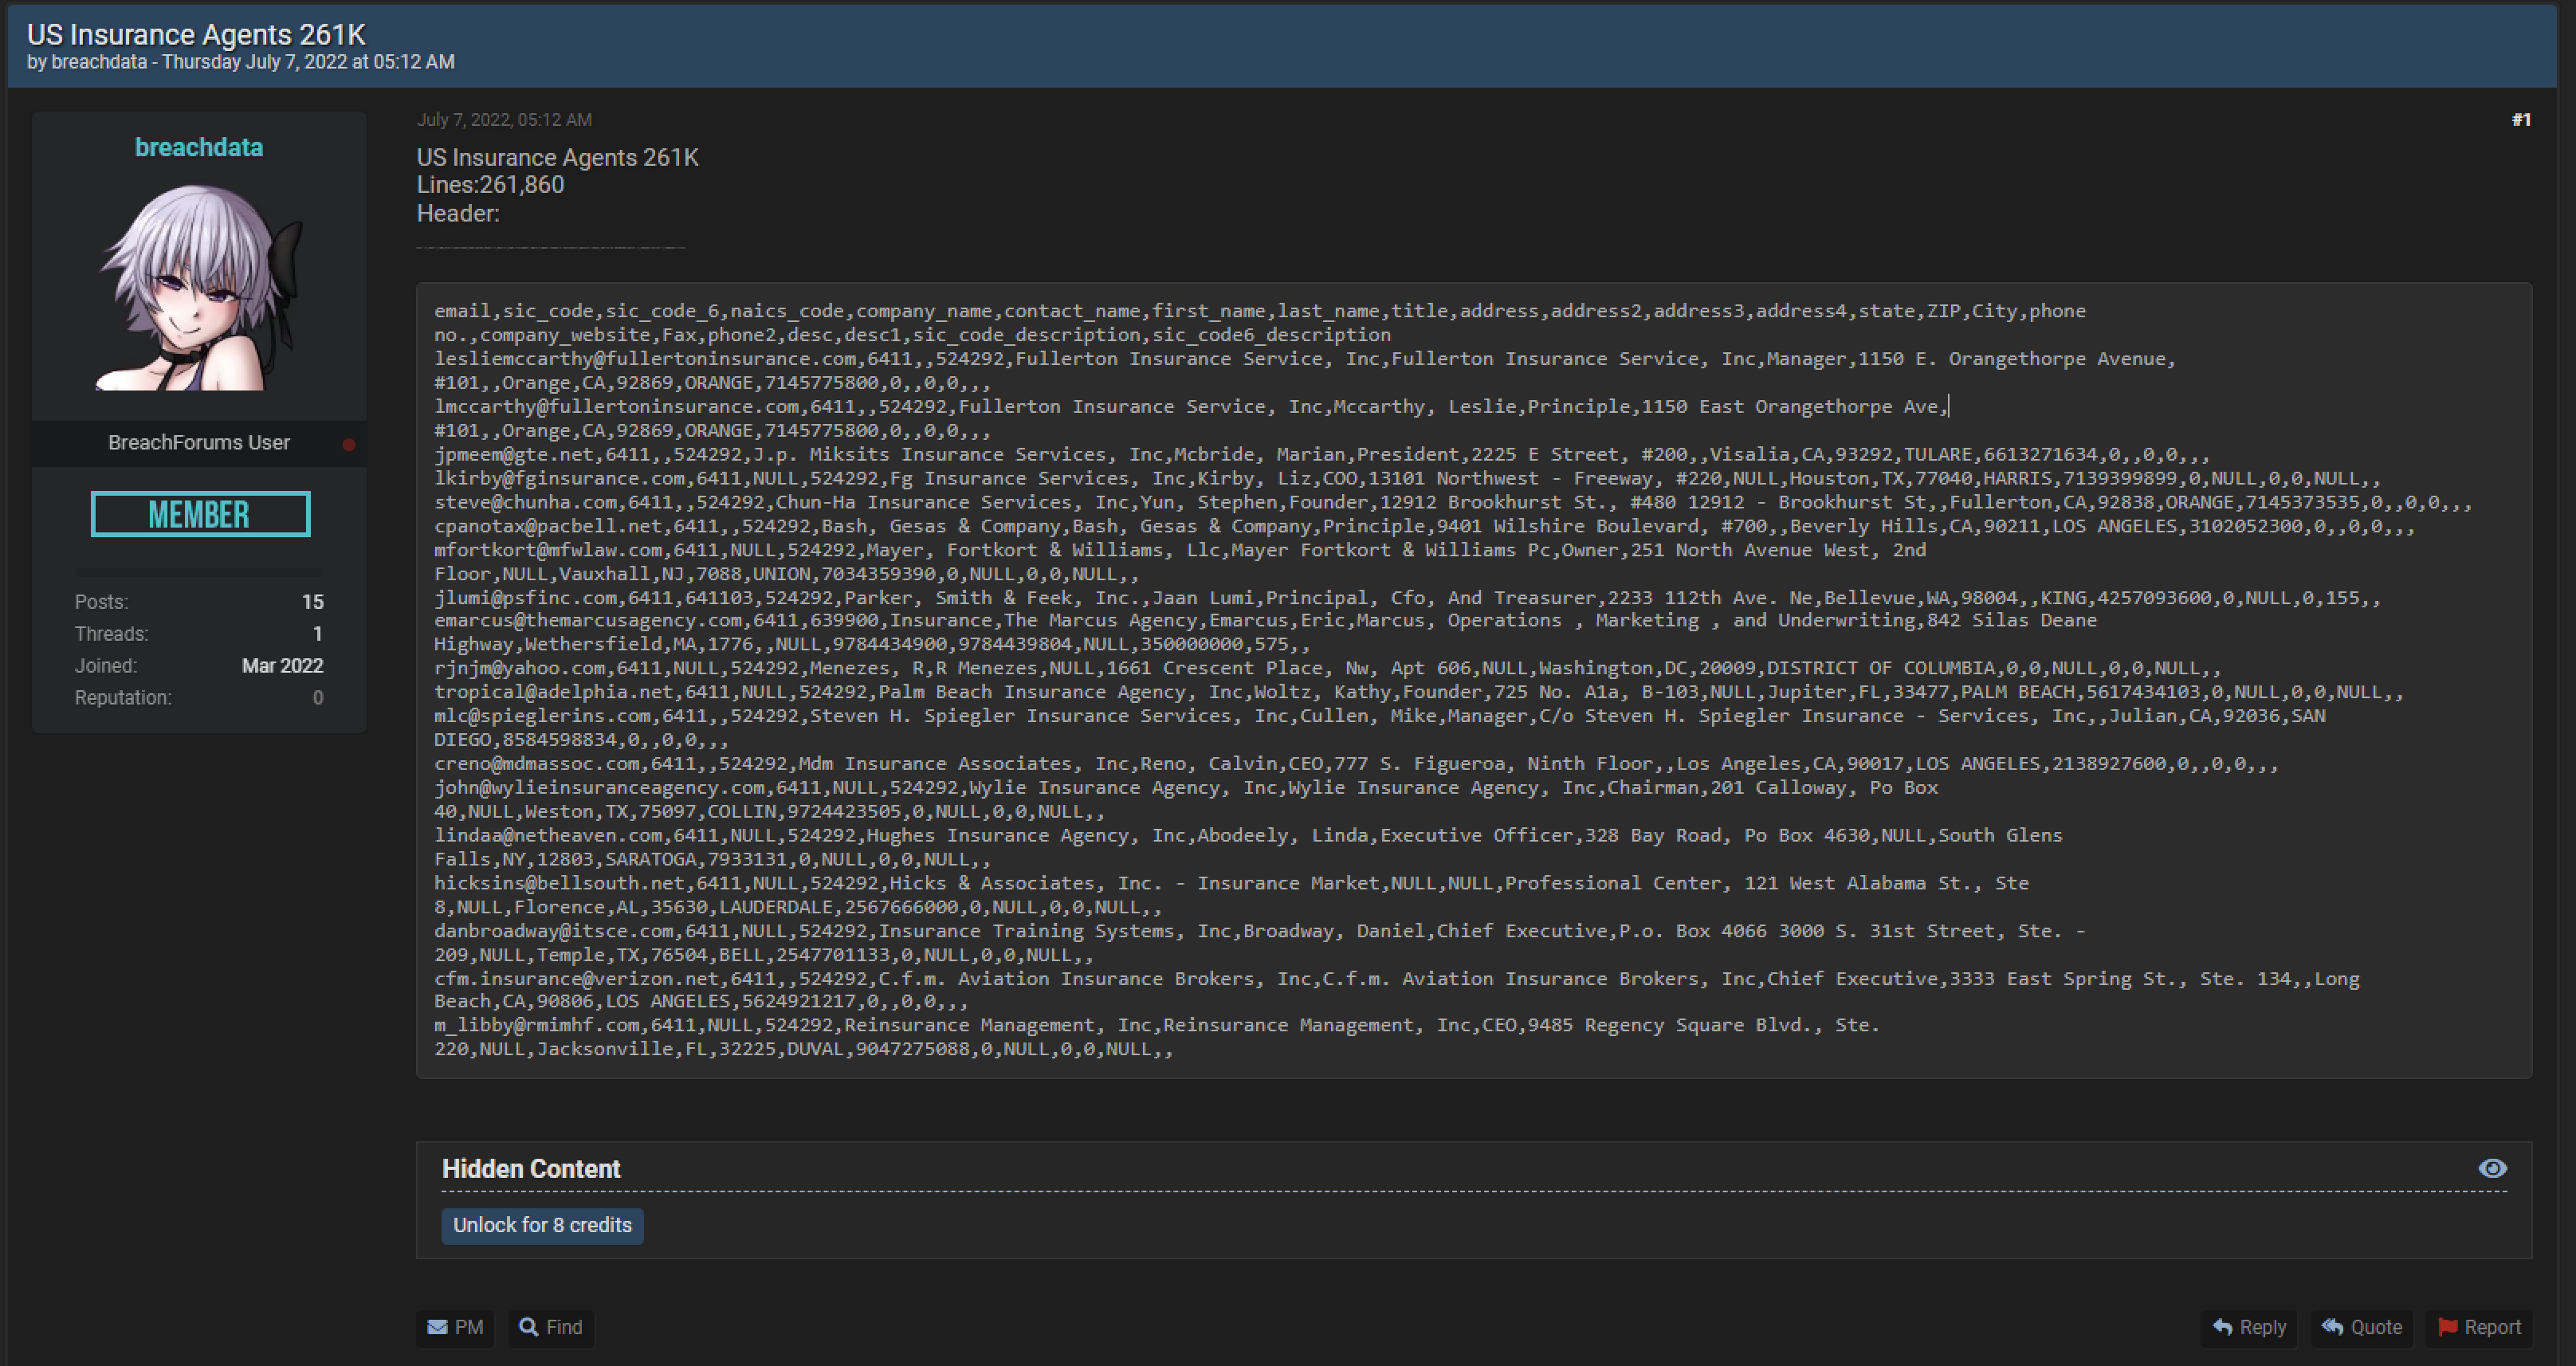
On July 7, 2022, a threat actor "breachdata" from the deep web forum BreachForums posted a data leak package titled "US Insurance Agents 261K". From this package, ZeroFox extracted 261,763 email addresses. No passwords were found in this breach.
Standing Intelligence Requirements
For the most up to date list of ZeroFox Threat Research’s Intelligence Requirements, please visit:
https://cloud.zerofox.com/alpha_team/advisories/14956
Details
On July 7, 2022, a threat actor "breachdata" from the deep web forum BreachForums posted a data leak package titled "US Insurance Agents 261K". The threat actor noted that the data dump includes 261,860 lines of US insurance agents' information. From this package, ZeroFox extracted 261,763 email addresses. No passwords were found in this breach.
Recommendations
- If not already enabled, turn on the compromised credentials rule for all relevant entities and ensure relevant emails are entered for those entities, or reach out to [email protected] for assistance
- If one of your entities receives an alert, ZeroFox recommends immediate password changes for the affected account
- Enable 2-factor authentication for all of your organizational accounts to help mitigate phishing and credential stuffing attacks
Breach Disclosure: US Debt Credit
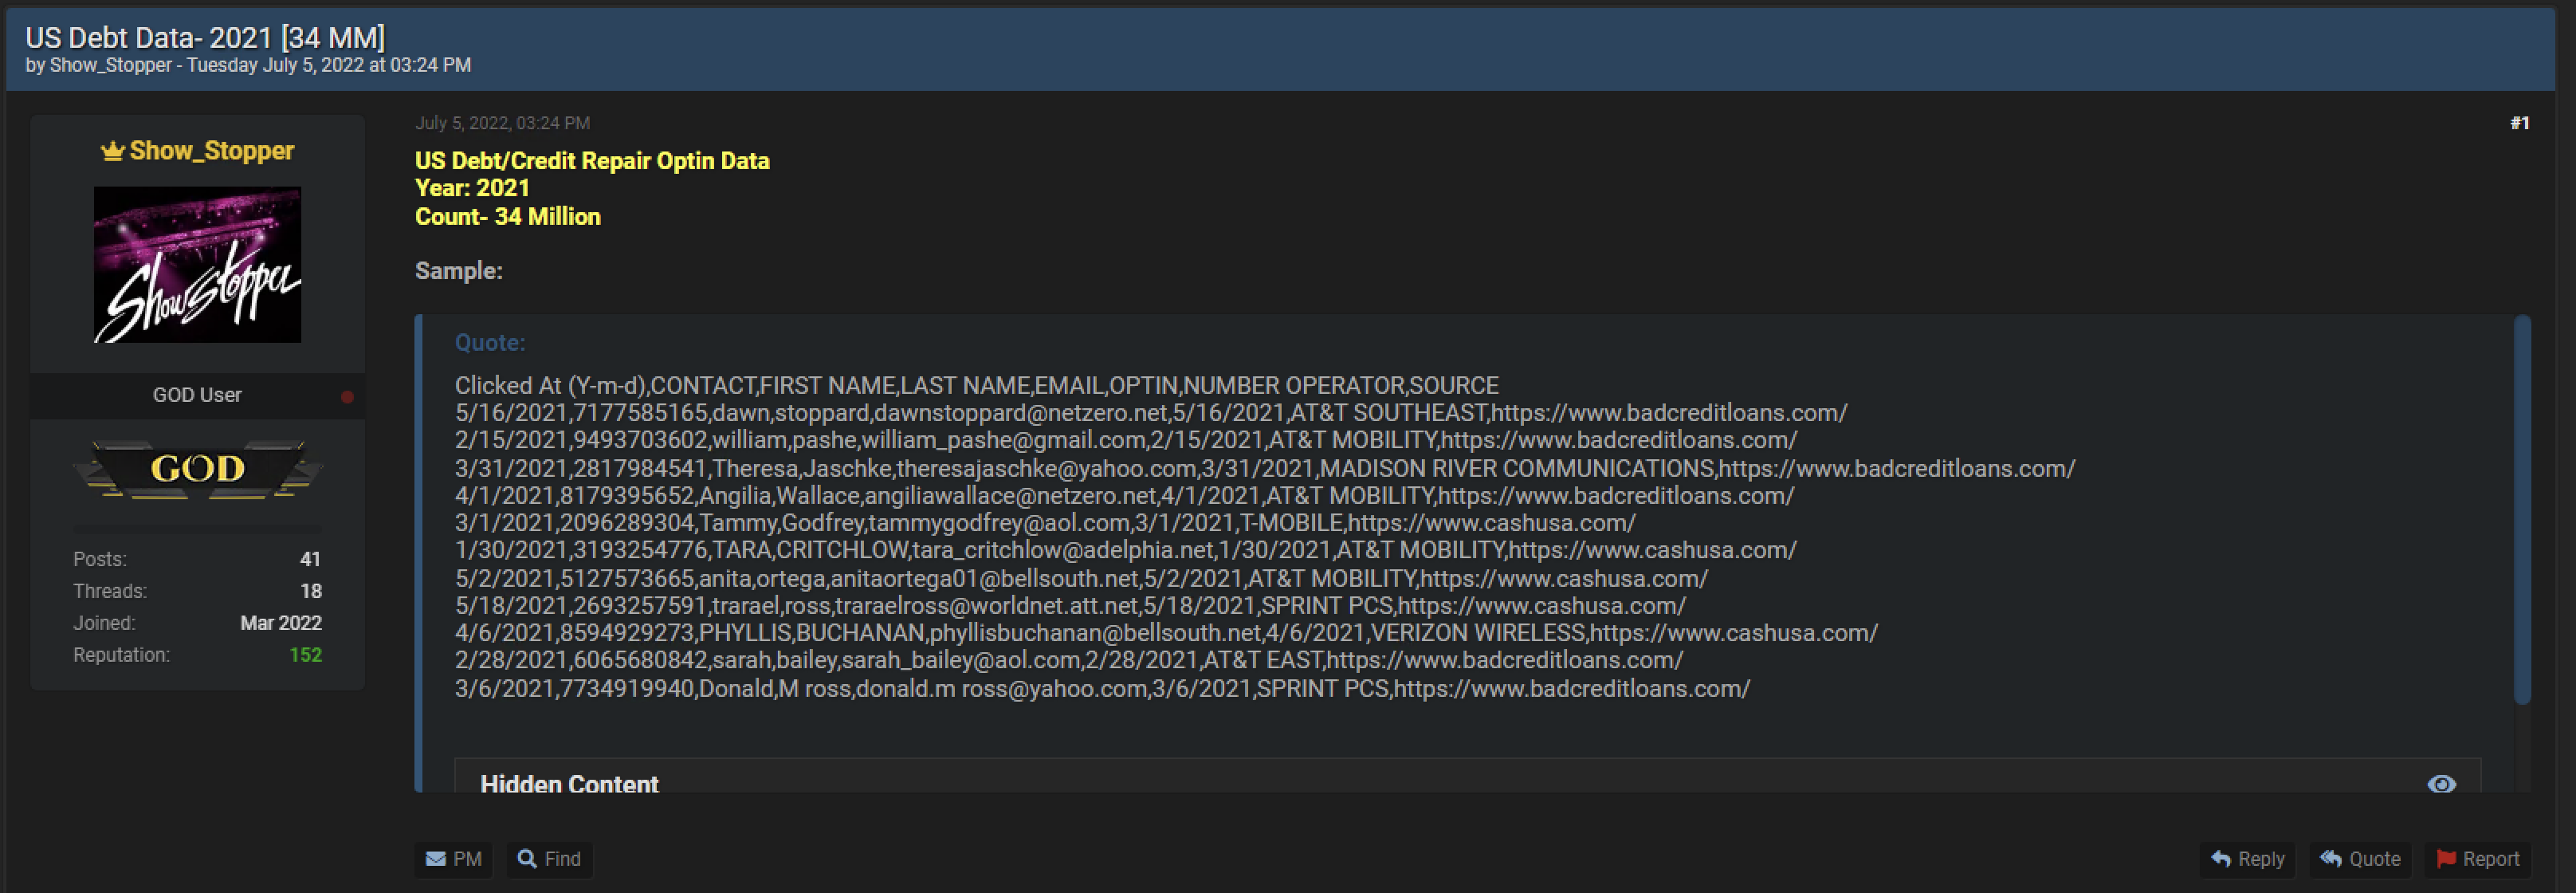
On July 5, 2022, a reputed threat actor "Show_Stopper" from the deep web forum BreachForums posted a data leak package titled "US Debt Data- 2021 [34 MM]". From this package, ZeroFox extracted 33,928,630 email addresses.
Standing Intelligence Requirements
For the most up to date list of ZeroFox Threat Research’s Intelligence Requirements, please visit:
https://cloud.zerofox.com/alpha_team/advisories/14956
Details
On July 5, 2022, a reputed threat actor "Show_Stopper" from the deep web forum BreachForums posted a data leak package titled "US Debt Data- 2021 [34 MM]". The threat actor noted that the data dump is from the year 2021 which includes 34 Million users' information. From this package, ZeroFox extracted 33,928,630 email addresses. No passwords were found in this breach.
Recommendations
- If not already enabled, turn on the compromised credentials rule for all relevant entities and ensure relevant emails are entered for those entities, or reach out to [email protected] for assistance
- If one of your entities receives an alert, ZeroFox recommends immediate password changes for the affected account
- Enable 2-factor authentication for all of your organizational accounts to help mitigate phishing and credential stuffing attacks
Breach Disclosure: Date Hot Brunettes
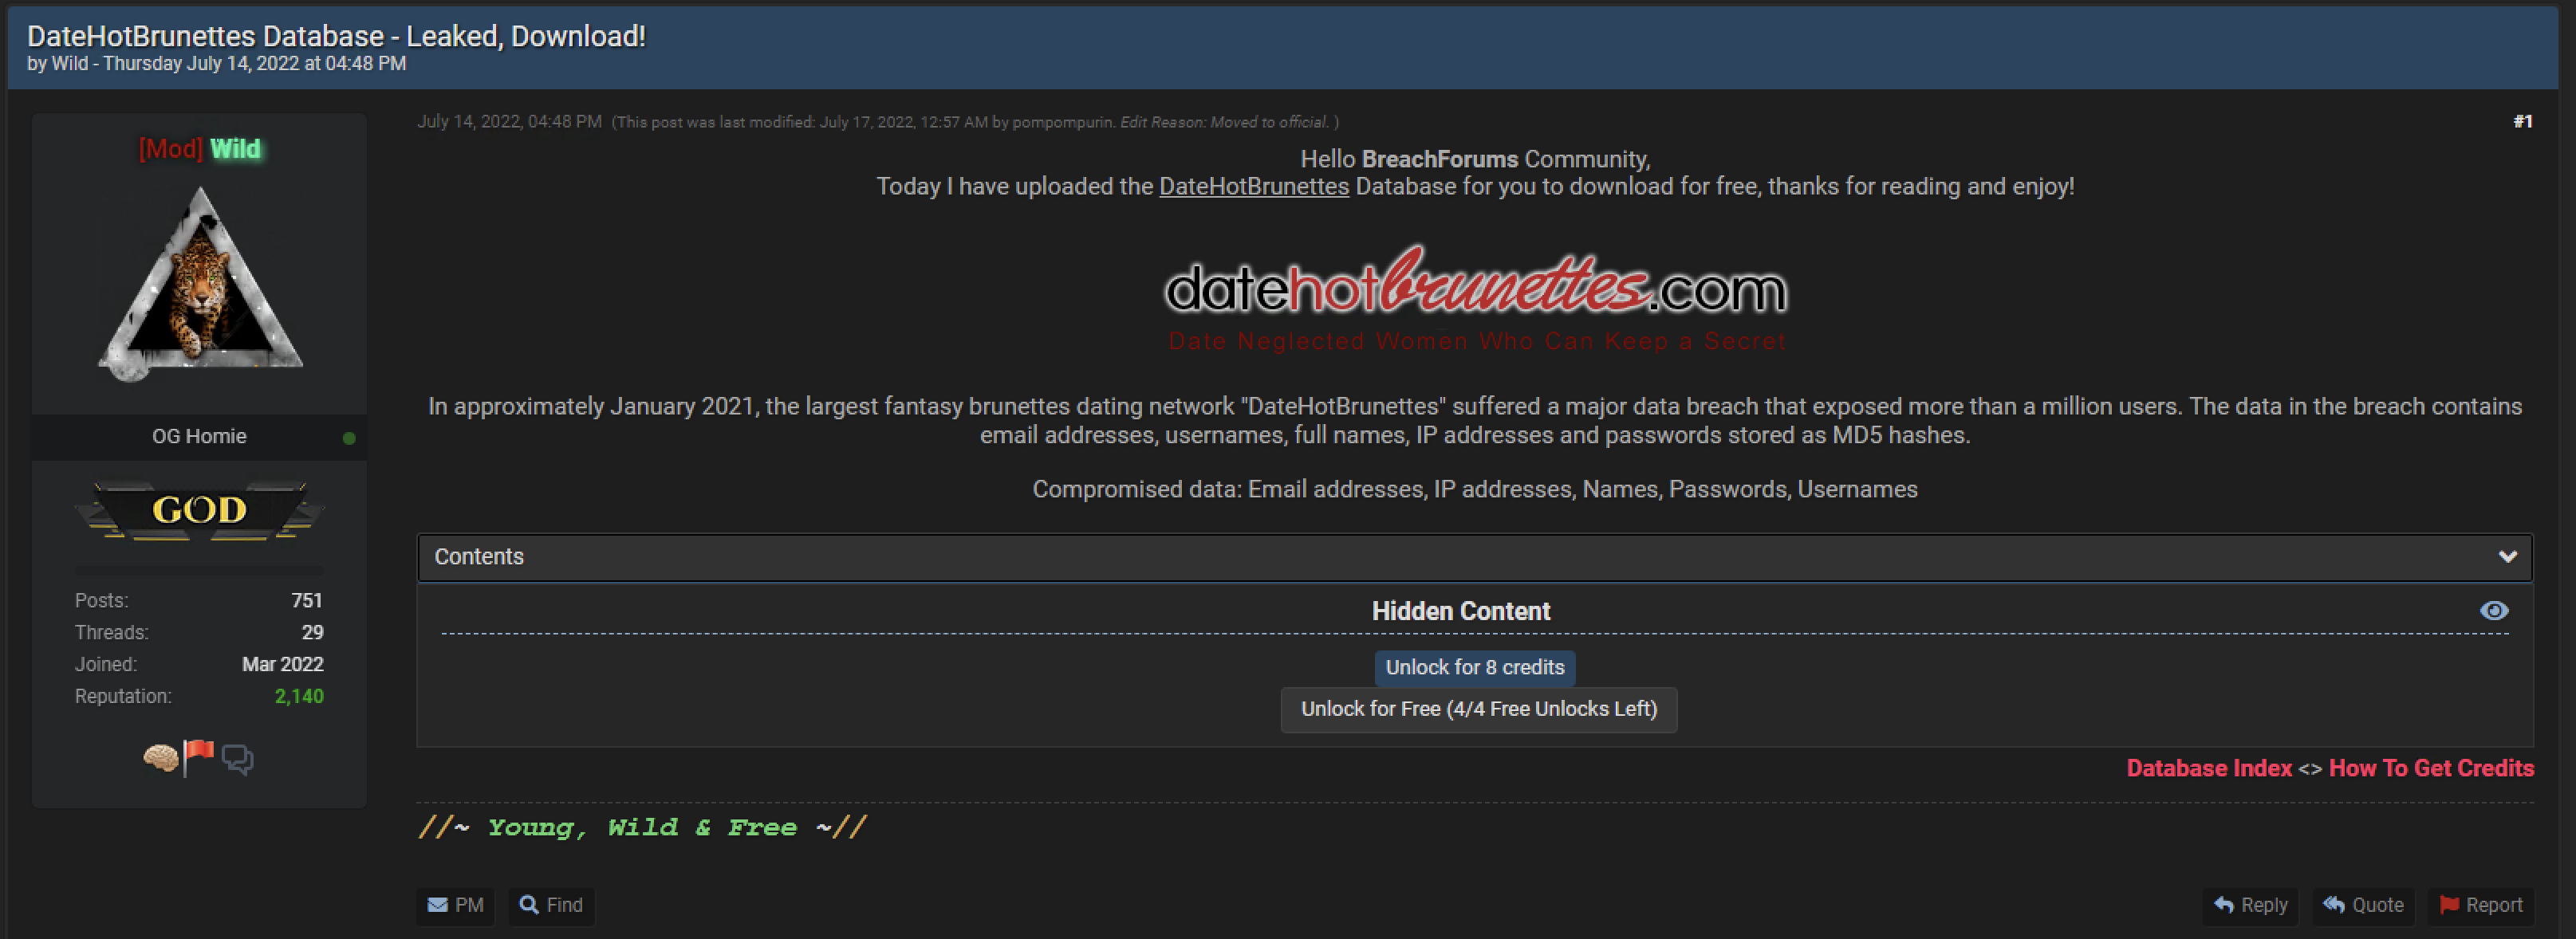
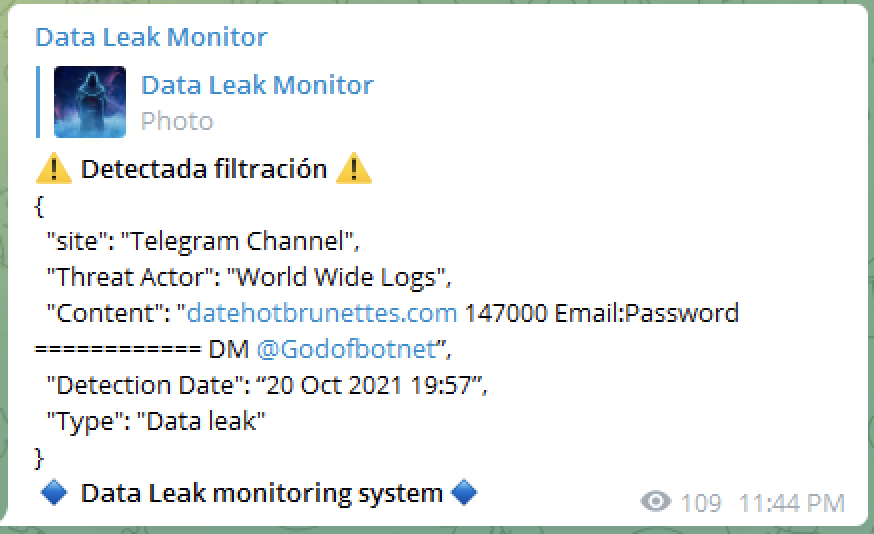
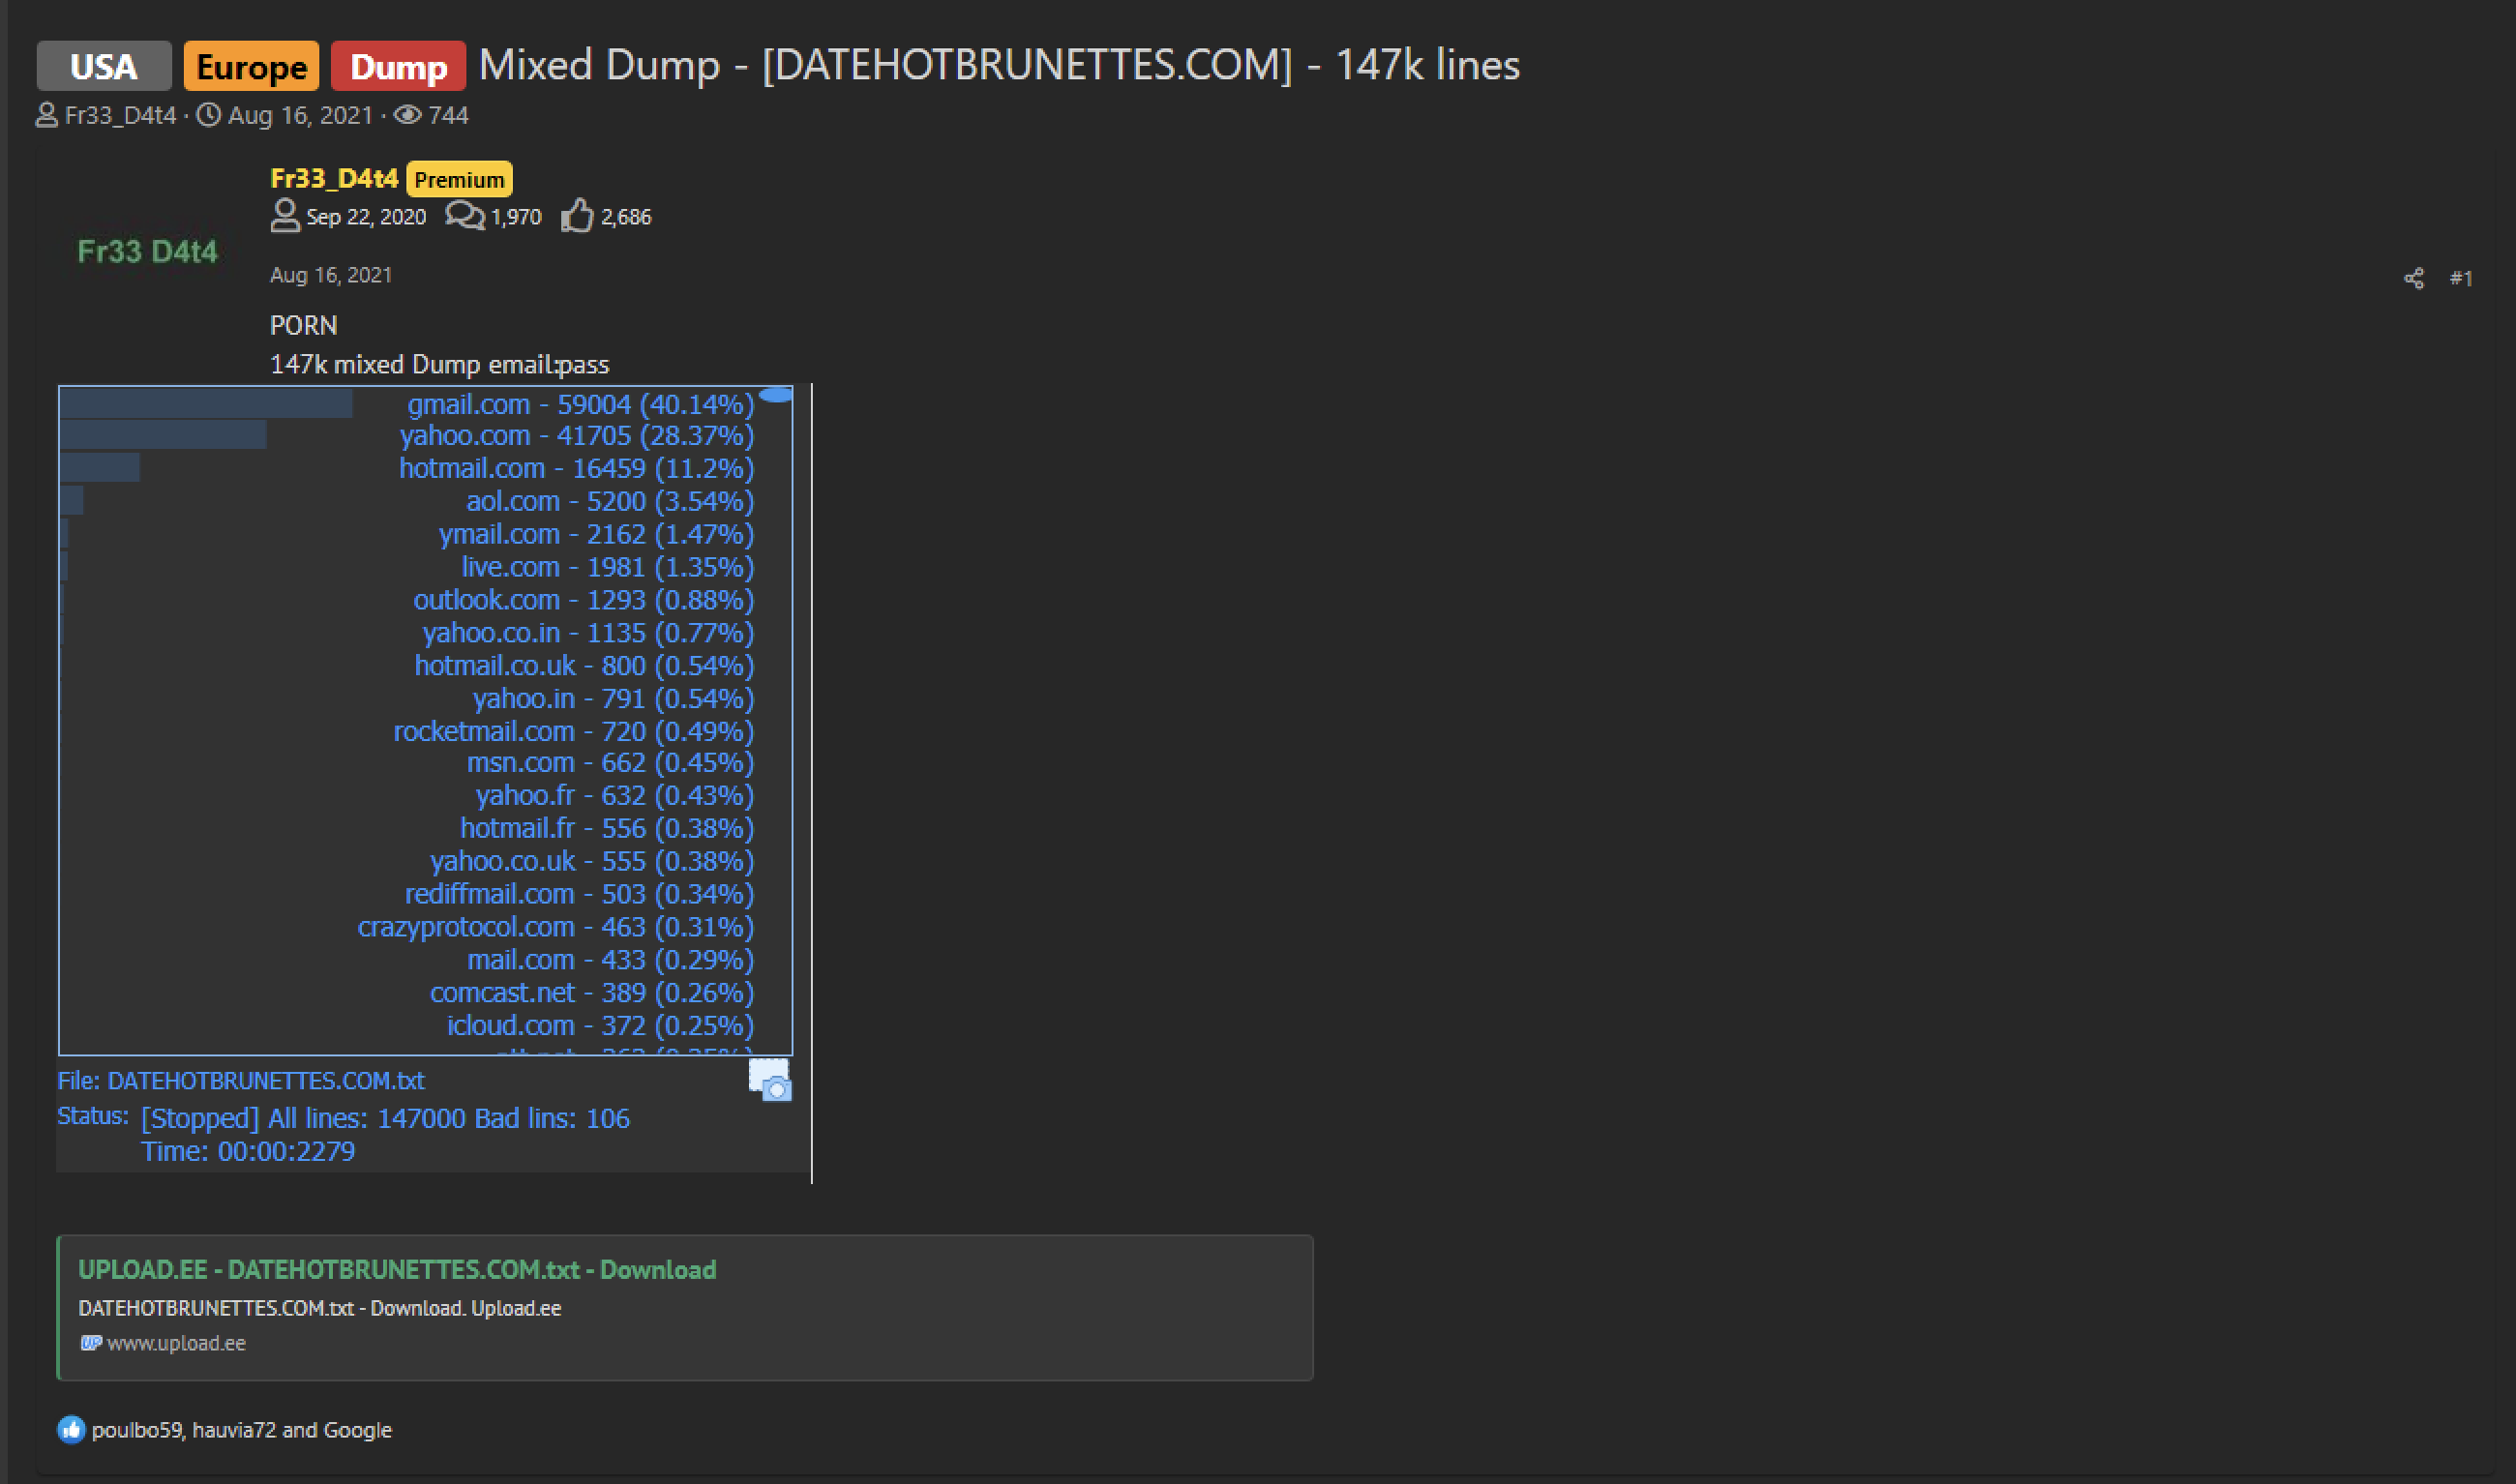
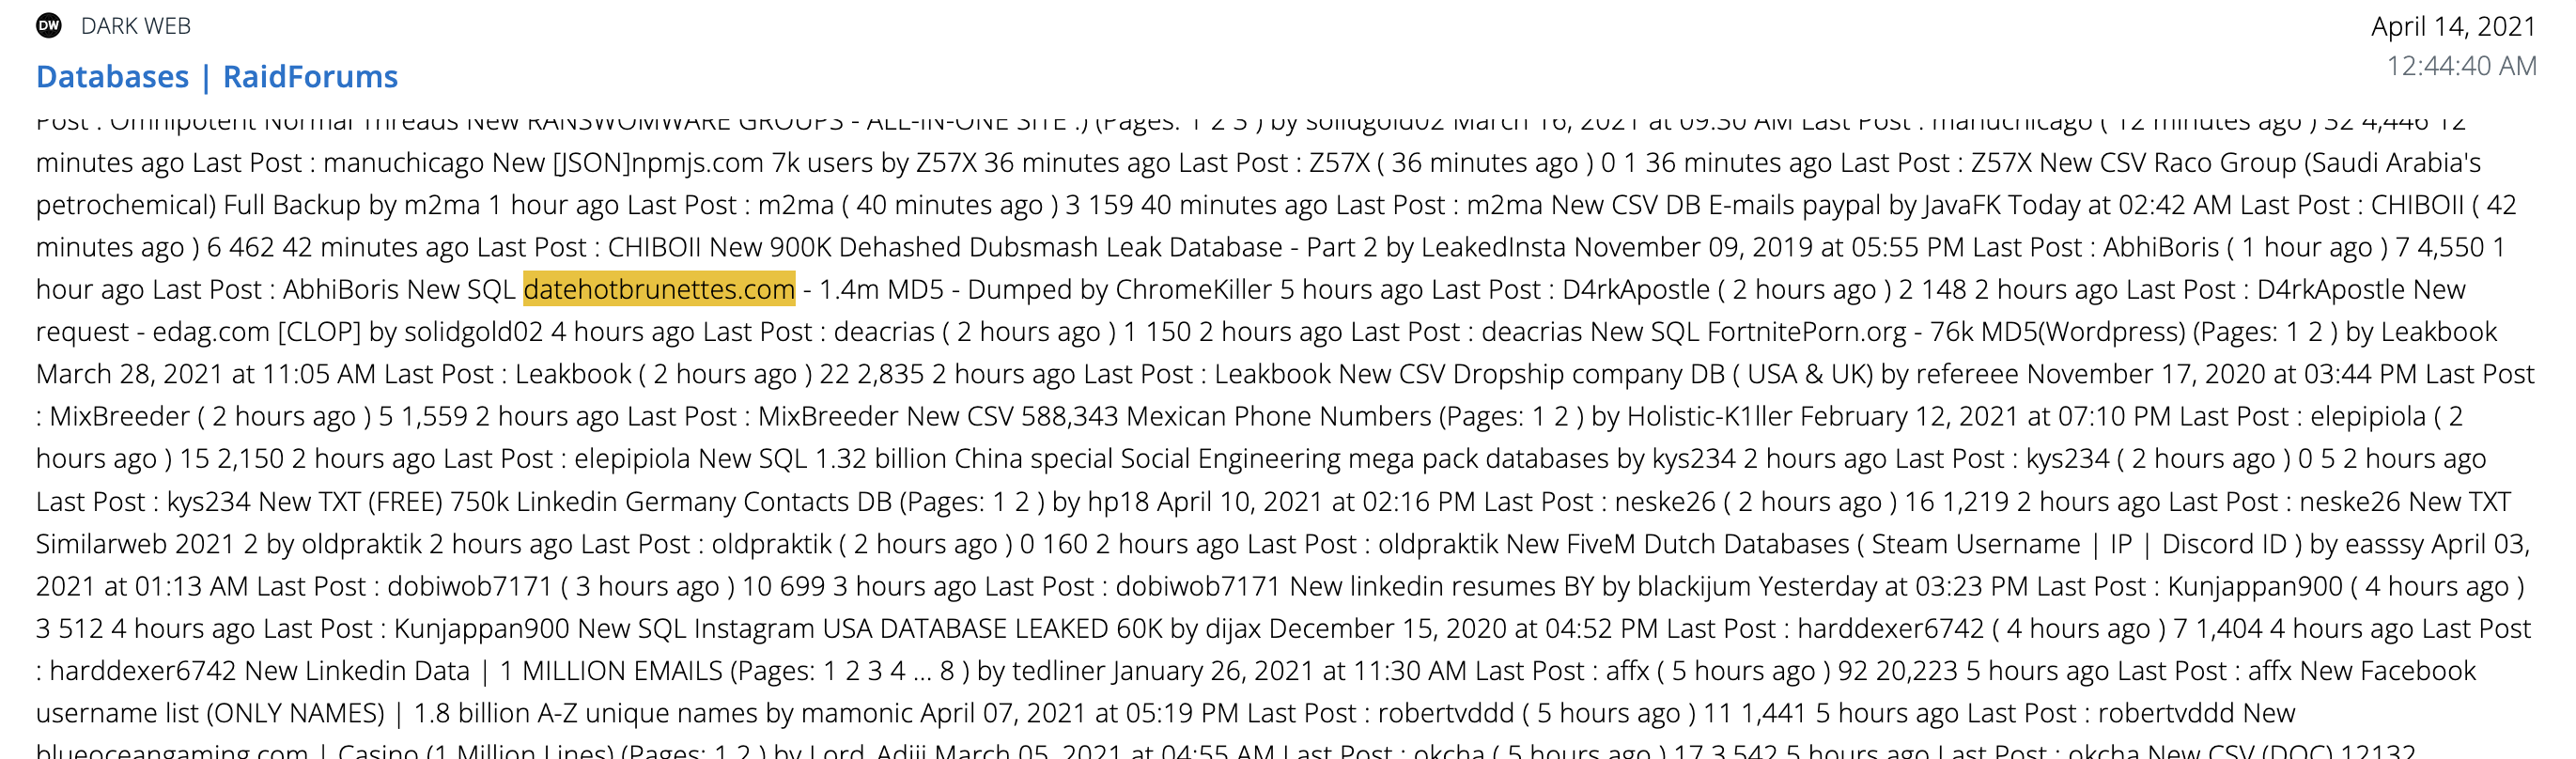
On July 14, 2022, a reputed threat actor "Wild" from the deep web forum BreachForums posted a data breach package targeting Date hot brunettes (datehotbrunettes[.]com), a dating site operating from United States. The threat actor noted that the data dump is from January 2021 which includes the user information with Email addresses, IP addresses, names, passwords, usernames. The data dump was also circulated in a Telegram channel "Data Leak Monitor" (hxxps[:]//t[.]me/breachdetector/7393) on October 20, 2021 and in the deep web forums like Leakbase on December 19, 2021 by the threat actor "Chucky", in NoHide on August 16, 2021 by the threat actor "Fr33_D4t4" and in Raid Forums on April 14, 2021. From the package on BreachForums, ZeroFox extracted 1,579,414 usernames, email addresses, and hashed passwords. Other compromised data fields of note in this package include: ip_address, first_name, last_name, gender, phone_number, and address.
Standing Intelligence Requirements
For the most up to date list of ZeroFox Threat Research’s Intelligence Requirements, please visit:
https://cloud.zerofox.com/alpha_team/advisories/14956
Details
On July 14, 2022, a reputed threat actor "Wild" from the deep web forum BreachForums posted a data breach package targeting Date Hot Brunettes, a dating site operating from United States. The threat actor noted that the data dump is from January 2021 which includes the user information with Email addresses, IP addresses, names, passwords, usernames. The data dump was also circulated in a Telegram channel "Data Leak Monitor" on October 20, 2021 and in the deep web forums like Leakbase on December 19, 2021 by the threat actor "Chucky", in NoHide on August 16, 2021 by the threat actor "Fr33_D4t4" and in Raid Forums on April 14, 2021. From the package on BreachForums, ZeroFox extracted 1,579,414 usernames, email addresses, and hashed passwords. Other compromised data fields of note in this package include: ip_address, first_name, last_name, gender, phone_number, and address.
Recommendations
- If not already enabled, turn on the compromised credentials rule for all relevant entities and ensure relevant emails are entered for those entities, or reach out to [email protected] for assistance
- If one of your entities receives an alert, ZeroFox recommends immediate password changes for the affected account
- Enable 2-factor authentication for all of your organizational accounts to help mitigate phishing and credential stuffing attacks
Breach Disclosure: Youthmanual
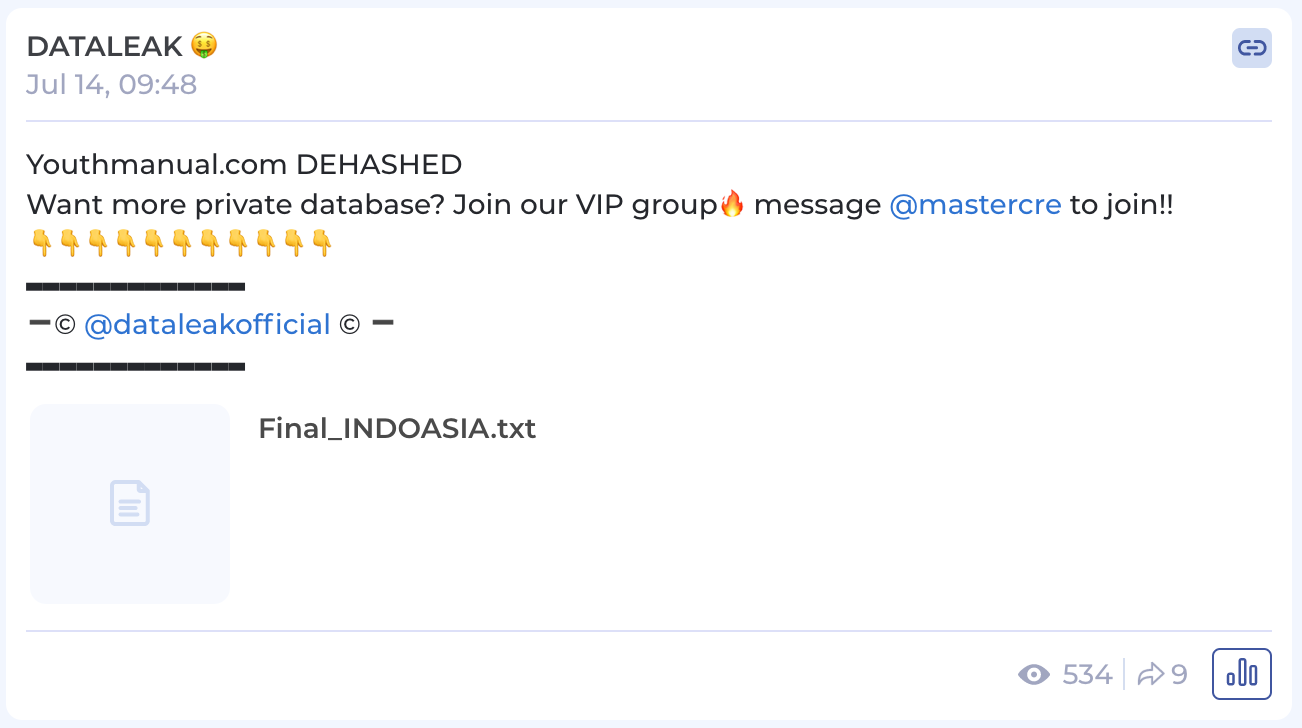
On July 14, 2022, the Telegram Channel "Dataleak" posted a data breach package targeting Youthmanual, a college and career readiness platform guides senior high school students to designing their future operating from Indonesia. From this package, ZeroFox extracted 479,512 email addresses and plain-text passwords.
Standing Intelligence Requirements
For the most up to date list of ZeroFox Threat Research’s Intelligence Requirements, please visit:
https://cloud.zerofox.com/alpha_team/advisories/14956
Details
On July 14, 2022, the Telegram Channel "Dataleak" (@dataleakofficial) posted a data breach package targeting Youthmanual (youthmanual[.]com), a college and career readiness platform guides senior high school students to designing their future operating from Indonesia. From this package, ZeroFox extracted 479,512 email addresses and plain-text passwords.
Recommendations
- If not already enabled, turn on the compromised credentials rule for all relevant entities and ensure relevant emails are entered for those entities, or reach out to [email protected] for assistance
- If one of your entities receives an alert, ZeroFox recommends immediate password changes for the affected account
- Enable 2-factor authentication for all of your organizational accounts to help mitigate phishing and credential stuffing attacks
Breach Disclosure: Foodco
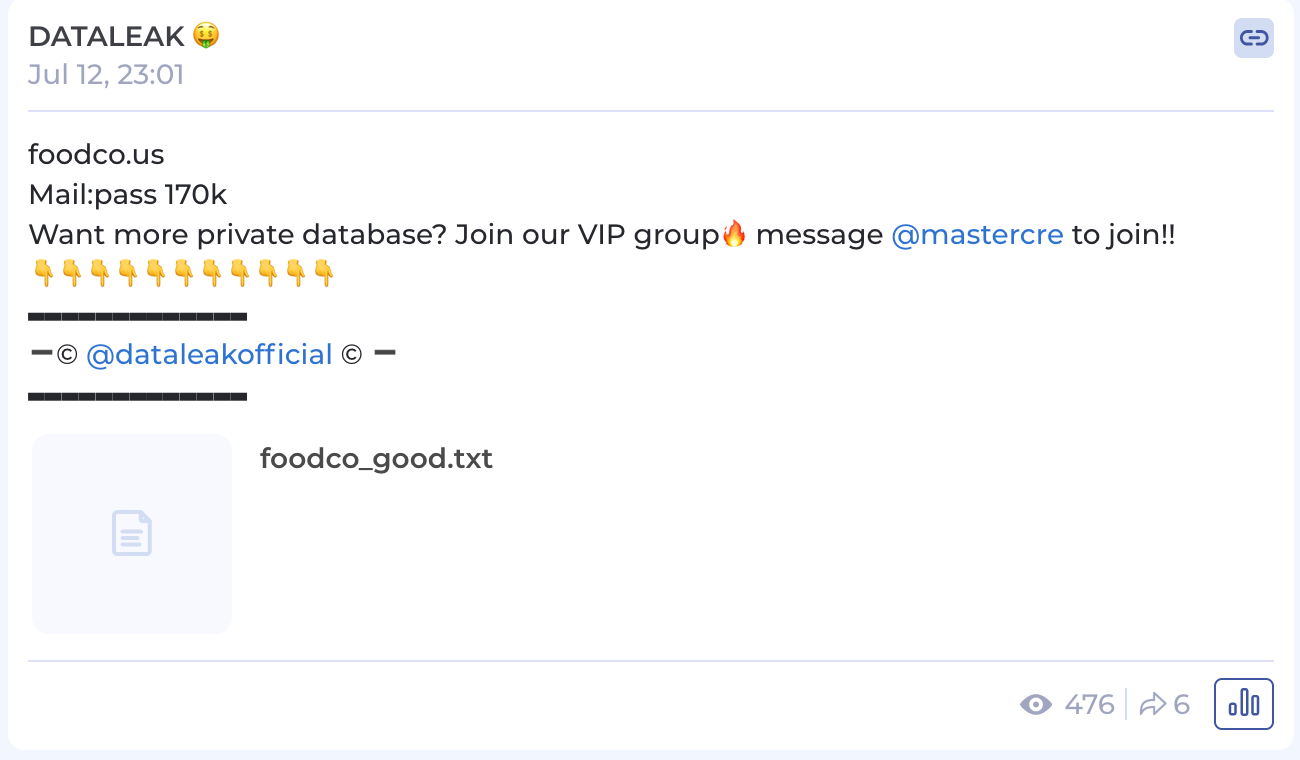
On July 12, 2022, the Telegram Channel "Dataleak" posted a data breach package targeting Foodco, a US-based back-office management program which is used for manage food service operations. From the package published in "Dataleak" Telegram channel , ZeroFox extracted 152,569 email addresses and plain-text passwords.
Standing Intelligence Requirements
For the most up to date list of ZeroFox Threat Research’s Intelligence Requirements, please visit:
https://cloud.zerofox.com/alpha_team/advisories/14956
Details
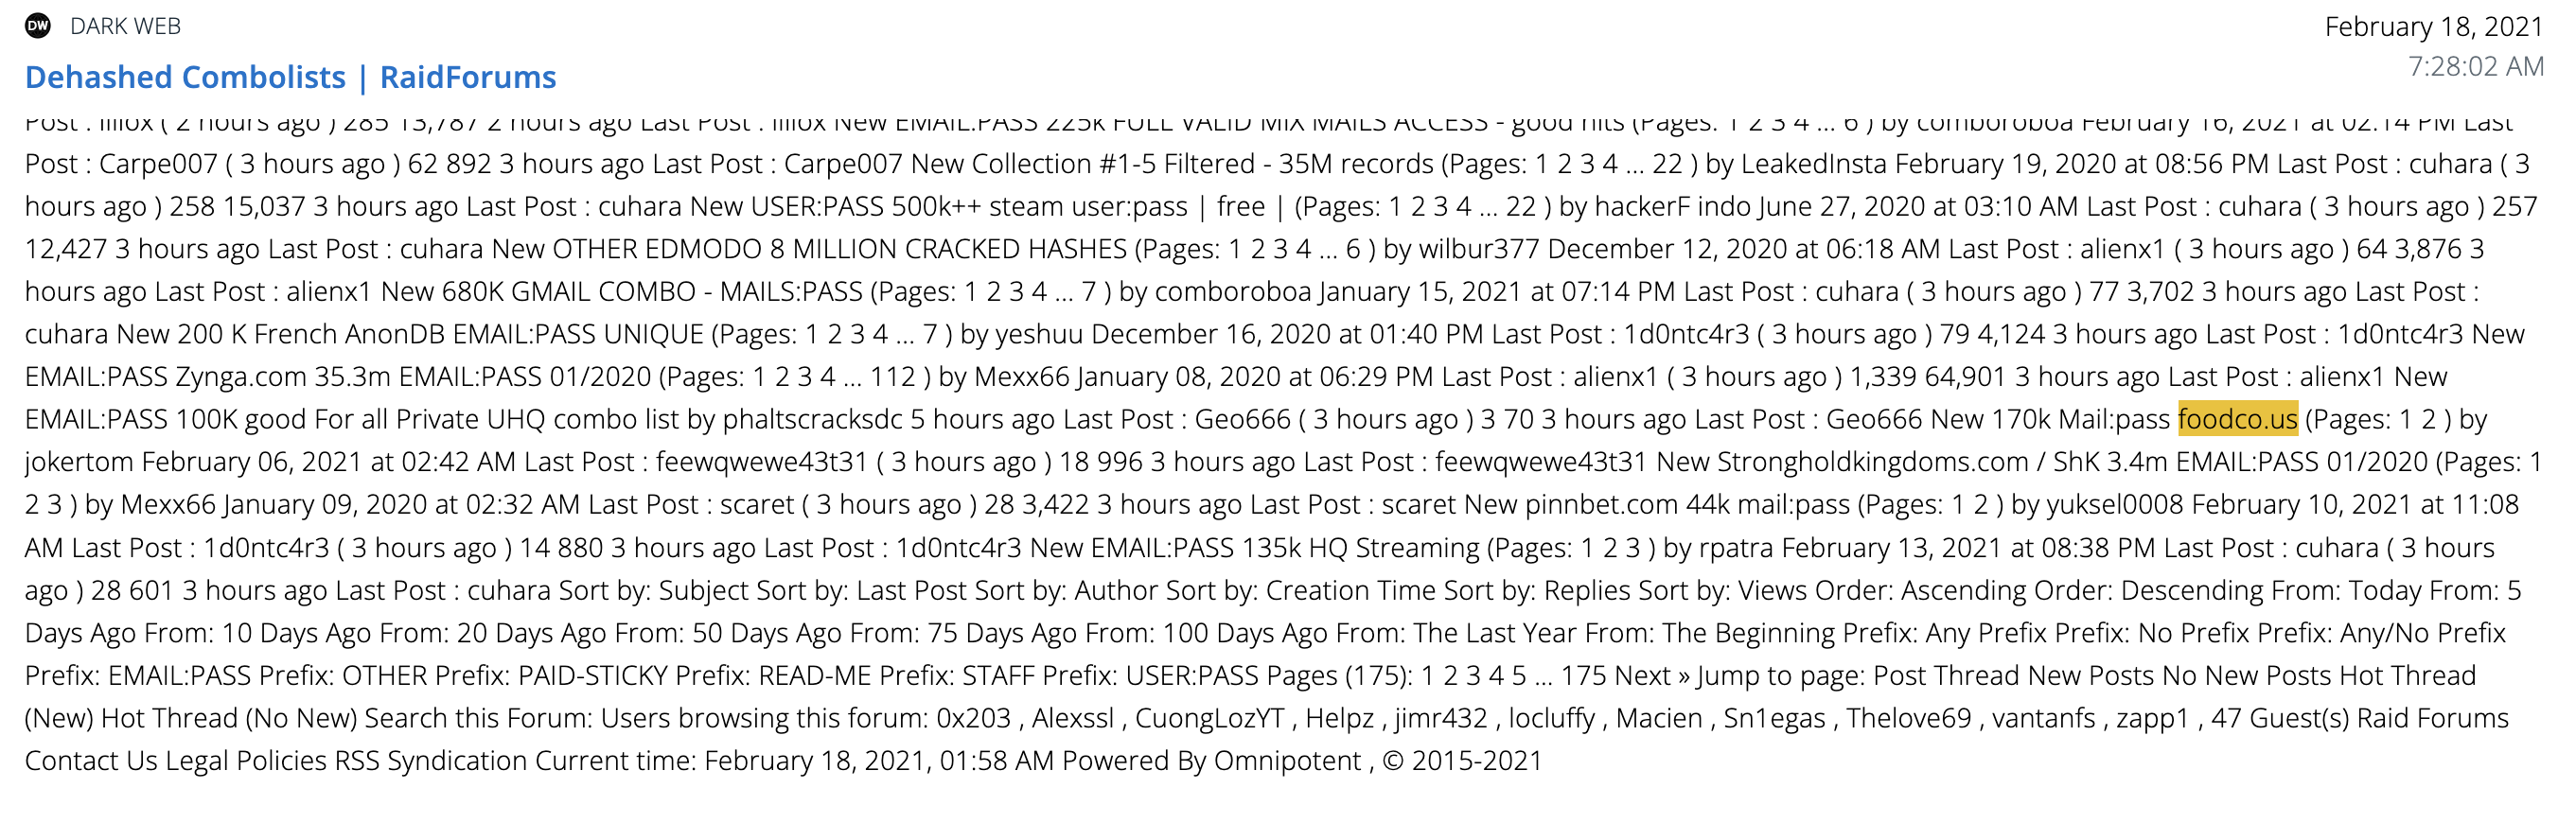
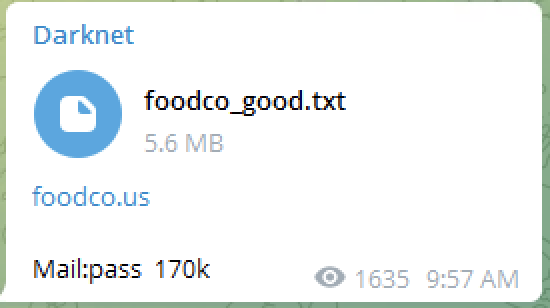
On July 12, 2022, the Telegram Channel "Dataleak" posted a data breach package targeting Foodco, a US-based back-office management program which is used for manage food service operations. The data dump was also circulated in Raid Forums on February 18, 2021 and also in a Telegram Channel "Darknet" (hxxps[:]//t[.]me/dbforall/92) on February 7, 2021. From the package published in "Dataleak" Telegram channel , ZeroFox extracted 152,569 email addresses and plain-text passwords.
Recommendations
- If not already enabled, turn on the compromised credentials rule for all relevant entities and ensure relevant emails are entered for those entities, or reach out to [email protected] for assistance
- If one of your entities receives an alert, ZeroFox recommends immediate password changes for the affected account
- Enable 2-factor authentication for all of your organizational accounts to help mitigate phishing and credential stuffing attacks
Breach Disclosure: Playstore Devs
On July 7, 2022, a reputed threat actor "Topazzz" from the Russian language deep web forum XSS posted a data leak package titled "Playstore_devs". From this package, ZeroFox extracted 276,810 email addresses.
Standing Intelligence Requirements
For the most up to date list of ZeroFox Threat Research’s Intelligence Requirements, please visit:
https://cloud.zerofox.com/alpha_team/advisories/14956
Details
On July 7, 2022, a reputed threat actor "Topazzz" from the Russian language deep web forum XSS posted a data leak package titled "Playstore_devs". From this package, ZeroFox extracted 276,810 email addresses. No passwords were found in this breach.
Recommendations
- If not already enabled, turn on the compromised credentials rule for all relevant entities and ensure relevant emails are entered for those entities, or reach out to [email protected] for assistance
- If one of your entities receives an alert, ZeroFox recommends immediate password changes for the affected account
- Enable 2-factor authentication for all of your organizational accounts to help mitigate phishing and credential stuffing attacks
Breach Disclosure: MemeChat
On July 5, 2022, a reputed threat actor "All3in" from the BreachForums posted a data breach package targeting MemeChat, an Indian-based online money earning app through competing with meme creators. From the package published in BreachForums, ZeroFox extracted 4,330,769 usernames and email addresses.
Standing Intelligence Requirements
For the most up to date list of ZeroFox Threat Research’s Intelligence Requirements, please visit:
https://cloud.zerofox.com/alpha_team/advisories/14956
Details
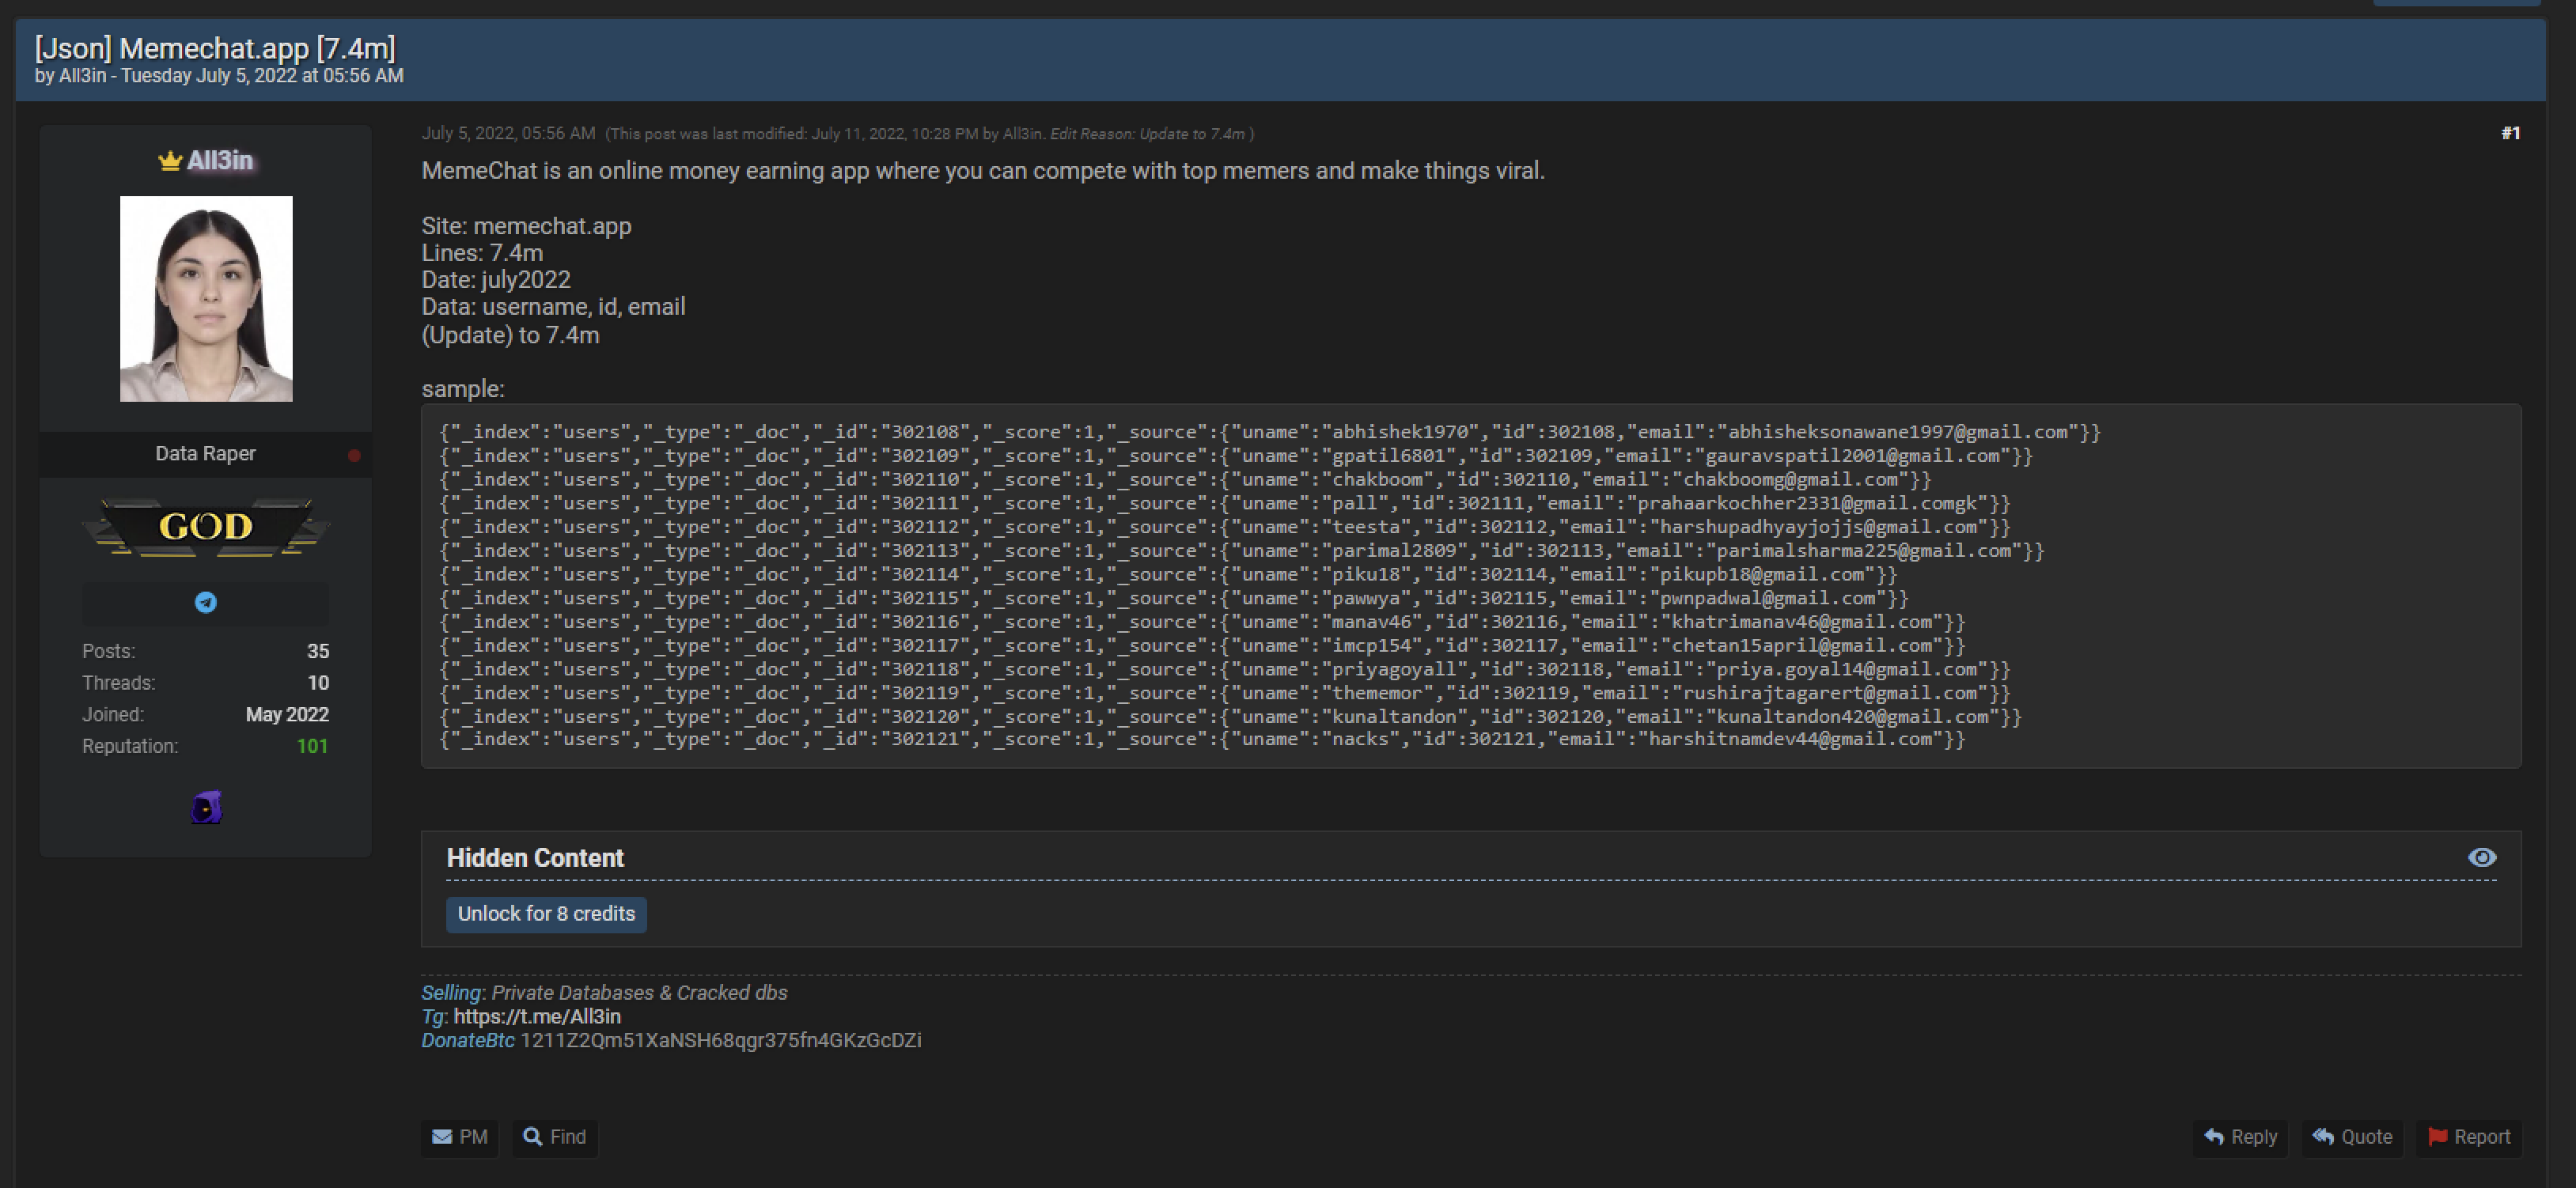
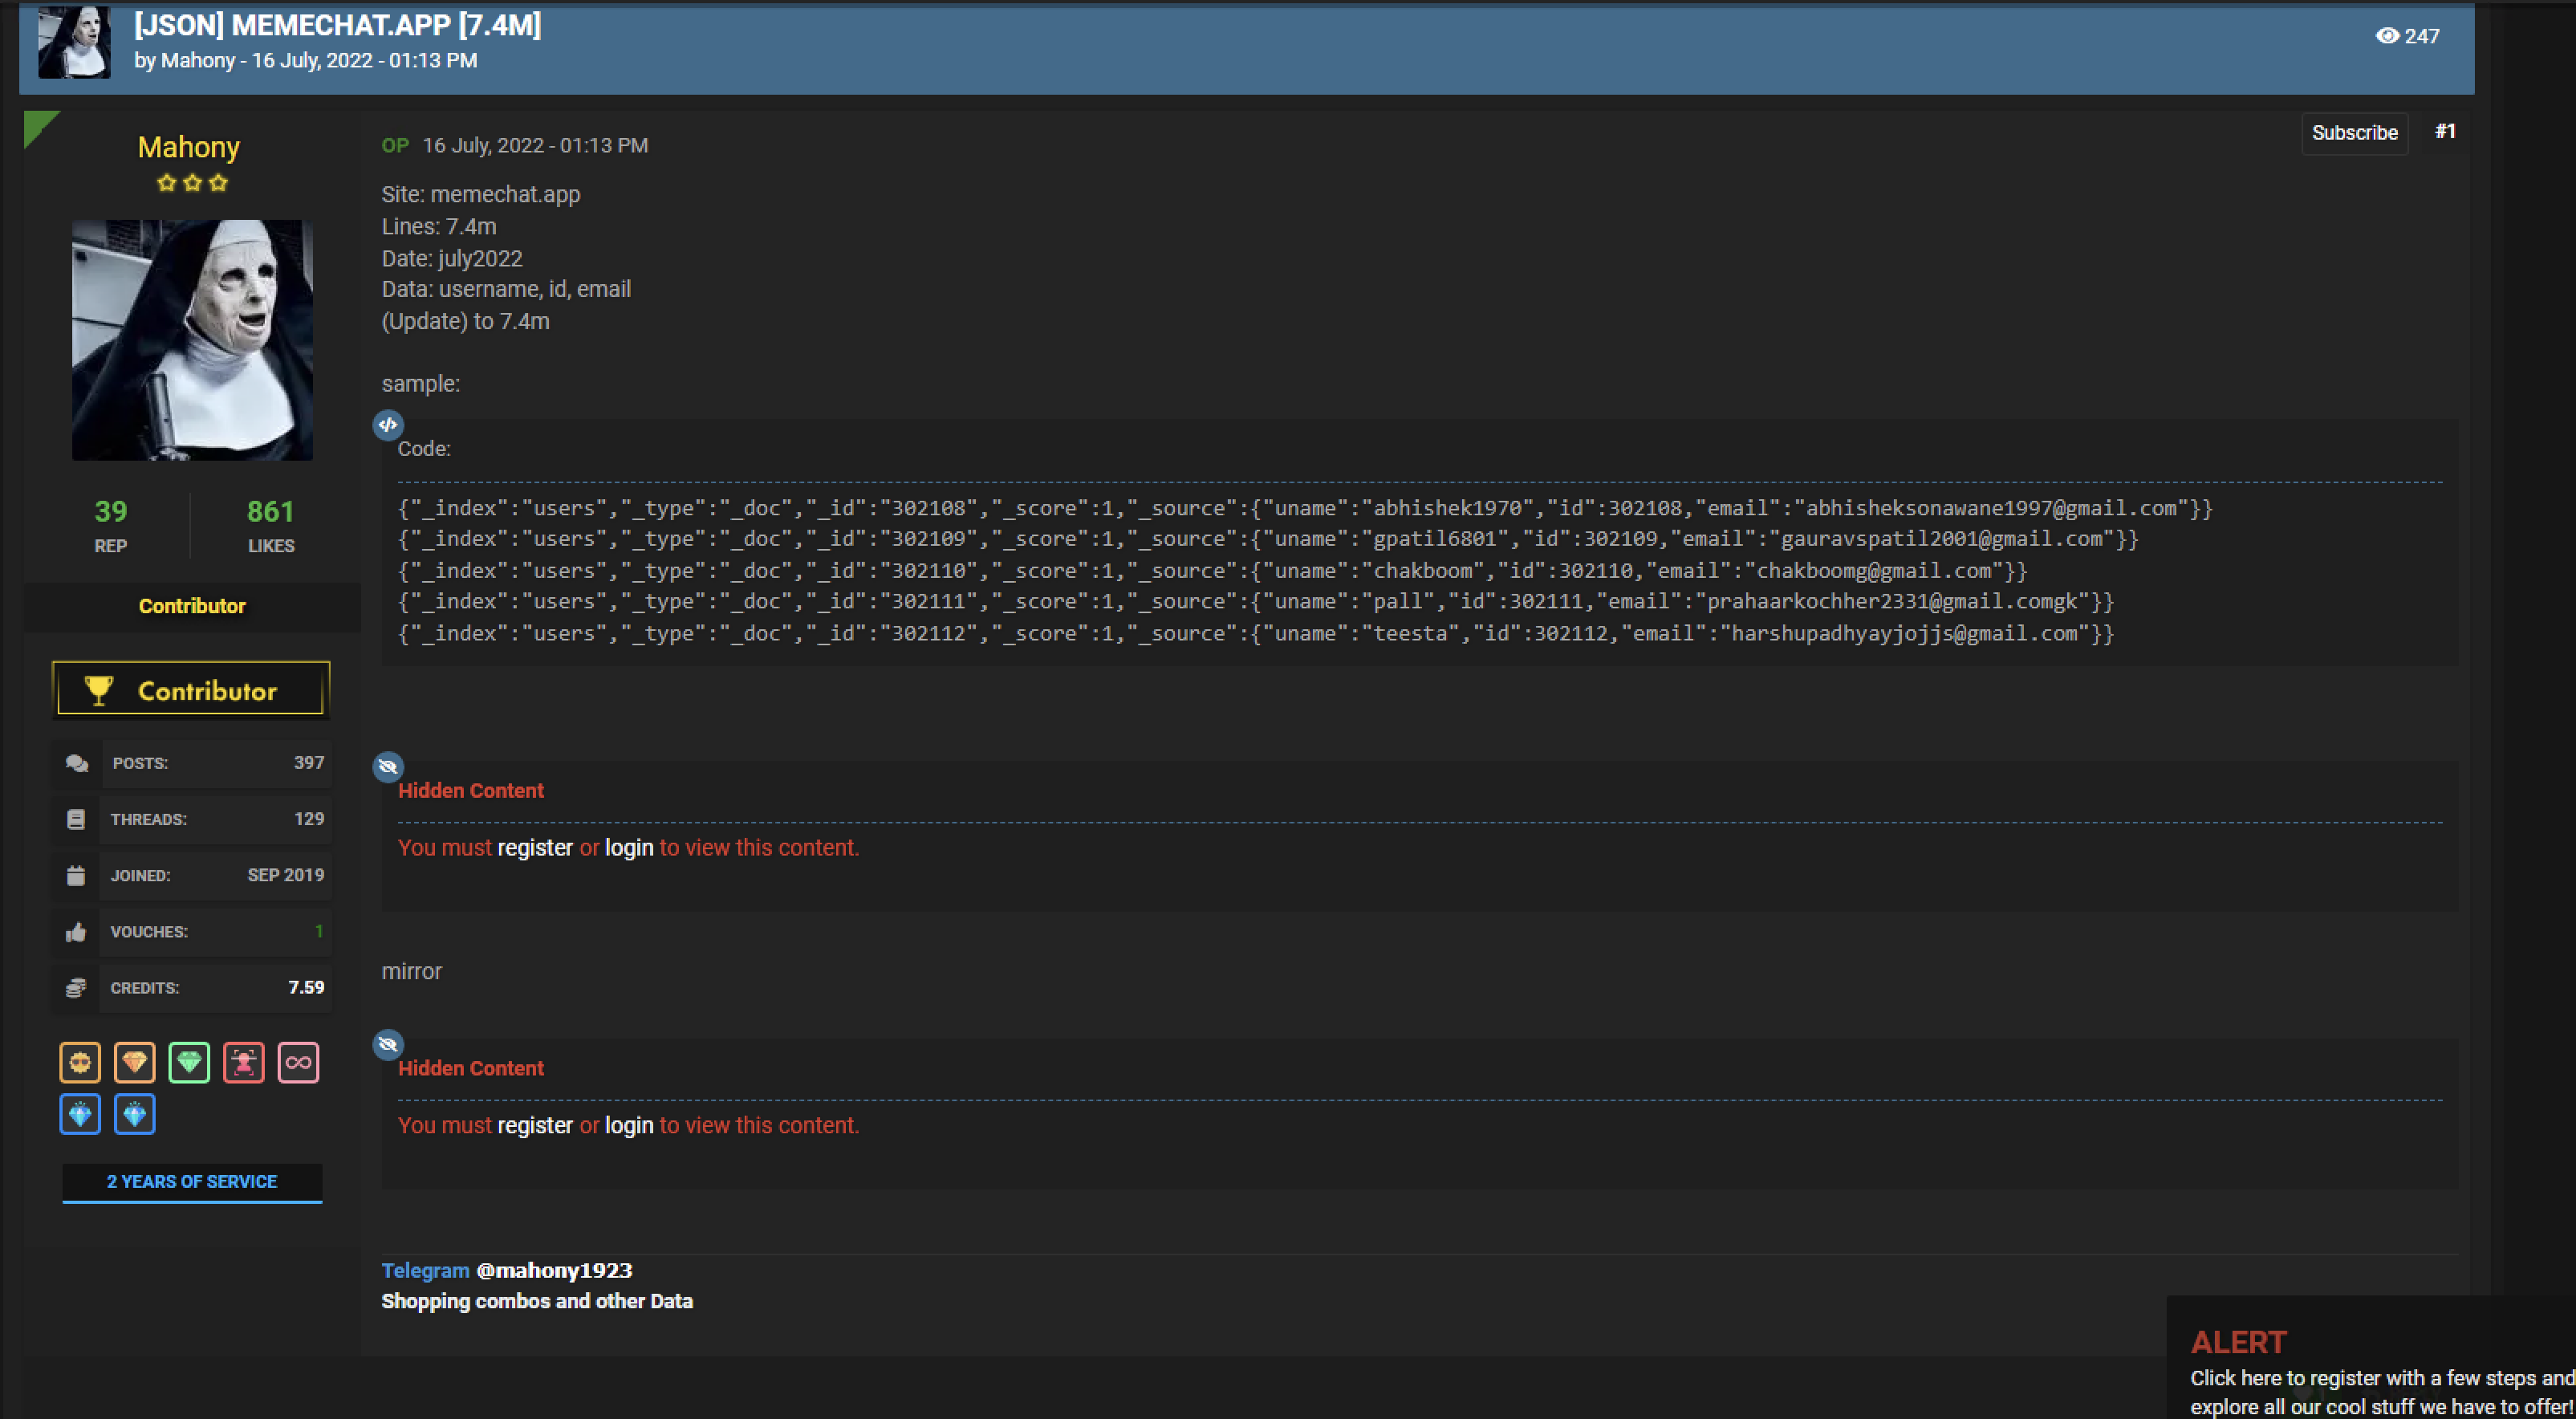
On July 5, 2022, a reputed threat actor "All3in" from the BreachForums posted a data breach package targeting MemeChat (memechat[.]app), an Indian-based online money earning app through competing with meme creators. The threat actor noted that the data dump includes 7.4m lines of user information with username, user id and email. The data dump was also circulated in the deep web forum Cracked on July 16, 2022 by the threat actor "Mahony". From the package published in BreachForums, ZeroFox extracted 4,330,769 usernames and email addresses. No passwords were found in this breach.
Recommendations
- If not already enabled, turn on the compromised credentials rule for all relevant entities and ensure relevant emails are entered for those entities, or reach out to [email protected] for assistance
- If one of your entities receives an alert, ZeroFox recommends immediate password changes for the affected account
- Enable 2-factor authentication for all of your organizational accounts to help mitigate phishing and credential stuffing attacks
Breach Disclosure: Comcast Crypto
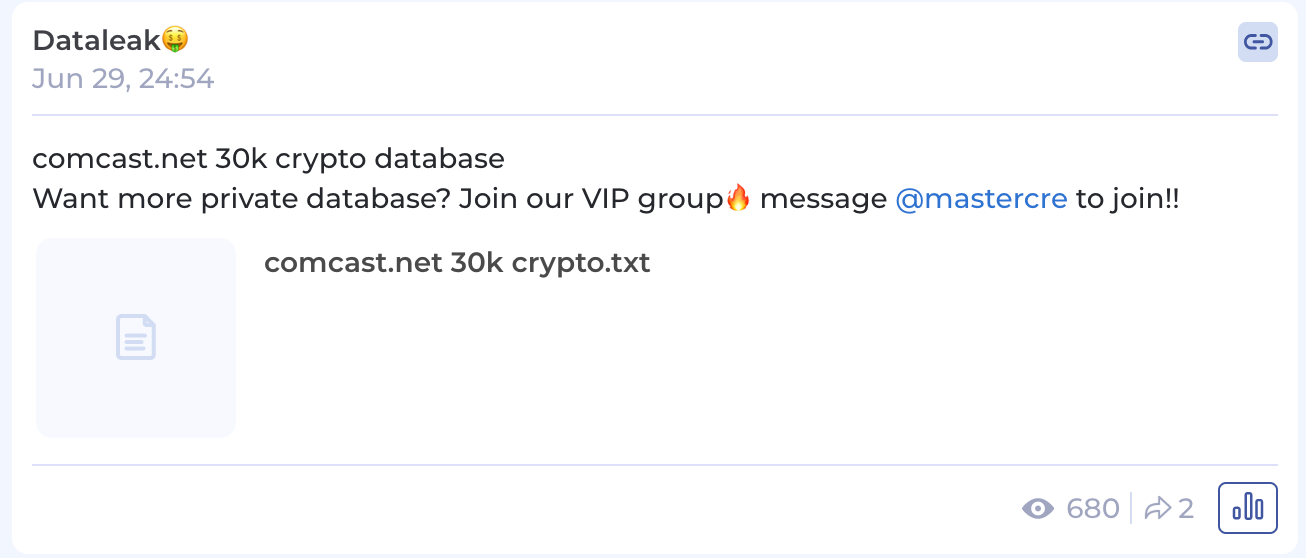
On June 28, 2022, the Telegram Channel "Dataleak" posted a data leak package titled "comcast.net 30k crypto database". From this package, ZeroFox extracted 46,717 email addresses and plain-text passwords.
Standing Intelligence Requirements
For the most up to date list of ZeroFox Threat Research’s Intelligence Requirements, please visit:
https://cloud.zerofox.com/alpha_team/advisories/14956
Details
On June 28, 2022, the Telegram Channel "Dataleak" posted a data leak package titled "comcast.net 30k crypto database". The data package allegedly contains Comcast email addresses used by the crypto users. From this package, ZeroFox extracted 46,717 email addresses and plain-text passwords.
Recommendations
- If not already enabled, turn on the compromised credentials rule for all relevant entities and ensure relevant emails are entered for those entities, or reach out to [email protected] for assistance
- If one of your entities receives an alert, ZeroFox recommends immediate password changes for the affected account
- Enable 2-factor authentication for all of your organizational accounts to help mitigate phishing and credential stuffing attacks
Breach Disclosure: Nova Publishers
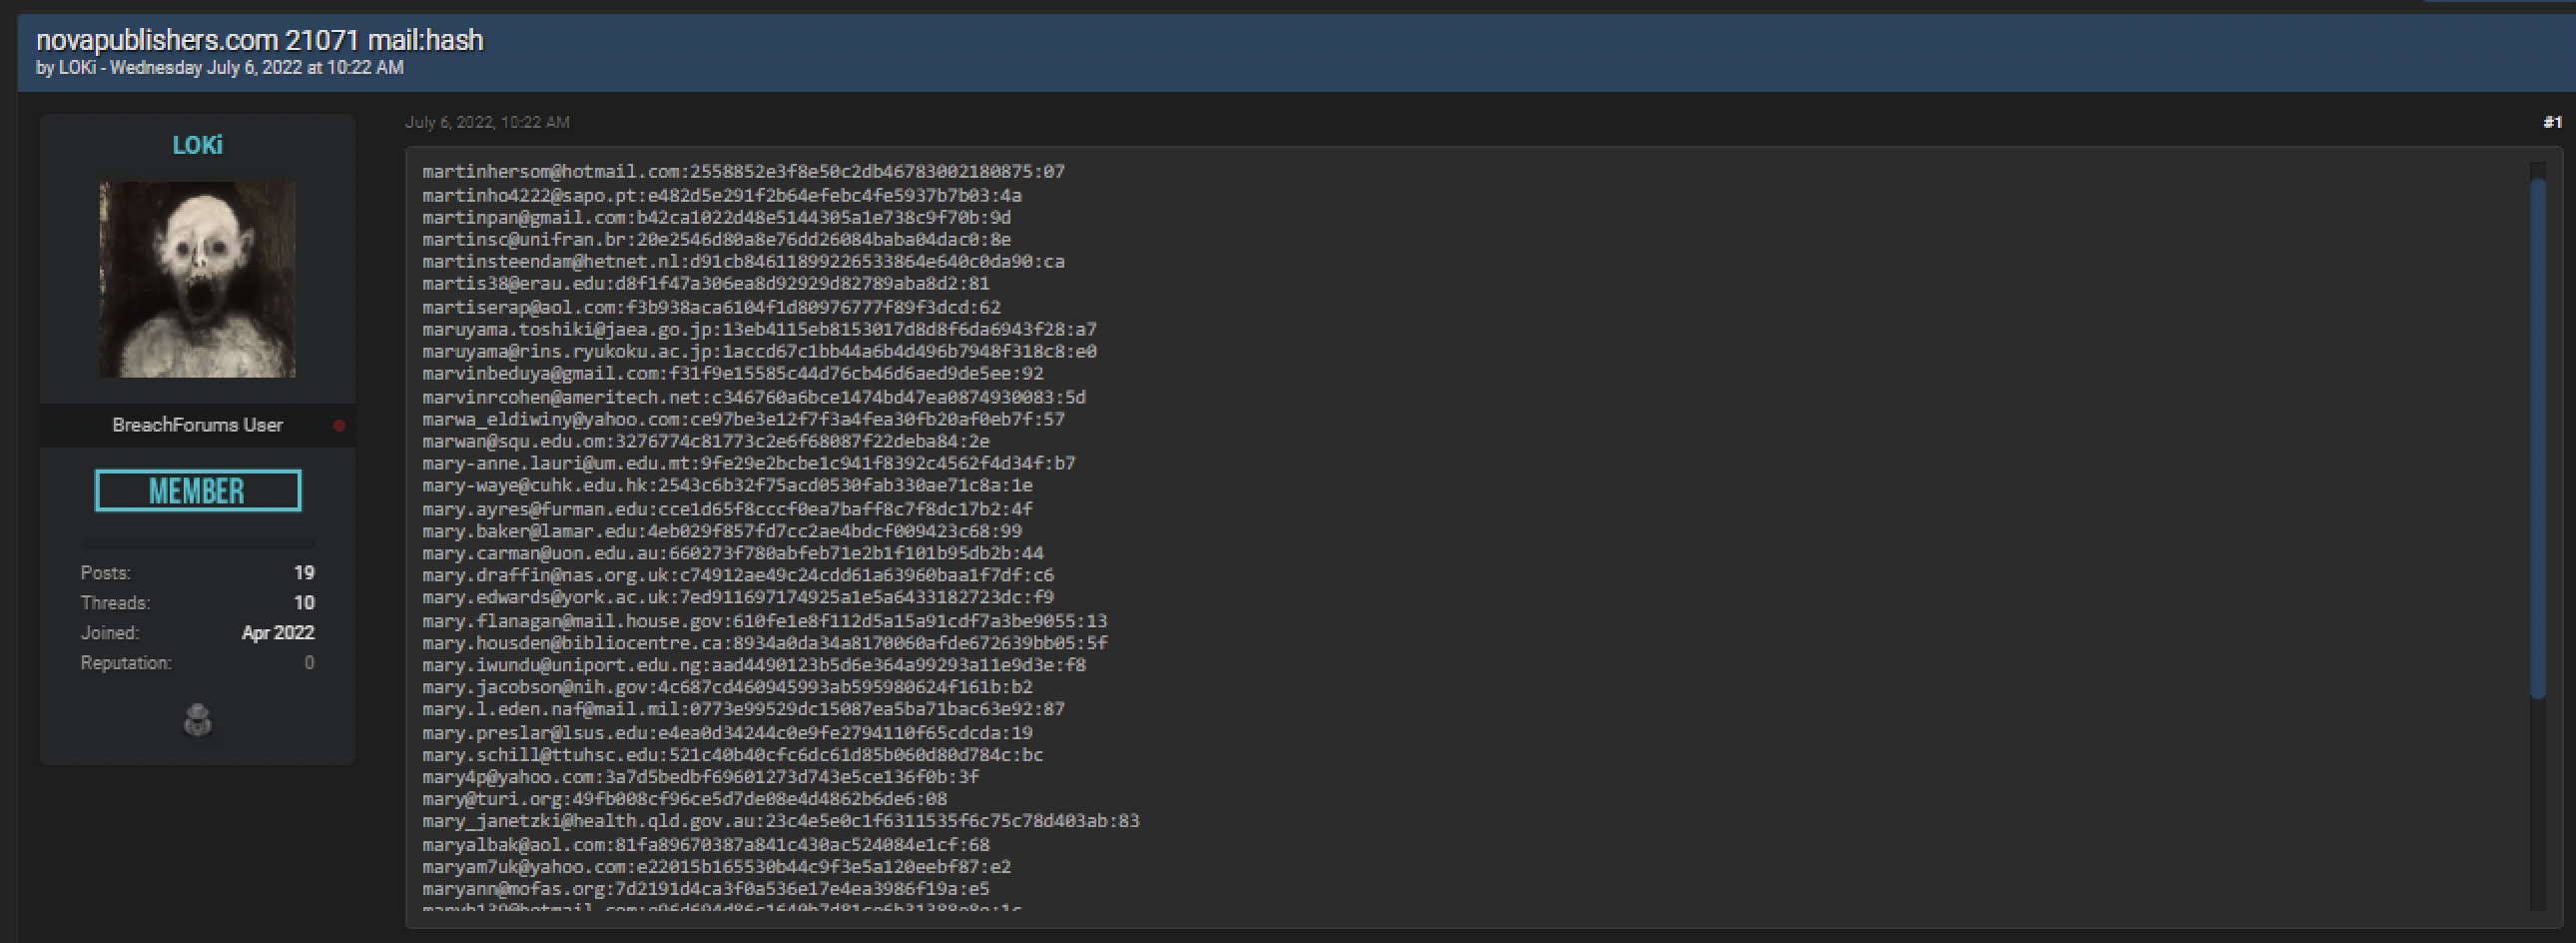
On July 6, 2022, a recently registered threat actor "LOKi" posted a data breach package targeting the organization Nova Publishers, a publishing website operating from the United States. From this package, ZeroFox extracted 21,067 email addresses and hashed passwords.
Standing Intelligence Requirements
For the most up to date list of ZeroFox Threat Research’s Intelligence Requirements, please visit:
https://cloud.zerofox.com/alpha_team/advisories/14956
Details
On July 6, 2022, a recently registered threat actor "LOKi" posted a data breach package targeting the organization Nova Publishers (novapublishers[.]com), a publishing website operating from the United States. From this package, ZeroFox extracted 21,067 email addresses and hashed passwords.
Recommendations
- If not already enabled, turn on the compromised credentials rule for all relevant entities and ensure relevant emails are entered for those entities, or reach out to [email protected] for assistance
- If one of your entities receives an alert, ZeroFox recommends immediate password changes for the affected account
- Enable 2-factor authentication for all of your organizational accounts to help mitigate phishing and credential stuffing attacks
Breach Disclosure: Saudi_64k
On July 5, 2022, a reputed threat actor "Topazzz" from the Russian language deep web forum XSS posted a data leak package titled "Saudi_64k". From this package, ZeroFox extracted 63,661 email addresses.
Standing Intelligence Requirements
For the most up to date list of ZeroFox Threat Research’s Intelligence Requirements, please visit:
https://cloud.zerofox.com/alpha_team/advisories/14956
Details
On July 5, 2022, a reputed threat actor "Topazzz" from the Russian language deep web forum XSS posted a data leak package titled "Saudi_64k". From this package, ZeroFox extracted 63,661 email addresses. No passwords were found in this breach.
Recommendations
- If not already enabled, turn on the compromised credentials rule for all relevant entities and ensure relevant emails are entered for those entities, or reach out to [email protected] for assistance
- If one of your entities receives an alert, ZeroFox recommends immediate password changes for the affected account
- Enable 2-factor authentication for all of your organizational accounts to help mitigate phishing and credential stuffing attacks
Breach Disclosure: US Mobile Feeds
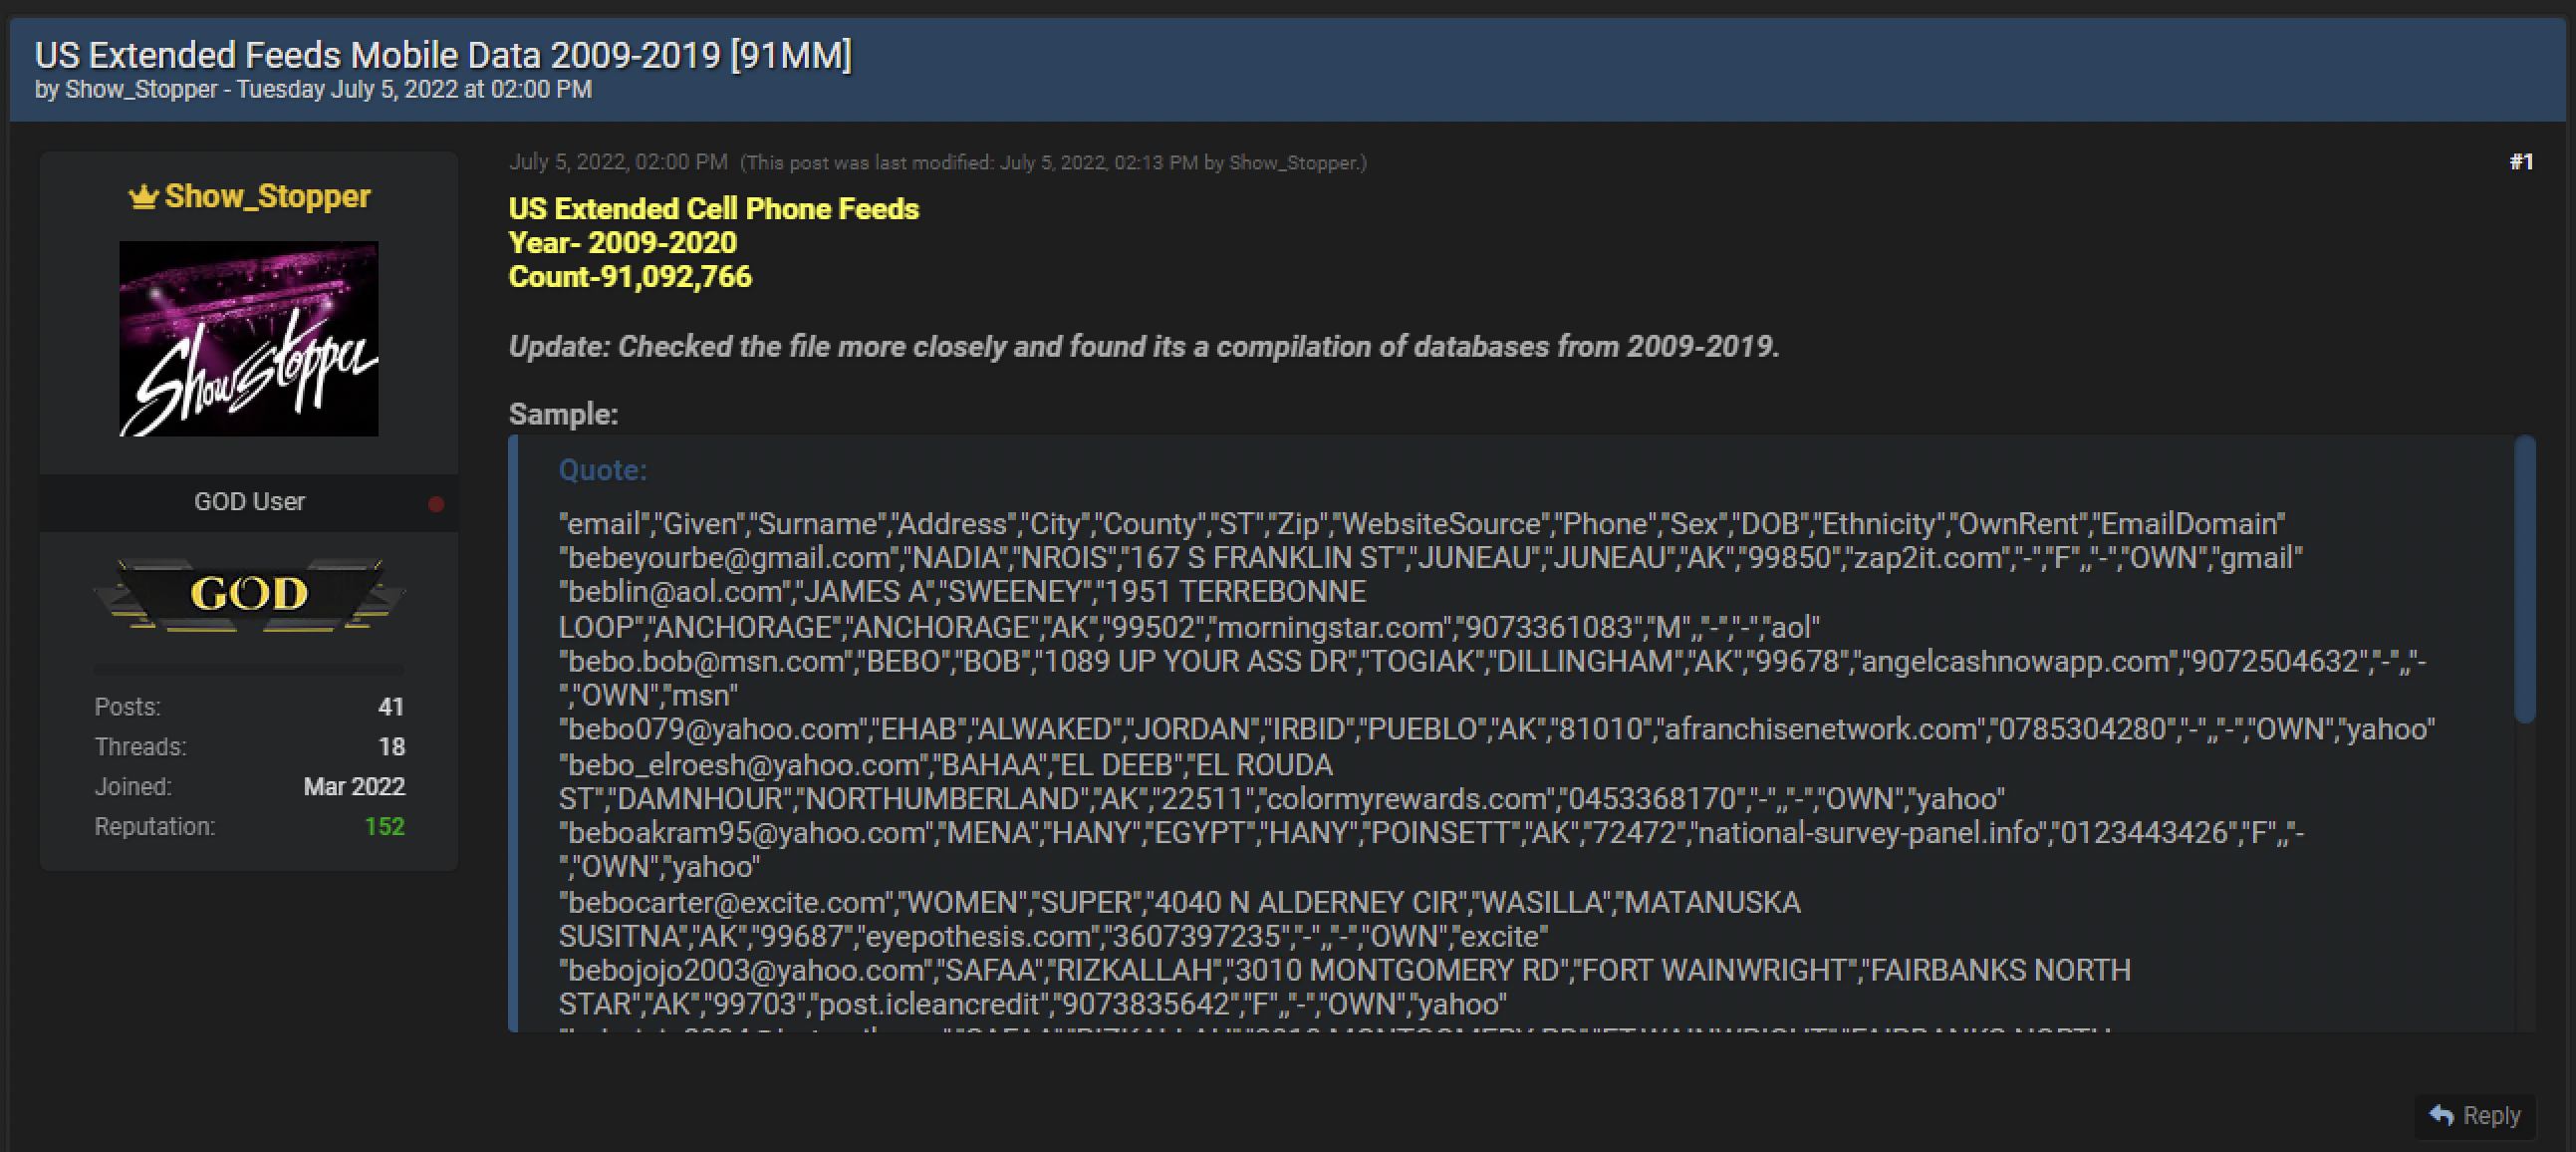
On July 5, 2022, a reputed threat actor "Show_Stopper" from the deep web forum BreachForums posted a data leak package titled "US Extended Feeds Mobile Data 2009-2019 [91MM]". From this package, ZeroFox extracted 91,102,858 email addresses.
Standing Intelligence Requirements
For the most up to date list of ZeroFox Threat Research’s Intelligence Requirements, please visit:
https://cloud.zerofox.com/alpha_team/advisories/14956
Details
On July 5, 2022, a reputed threat actor "Show_Stopper" from the deep web forum BreachForums posted a data leak package titled "US Extended Feeds Mobile Data 2009-2019 [91MM]". From this package, ZeroFox extracted 91,102,858 email addresses. No passwords were found in this breach.
Recommendations
- If not already enabled, turn on the compromised credentials rule for all relevant entities and ensure relevant emails are entered for those entities, or reach out to [email protected] for assistance
- If one of your entities receives an alert, ZeroFox recommends immediate password changes for the affected account
- Enable 2-factor authentication for all of your organizational accounts to help mitigate phishing and credential stuffing attacks
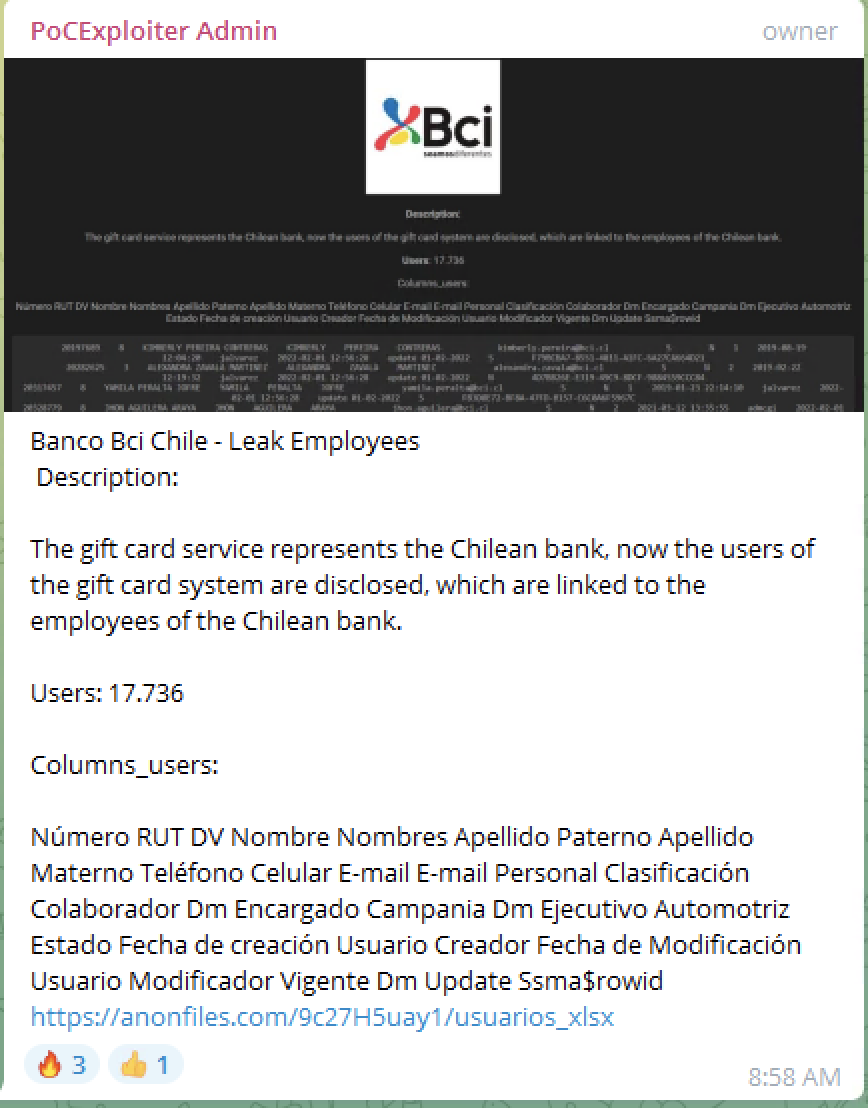
Breach Disclosure: Banco Bci
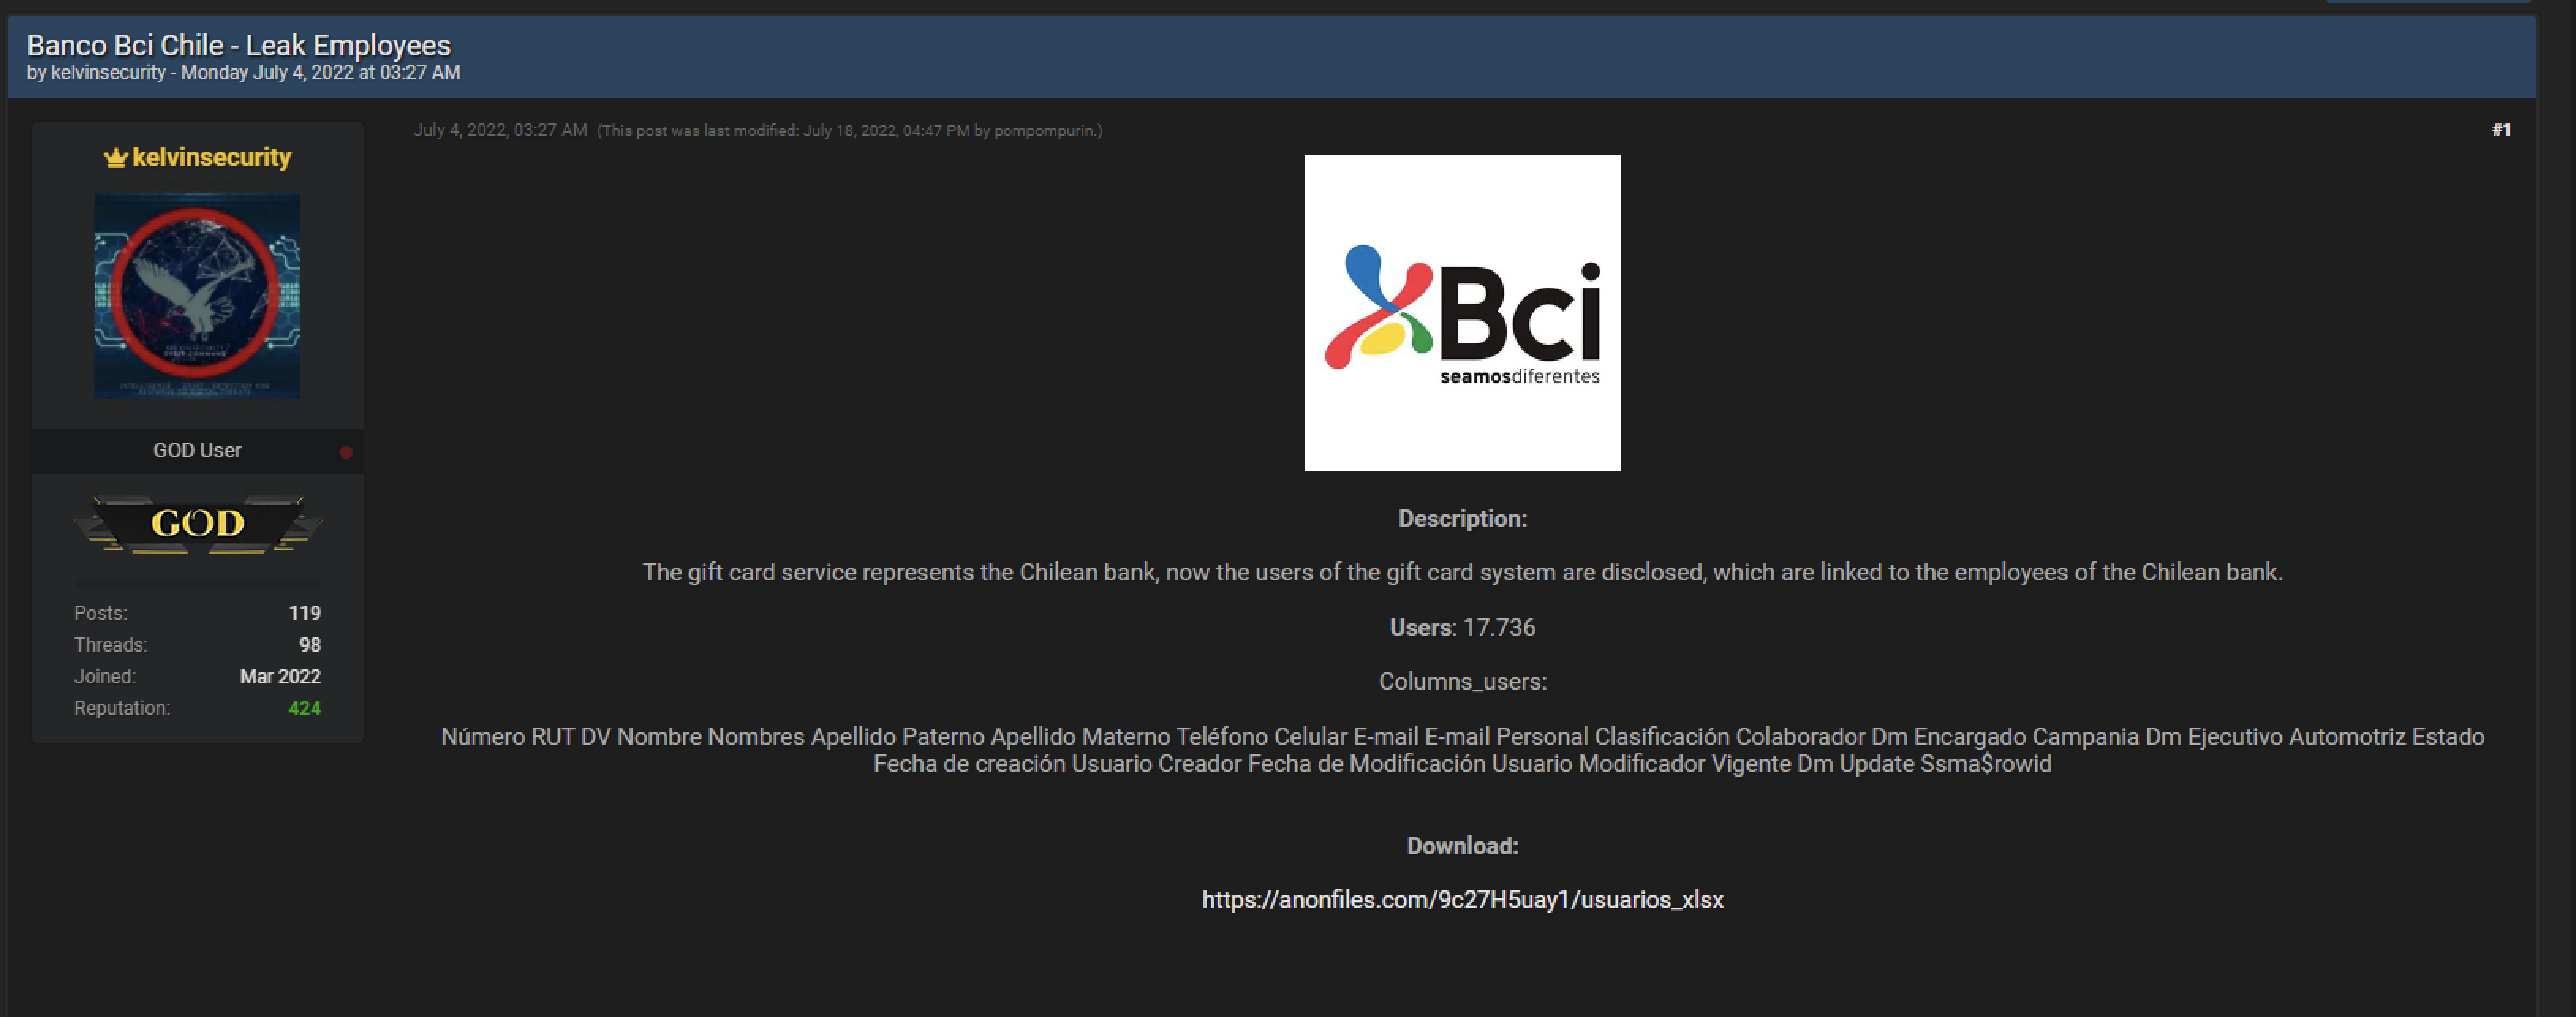
On July 4, 2022, a reputed threat actor "kelvinsecurity" from the BreachForums posted a data breach package targeting Banco Bci, a Chile-based commercial banking services company which operates through retail, wholesale and corporate banking. From the package published in BreachForums, ZeroFox extracted 12,877 email addresses.
Standing Intelligence Requirements
For the most up to date list of ZeroFox Threat Research’s Intelligence Requirements, please visit:
https://cloud.zerofox.com/alpha_team/advisories/14956
Details
On July 4, 2022, a reputed threat actor "kelvinsecurity" from the BreachForums posted a data breach package targeting Banco Bci (bci[.]cl), a Chile-based commercial banking services company which operates through retail, wholesale and corporate banking. The data dump was also circulated in the Telegram Channel "KelvinSecurity - Dark Market & Leaks" (hxxps://t[.]me/kelvinsecuritydarkmarket/3923) on July 4, 2022. From the package published in BreachForums, ZeroFox extracted 12,877 email addresses. No passwords were found in this breach.
Recommendations
- If not already enabled, turn on the compromised credentials rule for all relevant entities and ensure relevant emails are entered for those entities, or reach out to [email protected] for assistance
- If one of your entities receives an alert, ZeroFox recommends immediate password changes for the affected account
- Enable 2-factor authentication for all of your organizational accounts to help mitigate phishing and credential stuffing attacks
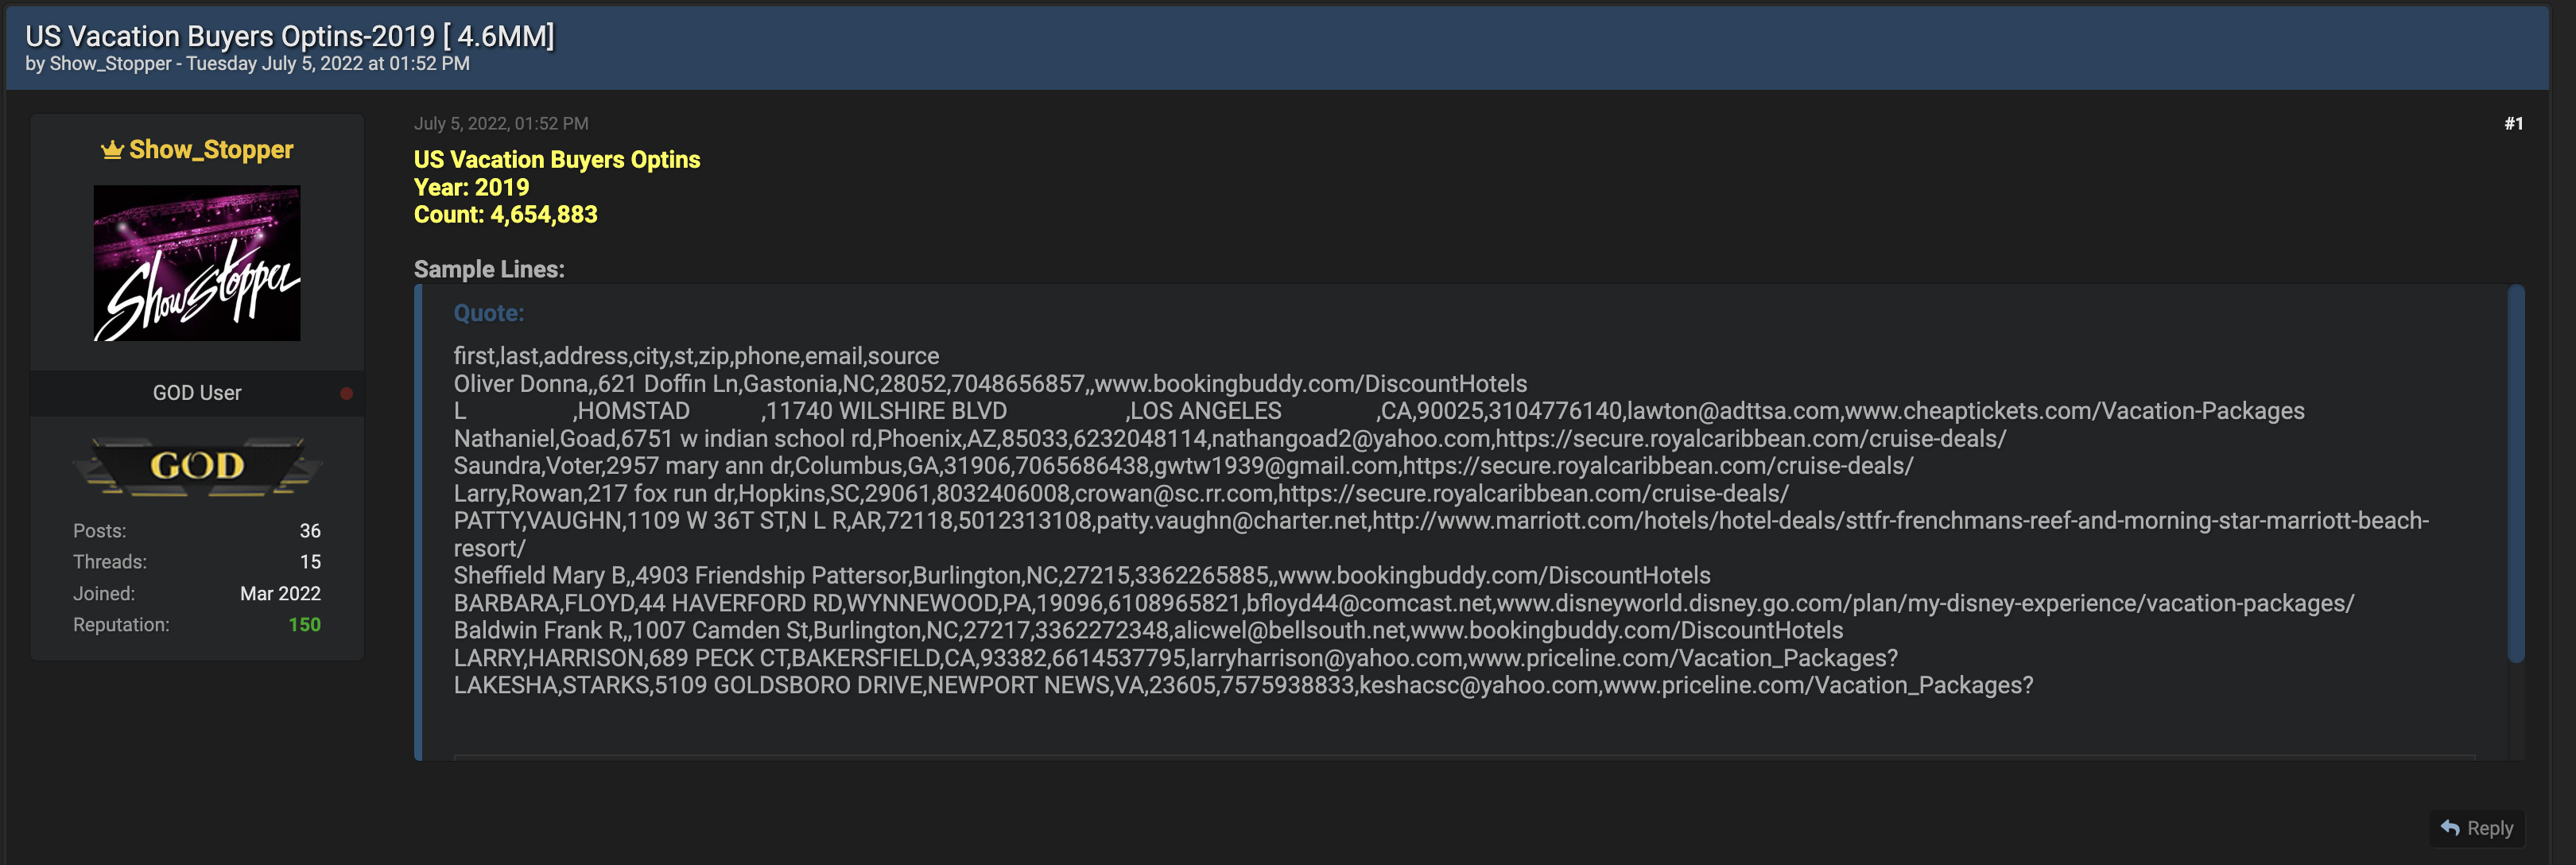
Breach Disclosure: US Vacationbuyers
On July 5, 2022, a reputed threat actor "Show_Stopper" from the deep web forum BreachForums posted a data leak package titled "US Vacation Buyers Optins-2019". From this package, ZeroFox extracted 3,725,191 email addresses.
Standing Intelligence Requirements
For the most up to date list of ZeroFox Threat Research’s Intelligence Requirements, please visit:
https://cloud.zerofox.com/alpha_team/advisories/14956
Details
On July 5, 2022, a reputed threat actor "Show_Stopper" from the deep web forum BreachForums posted a data leak package titled "US Vacation Buyers Optins-2019". From this package, ZeroFox extracted 3,725,191 email addresses. No passwords were found in this breach.
Recommendations
- If not already enabled, turn on the compromised credentials rule for all relevant entities and ensure relevant emails are entered for those entities, or reach out to [email protected] for assistance
- If one of your entities receives an alert, ZeroFox recommends immediate password changes for the affected account
- Enable 2-factor authentication for all of your organizational accounts to help mitigate phishing and credential stuffing attacks
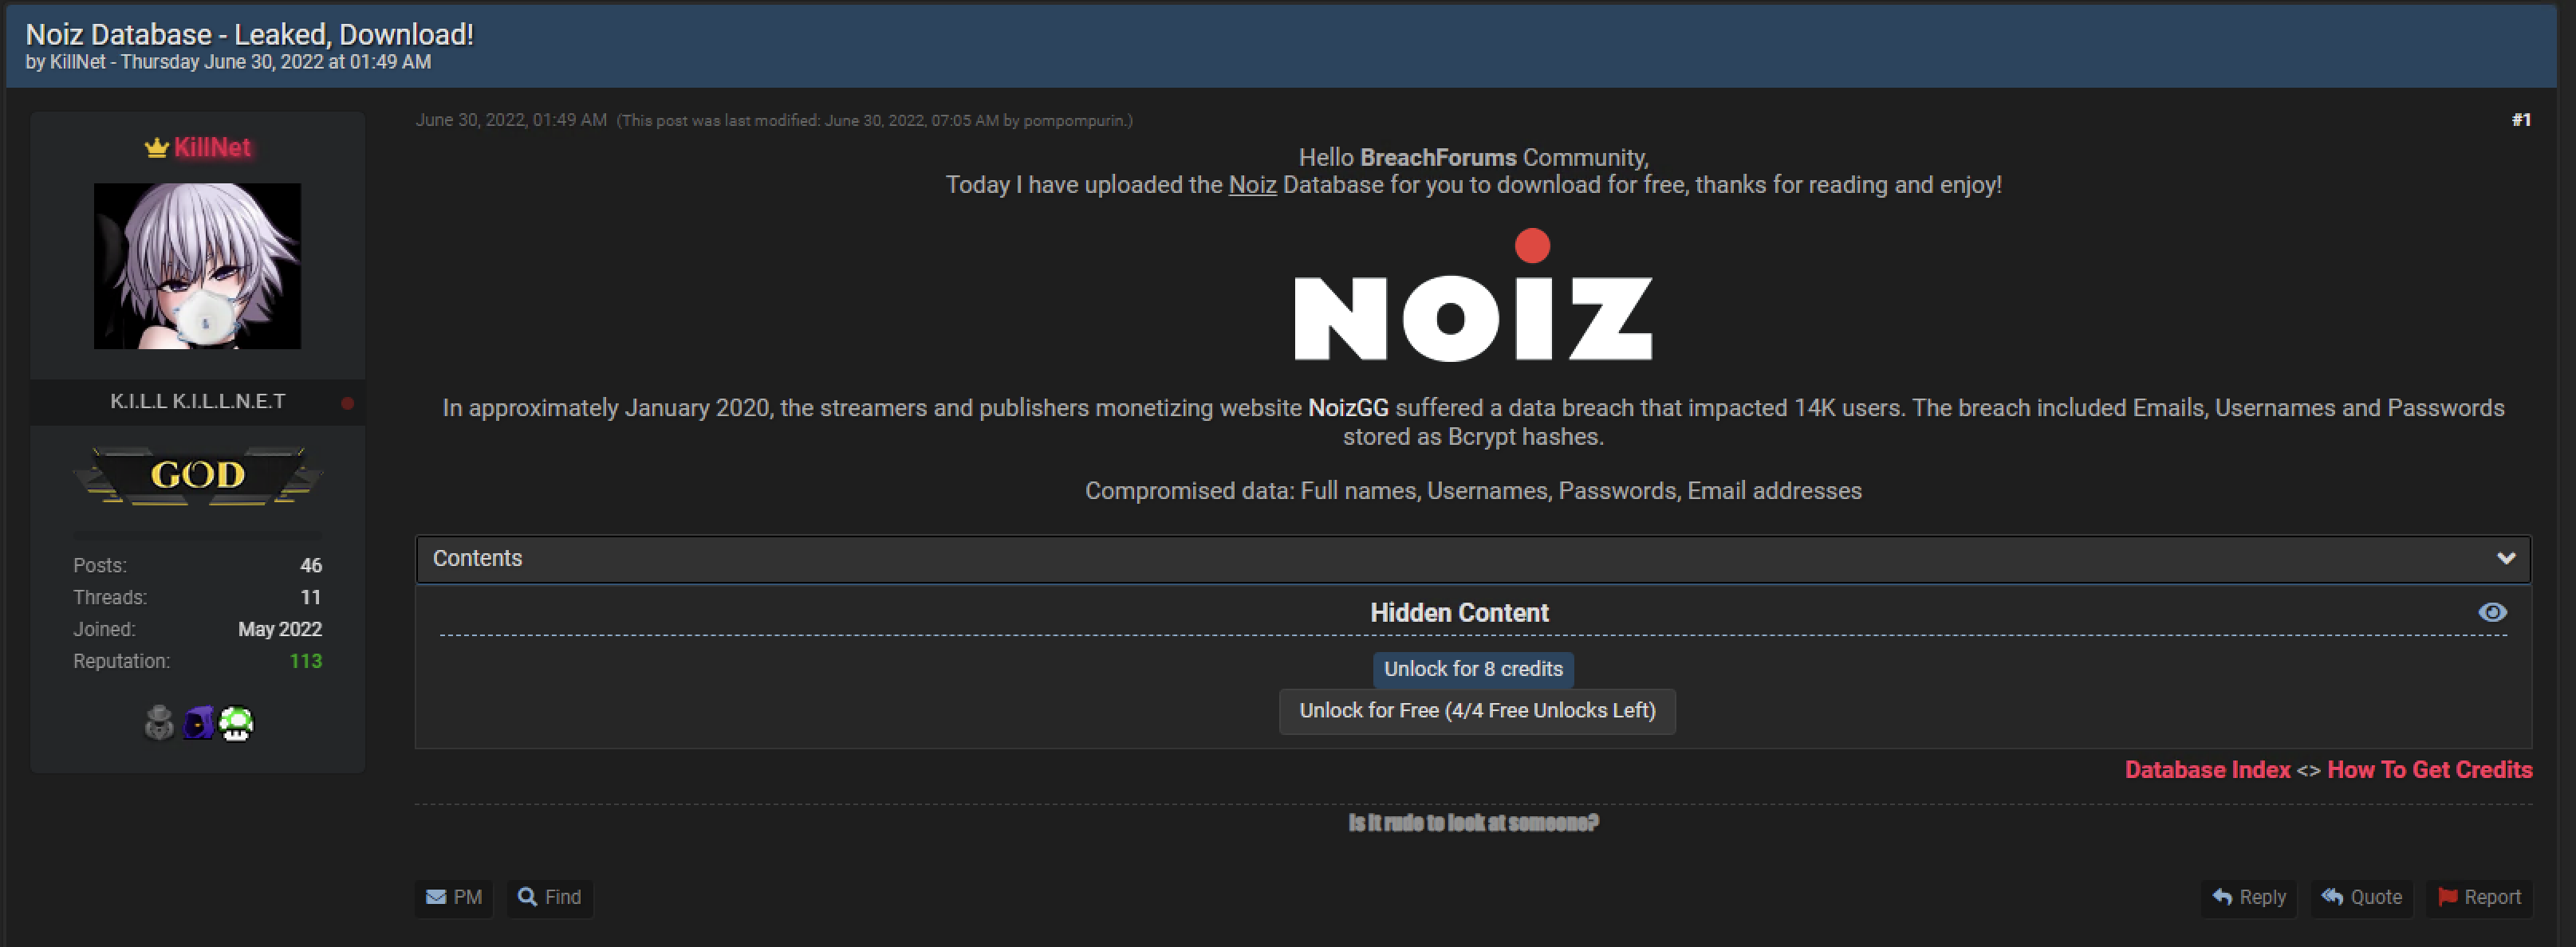
Breach Disclosure: Noiz
On June 30, 2022, a reputed threat actor "KillNet" from BreachForums posted a data breach package targeting the organization Noiz, a US-based gaming influencer that runs campaigns which connects game streamers and game companies to sponsorship opportunities. From the package published in BreachForums, ZeroFox extracted 13,893 usernames, email addresses, and hashed passwords.
Standing Intelligence Requirements
For the most up to date list of ZeroFox Threat Research’s Intelligence Requirements, please visit:
https://cloud.zerofox.com/alpha_team/advisories/14956
Details
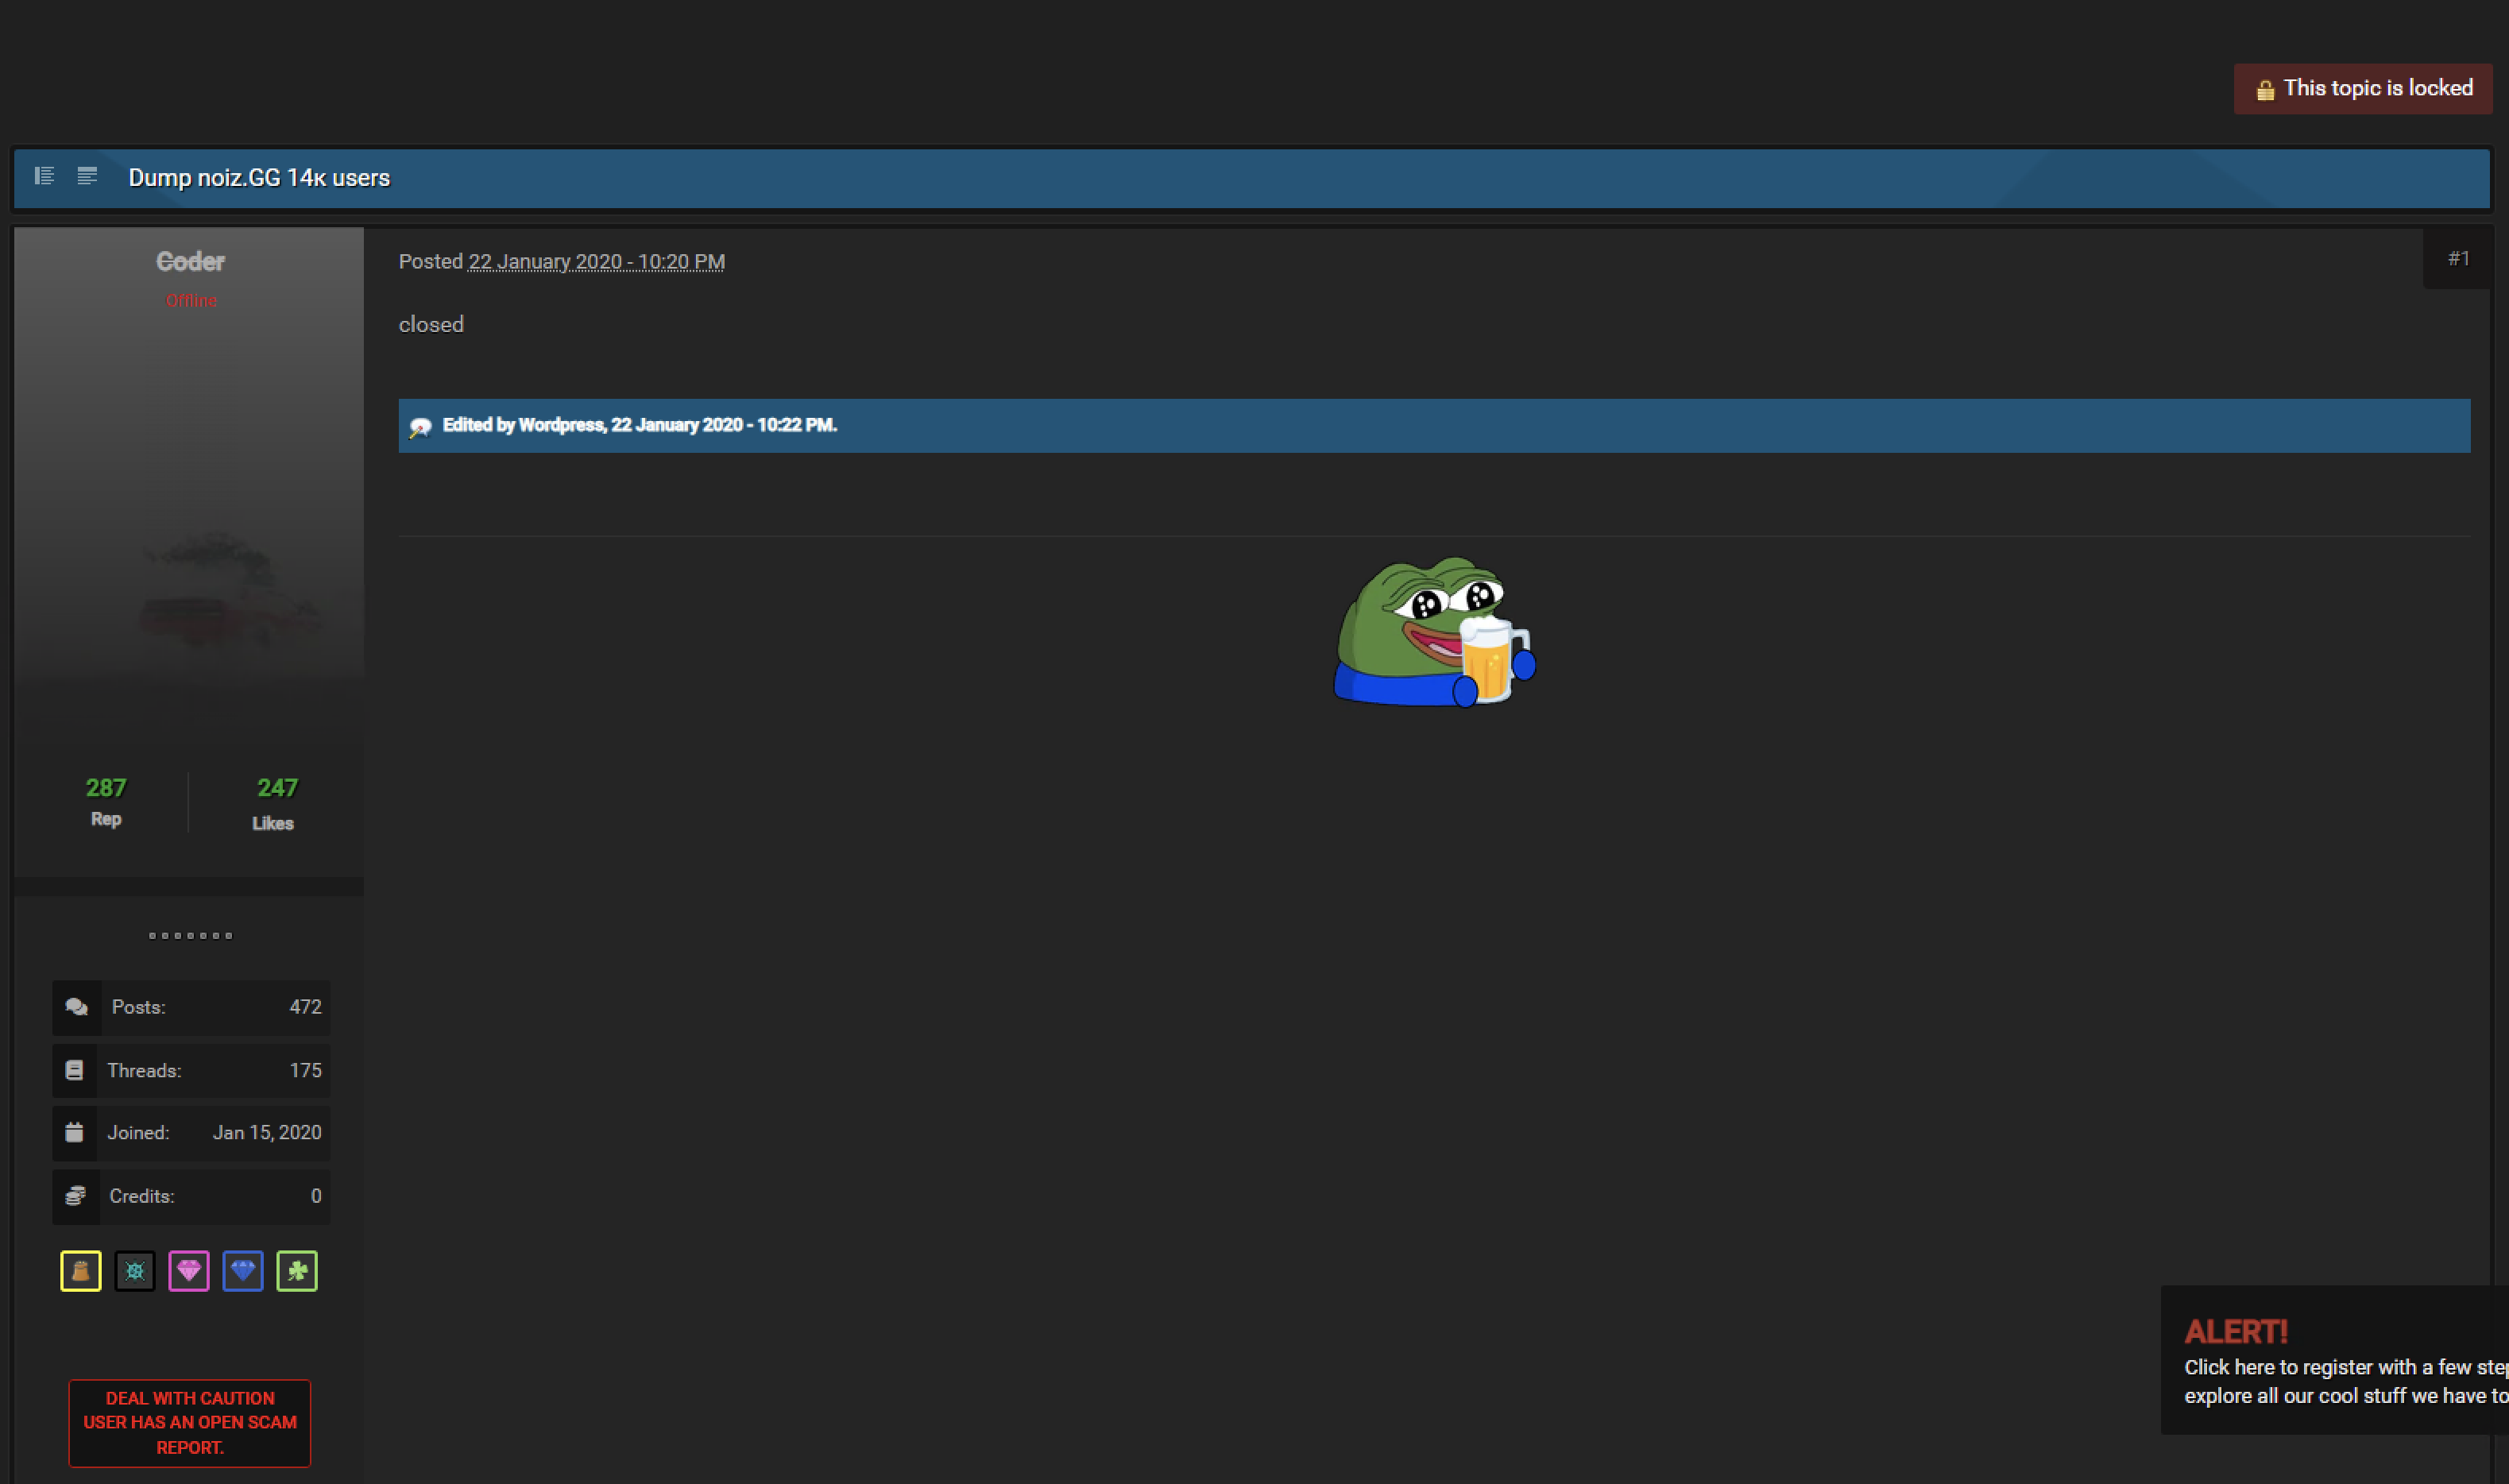
On June 30, 2022, a reputed threat actor "KillNet" from BreachForums posted a data breach package targeting the organization Noiz, a US-based gaming influencer that runs campaigns which connects game streamers and game companies to sponsorship opportunities. The threat actor noted that the data dump is from January 2020 which includes 14K users' information with full names, usernames, passwords, email addresses. The data dump was also circulated in the deep web forum Nulled on January 22, 2020 by the threat actor "Coder". The threat actor "coder" was offline due to scam activity reports. From the package published in BreachForums, ZeroFox extracted 13,893 usernames, email addresses, and hashed passwords.
Recommendations
- If not already enabled, turn on the compromised credentials rule for all relevant entities and ensure relevant emails are entered for those entities, or reach out to [email protected] for assistance
- If one of your entities receives an alert, ZeroFox recommends immediate password changes for the affected account
- Enable 2-factor authentication for all of your organizational accounts to help mitigate phishing and credential stuffing attacks
Breach Disclosure: Job in RU Region
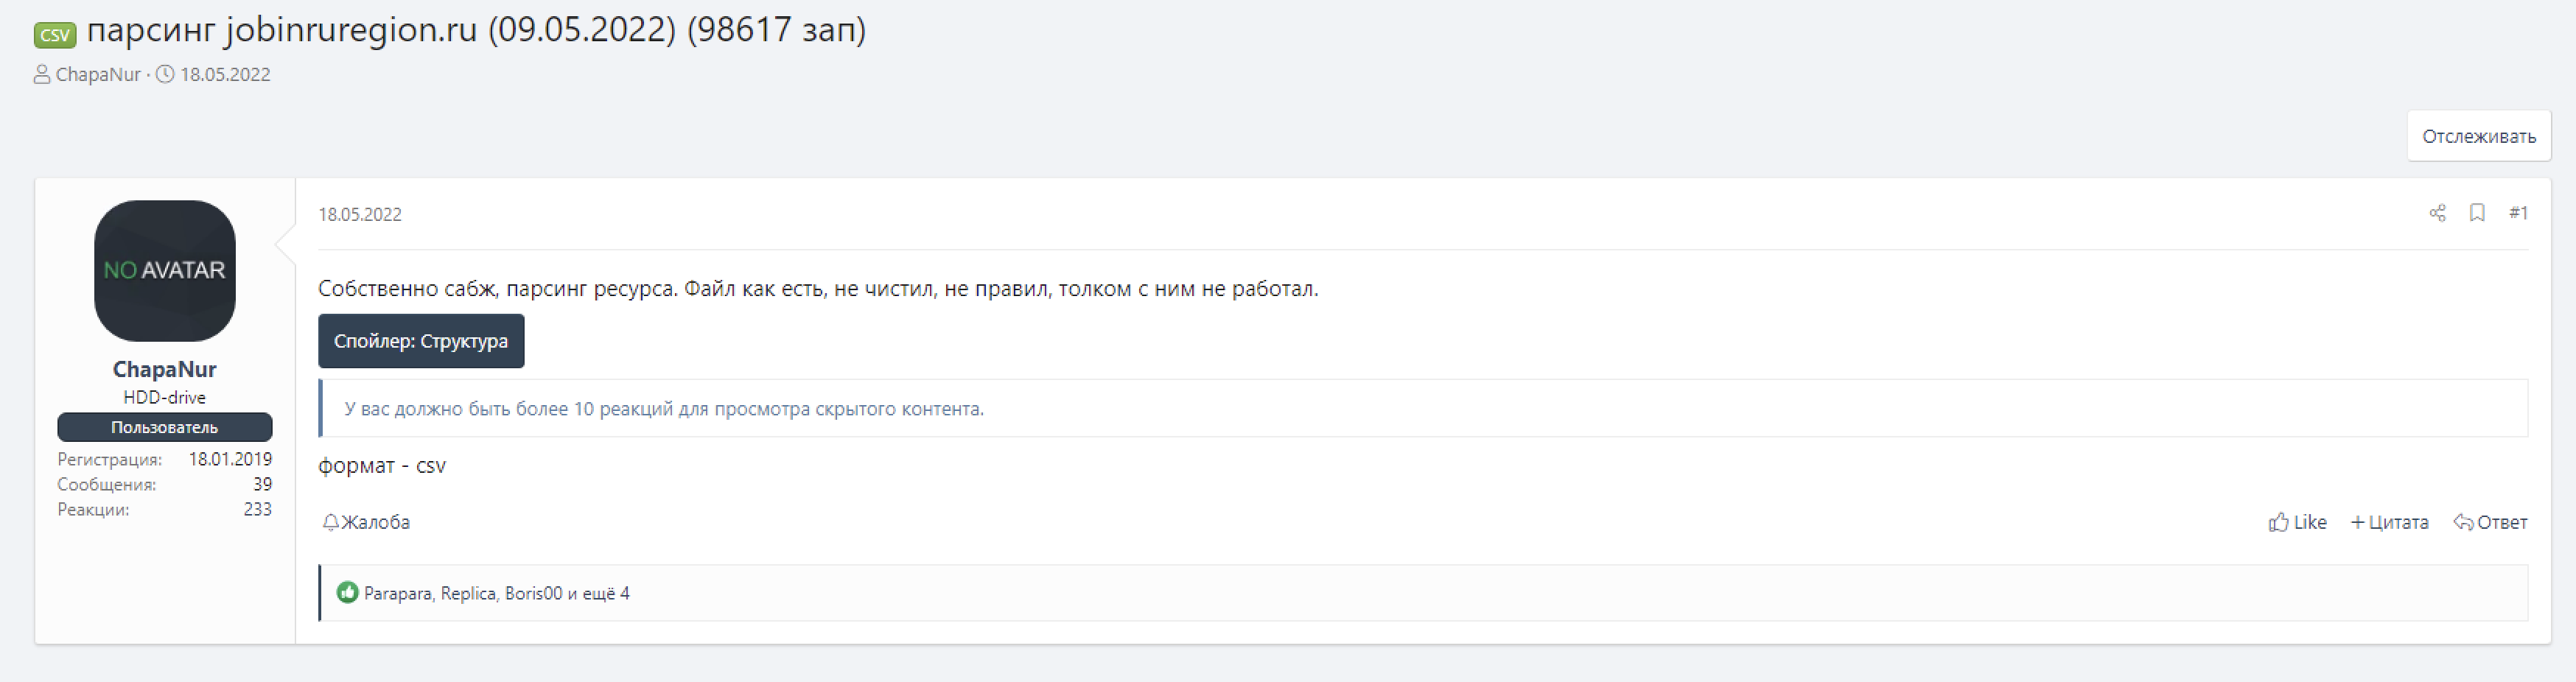
On May 18, 2022, a user level threat actor "ChapaNur" from the Russian language deep web forum XSS posted a data breach package targeting Job in RU Region, a job portal operating form Russia. From this package, ZeroFox extracted 92,581 email addresses.
Standing Intelligence Requirements
For the most up to date list of ZeroFox Threat Research’s Intelligence Requirements, please visit:
https://cloud.zerofox.com/alpha_team/advisories/14956
Details
On May 18, 2022, a user level threat actor "ChapaNur" from the Russian language deep web forum XSS posted a data breach package targeting Job in RU Region (jobinruregion[.]ru), a job portal operating form Russia. From this package, ZeroFox extracted 92,581 email addresses. No passwords were found in this breach.
Recommendations
- If not already enabled, turn on the compromised credentials rule for all relevant entities and ensure relevant emails are entered for those entities, or reach out to [email protected] for assistance
- If one of your entities receives an alert, ZeroFox recommends immediate password changes for the affected account
- Enable 2-factor authentication for all of your organizational accounts to help mitigate phishing and credential stuffing attacks
Breach Disclosure: AudioNow
On May 5, 2022, a reputed threat actor "louisthomas82" from the BreachForums posted a data breach package targeting AudioNow, a U.S.-based audio broadcasting platform and smartphone applications for broadcasters and listeners to share and create content. From the package on BreachForums, ZeroFox extracted 18,259 usernames and/or email addresses.
Standing Intelligence Requirements
For the most up to date list of ZeroFox Threat Research’s Intelligence Requirements, please visit:
https://cloud.zerofox.com/alpha_team/advisories/14956
Details
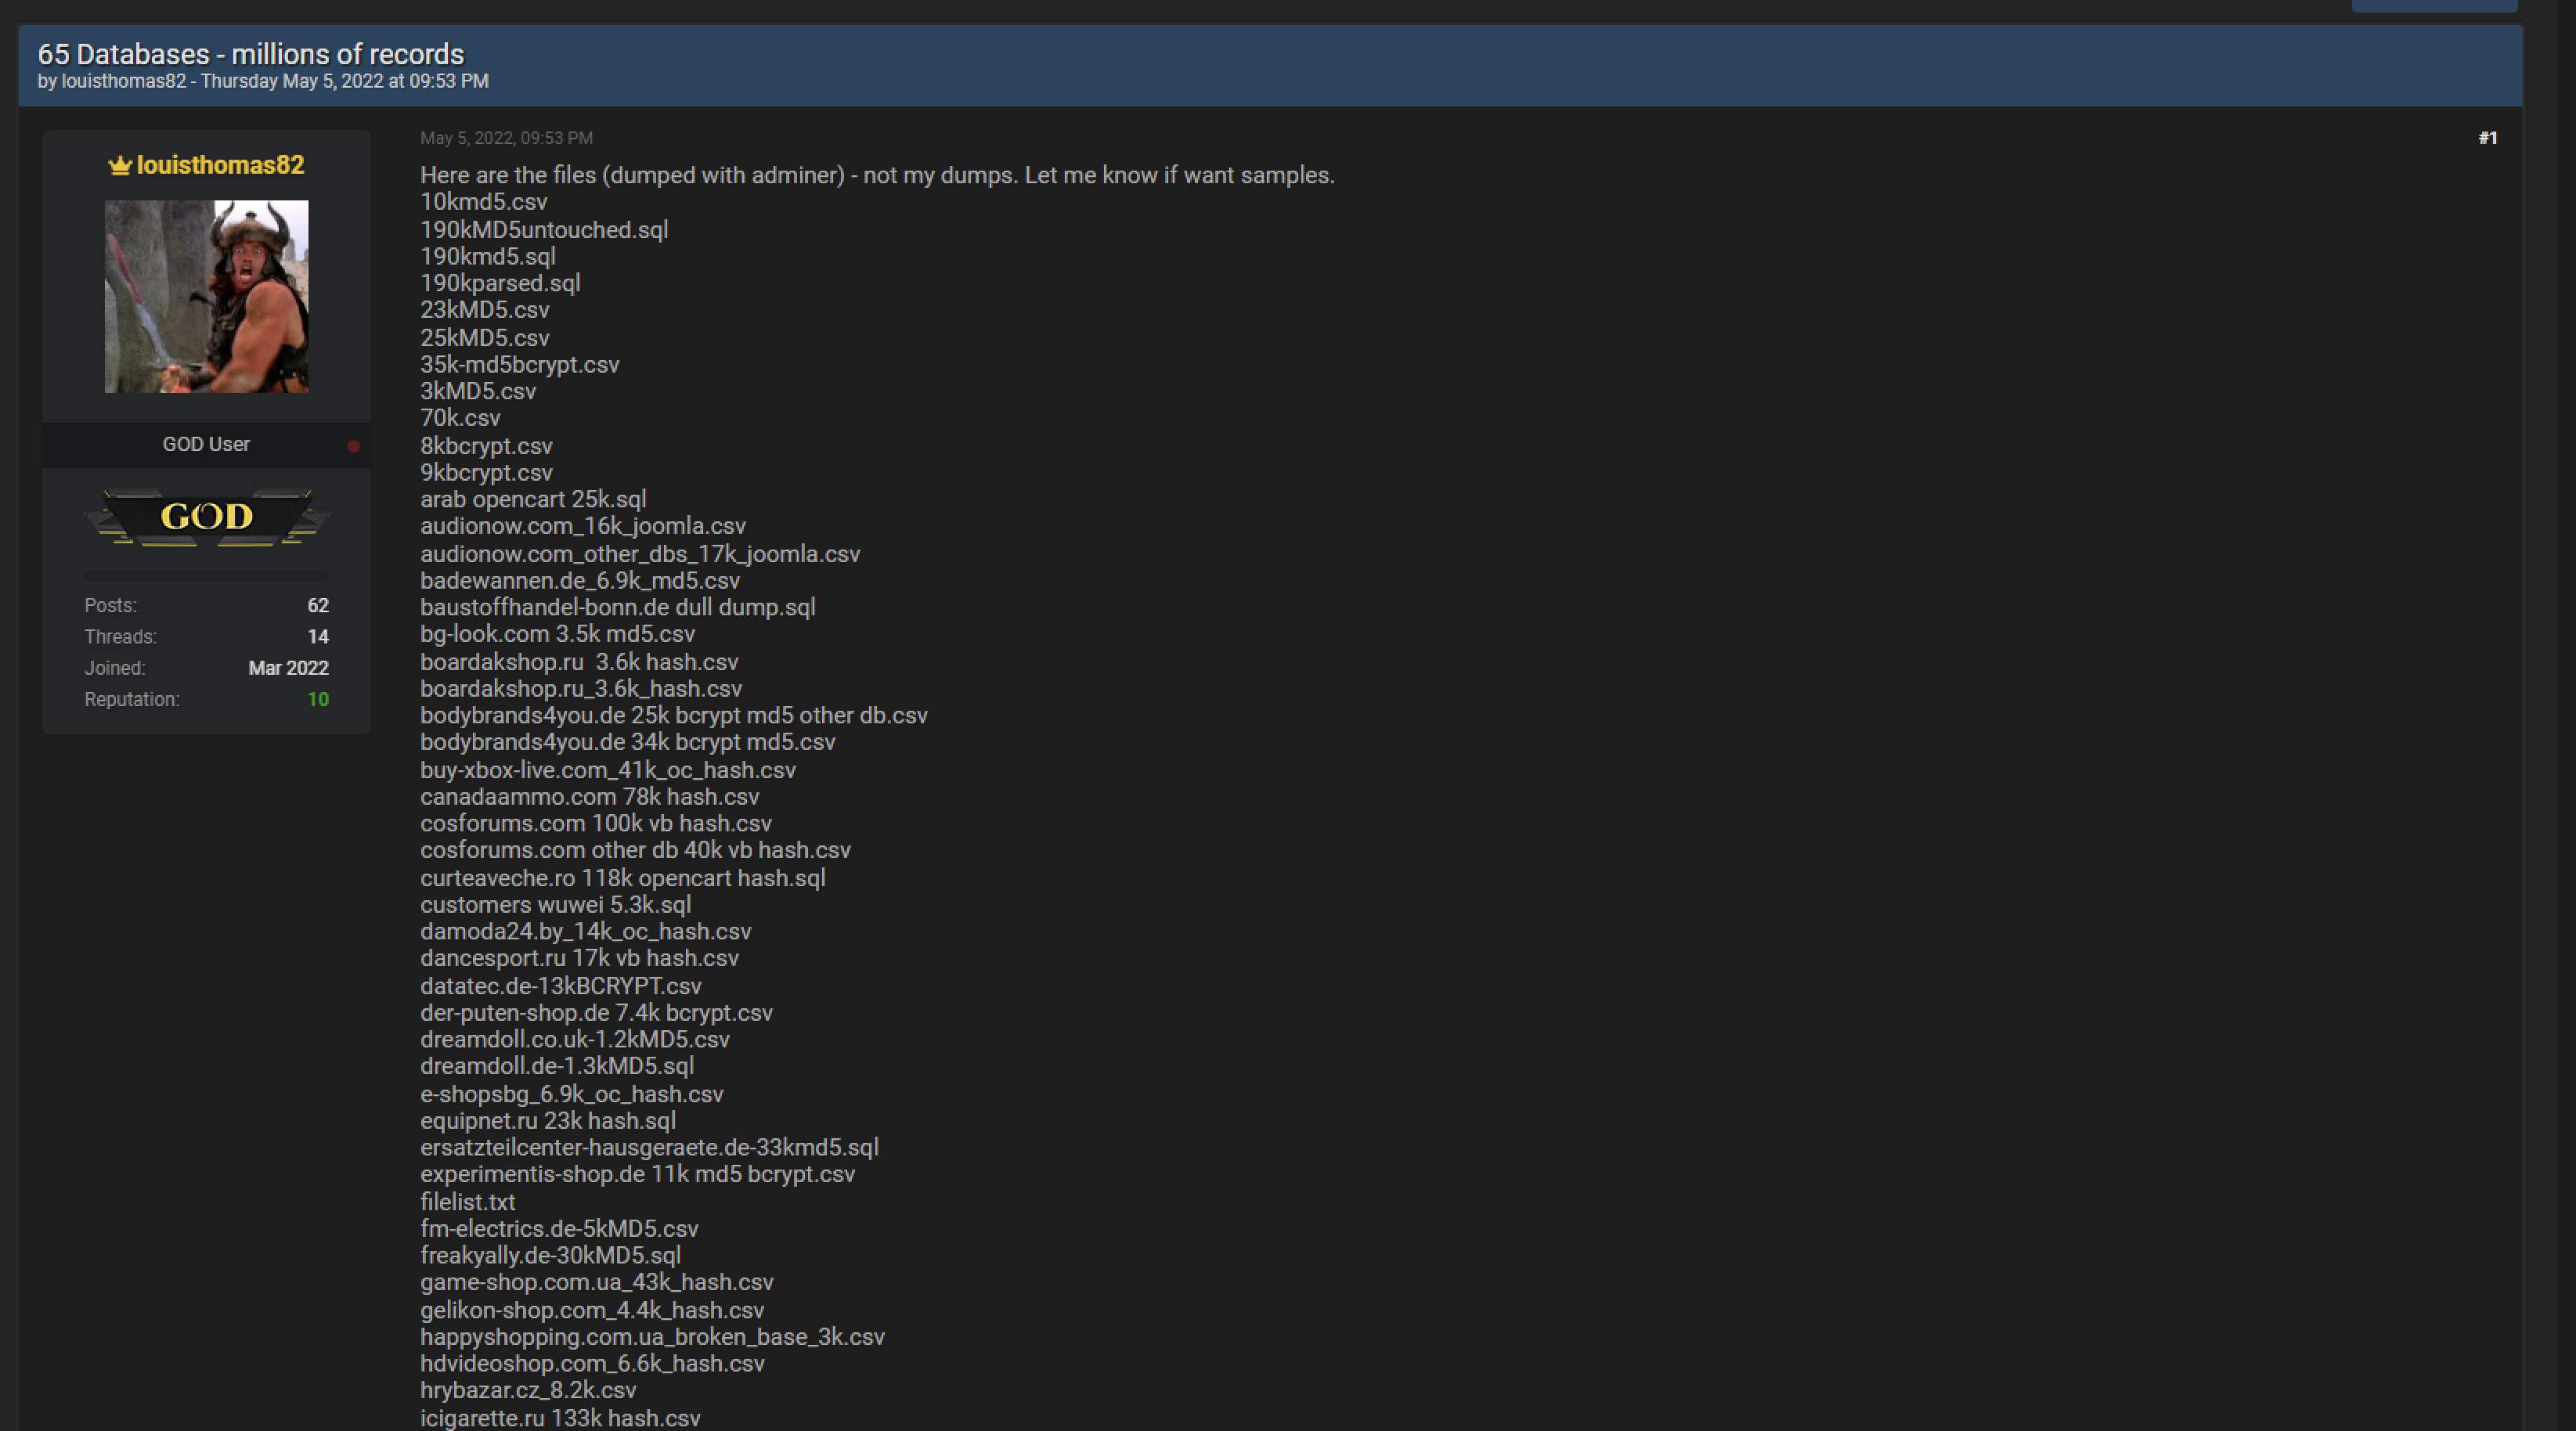
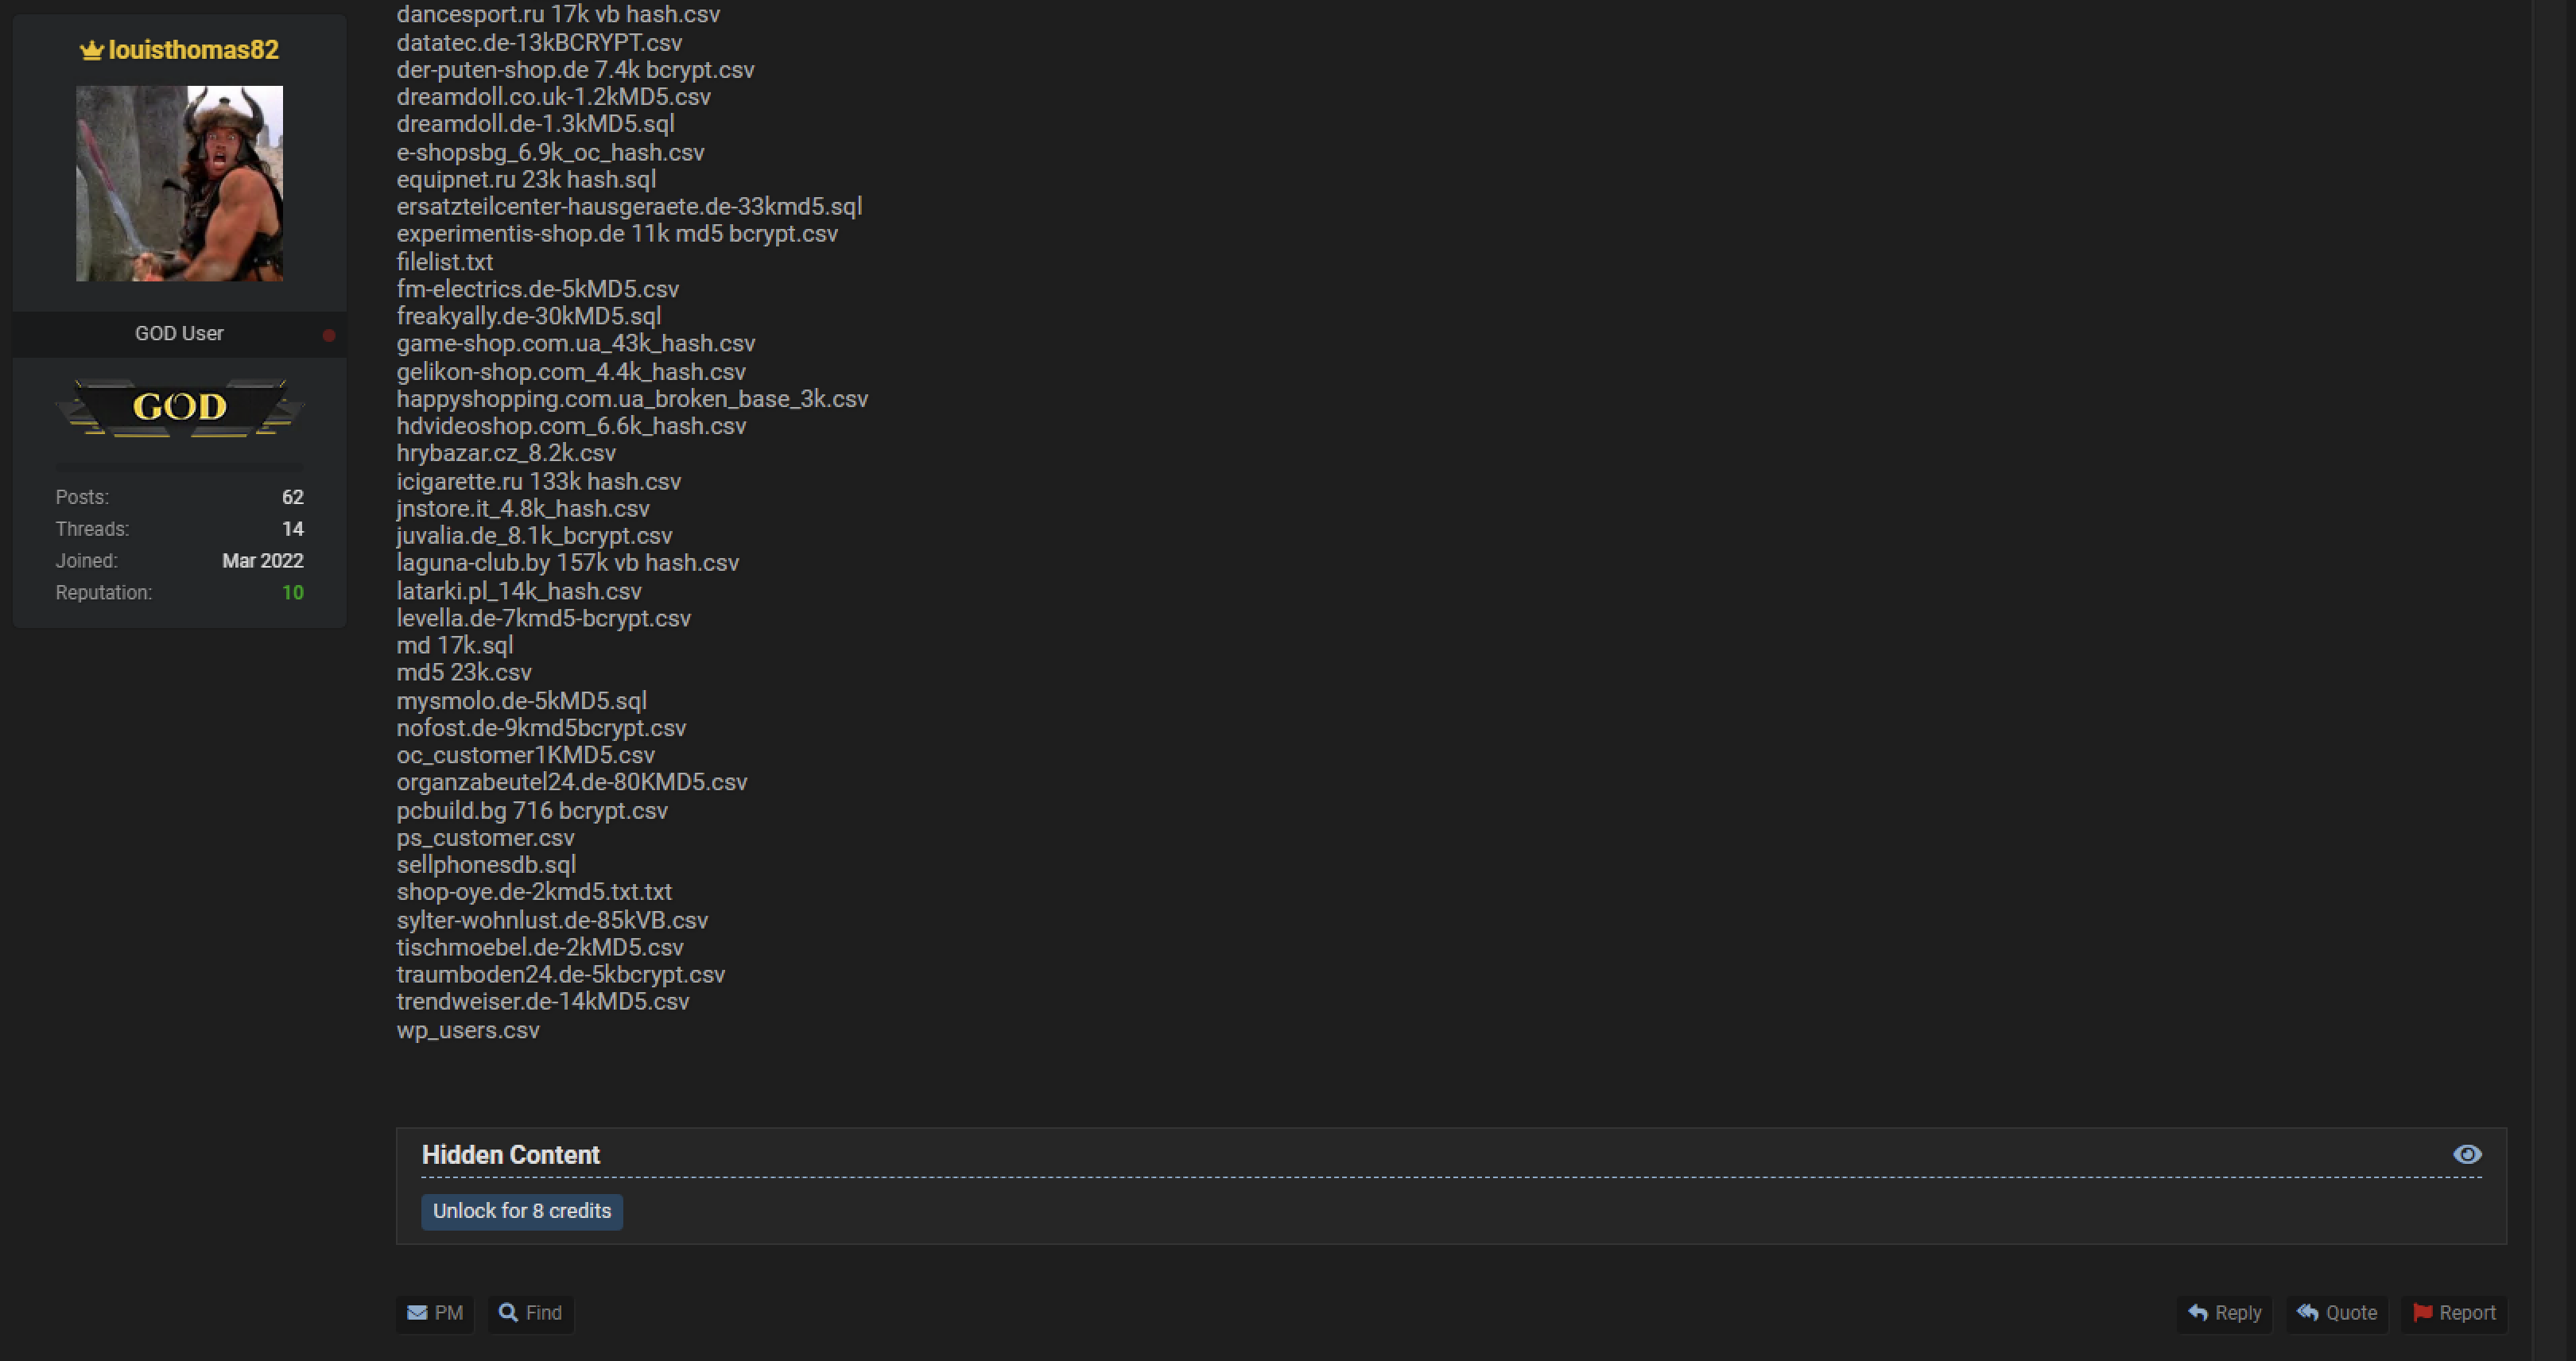
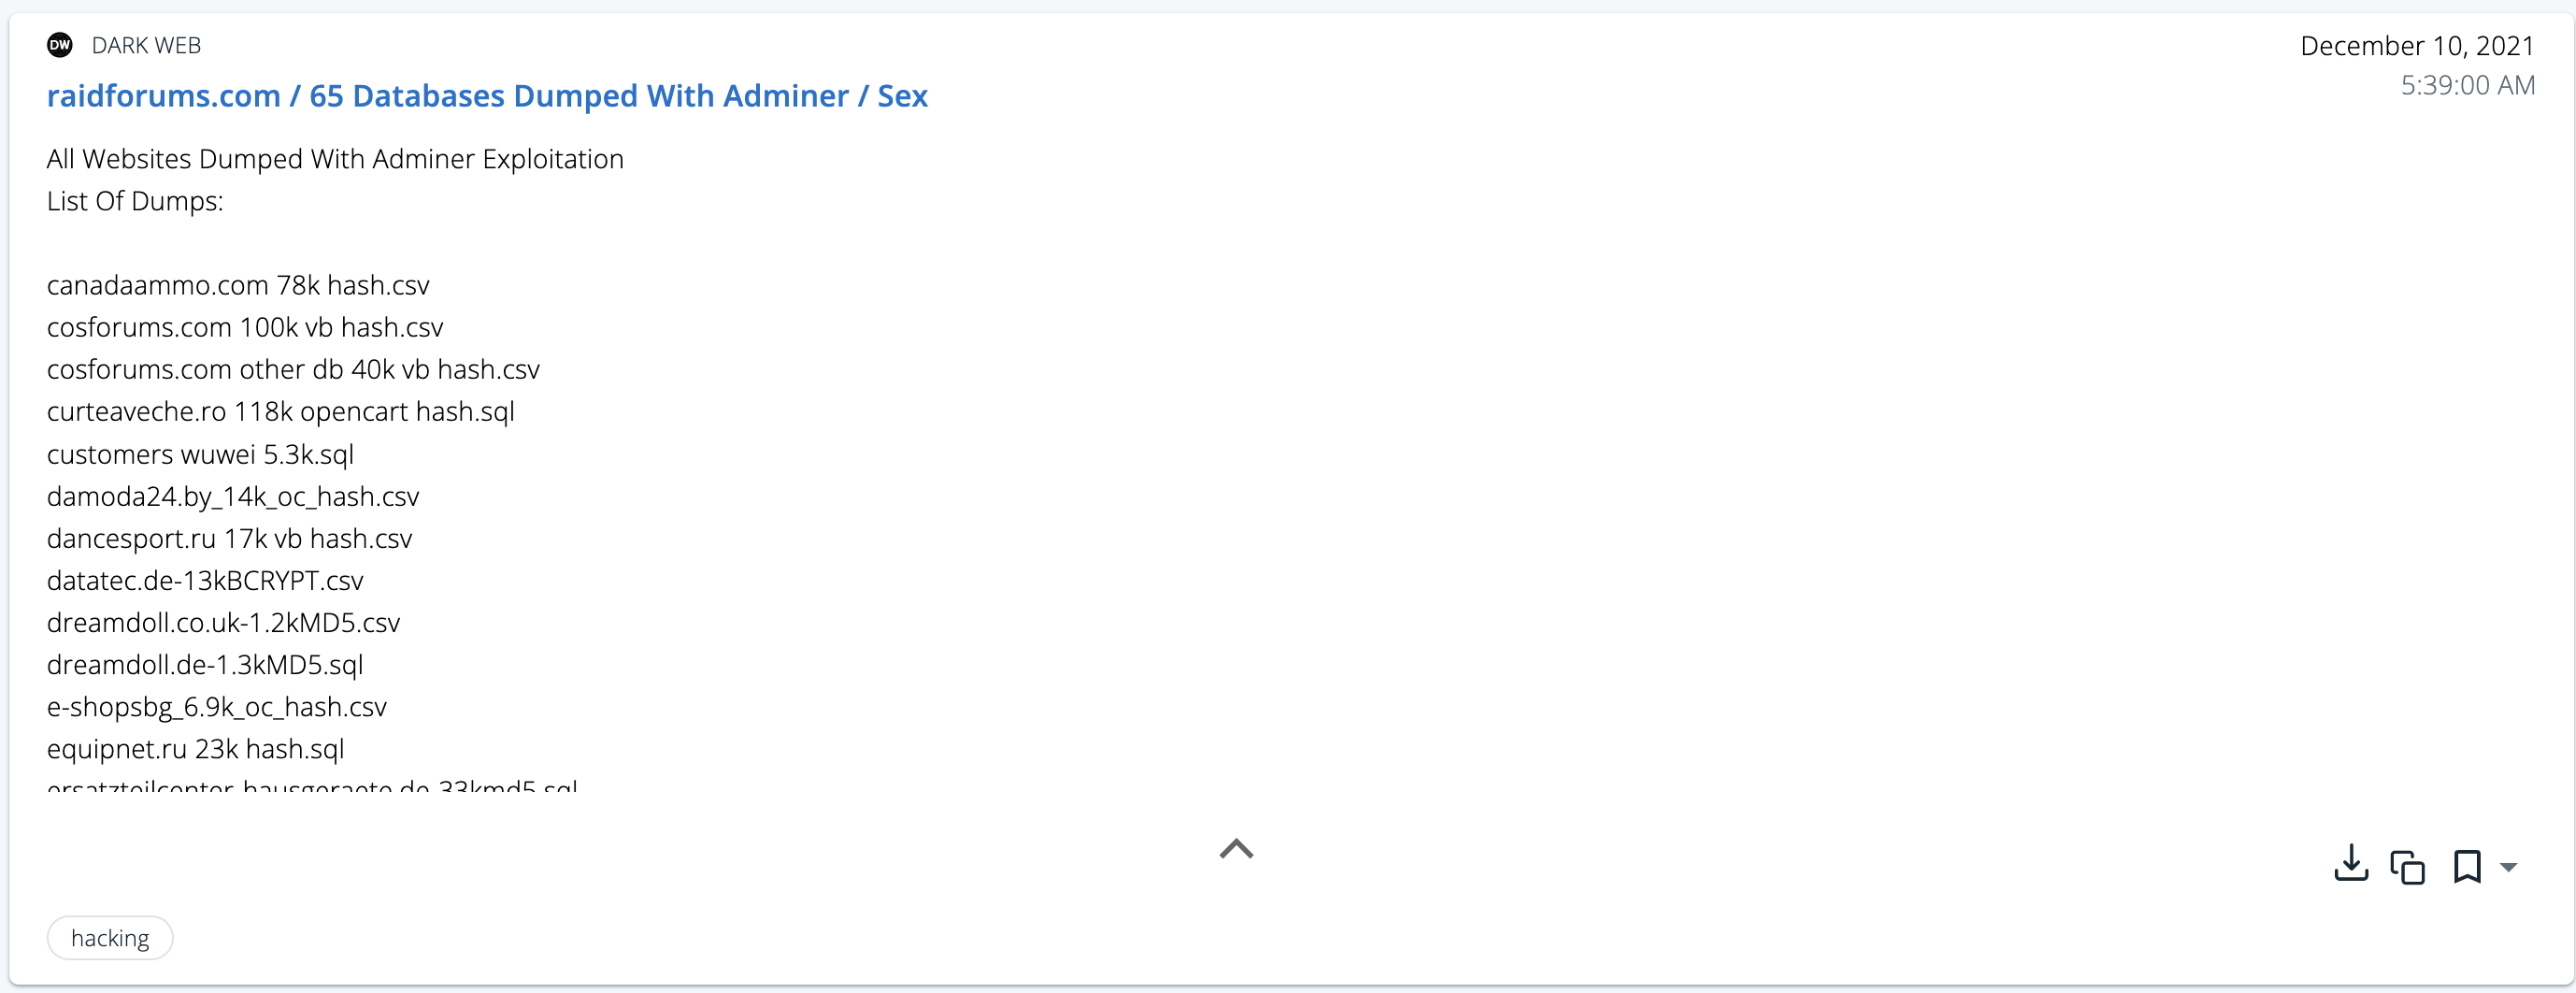
On May 5, 2022, a reputed threat actor "louisthomas82" from the BreachForums posted a data breach package targeting AudioNow (audionow[.]com), a U.S.-based audio broadcasting platform and smartphone applications for broadcasters and listeners to share and create content. The threat actor noted that the data breach package includes 65 Databases with millions of records. The database for AudioNow is a part of that 65 databases. The data dump was also circulated in Raid Forums on December 10, 2021 by the threat actor "Sex". From the package on BreachForums, ZeroFox extracted 18,259 usernames and/or email addresses. Of this total, an assessed 14,190 records contained hashed passwords.
Recommendations
- If not already enabled, turn on the compromised credentials rule for all relevant entities and ensure relevant emails are entered for those entities, or reach out to [email protected] for assistance
- If one of your entities receives an alert, ZeroFox recommends immediate password changes for the affected account
- Enable 2-factor authentication for all of your organizational accounts to help mitigate phishing and credential stuffing attacks
Breach Disclosure: 66M MailPass
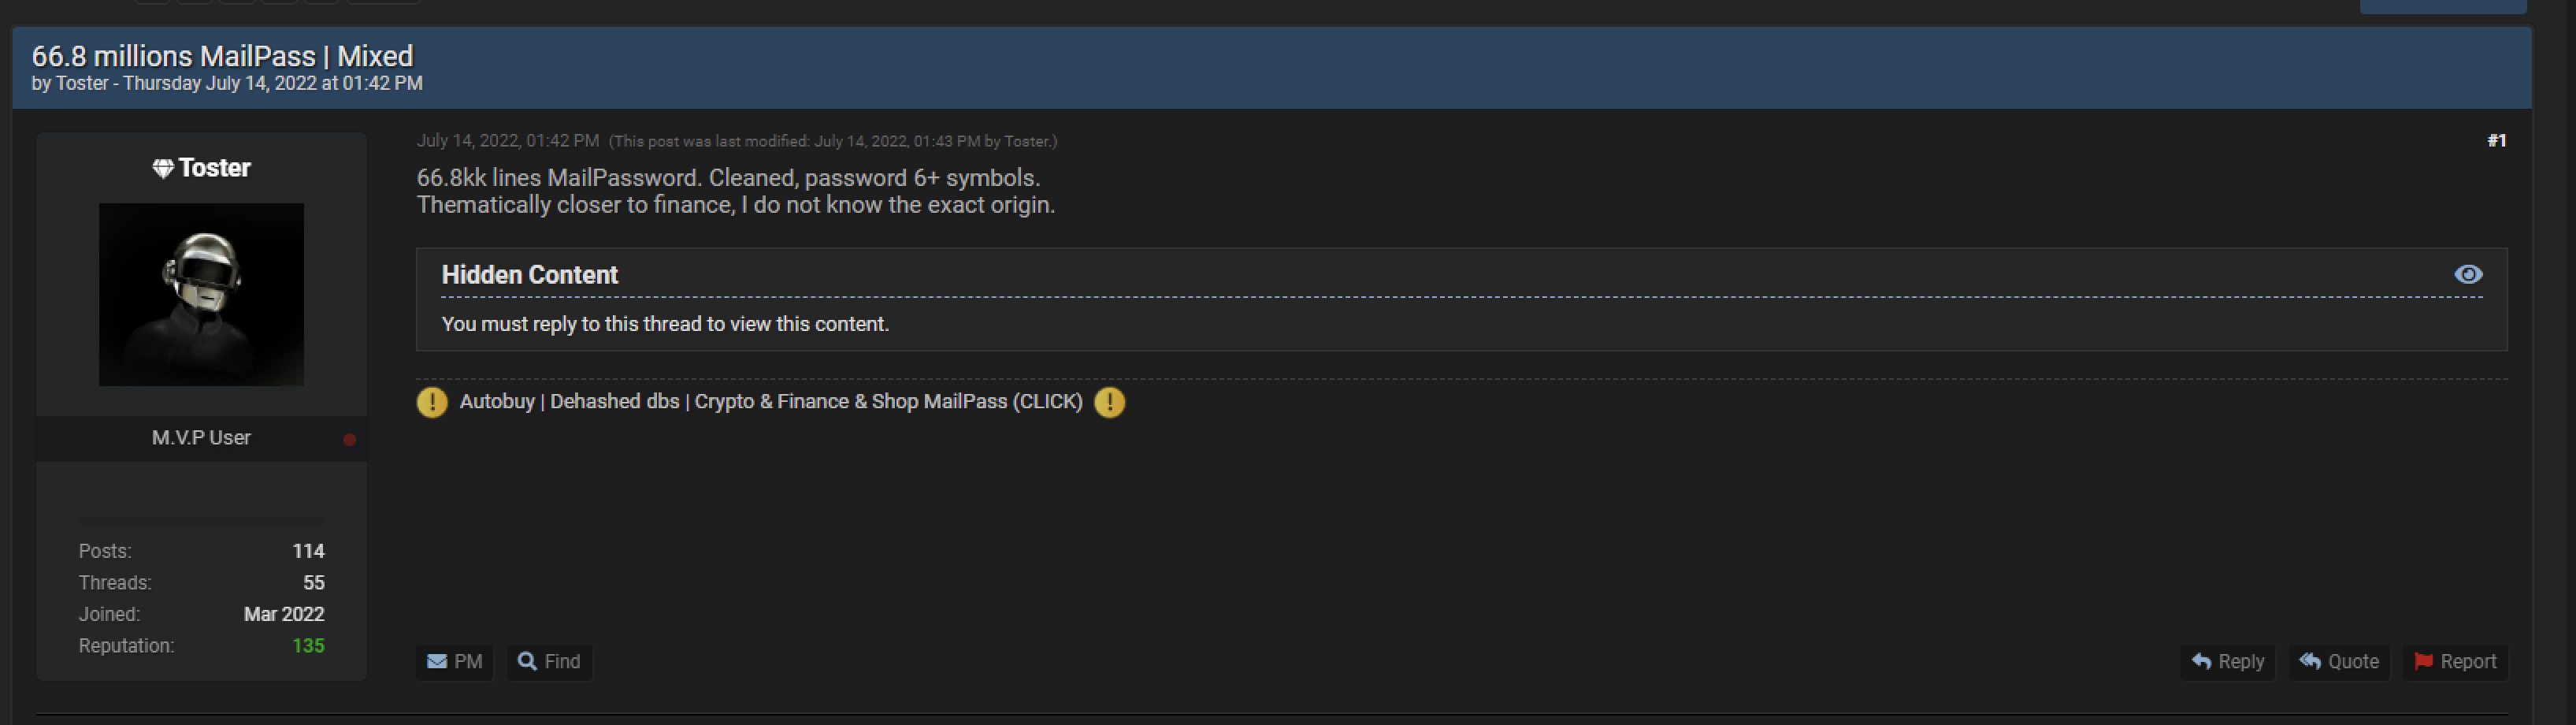
On July 14, 2022, a reputed threat actor "Toster" from the BreachForums posted a combo list package titled "66.8 millions MailPass | Mixed". From this package, ZeroFox extracted 66,763,793 email addresses and plain-text passwords.
Standing Intelligence Requirements
For the most up to date list of ZeroFox Threat Research’s Intelligence Requirements, please visit:
https://cloud.zerofox.com/alpha_team/advisories/14956
Details
On July 14, 2022, a reputed threat actor "Toster" from the BreachForums posted a combo list package titled "66.8 millions MailPass | Mixed". The alert you received was from the acquisition and ingestion of what is known as a "combolist" that was being shared on a Dark Web forum. A combolist is a list of compromised login credentials containing user’s email addresses and passwords. Combolists are often generated by threat actors from a variety of sources to be used in credential stuffing attacks. The login credentials in these lists often come from a threat actor compiling data from previous breaches or exposures to take advantage of user’s who re-use their password on multiple websites or have not changed their password since it was exposed. ZeroFox emphasizes that threat actors often misrepresent the authenticity of some email and password combinations and in some cases completely make up passwords on these lists. From this package, ZeroFox extracted 66,763,793 email addresses and plain-text passwords.
Recommendations
- If not already enabled, turn on the compromised credentials rule for all relevant entities and ensure relevant emails are entered for those entities, or reach out to [email protected] for assistance
- If one of your entities receives an alert, ZeroFox recommends immediate password changes for the affected account
- Enable 2-factor authentication for all of your organizational accounts to help mitigate phishing and credential stuffing attacks
Breach Disclosure: Labor Exchange
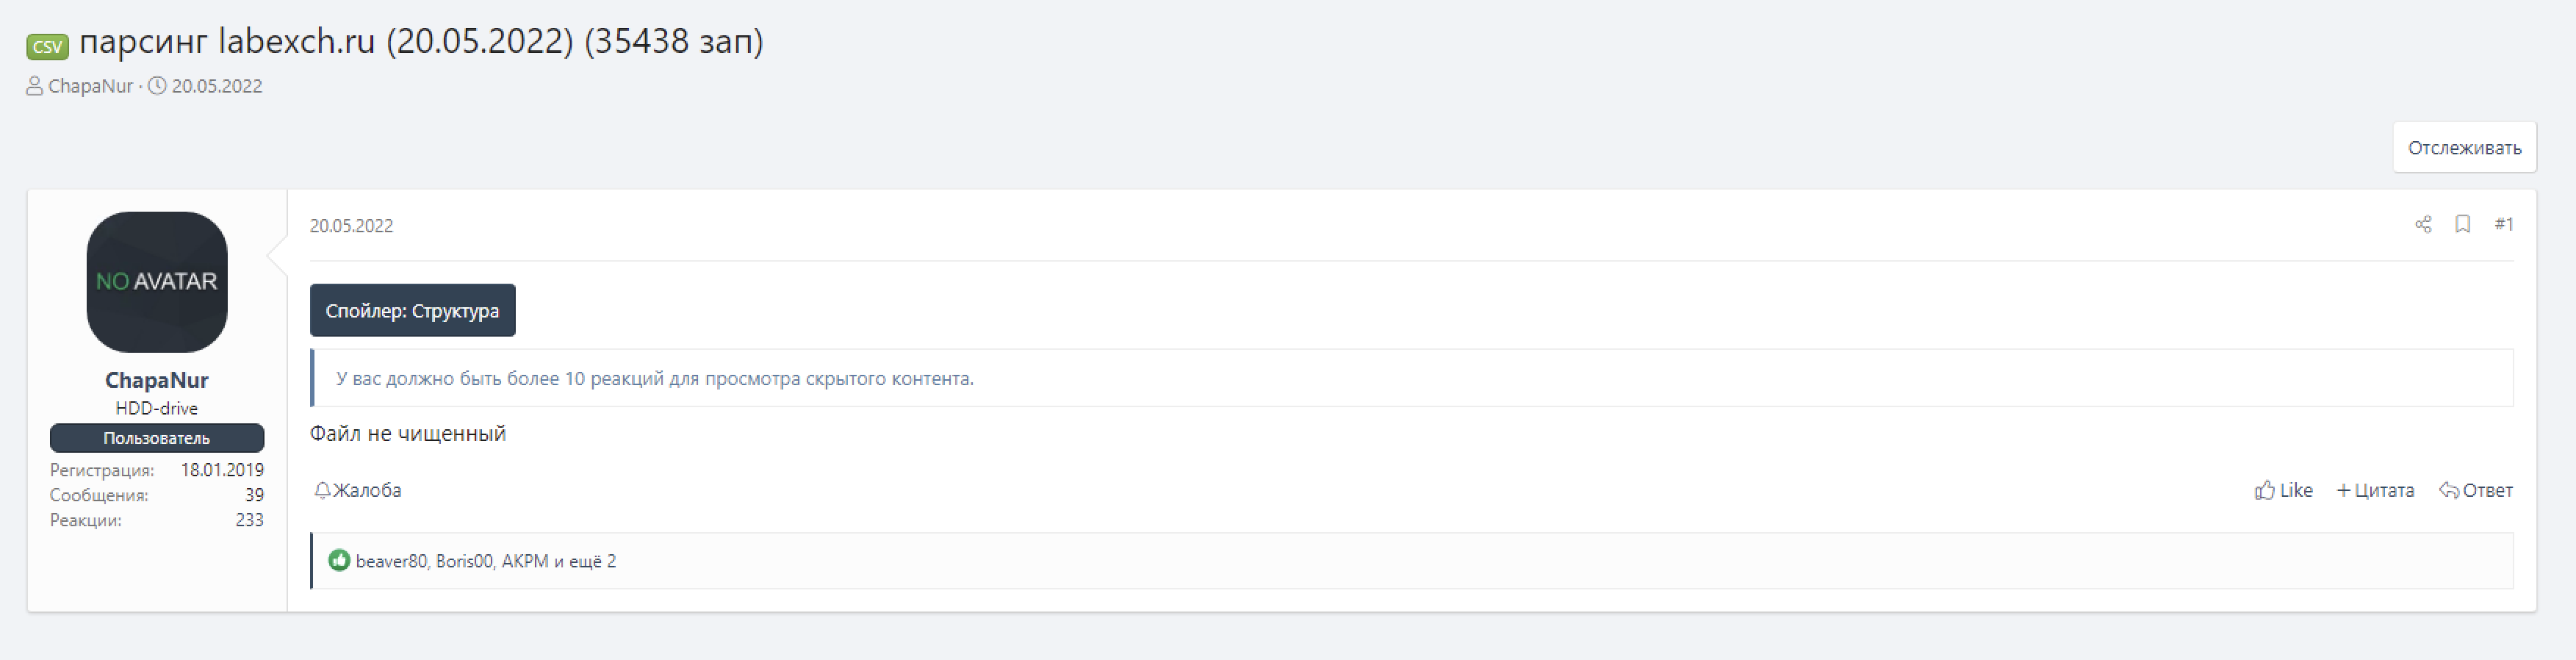
On May 20, 2022, a user level threat actor "ChapaNur" from the Russian language deep web forum XSS posted a data breach package targeting the organization Labor Exchange, a moderated electronic job portal which does the labor exchange for multiple cities in different countries. From this package, ZeroFox extracted 33,604 email addresses.
Standing Intelligence Requirements
For the most up to date list of ZeroFox Threat Research’s Intelligence Requirements, please visit:
https://cloud.zerofox.com/alpha_team/advisories/14956
Details
On May 20, 2022, a user level threat actor "ChapaNur" from the Russian language deep web forum XSS posted a data breach package targeting the organization Labor Exchange (labexch[.]ru), a moderated electronic job portal which does the labor exchange for multiple cities in different countries. From this package, ZeroFox extracted 33,604 email addresses. No passwords were found in this breach.
Recommendations
- If not already enabled, turn on the compromised credentials rule for all relevant entities and ensure relevant emails are entered for those entities, or reach out to [email protected] for assistance
- If one of your entities receives an alert, ZeroFox recommends immediate password changes for the affected account
- Enable 2-factor authentication for all of your organizational accounts to help mitigate phishing and credential stuffing attacks
Breach Disclosure: CTARS
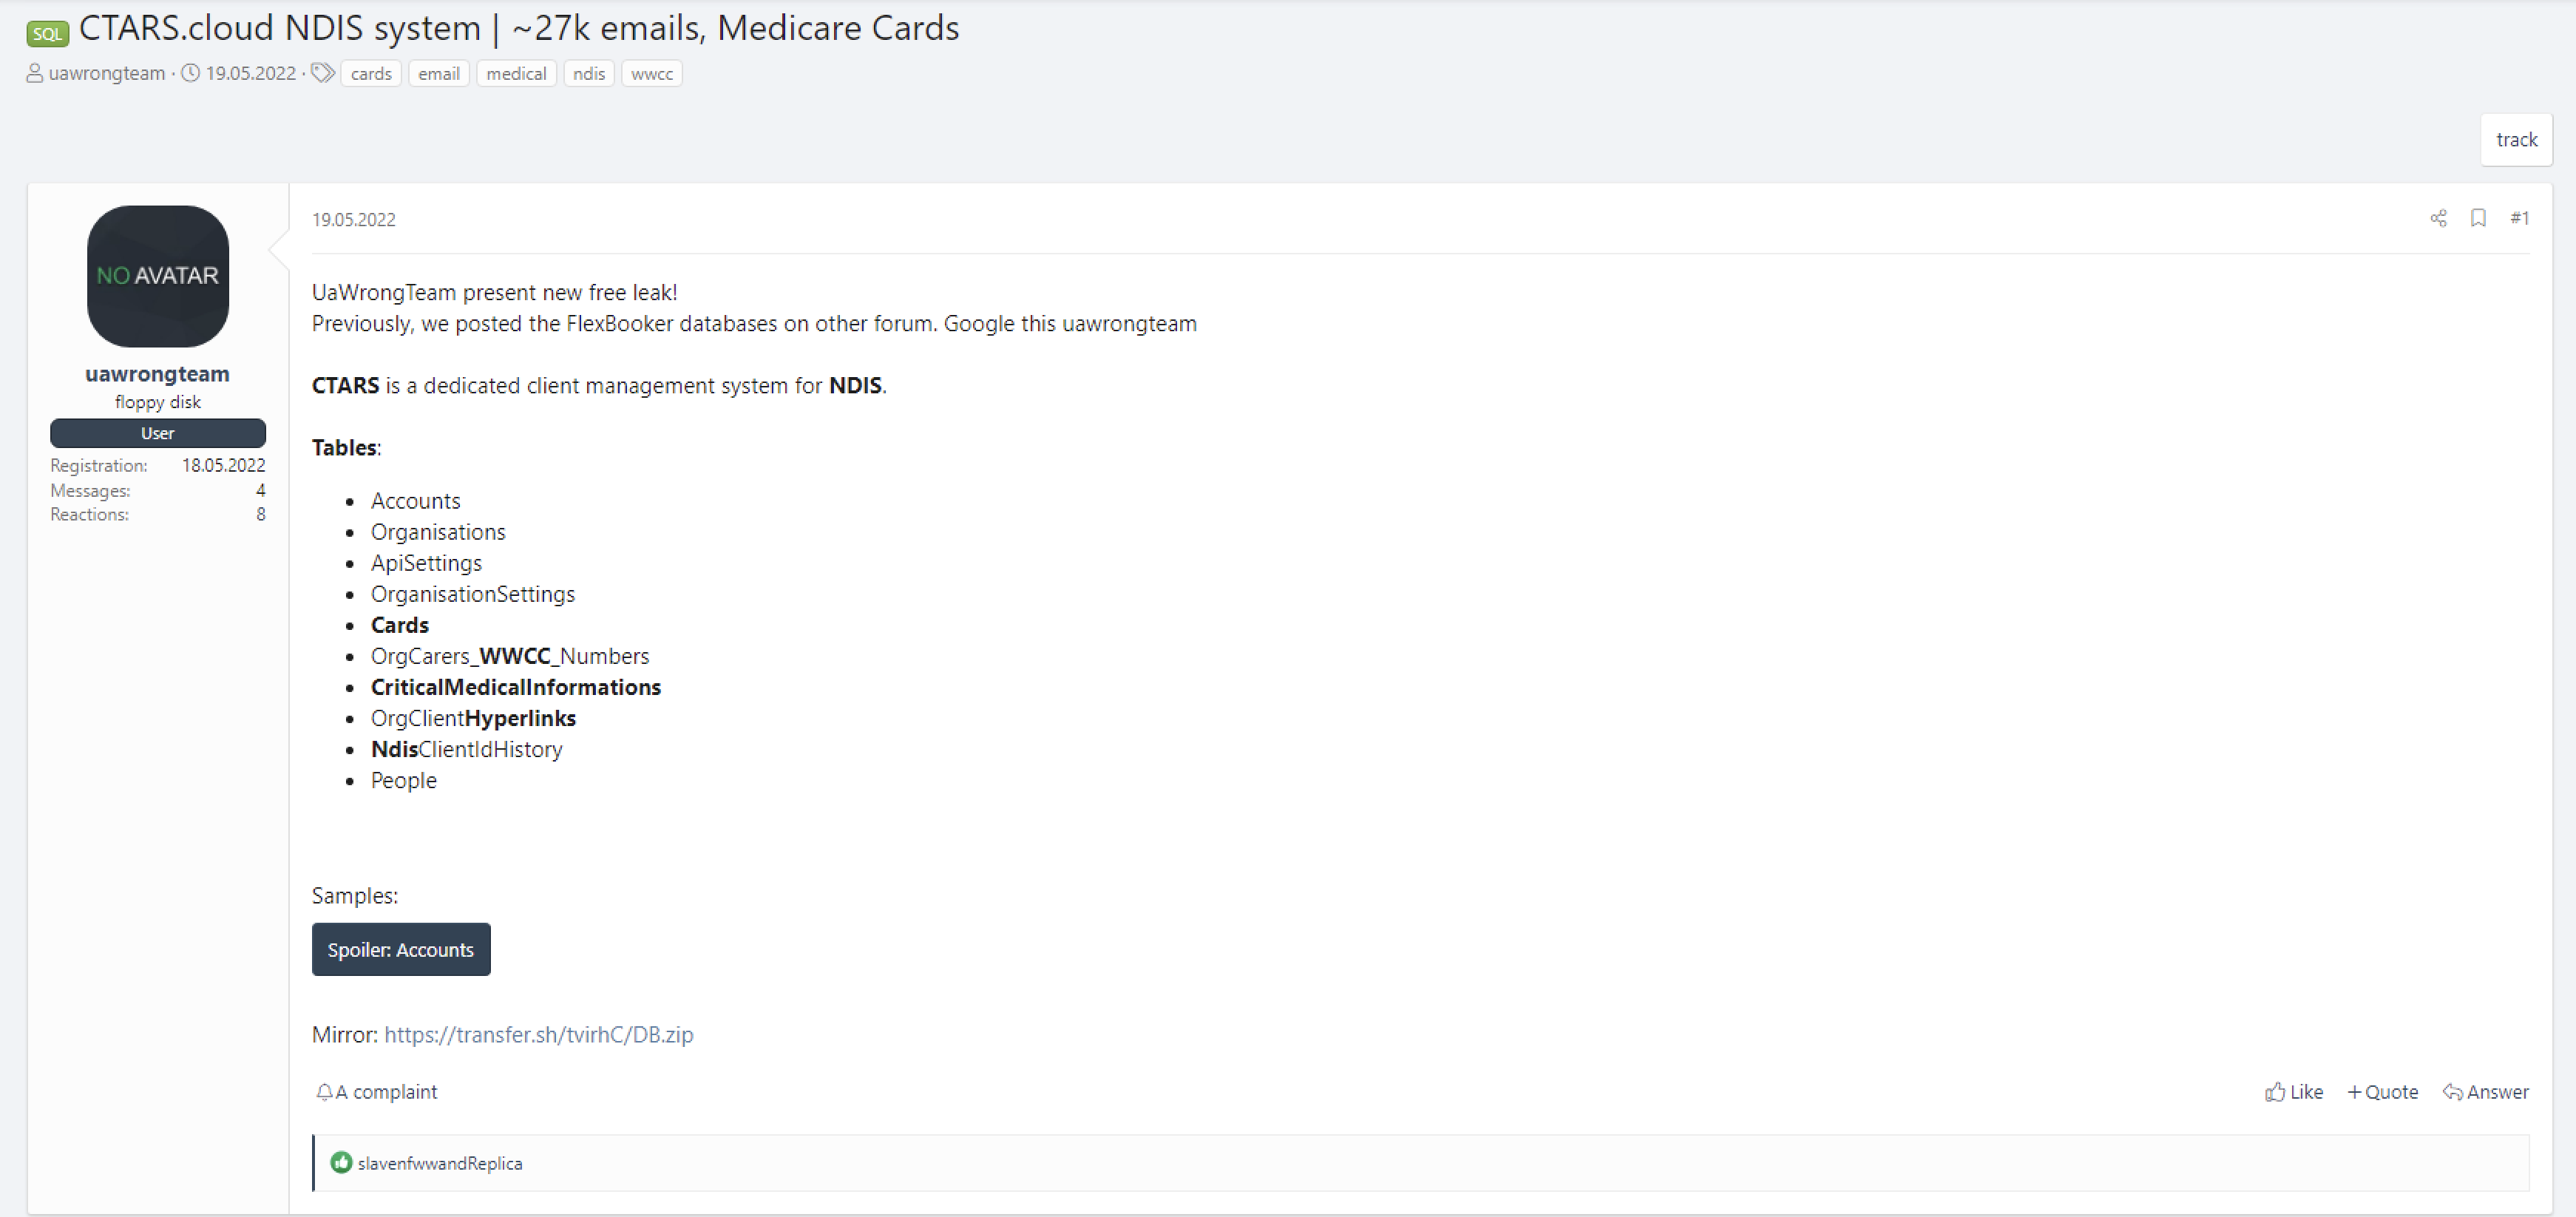
On May 19, 2022, a recently registered threat actor "uawrongteam" from the Russian language deep web forum XSS posted a data breach package targeting CTARS (ctars[.]cloud), a cloud-based client management system and operational service solution provider operating from Singapore. From the package on XSS, ZeroFox extracted 70,828 usernames and/or email addresses.
Standing Intelligence Requirements
For the most up to date list of ZeroFox Threat Research’s Intelligence Requirements, please visit:
https://cloud.zerofox.com/alpha_team/advisories/14956
Details
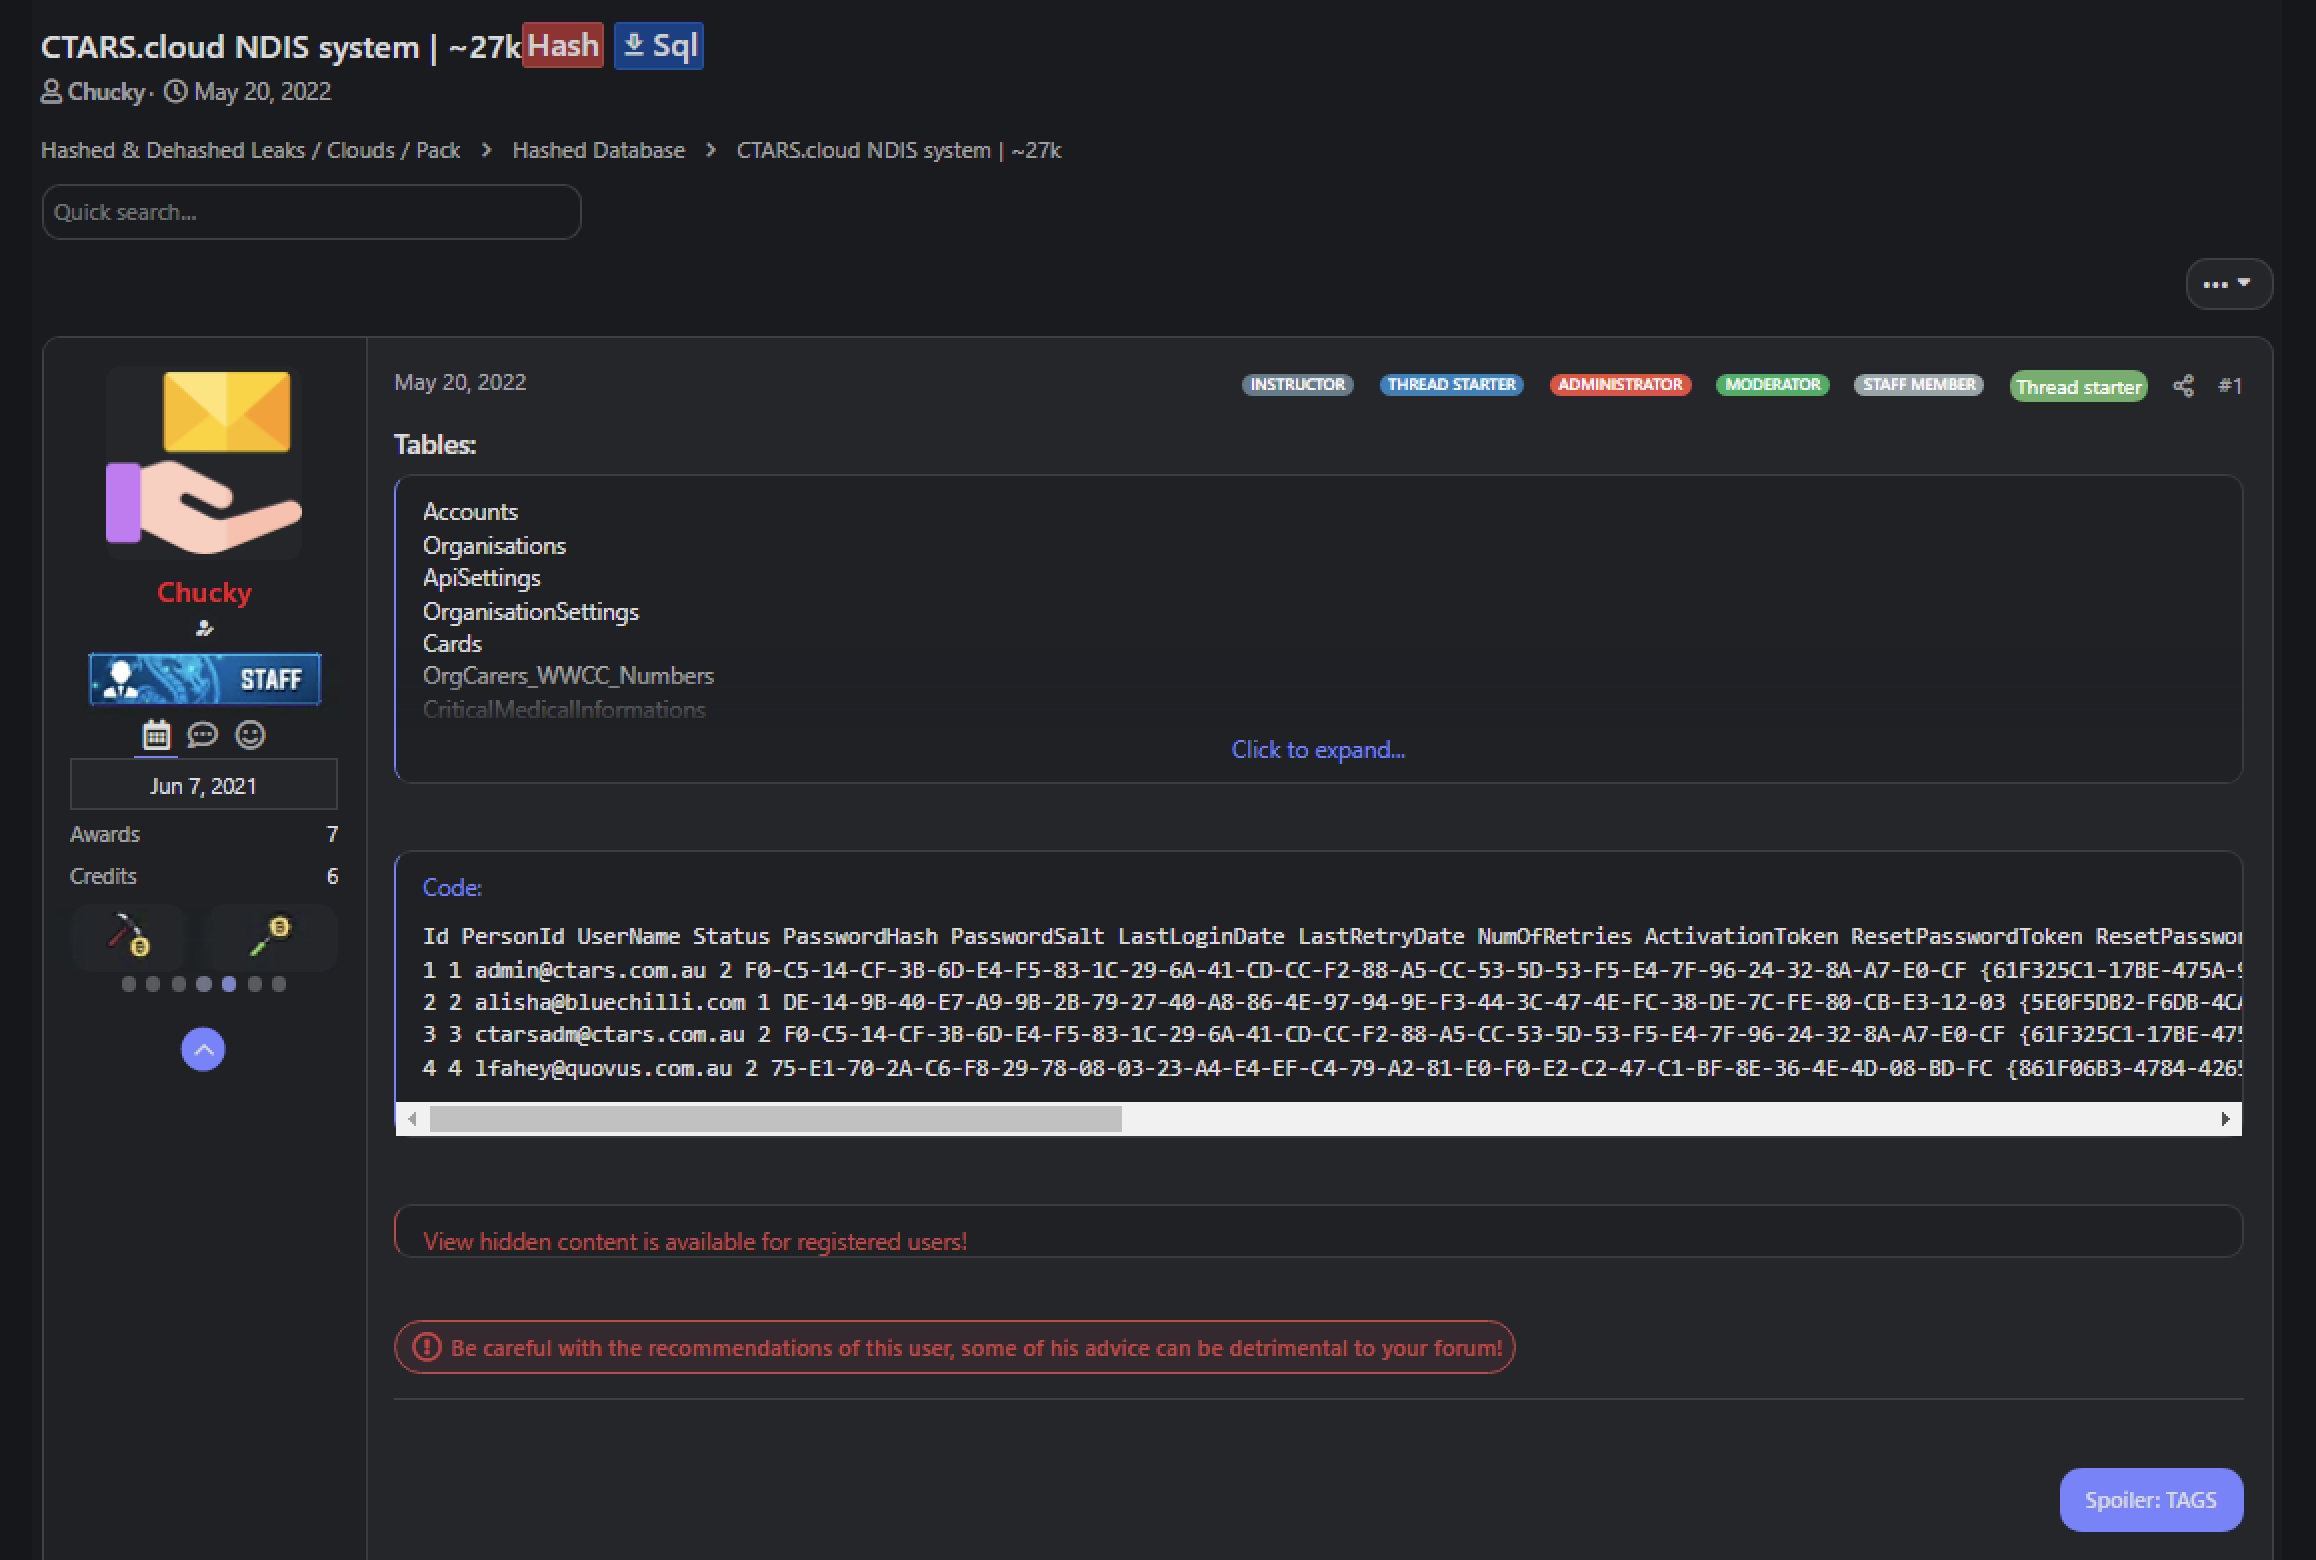
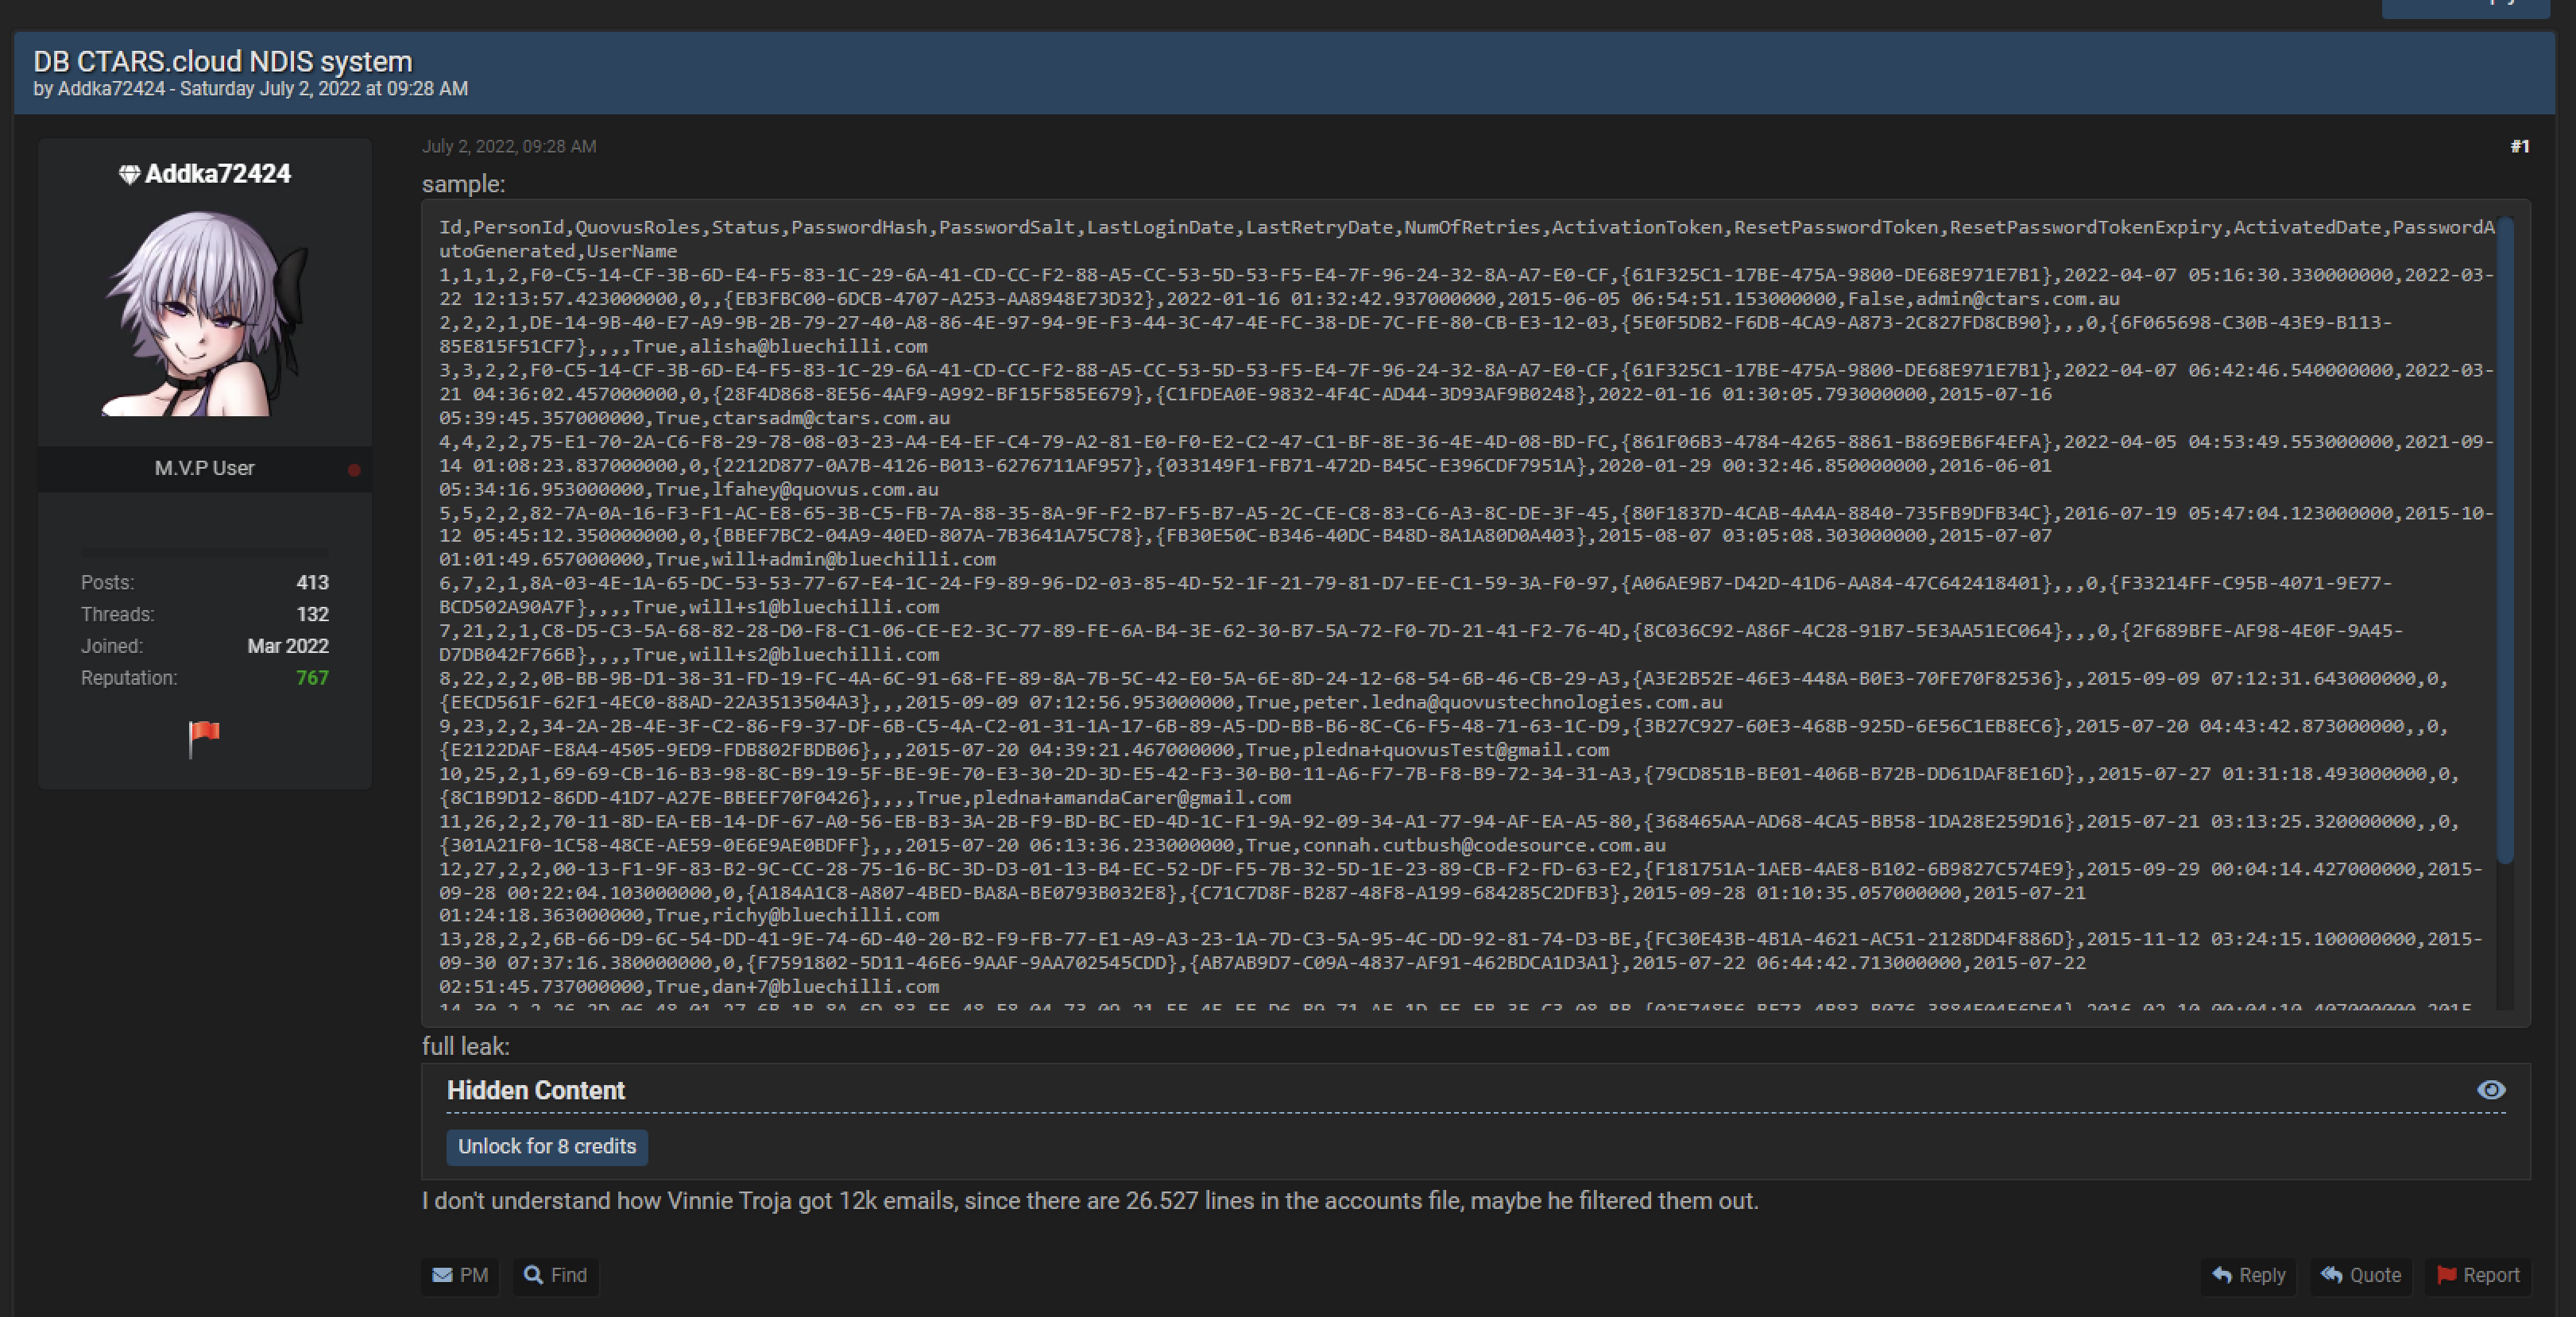
On May 19, 2022, a recently registered threat actor "uawrongteam" from the Russian language deep web forum XSS posted a data breach package targeting CTARS (ctars[.]cloud), a cloud-based client management system and operational service solution provider operating from Singapore. The threat actor noted that the data dump includes 27k user emails. The data dump was also circulated in deep web forums like Leakbase on May 20, 2022 by the threat actor "Chucky" and in BreachForums on July 2, 2022 by the threat actor "Addka72424". From the package on XSS, ZeroFox extracted 70,828 usernames and/or email addresses. Of this total, an assessed 11,806 records contained hashed passwords.
Recommendations
- If not already enabled, turn on the compromised credentials rule for all relevant entities and ensure relevant emails are entered for those entities, or reach out to [email protected] for assistance
- If one of your entities receives an alert, ZeroFox recommends immediate password changes for the affected account
- Enable 2-factor authentication for all of your organizational accounts to help mitigate phishing and credential stuffing attacks
Breach Disclosure: Damoda24
On May 5, 2022, a reputed threat actor "louisthomas82" from the BreachForums posted a data breach package targeting Damoda24, an online clothing store operating from Belarus. From this package, ZeroFox extracted 13,964 email addresses and hashed passwords.
Standing Intelligence Requirements
For the most up to date list of ZeroFox Threat Research’s Intelligence Requirements, please visit:
https://cloud.zerofox.com/alpha_team/advisories/14956
Details
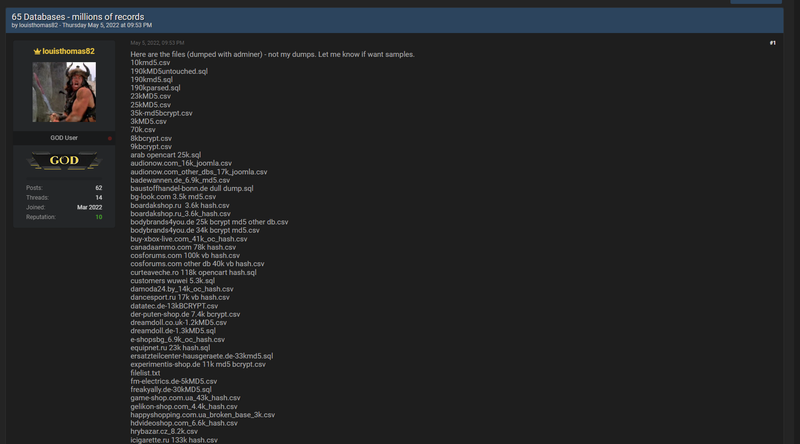
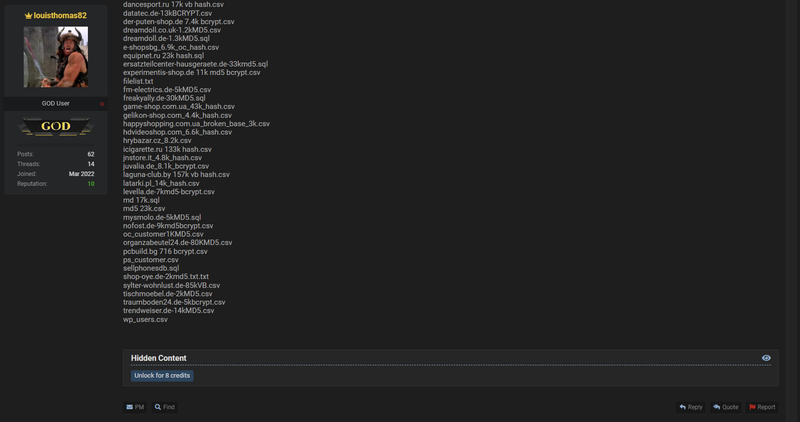
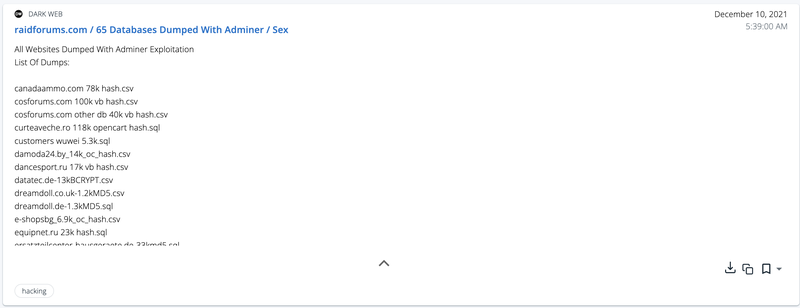
On May 5, 2022, a reputed threat actor "louisthomas82" from the BreachForums posted a data breach package targeting Damoda24 (damoda24[.]by), an online clothing store operating from Belarus. The threat actor noted that the data breach package includes 65 Databases with millions of records. The database for Damoda24 is a part of that 65 database. The data dump was also circulated in Raid Forums on December 10, 2021 by the threat actor "Sex". From this package, ZeroFox extracted 13,964 email addresses and hashed passwords.
Recommendations
- If not already enabled, turn on the compromised credentials rule for all relevant entities and ensure relevant emails are entered for those entities, or reach out to [email protected] for assistance
- If one of your entities receives an alert, ZeroFox recommends immediate password changes for the affected account
- Enable 2-factor authentication for all of your organizational accounts to help mitigate phishing and credential stuffing attacks
Breach Disclosure: Baustoffhandel Bonn
On May 5, 2022, a reputed threat actor "louisthomas82" from the deep web forum BreachForums posted a data breach package targeting Baustoffhandel Bonn, an online store for construction materials operating from Germany. From this package, ZeroFox extracted 2,348 email addresses.
Standing Intelligence Requirements
For the most up to date list of ZeroFox Threat Research’s Intelligence Requirements, please visit:
https://cloud.zerofox.com/alpha_team/advisories/14956
Details
On May 5, 2022, a reputed threat actor "louisthomas82" from the deep web forum BreachForums posted a data breach package targeting Baustoffhandel Bonn (baustoffhandel-bonn[.]de), an online store for construction materials operating from Germany. The threat actor noted that the data breach package includes 65 Databases with millions of records. The database for Baustoffhandel Bonn is a part of that 65 databases. The data dump was also circulated in Raid Forums on December 10, 2021 by the threat actor "Sex". From this package, ZeroFox extracted 2,348 email addresses. Of this total, an assessed 967 records contained hashed passwords.
Recommendations
- If not already enabled, turn on the compromised credentials rule for all relevant entities and ensure relevant emails are entered for those entities, or reach out to [email protected] for assistance
- If one of your entities receives an alert, ZeroFox recommends immediate password changes for the affected account
- Enable 2-factor authentication for all of your organizational accounts to help mitigate phishing and credential stuffing attacks
Breaking News: 2022-08-26 - 2022-09-01
Microsoft: Russian malware hijacks ADFS to log in as anyone in Windows
A new malware called MagicWeb, which enables authentication as anyone in a compromised network, is being used by the Russian threat group APT29 (a.k.a. NOBELIUM and Cozy Bear). APT29 reportedly employs the new capability to hide their presence on the networks of their targets, typically government and critical organizations across Europe, the United States, and Asia.
See the full report here: https://www.bleepingcomputer.com/news/security/microsoft-russian-malware-hijacks-adfs-to-log-in-as-anyone-in-windows/
PyPI packages hijacked after developers fall for phishing emails
PyPI has taken down hijacked versions of packages “spam” (versions 2.0.2 and 4.0.2) and “exotel” (version 0.1.6) – after some developers fell for a phishing campaign that led to their creations getting hijacked and laced with malware. PyPI admins stated that they had identified and removed "several hundred typosquats,” actively reviewing reports of new malicious releases, and ensuring that the malicious releases are removed and the maintainer accounts restored.
See the full report here: https://www.bleepingcomputer.com/news/security/pypi-packages-hijacked-after-developers-fall-for-phishing-emails/
Hackers adopt Sliver toolkit as a Cobalt Strike alternative
Threat actors are increasingly using the open-source, cross-platform kit Sliver in place of the Cobalt Strike penetration testing suite. The Sliver command-and-control (C2) framework is reportedly being adopted and integrated in intrusion campaigns by nation-state threat actors, cybercrime groups directly supporting ransomware and extortion, and other threat actors to evade detection.
See the full report here: https://www.bleepingcomputer.com/news/security/hackers-adopt-sliver-toolkit-as-a-cobalt-strike-alternative/
How Kimsuky hackers ensure their malware only reach valid targets
Security researchers have reported details of Kimsuky (also known as Thallium, Black Banshee and Velvet Chollima), which is a prolific threat actor primarily targeting South Korea. The group’s safeguards – to ensure that its payloads run only on the target systems and not on the systems of security researchers – are so effective that researchers find it challenging to acquire the final payloads even after successfully connecting to the threat actor’s command and control server.
See the full report here: https://www.bleepingcomputer.com/news/security/how-kimsuky-hackers-ensure-their-malware-only-reach-valid-targets/
LastPass developer systems hacked to steal source code
Password management firm LastPass suffered a cyberattack that enabled threat actors to steal the company's source code and proprietary technical information. LastPass stated that there is no evidence that customer data or encrypted password vaults were compromised.
See the full report here: https://www.bleepingcomputer.com/news/security/lastpass-developer-systems-hacked-to-steal-source-code/
Hackers abuse Genshin Impact anti-cheat system to disable antivirus
mhyprot2.sys, an anti-cheat driver for the role-playing game Genshin Impact, is being abused by a ransomware actor to kill antivirus processes and services for mass-deploying ransomware.
See the full report here: https://www.bleepingcomputer.com/news/security/hackers-abuse-genshin-impact-anti-cheat-system-to-disable-antivirus/
Twilio hackers hit over 130 orgs in massive Okta phishing attack
Hackers responsible for a string of recent cyberattacks, including those on Twilio, MailChimp, and Klaviyo, compromised over 130 organizations in the same phishing campaign. This phishing campaign used a phishing kit codenamed “0ktapus” to steal 9,931 login credentials that the hackers then used to gain access to corporate networks and systems through VPNs and other remote access devices.
See the full report here: https://www.bleepingcomputer.com/news/security/twilio-hackers-hit-over-130-orgs-in-massive-okta-phishing-attack/
This malware is deadly and you could receive it in your mailbox at home
A British pensioner received a letter at home with an infected flash drive, completely camouflaged as a Microsoft promotion.
See the full report here: https://www.gearrice.com/update/this-malware-is-deadly-and-you-could-receive-it-in-your-mailbox-at-home/
India’s Akasa Air exposed sensitive records of thousands of customers
Akasa Air, India’s newly launched airline that began operations earlier this month, exposed the personal data of thousands of its customers because of a technical glitch that affected its login and sign-up service. The exposed data included full names, gender, email addresses and phone numbers of Akasa Air customers.
See the full report here: https://techcrunch.com/2022/08/28/india-akasa-air-sensitive-customer-data-records-exposed-glitch/
Ransomware attacks threaten nations, 137 S'pore firms fell prey in 2021: CSA
The number of firms in Singapore that had their systems locked up until a ransom was paid shot up from 89 in 2020 to 137 last year, said the Cyber Security Agency (CSA) of Singapore. As not every attack was reported, the figures may very well represent only the tip of the iceberg.
See the full report here: https://www.straitstimes.com/tech/tech-news/ransomware-attacks-threaten-nations-137-spore-firms-fell-prey-in-2021-csa
Twilio breach let hackers gain access to Authy 2FA accounts
Twilio’s investigation into its recent data breach revealed that hackers gained access to 93 Authy user accounts and registered unauthorized devices. Authy is a two-factor authentication (2FA) service from Twilio. The company stated that it has removed the unauthorized devices from the compromised accounts and has contacted the affected users to provide instructions on how to protect their accounts.
See the full report here: https://www.bleepingcomputer.com/news/security/twilio-breach-let-hackers-gain-access-to-authy-2fa-accounts/
LockBit ransomware gang gets aggressive with triple-extortion tactic
LockBit ransomware gang announced that it is improving defenses against distributed denial-of-service (DDoS) attacks and working to take the operation to triple-extortion level – adding DDoS as an extortion tactic on top of encrypting data and leaking it. This follows a recent DDoS attack on the gang, allegedly on behalf of digital security firm Entrust.
See the full report here: https://www.bleepingcomputer.com/news/security/lockbit-ransomware-gang-gets-aggressive-with-triple-extortion-tactic/
Twilio breach let hackers see Okta's one-time MFA passwords
The threat actor behind the Twilio hack used their access to steal one-time passwords (OTPs) delivered over SMS from customers of Okta identity and access management company. Okta provides its customers with multiple forms of authentication for services, including temporary codes delivered over SMS through Twilio.
See the full report here: https://www.bleepingcomputer.com/news/security/twilio-breach-let-hackers-see-oktas-one-time-mfa-passwords/
Fake "Cthulhu World" P2E project used to push info-stealing malware
Hackers have created a fake “Cthulhu World” play-to-earn community, including websites, Discord groups, social accounts, and a Medium developer site, to distribute the Raccoon Stealer, AsyncRAT, and RedLine password-stealing malware. People who visited Cthulhu-world.com and downloaded any of their software should immediately run an antivirus scan and remove anything detected, reset all passwords and create new cryptocurrency wallets, and ideally reinstall their computer from scratch.
See the full report here: https://www.bleepingcomputer.com/news/security/fake-cthulhu-world-p2e-project-used-to-push-info-stealing-malware/
CISA: Prepare now for quantum computers, not when hackers use them
The U.S. CISA (Cybersecurity and Infrastructure Security Agency) published a paper calling for industry leaders to start preparing for the migration to stronger secret guarding systems, exploring risk-mitigation methods, and participating in developing new standards. CISA recommends that all stakeholders follow the “post-quantum cryptography roadmap” and not wait to act until quantum computers are in use by adversaries.
See the full report here: https://www.bleepingcomputer.com/news/security/cisa-prepare-now-for-quantum-computers-not-when-hackers-use-them/
DoorDash discloses new data breach tied to Twilio hackers
Food delivery firm DoorDash has disclosed that a threat actor gained access to the company's internal tools using stolen credentials from a third-party vendor that had access to their systems. The breach is reportedly linked to the same threat actors as the recent cyberattack on Twilio.
See the full report here: https://www.bleepingcomputer.com/news/security/doordash-discloses-new-data-breach-tied-to-twilio-hackers/
Atlassian Bitbucket Server vulnerable to critical RCE vulnerability
Atlassian has published a security advisory warning Bitbucket Server and Data Center users of a critical security flaw (CVE-2022-36804) that attackers could leverage to execute arbitrary code on vulnerable instances. Bitbucket is a Git-based code hosting, management, and collaboration tool, with Jira and Trello integration. The vulnerability impacts all Bitbucket Server and Data Center versions after 6.10.17. The versions that address the problem are 7.6.17, 7.17.10, 7.21.4, 8.0.3, 8.1.3, 8.2.2, and 8.3.1.
See the full report here: https://www.bleepingcomputer.com/news/security/atlassian-bitbucket-server-vulnerable-to-critical-rce-vulnerability/
Microsoft: Iranian hackers still exploiting Log4j bugs against Israel
The Iranian threat actor group called “MuddyWater” has been observed targeting Israeli organizations using the SysAid software, exploiting the Log4j vulnerability. MuddyWater (a.k.a. MERCURY) is an espionage group believed to be operated directly by Iran’s Ministry of Intelligence and Security (MOIS).
See the full report here: https://www.bleepingcomputer.com/news/security/microsoft-iranian-hackers-still-exploiting-log4j-bugs-against-israel/
CISA Adds 10 New Known Actively Exploited Vulnerabilities to its Catalog
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Friday added 10 new actively exploited vulnerabilities to its Known Exploited Vulnerabilities (KEV) Catalog, including a high-severity security flaw (CVE-2021-38406; CVSS score: 7.8) affecting industrial automation software from Delta Electronics. Because no patches address the vulnerability, CISA noted that the "impacted product is end-of-life and should be disconnected if still in use." Federal Civilian Executive Branch (FCEB) agencies are mandated to follow the guideline by September 15, 2022.
See the full report here: https://thehackernews.com/2022/08/cisa-adds-10-new-known-actively.html
Ransomware cyber attacks spike to over 1.2 mn per month in H12022
A security report has revealed that the volume of ransomware threats detected spiked to more than 1.2 million per month in the January to June (2022) period. The dominant targets are five key industries: education, municipalities, healthcare, infrastructure, and finance.
See the full report here: https://www.business-standard.com/article/technology/ransomware-cyber-attacks-spike-to-over-1-2-mn-per-month-in-h12022-122082800252_1.html
Nato investigates hacker sale of missile firm data
NATO is assessing the impact of a data breach of classified military documents being (including those potentially belonging to MBDA Missile Systems) allegedly sold by a hacker group online. The data includes blueprints of weapons being used by Nato allies in the Ukraine war. Cyber criminals, operating on Russian and English forums, are selling 80GB of the stolen data for 15 BTC and claimed to have sold the stash to at least one unknown buyer so far.
See the full report here: https://www.bbc.com/news/technology-62672184
Windows malware delays coinminer install by a month to evade detection
A new malware campaign disguised as Google Translate or MP3 downloader programs was found distributing cryptocurrency mining malware across 11 countries. The fake applications are being distributed through legitimate free software sites, providing broad exposure to the malicious applications to both regular visitors of the sites and search engines.
See the full report here: https://www.bleepingcomputer.com/news/security/windows-malware-delays-coinminer-install-by-a-month-to-evade-detection/
Italy’s Energy Agency Suffered Malware Attack, Halted IT Systems
Italy’s energy agency Gestore dei Servizi Energetici SpA suffered a malware attack, according to a statement. GSE’s IT systems and websites were shut down to protect the data, the statement said. The agency’s role as a gas buyer of last resort for Italy’s electricity network hasn’t been hampered.
See the full report here: https://www.bloomberg.com/news/articles/2022-08-29/italy-s-energy-agency-suffered-malware-attack-halted-it-systems
Researchers find malicious plugins on 25,000 WordPress sites
A new study from Georgia Institute of Technology researchers has found malicious plugins installed on some 25,000 WordPress websites. The researchers analyzed backups from over 400,000 web servers and found 47,337 malicious plugins across 24,931 unique WordPress sites using a web development tool named “YODA.”
See the full report here: https://siliconangle.com/2022/08/29/researchers-find-malicious-plugins-25000-wordpress-sites/
Hi-tech cheaters gang who used to hack online exam servers with mobile phones held in India
In the technical assistant recruitment exam, a system was allotted to the candidate to give the online exam. If the candidate had given the fixed amount, then these hackers would hack their system from the main cheating centre located in a neighbouring town. The paper appearing on the candidate's computer would have come on their computer after hacking.
See the full report here: https://www.timesnownews.com/mirror-now/crime/hi-tech-cheaters-gang-who-used-to-hack-online-exam-servers-with-mobile-phones-held-in-rajasthan-article-93847077
EmergeOrtho & General Health System Victims of Ransomware Attacks
EmergeOrtho, a North Carolina orthopedic practice, has recently notified 75,200 patients that some of their protected health information has been accessed by unauthorised individuals. A sophisticated ransomware attack was detected and blocked, but the threat actors behind the attack had accessed files containing patients’ protected health information, said the hospital.
See the full report here: https://www.hipaajournal.com/emergeortho-general-health-system-victims-of-ransomware-attacks/
Napa Valley College Files Report of Recent Data Breach Following Ransomware Attack
On August 25, 2022, Napa Valley College confirmed that the company experienced a data breach after an unauthorized party gained access to sensitive consumer data contained on NVC’s network. According to NVC, the breach resulted in the names and Social Security numbers belonging to certain individuals being compromised
See the full report here: https://www.jdsupra.com/legalnews/napa-valley-college-files-report-of-1518588/
Nelnet Servicing breach exposes data of 2.5M student loan accounts
Data for over 2.5 million individuals with student loans from Oklahoma Student Loan Authority (OSLA) and EdFinancial was exposed after hackers breached the systems of technology services provider Nelnet Servicing. Unidentified intruders compromised the company's network likely after exploiting a vulnerability.
See the full report here: https://www.bleepingcomputer.com/news/security/nelnet-servicing-breach-exposes-data-of-25m-student-loan-accounts/
Axel Royal LLC Confirms Recent Data Breach Impacting Consumers’ Social Security Numbers
Axel Royal reported a data breach on the company’s website as well as with various state attorney general offices. The breach resulted in the names, driver’s license numbers, state ID numbers, financial account information, payment card information, and medical information among others.
See the full report here: https://www.jdsupra.com/legalnews/axel-royal-llc-confirms-recent-data-4237012/
Leading Russian streaming platform suffers data leak allegedly impacting 44 million users
Russian streaming giant START said on Sunday that the personal information of its customers was leaked during a cyberattack. According to the Russian Telegram channel Information Leaks — which first publicized the incident and posted alleged screenshots of leaked information — the 72 GB database contains data on 44 million customers.
See the full report here: https://therecord.media/leading-russian-streaming-platform-suffers-data-leak-allegedly-impacting-44-million-users/
Neopets Provides Notice of Data Breach
Virtual pet website Neopets began updating individuals through its communication channels regarding a data incident that may have affected players' information. Neopets previously communicated about this incident to players on July 21, 2022, and August 1, 2022.
See the full report here: https://www.prnewswire.com/news-releases/neopets-provides-notice-of-data-breach-301613578.html
FBI: Hackers increasingly exploit DeFi bugs to steal cryptocurrency
The FBI has observed cyber criminals exploiting vulnerabilities in the smart contracts governing DeFi (decentralized finance) platforms to steal investors' cryptocurrency. Methods used in these attacks include initiating flash loans that trigger exploits in the platforms' smart contracts and exploiting signature verification flaws in their token bridge to withdraw all investments. Investors who suspect cyber criminals have stolen their DeFi investments should contact the FBI via the Internet Crime Complaint Center or their local FBI field office.
See the full report here: https://www.bleepingcomputer.com/news/security/fbi-hackers-increasingly-exploit-defi-bugs-to-steal-cryptocurrency/
Cloudflare CDN clients caught in Austrian fight against pirate sites
An anti-piracy campaign in Austria has affected Cloudflare content delivery network (CDN), with many IP addresses relating to sites that do not violate copyright laws getting banned. Cloudflare has confirmed the problem and has notified affected customers.
See the full report here: https://www.bleepingcomputer.com/news/security/cloudflare-cdn-clients-caught-in-austrian-fight-against-pirate-sites/
US govt sues Kochava for selling sensitive geolocation data
The U.S. Federal Trade Commission (FTC) has filed a lawsuit against location data broker Kochava for selling sensitive and precise geolocation data collected from hundreds of millions of mobile devices. Kochava's clients could use this data to track mobile users' movements to and from various locations such as reproductive health, mental care, and addiction recovery facilities or shelters for domestic violence survivors or the homeless.
See the full report here: https://www.bleepingcomputer.com/news/security/us-govt-sues-kochava-for-selling-sensitive-geolocation-data/
New Golang-based 'Agenda Ransomware' Can Be Customized For Each Victim
A new ransomware written in the Go language has been targeting healthcare and education enterprises in Asia and Africa. This ransomware is called Agenda/ Qilin and is customized per victim. Also, the ransom amount requested is different per company, ranging from USD 50,000 to USd 800,000.
See the full report here: https://thehackernews.com/2022/08/new-golang-based-agenda-ransomware-can.html
Leading library services firm hit by ransomware
Baker & Taylor, a distributor of books to libraries worldwide, stated that it is working on restoring systems after being hit by ransomware attack. There is no information yet on which ransomware group or affiliate is behind the attack.
See the full report here: https://www.bleepingcomputer.com/news/security/leading-library-services-firm-baker-and-taylor-hit-by-ransomware/
Notorious Russian Hacking Group Has A New Trick to Maintain Persistence
NOBELIUM—the codename attached to the same threat group that leveraged the SolarWinds Orion platform and other tools to gain access to sensitive U.S. agency networks—uses a post-exploitation capability named MagicWeb.
See the full report here: https://mytechdecisions.com/it-infrastructure/russian-hacking-group-microsoft-adfs-server-trick/
CERT-In issues alerts for multiple high severity vulnerabilities in Mozilla products and Drupal
CERT-In issued a warning for seven vulnerabilities, including these two, that exist in various Mozilla FireFox, Mozilla ESR and Mozilla Thunderbird. While Firefox is a regular browser, Firefox Extended Support Release (ESR) is developed for large organisations like universities and businesses and Thunderbird is an application that helps individuals and organisations manage their email.
See the full report here: https://www.thehindu.com/sci-tech/technology/cert-in-alerts-high-severity-vulnerabilities-mozilla-products-drupal/article65829557.ece
Valex Corporation Announces Data Breach Following Malware Attack
Valex Corporation filed an official notice of a data breach with the Attorney General of California after the company reportedly experienced a malware attack that leaked consumer data. The breach resulted in the names, dates of birth and Social Security numbers of certain individuals being compromised.
See the full report here: https://www.jdsupra.com/legalnews/valex-corporation-announces-data-breach-8512646/
KeyBank Announces Third-Party Data Breach Following Incident at Third-Party Vendor, Overby-Seawell Company
KeyBank reported a data breach with the Attorney General of Montana and several other government entities stemming from what appears to have been an incident at a third-party vendor. The names, mortgage information, phone numbers, property information, home insurance information and partial Social Security numbers of certain borrowers were compromised
See the full report here: https://www.jdsupra.com/legalnews/keybank-announces-third-party-data-8464347/
Hackers hide malware in James Webb telescope images
Threat analysts have spotted a new malware campaign dubbed ‘GO#WEBBFUSCATOR’ that relies on phishing emails, malicious documents, and space images from the James Webb telescope to spread malware. The malware is written in Golang, a programming language that is gaining popularity among cybercriminals
See the full report here: https://www.bleepingcomputer.com/news/security/hackers-hide-malware-in-james-webb-telescope-images/
Hackers Use ModernLoader to Infect Systems with Stealers and Cryptominers
The malicious implant in question, ModernLoader, is designed to provide attackers with remote control over the victim's machine, which enables the adversaries to deploy additional malware, steal sensitive information, or even ensnare the computer in a botnet. Infections are attributed to a previously undocumented Russian-speaking threat actor and potential targets included Eastern European users in Bulgaria, Poland, Hungary, and Russia.
See the full report here: https://thehackernews.com/2022/08/hackers-use-modernloader-to-infect.html
Newcourse Communications, Inc. Announces Data Breach Leaking the Social Security Numbers of as Many as 47,000 People
Newcourse Communications, Inc. reported a data breach with several state attorney generals’ offices after the company’s computer systems were hacked. The breach resulted in the names and Social Security numbers of certain individuals being compromised.
See the full report here: https://www.jdsupra.com/legalnews/newcourse-communications-inc-announces-8964303/
Chrome extensions with 1.4 million installs steal browsing data
Five Google Chrome extensions have been found tracking users’ browsing activity. Collectively, the extensions have been downloaded more then 1.4 million times. The purpose of the malicious extensions is to monitor when users visit e-commerce website and to modify the visitor's cookie to appear as if they came through a referrer link.
See the full report here: https://www.bleepingcomputer.com/news/security/chrome-extensions-with-14-million-installs-steal-browsing-data/
Two of the simplest forms of evasion are surprisingly effective against EDRs
Researchers estimate that Endpoint Detection and Response (EDR) evasion is possible when two fairly basic bypass techniques are combined. The process appear to work on most EDRs available in the industry.
See the full report here: https://arstechnica.com/information-technology/2022/08/newfangled-edr-malware-detection-generates-billions-but-is-easy-to-bypass/
Hackers exploiting LinkedIn's chat, job posting tools to steal users' data
Since most LinkedIn users accept any and all connection requests they receive, scammers can easily make connections and build credibility on the platform. After building credibility, the actors share malicious files and links, which are then opened by unsuspecting victims.
See the full report here: https://www.cnbctv18.com/technology/linked-in-hackers-exploiting-chat-job-posting-tools-steal-user-data-14616601.htm
Chinese state hackers targeted Australian federal and local gov
Threat actors believed to be sponsored by China are said to be behind espionage campaigns around the world, with Australian local and federal government agencies among the targets. The Australian Navy is believed to have been one of the targets of a sophisticated phishing campaign.
See the full report here: https://www.itnews.com.au/news/chinese-state-hackers-targeted-australian-federal-and-local-govt-584649
Own an Insta360 camera? This flaw could let anyone access your photos and videos
By following a simple URL with an IP address of the camera, one could access and download photos and videos right from a browser. This makes it possible to gain root access to the camera over Wi-Fi. From here, an attacker with basic tools could put malware on the camera’s SD card which could then be easily transferred to their computer when they plug it in.
See the full report here: https://www.tomsguide.com/news/own-an-insta360-camera-this-flaw-could-let-anyone-access-your-photos-and-videos
EmergeOrtho Reports Data Breach Leaking Social Security Numbers of Up to 75,200 Individuals
EmergeOrtho reported a data breach with the various state attorney generals’ offices after the company learned it was the target of a ransomware attack. The breach resulted in the first and last names, addresses, Social Security numbers, and dates of birth of certain individuals being compromised.
See the full report here: https://www.jdsupra.com/legalnews/emergeortho-reports-data-breach-leaking-5173978/
0ktapus/‘Scatter Swine’ Hacking Gang Stole 10,000 Corp Logins via Twilio
The Twilio debacle continues, with researchers revealing that hacker groups 0ktapus and Scatter Swine swiped at least 9,931 user credentials from more than 130 organizations. The plan seemingly was to launch software supply chain attacks but the techniques were “low-skill,” said the researchers.
See the full report here: https://securityboulevard.com/2022/08/0ktapus-scatter-swine-twilio-richixbw/
Chinese hackers - TA423/Red Ladon, target energy firms in South China Sea, Asia-Pacific
Cyber-security researchers discovered a recent cyber espionage campaign targeting energy and manufacturing firms globally, including in the South China Sea, that was perpetrated by Chinese hackers. The targets of this cyber attack spanned Australia, Malaysia, and Europe, as well as entities that operate in the South China Sea.
See the full report here: https://www.timesnownews.com/technology-science/chinese-hackers-ta423/red-ladon-target-energy-firms-in-south-china-sea-asia-pacific-article-93883316
CorrectHealth Announces Data Breach Affecting the Personal Information of More than 54k Individuals
CorrectHealth reported a data breach with the various state attorney generals’ offices after the company learned that an unauthorized party had gained access to several employee email accounts. According to Correct Health, the leaked data include names, addresses, Social Security numbers, Driver’s License numbers, and passport numbers among others.
See the full report here: https://www.jdsupra.com/legalnews/correcthealth-announces-data-breach-1289445/
Microsoft Azure outage knocks Ubuntu VMs offline after buggy update
Microsoft Azure customers' virtual machines (VMs) running Ubuntu 18.04 were taken offline by an ongoing outage caused by a faulty systemd update. Services impacted include Azure Kubernetes Service (AKS), Azure Monitor, Azure Sentinel, Azure Container Apps, and more.
See the full report here: https://www.bleepingcomputer.com/news/microsoft/microsoft-azure-outage-knocks-ubuntu-vms-offline-after-buggy-update/
Google Chrome bug lets sites write to clipboard without asking
Chrome version 104 (for mobile and desktop) accidentally introduced a bug that removes the user requirement to approve clipboard writing events from websites they visit. The bug hasn’t been fixed, as of the time of this report.
See the full report here: https://www.bleepingcomputer.com/news/security/google-chrome-bug-lets-sites-write-to-clipboard-without-asking/
Ragnar Locker ransomware claims attack on Portugal's flag airline
The Ragnar Locker ransomware gang has claimed an attack on TAP Air Portugal. The airlines company said the attack was blocked and it found no evidence indicating the attackers gained access to customer information stored on impacted servers.
See the full report here: https://www.bleepingcomputer.com/news/security/ragnar-locker-ransomware-claims-attack-on-portugals-flag-airline/
FBI deploys cyber team to Montenegro following massive cyberattack
The FBI is deploying a team of cybersecurity experts to Montenegro to investigate a massive cyberattack that hit the country’s critical infrastructure. Montenegrin officials have blamed Russia for the attack, which targeted Montenegro’s water supply systems, transportation services and online government services.
See the full report here: https://thehill.com/policy/cybersecurity/3622729-fbi-deploys-cyber-team-to-montenegro-following-massive-cyberattack/
Microsoft found TikTok Android flaw that let hackers hijack accounts
Microsoft reported a high severity flaw in the TikTok Android app that allowed attackers to quickly and quietly take over accounts with one click by tricking targets into clicking a specially crafted malicious link. Attackers could have then accessed and modified users' TikTok profiles and sensitive information. The vulnerability (CVE-2022-28799) is now patched since the release of TikTok version 23.7.3
See the full report here: https://www.bleepingcomputer.com/news/security/microsoft-found-tiktok-android-flaw-that-let-hackers-hijack-accounts/
Ukraine takes down cybercrime group hitting crypto fraud victims
The National Police of Ukraine (NPU) took down a network of call centers used by a cybercrime group focused on financial scams and targeting victims of cryptocurrency scams under the guise of helping them recover their stolen funds. Those linked to this fraud scheme are investigated for being part of an organized criminal group, fraud, and using malicious software, and are facing up to 12 years in prison.
See the full report here: https://www.bleepingcomputer.com/news/security/ukraine-takes-down-cybercrime-group-hitting-crypto-fraud-victims/
Apple Releases iOS Update for Older iPhones to Fix Actively Exploited Vulnerability
Apple backported security updates to older iPhones, iPads, and iPod touch devices to address a critical security flaw (CVE-2022-32893; CVSS score: 8.8) that has been actively exploited in the wild. The iOS 12.5.6 update is available for iPhone 5s, iPhone 6, iPhone 6 Plus, iPad Air, iPad mini 2, iPad mini 3, and iPod touch (6th generation).
See the full report here: https://thehackernews.com/2022/09/apple-releases-ios-update-for-older.html
Monero Mining Malware Finds Success at Top of Google Search
An insidious malware campaign targeting users searching for Google applications has infected thousands of computers globally to mine privacy-focused crypto monero (XMR). Titled Nitrokod, the malware initially masks itself as a free software, having found remarkable success at the top of Google search results for “Google Translate desktop download.”
See the full report here: https://blockworks.co/monero-mining-malware-finds-success-at-top-of-google-search/
SCA Pharmaceuticals, LLC Announces Data Breach
SCA Pharmaceuticals reported a data breach with the Montana Attorney General’s office after the company experienced a malware attack. The breach resulted in the names, dates of birth, Social Security numbers, other governmental identifiers, certain health information, and bank account information of certain individuals being compromised.
See the full report here: https://www.jdsupra.com/legalnews/sca-pharmaceuticals-llc-announces-data-3642373/
Fake ‘YouTube’ DMCA Notices Exploit Suspension Fears to Install Malware
A scam currently doing the rounds warns of copyright strikes on genuine YouTube accounts, but after targeting a security researcher, the scam's secrets are now public.
See the full report here: https://torrentfreak.com/fake-youtube-dmca-notices-exploit-suspension-fears-to-install-malware-220831/
Evil Corp Cybercriminal Syndicate Poses Threat to Healthcare Cybersecurity
The Health Sector Cybersecurity Coordination Center (HC3) issued a threat profile about Evil Corp and warned that the prolific group could threaten healthcare cybersecurity. HC3 described the group as “exceptionally aggressive and capable.”
See the full report here: https://www.hhs.gov/sites/default/files/evil-corp-threat-profile.pdf
Donlen Corporation Reports Data Breach After Unauthorized Party Gain Access to the Company’s Computer Network
Donlen Corporation reported a data breach with the office of the Montana Attorney General after the company detected “unusual activity related to the inaccessibility of certain systems” on its computer network. The company did not publicly release the data types that were leaked as a result of the incident.
See the full report here: https://www.jdsupra.com/legalnews/donlen-corporation-reports-data-breach-8797830/
Chile says gov’t agency struggling with ransomware attack
Chile’s cybersecurity incident response team said an unnamed government agency is dealing with a ransomware attack that targeted the organization’s Microsoft tools and VMware ESXi servers. CSIRT did not disclose the details about the group behind the attack or the department or agency that was attacked.
See the full report here: https://therecord.media/chile-says-govt-agency-struggling-with-ransomware-attack/
Hackers Hit Italian Oil Giant Eni’s Computer Network
Italian oil giant Eni SpA disclosed that its computer networks were hacked in recent days and that the consequences so far appeared to be minor. Eni, the country’s largest energy company, is working with local authorities to assess the consequences of the attack. People familiar with the situation said Eni appeared to be hit by a ransomware attack.
See the full report here: https://news.bloomberglaw.com/privacy-and-data-security/hackers-hit-italian-oil-giant-enis-computer-network-1
Ransomware Gang Accessed Water Supplier’s Control System
The ransomware gang Cl0p appeared to have accessed the industrial control systems of a UK water supply company, say researchers.
See the full report here: https://www.vice.com/en/article/4axaeq/ransomware-gang-accessed-water-suppliers-control-system
Migration policy org confirms cyberattack after extortion group touts theft
The International Centre for Migration Policy Development (ICMPD) confirmed a cyberattack that led to a data breach. ICMPD operates in 90 countries conducting research, projects and activities centered around migration. It currently has 19 member states — most of which are European — and has observer status at the United Nations.
See the full report here: https://therecord.media/migration-policy-org-confirms-cyberattack-after-extortion-group-touts-theft/
Ellington Management Group, LLC Announces Data Breach Related to Compromised Employee Email Accounts
Ellington Management Group reported a data breach with the Montana Attorney General after the company learned that an unauthorized party had gained access to two employee email accounts. The breach involved mortgage holders’ names, Social Security numbers, driver’s license numbers, electronic signatures, credit card numbers, dates of birth, bank or financial account numbers, and other information provided in connection with mortgage loans.
See the full report here: https://www.jdsupra.com/legalnews/ellington-management-group-llc-4015369/
Evil Corp and Conti Linked to Cisco Data Breach
A new research report has connected the data breach affecting Cisco Talos systems in May with an Evil Corp-affiliate group. More specifically, the IT infrastructure used to attack Cisco was also deployed in an attempted compromise of one of its clients in April 2022.
See the full report here: https://www.hhs.gov/sites/default/files/evil-corp-threat-profile.pdf
US Army to launch offensive cyber capabilities office
The U.S. Army will establish an office dedicated to offensive cyber and space capabilities next year amid rapidly shifting priorities. The office, dubbed Program Manager Cyber and Space, will fall under the Program Executive Office for Intelligence, Electronic Warfare and Sensors
See the full report here: https://www.defensenews.com/electronic-warfare/2022/08/31/us-army-to-launch-offensive-cyber-capabilities-office/
Data of 800 Million Chinese Citizens Exposed in Second Massive Data Breach in 2 Months
China is facing another massive data leak of its citizens as a huge database of at least 800 million records containing faces and vehicle license plates has been exposed online.
See the full report here: https://www.latestly.com/world/china-cyber-attack-data-of-800-million-people-exposed-in-second-massive-data-breach-in-2-months-4150259.html
Tags: all industries, global