
Threat Intelligence Bulletin: 09/02/2022 - 09/08/2022
|by Alpha Team
The Underground Economist: Volume 2, Issue 16
Welcome back to The Underground Economist, Volume 2, Issue 16, an intelligence focused blog series illuminating Dark Web findings in digestible tidbits from our ZeroFox Dark Ops intelligence team. The Dark Ops team scours the Dark Web, extending visibility and engagement into places traditional security teams can’t reach to share meaningful and insightful intelligence on the trends and tactics threat actors are leveraging across the Dark Web and criminal underground. Here’s the latest for the week of September 2, 2022.
Standing Intelligence Requirements

For the most up-to-date list of ZeroFox Threat Research’s Intelligence Requirements, please visit:
https://cloud.zerofox.com/intelligence/advisories/14956
Link to Download
View the full piece here.
U.S. Midterm Elections Series: Zero Trust and Election Security
Product Serial: S-2022-08-19a
TLP:CLEAR
In this brief, ZeroFox Intelligence explores the idea of Zero Trust architecture and how it may be incorporated into the U.S. elections process to help in secure the integrity of election assets.
Standing Intelligence Requirements

For the most up-to-date list of ZeroFox Threat Research’s Intelligence Requirements, please visit:
https://cloud.zerofox.com/intelligence/advisories/14956
Link to Download
View the full report here.
Scope Note
ZeroFox Intelligence is derived from a variety of sources, including—but not limited to—curated open-source accesses, vetted social media, proprietary data sources, and direct access to threat actors and groups through covert communication channels. Information relied upon to complete any report cannot always be independently verified. As such, ZeroFox applies rigorous analytic standards and tradecraft in accordance with best practices and includes caveat language and source citations to clearly identify the veracity of our Intelligence reporting and substantiate our assessments and recommendations. All sources used in this particular Intelligence product were identified prior to 5:00 PM (EDT) on August 30, 2022; per cyber hygiene best practices, caution is advised when clicking on any third-party links.
Executive Summary
Elements of network security architecture can be incorporated into the U.S. elections process to help in securing the integrity of election assets. Zero Trust architecture, which eschews implicit trust even of personnel approved for access to resources, is fully applicable to the oversight of voter registration databases. The principle of least privilege, which limits access according to minimum need, is more applicable to the non-networked processes of counting in-person votes and mailed ballots.
Breach Disclosure: Chamber of Secrets
On May 5, 2022, a reputed threat actor "louisthomas82" from the deep web forum BreachForums posted a data breach package targeting Chamber of Secrets, a discussion forum operating from Brazil. From this package on BreachForums, ZeroFox extracted 123,360 usernames, email addresses, and hashed passwords.
Standing Intelligence Requirements

For the most up to date list of ZeroFox Threat Research’s Intelligence Requirements, please visit:
https://cloud.zerofox.com/intelligence/advisories/14956
Details
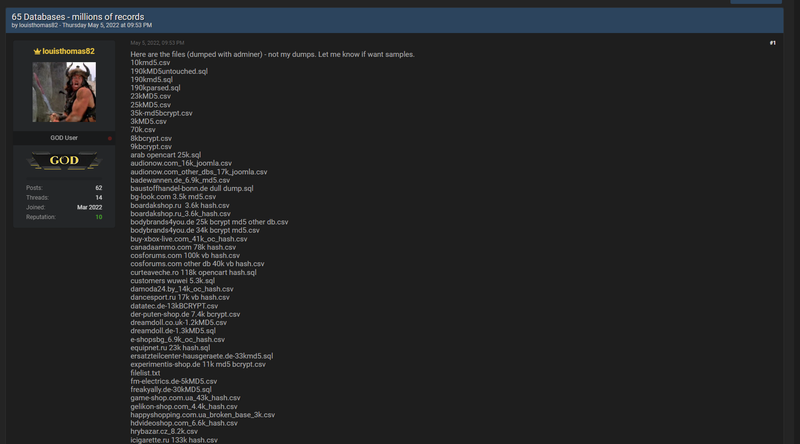
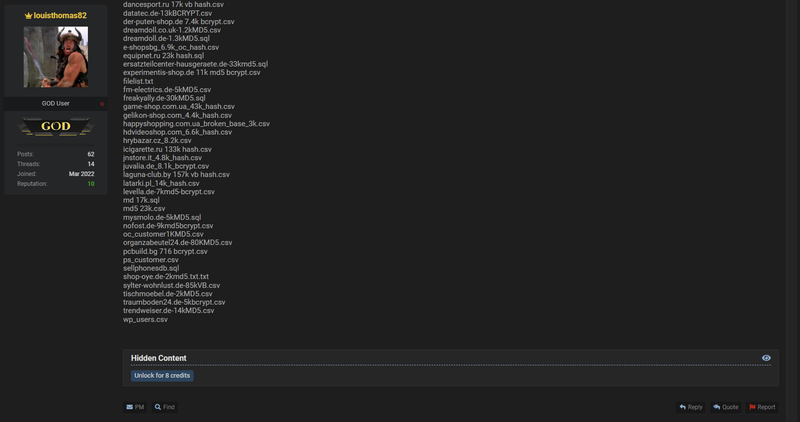
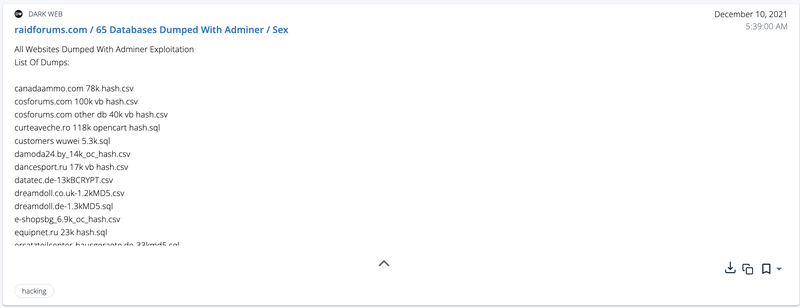
On May 5, 2022, a reputed threat actor "louisthomas82" from the deep web forum BreachForums posted a data breach package targeting Chamber of Secrets (cosforums[.]com), a discussion forum operating from Brazil. The threat actor noted that the data breach package includes 65 Databases with millions of records. The database for Chamber of Secrets is a part of that 65 databases. The data dump was also circulated in Raid Forums on December 10, 2021 by the threat actor "Sex". From this package on BreachForums, ZeroFox extracted 123,360 usernames, email addresses, and hashed passwords.
Recommendations
- If not already enabled, turn on the compromised credentials rule for all relevant entities and ensure relevant emails are entered for those entities, or reach out to [email protected] for assistance
- If one of your entities receives an alert, ZeroFox recommends immediate password changes for the affected account
- Enable 2-factor authentication for all of your organizational accounts to help mitigate phishing and credential stuffing attacks
Breach Disclosure: Qatar Ministry of Justice
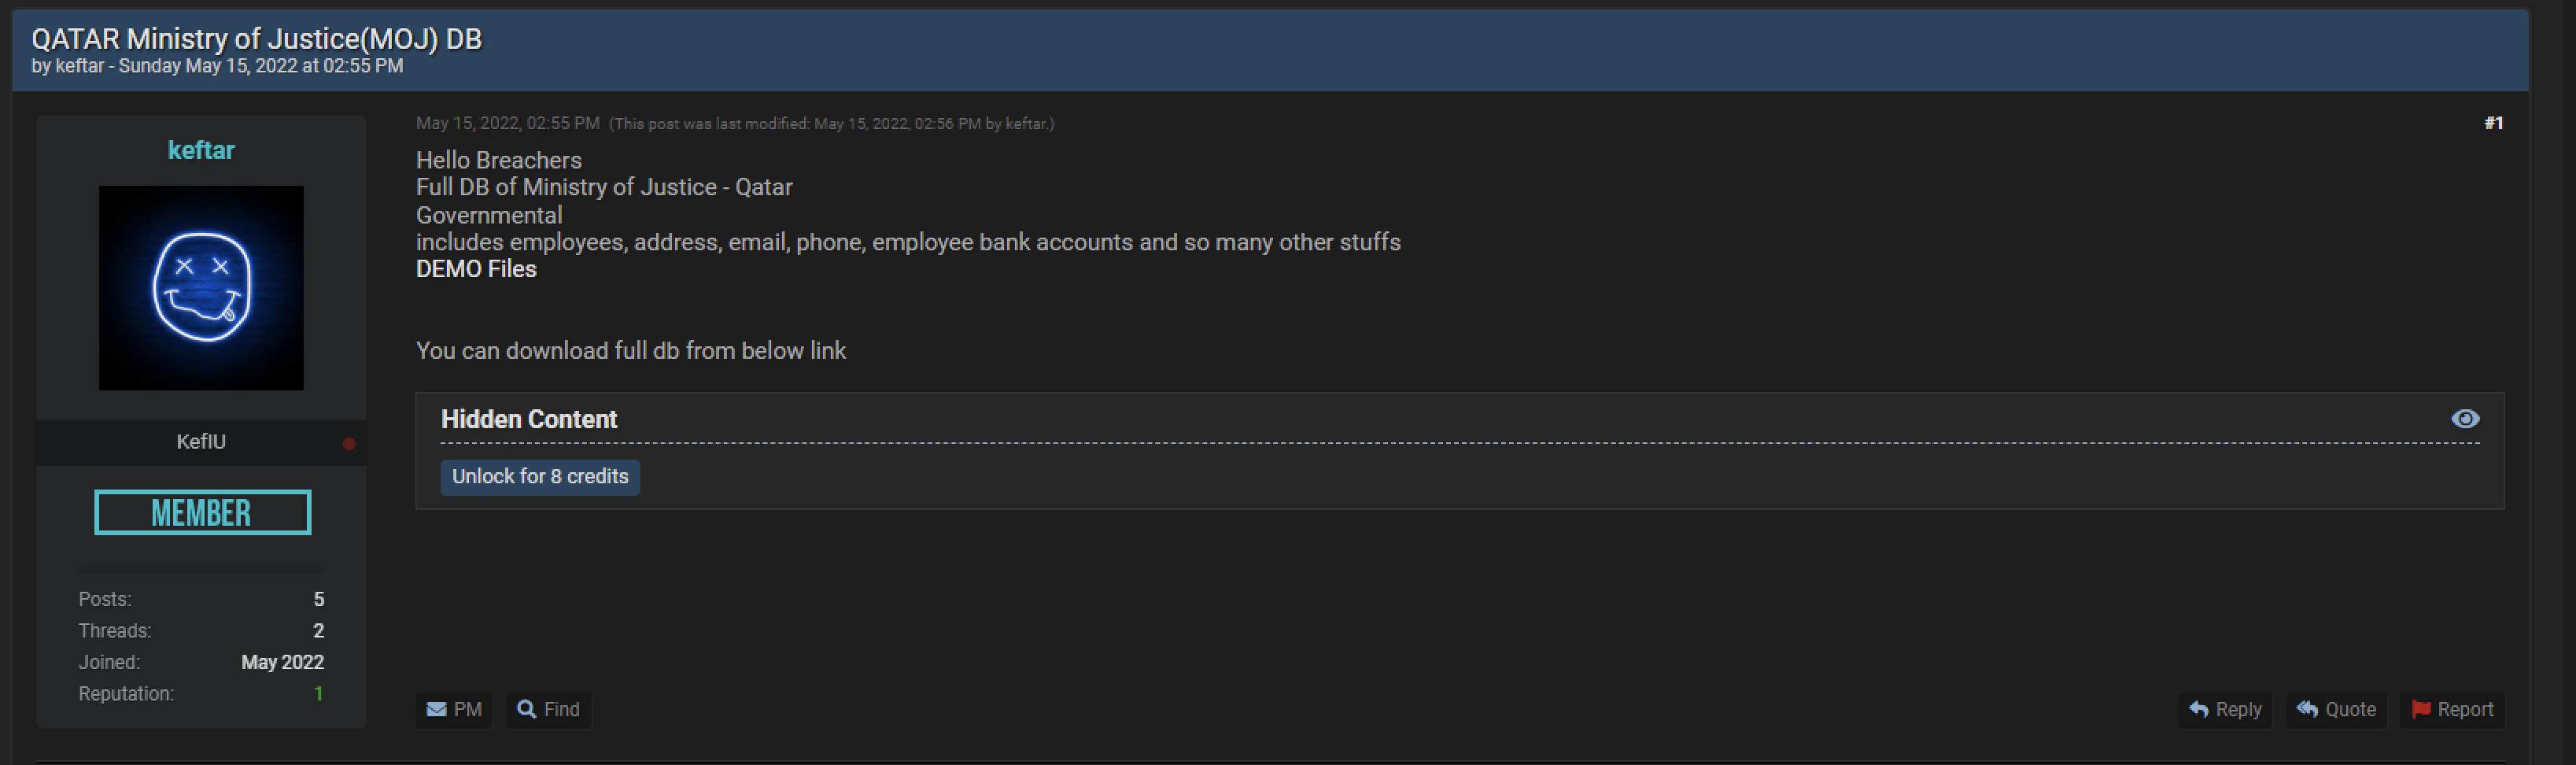
On May 15, 2022, a recently registered threat actor "keftar" from the BreachForums posted a data breach package targeting Qatar Ministry of Justice, a government legal affairs and legislative activities management in Qatar. From this package, ZeroFox extracted 1,329 email addresses.
Standing Intelligence Requirements
For the most up to date list of ZeroFox Threat Research’s Intelligence Requirements, please visit:
https://cloud.zerofox.com/intelligence/advisories/14956
Details
On May 15, 2022, a recently registered threat actor "keftar" from the BreachForums posted a data breach package targeting Qatar Ministry of Justice (moj[.]gov[.]qa), a government legal affairs and legislative activities management in Qatar. From this package, ZeroFox extracted 1,329 email addresses. No passwords were found in this breach..
Recommendations
- If not already enabled, turn on the compromised credentials rule for all relevant entities and ensure relevant emails are entered for those entities, or reach out to [email protected] for assistance
- If one of your entities receives an alert, ZeroFox recommends immediate password changes for the affected account
- Enable 2-factor authentication for all of your organizational accounts to help mitigate phishing and credential stuffing attacks
Breach Disclosure: Bodybrands4you
On May 5, 2022, a reputed threat actor "louisthomas82" from the BreachForums posted a data breach package targeting Bodybrands4you, a Germany-based online fitness store that sells products related to sports nutrition, fitness accessories, technology, and training equipment. From the package on BreachForums, ZeroFox extracted 39,136 email addresses and hashed passwords.
Standing Intelligence Requirements
For the most up to date list of ZeroFox Threat Research’s Intelligence Requirements, please visit:
https://cloud.zerofox.com/intelligence/advisories/14956
Details
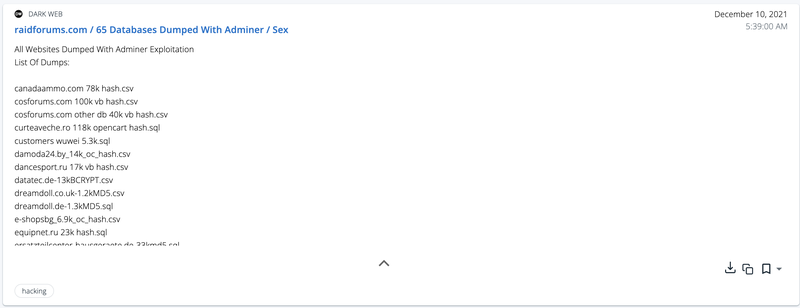
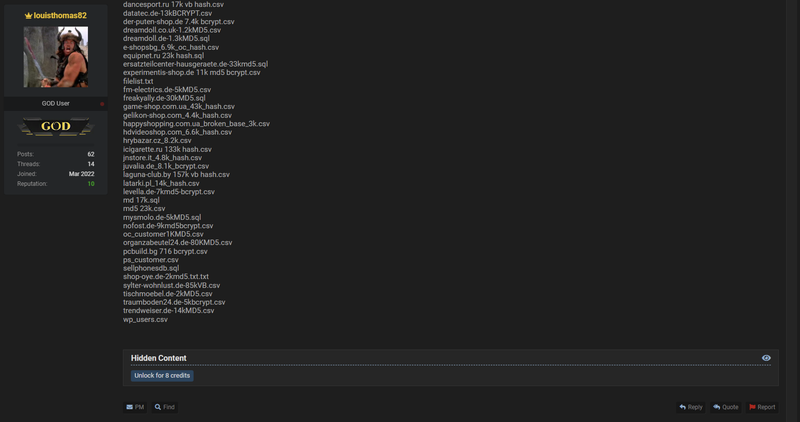
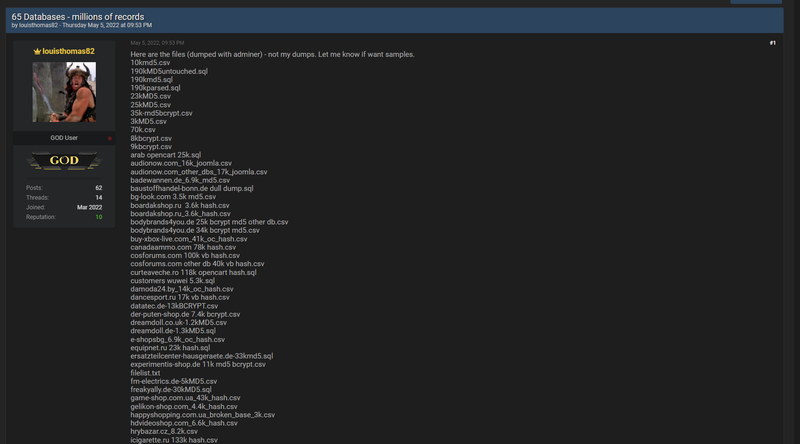
On May 5, 2022, a reputed threat actor "louisthomas82" from the BreachForums posted a data breach package targeting Bodybrands4you (bodybrands4you[.]de), a Germany-based online fitness store that sells products related to sports nutrition, fitness accessories, technology, and training equipment. The threat actor noted that the data breach package includes 65 Databases with millions of records. The database for Bodybrands4you is a part of that 65 databases. The data dump was also circulated in Raid Forums on December 10, 2021 by the threat actor "Sex". From the package on BreachForums, ZeroFox extracted 39,136 email addresses and hashed passwords.
Recommendations
- If not already enabled, turn on the compromised credentials rule for all relevant entities and ensure relevant emails are entered for those entities, or reach out to [email protected] for assistance
- If one of your entities receives an alert, ZeroFox recommends immediate password changes for the affected account
- Enable 2-factor authentication for all of your organizational accounts to help mitigate phishing and credential stuffing attacks
Breaking News: 2022-09-02 - 2022-09-08
Researchers Detail Emerging Cross-Platform BianLian Ransomware Attacks
The operators of the emerging cross-platform BianLian ransomware have increased their command-and-control (C2) infrastructure. The group has reportedly been adept with the Living of the Land (LOL) methodology to move laterally, adjusting their operations based on the capabilities and defenses they encountered in the target network.
See the full report here: https://thehackernews.com/2022/09/researchers-detail-emerging-cross.html
Montenegro hit by ransomware attack, hackers demand $10 million
The government of Montenegro has provided more information about the attack on its critical infrastructure, saying there is a ransom demand of $10 million. Cuba ransomware gang listed the Parliament of Montenegro (Skupstina) as its victim and claimed to have stolen financial documents, correspondence with banks, balance sheets, tax documents, compensation, and even source code. Montenegro's government had previously linked the attack to Russia, which gave the incident a geopolitical hue – with NATO allies helping with incident response, defense, and remediation.
See the full report here: https://www.bleepingcomputer.com/news/security/montenegro-hit-by-ransomware-attack-hackers-demand-10-million/
NSA and CISA share tips to secure the software supply chain
The U.S. National Security Agency (NSA) and the Cybersecurity and Infrastructure Security Agency (CISA) have released tips today on securing the software supply chain. Two more advisories will be released relating to this theme, focusing on software suppliers and customers.
See the full report here: https://www.bleepingcomputer.com/news/security/nsa-and-cisa-share-tips-to-secure-the-software-supply-chain/
Thousands lured with blue badges in Instagram phishing attack
A Instagram phishing campaign is attempting to scam users by luring them with a blue-badge offer. The targeted victims are urged to fill out a form and claim their verification badge in the next 48 hours. The first form requests “username,” the second asks the victim to enter “name,” “email,” and “phone number,” while the third and final step requests entering the user “password.”
See the full report here: https://www.bleepingcomputer.com/news/security/thousands-lured-with-blue-badges-in-instagram-phishing-attack/
Neopets says hackers had access to its systems for 18 months
Neopets has released details about the recently disclosed data breach incident that exposed personal information of more than 69 million members. The affected information may include the data provided when registering for or playing Neopets, including name, email address, username, date of birth, gender, IP address, Neopets PIN, hashed password, as well as data about a player's pet.
See the full report here: https://www.bleepingcomputer.com/news/security/neopets-says-hackers-had-access-to-its-systems-for-18-months/
Over 1,000 iOS apps found exposing hardcoded AWS credentials
Security researchers have found over 1,800 applications containing hard-coded Amazon Web Services (AWS) credentials, most of them being iOS apps and just 37 for Android. A majority of those applications contained valid AWS access tokens that could be used for direct access to private cloud services.
See the full report here: https://www.bleepingcomputer.com/news/security/over-1-000-ios-apps-found-exposing-hardcoded-aws-credentials/
Traffers threat: The invisible thieves
Traffers are cybercriminals organized in teams whose purpose is to steal a maximum of bankable information from infected computers, which they sell to other cybercriminals.
See the full report here: https://www.techrepublic.com/article/traffers-threat/
RedAlert and Monster: multiplatform ransomware gains steam
New ransomware gangs have learned to adapt their malware to different operating systems at the same time – and therefore cause damage to more organizations. A recent investigation has uncovered the activity of RedAlert and Monster – groups that managed to perform attacks on different operating systems without resorting to multiplatform languages.
See the full report here: https://www.zawya.com/en/press-release/companies-news/redalert-and-monster-multiplatform-ransomware-gains-steam-wbsmwwhu
Prynt Stealer’s Backdoor Exposed
Prynt Stealer builder, also attributed with WorldWind, and DarkEye, has a secret backdoor in the code that ends up in every derivative copy and variant of these malware families. The backdoor sends copies of victims' exfiltrated data gathered by other threat actors to a private Telegram chat monitored by the builder’s developers.
See the full report here: https://securityboulevard.com/2022/09/no-honor-among-thieves-prynt-stealers-backdoor-exposed/
Actors behind PyPI supply chain attack have been active since late 2021
The official software repository for the Python language, Python Package Index (PyPI), has been targeted in a complex supply chain attack recently. The attacks were part of a larger campaign by a group that has been active since at least late last year to spread credential-stealing malware the researchers are dubbing JuiceStealer.
See the full report here: https://arstechnica.com/information-technology/2022/09/actors-behind-pypi-supply-chain-attack-have-been-active-since-late-2021/
Ragnar Locker Ransomware Targets Energy Sector
Ragnar Locker is a ransomware that has been in use since at least December 2019 and is generally aimed at English-speaking users. It has been on the FBI’s radar since the gang breached more than fifty organizations across ten critical infrastructure sectors, mainly energy.
See the full report here: https://www.infosecurity-magazine.com/news/ragnar-locker-ransomware-energy/
REvil claims ransomware attack on multi-billion-dollar manufacturing giant Midea Group
The REvil ransomware gang has claimed an attack on Chinese electrical appliance manufacturer Midea Group and has already published what is believed to be stolen data. The gang re-emerged in April 2022 after shutting down for several months following the notorious hack on Kaseya in 2021.
See the full report here: https://www.itpro.co.uk/security/ransomware/368955/revil-claims-ransomware-attack-on-multi-billion-dollar-manufacturing-giant-midea-group
Bridgestone Americas, Inc. Releases Additional Details About February 2022 Ransomware Attack
Bridgestone Americas has shared the details on a data breach with the Attorney General of Massachusetts after the company was targeted in a ransomware attack in February 2022. The breach resulted in the names, Social Security numbers and bank account information of certain individuals being compromised.
See the full report here: https://www.jdsupra.com/legalnews/bridgestone-americas-inc-releases-6242225/
BlackCat Ransomware responsible for impacting Fremont County systems
In collaboration with county, state and federal partners, the Governor’s Office of Information has determined through its investigation that the recent cybersecurity event impacting Fremont County systems was the result of BlackCat ransomware, also known as ALPHV.
See the full report here: https://www.canoncitydailyrecord.com/2022/09/01/blackcat-ransomware-responsible-for-impacting-fremont-county-systems/
Hacks tied to Russia and Ukraine war have had minor impact, researchers say
Although politicians and cybersecurity experts have warned about the potential for widespread hacks in the wake of Russia’s invasion of Ukraine, a new study finds that attacks linked to the conflict have had minor impact and are unlikely to escalate further.
See the full report here: https://therecord.media/hacks-tied-to-russia-and-ukraine-war-have-had-minor-impact-researchers-say/
Sebi rejigs panel on cyber security; expands to 6 members
The Indian stock market regulator SEBI has restructured its high-level panel on cyber security that suggests measures to safeguard capital markets from such attacks.
See the full report here: https://www.financialexpress.com/market/sebi-rejigs-panel-on-cyber-security-expands-to-6-membersnbsp/2652104/
Platinum Performance Reports Data Breach Following Successful Phishing Attack
Platinum Performance reported a data breach with the Attorney General of Montana after the company was targeted in an email phishing attack. The company did not publicly release the type of data that was leaked as a result of the recent data security incident.
See the full report here: https://www.jdsupra.com/legalnews/platinum-performance-reports-data-4245822/
SharkBot malware sneaks back on Google Play to steal your logins
A new and upgraded version of the SharkBot malware has returned to Google's Play Store, targeting banking logins of Android users through apps that have tens of thousands of installations. The malware was present in two Android apps that did not feature any malicious code when submitted to Google's automatic review.
See the full report here: https://www.bleepingcomputer.com/news/security/sharkbot-malware-sneaks-back-on-google-play-to-steal-your-logins/
Malware dev open-sources CodeRAT after being exposed
The source code of a remote access trojan (RAT) dubbed 'CodeRAT' has been leaked on GitHub after malware analysts confronted the developer about attacks that used the tool. The malicious operation, which appears to originate from Iran, targeted Farsi-speaking software developers with a Word document that included a Microsoft Dynamic Data Exchange (DDE) exploit.
See the full report here: https://www.bleepingcomputer.com/news/security/malware-dev-open-sources-coderat-after-being-exposed/
Microsoft Defender falsely detects Win32/Hive.ZY in Google Chrome, Electron apps
Microsoft has released Microsoft Defender security intelligence update version 1.373.1537.0, which from reports, appears to resolve the Win32/Hive.ZY false positive experienced by Windows users.
See the full report here: https://www.bleepingcomputer.com/news/microsoft/microsoft-defender-falsely-detects-win32-hivezy-in-google-chrome-electron-apps/
IRS data leak exposes personal info of 120,000 taxpayers
The Internal Revenue Service, USA, has accidentally leaked confidential information for approximately 120,000 taxpayers who filed a form 990-T as part of their tax returns. IRS Form 990T is used to report 'unrelated business income' paid to a tax-exempt entity, such as nonprofits (charities) or IRA and SEP retirement accounts.
See the full report here: https://www.bleepingcomputer.com/news/security/irs-data-leak-exposes-personal-info-of-120-000-taxpayers/
China orders tech companies to 'improve traceability' of users to control 'rumours and false information'
The nation's Cyberspace Administration has announced a plan that calls for local tech companies to improve their ability to identify the source of rumors and fake news, then punish account-holders who share it with warnings, bans, and permanent suspensions.
See the full report here: https://www.theregister.com/2022/09/05/asia_in_brief/
DeFi venture OptiFi permanently locks up $661,000 of assets in code snafu
OptiFi, a decentralized options exchange using the Solana blockchain, inadvertently disabled its mainnet service with a misunderstood command and locked up some $661,000 worth of USDC 'digital dollar' tokens.
See the full report here: https://www.theregister.com/2022/09/02/defi_optifi_assets/
Revealed: US telcos admit to storing, handing over location data
US mobile carriers know a lot about where their customers every move, and according to letters sent to the Federal Communications Commission (FCC), they routinely store such location data for years, willingly hand it over to law enforcement if served a proper subpoena, and say users can't opt out.
See the full report here: https://www.theregister.com/2022/09/02/us_carriers_fcc_data_report/
Anonymous claims responsibility for Moscow traffic jam tied to app exploit
Hackers used Russia’s Yandex Taxi ride-hailing app to order dozens of drivers to converge on Kutuzovsky Prospekt, one of the city’s main thoroughfares. The act caused traffic on part of the already congested street to come to a standstill.
See the full report here: https://www.engadget.com/anonymous-claims-responsibility-yandex-moscow-taxi-exploit-200422959.html
Ransomware attacks on Linux to surge
Researchers say ransomware groups will increasingly target Linux servers and embedded systems over the coming years. It recorded a double-digit year-on-year (YoY) increase in attacks on these systems in 1H 2022.
See the full report here: https://www.helpnetsecurity.com/2022/09/05/ransomware-groups-target-linux/
Samsung says personal data of some U.S. customers exposed in breach
Samsung Electronics Co. is warning some U.S. customers that their personal data was exposed in a recent breach. The company stressed the breach did not involve Social Security numbers or credit- or debit-card numbers, but said data such as name, contact and demographic information, date of birth, and product registration information may have been affected.
See the full report here: https://www.marketwatch.com/story/samsung-says-personal-data-of-some-u-s-customers-exposed-in-breach-11662333643?mod=mw_latestnews
NFT-based Rug Pull Finder falls victim to a smart contract exploit
Rug Pull Finder (RPF), a non-fungible token (NFT) watchdog aiming to look for Web3.0-oriented frauds, has reportedly been at the receiving end of a smart contract exploit of its own.
See the full report here: https://www.financialexpress.com/digital-currency/nft-based-rug-pull-finder-falls-victim-to-a-smart-contract-exploit/2655434/
Kyber Network offers bounty following $265K hack of decentralized exchange
KyberSwap, the decentralized exchange built on liquidity protocol Kyber Network, has offered a hacker 15% of the funds from a $265,000 exploit as a bug bounty.
See the full report here: https://www.investing.com/news/cryptocurrency-news/kyber-network-offers-bounty-following-265k-hack-of-decentralized-exchange-2885614
Hackers stole Ethereum worth $185,000 from Bill Murray after he auctioned an NFT for charity
Hackers stole Ethereum worth more than $180,000 raised by Bill Murray as part of a charity auction. Murray was auctioning off a "Beer with Bill Murray" NFT. The successful bidder won a meeting with the comic actor while an artist painted the scene on canvas and to turn into a digital copy.
See the full report here: https://www.businessinsider.in/cryptocurrency/news/hackers-stole-ethereum-worth-185000-from-bill-murray-after-he-auctioned-an-nft-for-charity/articleshow/93987312.cms
Google Chrome emergency update fixes new zero-day used in attacks
Google has released Chrome 105.0.5195.102 for Windows, Mac, and Linux users to address a high-severity security flaw (CVE-2022-3075) that is actively exploited in the wild. The bug is caused by insufficient data validation in Mojo, a collection of runtime libraries that facilitates message passing across arbitrary inter- and intra-process boundaries. People should upgrade their Google Chrome web browser as soon as possible to guard against attacks.
See the full report here: https://www.bleepingcomputer.com/news/security/google-chrome-emergency-update-fixes-new-zero-day-used-in-attacks/
Damart clothing store hit by Hive ransomware, $2 million demanded
Hive ransomware gang has demanded $2 million after a ransomware attack on French clothing company Damart. Damart has reportedly not engaged in negotiations yet but informed the national police of the incident, which makes it unlikely that Hive would receive a payment.
See the full report here: https://www.bleepingcomputer.com/news/security/damart-clothing-store-hit-by-hive-ransomware-2-million-demanded/
San Francisco 49ers: Blackbyte ransomware gang stole info of 20K people
NFL's San Francisco 49ers are mailing notification letters confirming a data breach following a ransomware attack that hit its network earlier this year. Personal information (including names and Social Security numbers) belonging to 20,930 impacted individuals was accessed and/or stolen in the attack between February 6 and February 11, 2022.
See the full report here: https://www.bleepingcomputer.com/news/security/san-francisco-49ers-blackbyte-ransomware-gang-stole-info-of-20k-people/
BlackCat ransomware claims attack on Italian energy agency
The BlackCat/ALPHV ransomware gang claimed responsibility for an attack on Italy's energy agency Gestore dei Servizi Energetici SpA (GSE). The ransomware group claims to have stolen roughly 700 GB of files, including contracts, reports, project information, accounting documents, and other internal documentation.
See the full report here: https://www.bleepingcomputer.com/news/security/blackcat-ransomware-claims-attack-on-italian-energy-agency/
TikTok denies security breach after hackers leak user data, source code
TikTok has denied claims that it was breached (with source code and user data stolen) and stated that the data posted to a hacking forum is unrelated to the company. A hacking group AgainstTheWest created a topic on a hacking forum claiming to have breached both TikTok and WeChat. The threat actor claimed the breach involves 2.05 billion records in a massive 790 GB database containing user data, platform statistics, software code, cookies, auth tokens, server info, and more.
See the full report here: https://www.bleepingcomputer.com/news/security/tiktok-denies-security-breach-after-hackers-leak-user-data-source-code/
Interpol dismantles sextortion ring, warns of increased attacks
A transnational sextortion ring was dismantled following a joint investigation between Interpol's cybercrime division and police in Singapore and Hong Kong. The threat actors asked potential victims to download a malicious mobile app, which steals the contents of their phones' contact lists. The criminals would use this to blackmail the victims, threatening to share their videos with relatives and friends in their address books.
See the full report here: https://www.bleepingcomputer.com/news/security/interpol-dismantles-sextortion-ring-warns-of-increased-attacks/
QNAP patches zero-day used in new Deadbolt ransomware attacks
QNAP is warning customers of ongoing DeadBolt ransomware attacks that exploit a zero-day vulnerability in Photo Station. The company has patched the security flaw but attacks continue to happen. QNAP urges NAS customers to immediately update Photo Station to the newest version or replace Photo Station with QuMagie, a safer photo storage management tool for QNAP NAS devices.
See the full report here: https://www.bleepingcomputer.com/news/security/qnap-patches-zero-day-used-in-new-deadbolt-ransomware-attacks/
New EvilProxy service lets all hackers use advanced phishing tactics
A reverse-proxy Phishing-as-a-Service (PaaS) platform called EvilProxy claims to steal authentication tokens to bypass multi-factor authentication (MFA) on Apple, Google, Facebook, Microsoft, Twitter, GitHub, GoDaddy, and PyPI. The service enables low-skill threat actors who don't know how to set up reverse proxies to steal online accounts that are otherwise well-protected.
See the full report here: https://www.bleepingcomputer.com/news/security/new-evilproxy-service-lets-all-hackers-use-advanced-phishing-tactics/
Irish regulators fine Instagram 405 million euros for data breach
Ireland’s Data Protection Commission will impose a 405 million euro ($402 million) penalty on Instagram. The penalty is the second-biggest issued under the European Union’s stringent privacy rules, after Luxembourg’s regulators fined Amazon 746 million euros last year.
See the full report here: https://www.thehindu.com/news/international/irish-regulators-fine-instagram-405-million-euros-for-data-breach/article65855113.ece
Terror groups may turn to NFTs to raise funds and spread messages:
The first known case of a nonfungible token (NFT) created and shared by a “terrorist sympathizer” has come to light, raising concerns that the immutable nature of blockchain tech could help the spread of terrorist messages and propaganda.
See the full report here: https://cointelegraph.com/news/terror-groups-may-turn-to-nfts-to-raise-funds-and-spread-messages-wsj
Microsoft mistakenly rated Chromium, Electron, as malware
Microsoft appears to have fixed a problem that saw its Defender antivirus program identify apps based on the Chromium browser engine and/or Electron JavaScript framework as malware, and suggest users remove them.
See the full report here: https://www.theregister.com/2022/09/05/windows_defender_chrome_false_positive/
Russian-speaking cyber criminals feel economic pinch
Russian-speaking cyber criminals are being forced to refine and adapt their techniques as Vladimir Putin’s invasion of Ukraine makes current methods redundant.
See the full report here: https://www.computerweekly.com/news/252524585/Russian-speaking-cyber-criminals-feel-economic-pinch
Hacker group claims it accessed data from Israeli education sites
A hacker group called "The Generous Thief" has claimed that it had stolen the data of millions of former and current Israeli students and teachers, providing Excel files with addresses, ID numbers, emails and more.
See the full report here: https://www.jpost.com/business-and-innovation/tech-and-start-ups/article-716391
Concerns raised after alleged Northern Ireland Police data breach
Concerns have been raised after physical documents of Police Service Northern Ireland containing the names and addresses of loyal order members were found by a member of the public. The extent of data leaked is not known.
See the full report here: https://www.irishnews.com/news/northernirelandnews/2022/09/06/news/concerns_raised_after_alleged_psni_data_breach-2819203/
Ukrainian hackers create honeytrap for Russian soldiers
Ukrainian hackers set up fake accounts of attractive women to trick Russian soldiers into sending them photos, which they located and passed to the Ukrainian military.
See the full report here: https://finance.yahoo.com/news/ukrainian-hackers-created-fake-profiles-142721144.html
Minecraft is hackers’ favorite game title for hiding malware
Minecraft-related files accounted for roughly 25% of malicious files spreading via game brand abuse, followed by FIFA (11%), Roblox (9.5%), Far Cry (9.4%), and Call of Duty (9%).
See the full report here: https://www.bleepingcomputer.com/news/security/minecraft-is-hackers-favorite-game-title-for-hiding-malware/
Redline Stealer: Malware spread via hacked Facebook accounts
Researchers have discovered hacked Facebook business pages spreading a password stealer called Redline Stealer, which is capable of stealing passwords and downloading further malware. The malware is available for purchase on the dark web for about $100 to $150.
See the full report here: https://securityboulevard.com/2022/09/redline-stealer-malware-spread-via-hacked-facebook-accounts/
New Android Spyware found disguised as a book, likely to target Uyghur community
The Spyware disguises itself as a book named 'The China Freedom Trap' a personal and political account of the president of the Uyghur Congress, Dolkun Isa. However, it steals SMS, Contact details, Call logs, and even neighboring cell tower information.
See the full report here: https://www.timesnownews.com/technology-science/new-android-spyware-found-disguised-as-a-book-likely-to-target-uyghur-community-article-94024893
Newly discovered cyberspy crew targets Asian governments and corporations
A cyberespionage group has targeted government agencies and big-name corporations throughout Asia since at least 2020, using the notorious ProxyShell vulnerabilities in Microsoft Exchange to gain initial access. The crew, named Worok, may be associated with TA428, a similar group thought to be backed by China, that has been around since 2019.
See the full report here: https://www.theregister.com/2022/09/06/worok_espionage_asia/
Moobot botnet is coming for your unpatched D-Link router
The Mirai malware botnet variant known as ‘MooBot’ has re-emerged in a new attack wave that started early last month, targeting vulnerable D-Link routers with a mix of old and new exploits.
See the full report here: https://www.bleepingcomputer.com/news/security/moobot-botnet-is-coming-for-your-unpatched-d-link-router/
Ransomware attack hits Standard-Examiner newspaper
A ransomware attack damaged the Standard-Examiner newspaper’s computer network, delaying delivery of the print edition by a day. The outage also affected the Provo Daily Herald, the Standard-Examiner’s sister paper.
See the full report here: https://www.standard.net/news/local/2022/sep/06/ransomware-attack-hits-standard-examiner-delays-tuesday-paper/
Ransomware attack on leading US art college leads to data leak
Savannah College of Art and Design (SCAD) — an acclaimed art school in the U.S. serving more than 15,000 students — suffered a ransomware attack that leaked the sensitive information of hundreds of people.
See the full report here: https://therecord.media/ransomware-attack-on-leading-georgia-art-college-leads-to-data-leak/
Second largest U.S. school district LAUSD hit by ransomware
LAUSD enrolls more than 640,000 students, spanning from kindergarten through 12th grade. It includes Los Angeles and 31 smaller municipalities, as well as several Los Angeles County unincorporated sections.
See the full report here: https://www.bleepingcomputer.com/news/security/second-largest-us-school-district-lausd-hit-by-ransomware/
FBI warns of Vice Society ransomware attacks on school districts
FBI, CISA, and MS-ISAC jointly warned of U.S. school districts being increasingly targeted by the Vice Society ransomware group, with more attacks expected after the start of the new school year.
See the full report here: https://www.bleepingcomputer.com/news/security/fbi-warns-of-vice-society-ransomware-attacks-on-school-districts/
Data breach stalls IHG Hotels & Resorts' booking channels and apps
IHG Hotels & Resorts' booking channels and apps are experiencing widespread disruptions after the company's technology systems were impacted by what IHG called "unauthorized activity."
See the full report here: https://www.travelweekly.com/Travel-News/Hotel-News/Data-breach-disrupts-IHG-booking-system
Fitness influencer’s app exposes “personal” information and “sensitive” pictures of users
An influencer’s fitness app has been involved in a major data breach that potentially exposed customers’ personal information and revealing photos. Formerly known as Bodies By Rachel, the service encourages users to take before-and-after photos to show off their progress.
See the full report here: https://www.adelaidenow.com.au/technology/online/rachel-dillons-fitness-app-exposes-users-after-major-data-breach/news-story/adca32fcd27d4795fe827711424e0993
COVID contact tracing possible cause of Philippines data leak
Contact tracing conducted by business establishments at the height of the COVID-19 pandemic is possibly one of the culprits behind the spate of scam text messages sent to mobile phone users.
See the full report here: https://newsinfo.inquirer.net/1659610/salceda-suspects-contact-tracing-as-source-of-data-leak
Email hacking scheme leads to attempted theft of $13M from Pennsylvania school district
Chester Upland School District in Pennsylvania faced an attempted theft of $13 million through a complex scheme that involved hacked email accounts, cryptocurrency, and a romance scam of a recently widowed Florida woman.
See the full report here: https://www.k12dive.com/news/email-hacking-scheme-leads-to-attempted-theft-of-13m-from-pennsylvania-sch-1/631225/
Hacker Leaks Data of 42,064 Consumers in Karachi Through a Retail Website
A hacker got access to the personal data of 42,064 Karachiites. Stolen from a retail website, this data was more like an excel sheet with information such as names, phone numbers, residential addresses, invoice details, and more.
See the full report here: https://www.techjuice.pk/hacker-leaks-data-of-42064-karachiities-through-a-retail-website/
Dutch agency investigates cybersecurity of PV inverters after hack
A Dutch hacker known as “Jelle Ursem” recently gained access to PV systems operated via a monitoring tool developed by Chinese manufacturer Solarman. The state-run Dutch Radiocommunications Agency has launched an investigation into whether PV inverters pose a threat to the cybersecurity of the electricity system in the Netherlands.
See the full report here: https://www.pv-magazine.com/2022/09/06/dutch-agency-investigates-cybersecurity-of-pv-inverters-after-hack/
US seizes WT1SHOP market selling credit cards, credentials, and IDs
Law enforcement officials have seized the website and domains for WT1SHOP, a criminal marketplace that sold stolen credit cards, I.D. cards, and millions of login credentials. Bitcoin payments, email addresses, and admin accounts for WT1SHOP trace back to a 36-year-old person from the Republic of Moldova.
See the full report here: https://www.bleepingcomputer.com/news/security/us-seizes-wt1shop-market-selling-credit-cards-credentials-and-ids/
Zyxel releases new NAS firmware to fix critical RCE vulnerability
Networking device maker Zyxel advises customers to install patches for a new critical remote code execution (RCE) vulnerability (CVE-2022-34747; CVSS v3 severity score of 9.8) that affects three models of its Networked Attached Storage (NAS) products.
See the full report here: https://www.bleepingcomputer.com/news/security/zyxel-releases-new-nas-firmware-to-fix-critical-rce-vulnerability/
TA505 Hackers Using TeslaGun Panel to Manage ServHelper Backdoor Attacks
Cybersecurity researchers have offered fresh insights into a previously undocumented software control panel (called TeslaGun) used by a financially motivated threat group TA505 (also known as Evil Corp, Gold Drake, Dudear, Indrik Spider, and SectorJ04). TA505 is an aggressive Russian cybercrime syndicate behind the Dridex banking trojan and potentially the Raspberry Robin attacks.
See the full report here: https://thehackernews.com/2022/09/ta505-hackers-using-teslagun-panel-to.html
Cisco Releases Security Patches for New Vulnerabilities Impacting Multiple Products
Cisco has rolled out patches to address three security flaws affecting its products. The patched bugs include a high-severity weakness – CVE-2022-28199 (CVSS score: 8.6) – disclosed in NVIDIA Data Plane Development Kit (MLNX_DPDK).
See the full report here: https://thehackernews.com/2022/09/cisco-releases-security-patches-for-new.html
Some Members of Conti Group Targeting Ukraine in Financially Motivated Attacks
Former members of the Conti cybercrime cartel have been implicated in five different campaigns targeting Ukraine from April to August 2022. The activities of these groups reveal the blurring of lines between financially motivated and government-backed groups in Eastern Europe, with threat actors changing their targeting to align with regional geopolitical interests.
See the full report here: https://thehackernews.com/2022/09/some-members-of-conti-group-targeting.html
North Korean Hackers Deploying New MagicRAT Malware in Targeted Campaigns
North Korean nation-state threat actor Lazarus Group has been linked to a new remote access trojan called MagicRAT. This piece of malware is being deployed in victim networks that had been initially breached via successful exploitation of internet-facing VMware Horizon servers.
See the full report here: https://thehackernews.com/2022/09/north-korean-hackers-spotted-using-new.html
HP fixes severe bug in pre-installed Support Assistant tool
HP has issued a security advisory alerting users about a newly discovered vulnerability in HP Support Assistant. The bug (CVE-2022-38395, with a severity score of 8.2) enables attackers to elevate their privileges on vulnerable systems when users attempt to launch HP Performance Tune-up from within HP Support Assistant. HP recommends that customers using version 9.x update to the latest version of the Support Assistant.
See the full report here: https://www.bleepingcomputer.com/news/security/hp-fixes-severe-bug-in-pre-installed-support-assistant-tool/
Cisco won’t fix authentication bypass zero-day in EoL routers
Cisco will not patch a zero-day bug (CVE-2022-20923) affecting Cisco Small Business RV110W, RV130, RV130W, and RV215W Routers owing to the products reaching end-of-life (EOL). Cisco asked users using these products to migrate to Cisco Small Business RV132W, RV160, or RV160W Routers.
See the full report here: https://www.bleepingcomputer.com/news/security/cisco-won-t-fix-authentication-bypass-zero-day-in-eol-routers/
Ukraine dismantles more bot farms spreading Russian disinformation
The Cyber Department of the Ukrainian Security Service (SSU) has dismantled bot farms that spread Russian disinformation on social networks and messaging platforms via thousands of fake accounts. This bot army of almost 7,000 accounts was used to push content discrediting the Defence Forces of Ukraine, justify Russia's armed aggression, and destabilize Ukraine's social and political situation.
See the full report here: https://www.bleepingcomputer.com/news/security/ukraine-dismantles-more-bot-farms-spreading-russian-disinformation/
New Iranian hacking group APT42 deploys custom Android spyware
An Iranian state-sponsored hacking group (APT42) is reportedly using a custom Android malware to spy on targets of interest to the Iranian government. The Android spyware is primarily spread to Iranian targets via SMS texts containing links to a messaging or VPN app that can help bypass government-imposed restrictions.
See the full report here: https://www.bleepingcomputer.com/news/security/new-iranian-hacking-group-apt42-deploys-custom-android-spyware/
Ransomware gang's Cobalt Strike servers DDoSed with anti-Russia messages
At least four Cobalt Strike servers allegedly controlled by ex-Conti members are being flooded with anti-Russian messages to disrupt their activity. Former Conti members continue to use the same Cobalt Strike infrastructure to conduct new attacks under other ransomware operations, after Conti ransomware turned off their internal infrastructure in May 2022.
See the full report here: https://www.bleepingcomputer.com/news/security/ransomware-gangs-cobalt-strike-servers-ddosed-with-anti-russia-messages/
Albania blames Iran for July cyberattack, severs diplomatic ties
Albania has severed diplomatic relations with Iran after a July 2022 cyberattack that targeted Albanian government infrastructure was attributed to Iranian threat actors. The United States government also formally blamed Iran for attacking Albania in July and said the country would be held accountable for threatening the security of a NATO ally.
See the full report here: https://www.bleepingcomputer.com/news/security/albania-blames-iran-for-july-cyberattack-severs-diplomatic-ties/
Tags: all industries, global