
Breach Disclosure: 65 DBs
|by Alpha Team
Standing Intelligence Requirements

For the most up to date list of ZeroFox Threat Research’s Intelligence Requirements, please visit:
https://cloud.zerofox.com/intelligence/advisories/14956
Details
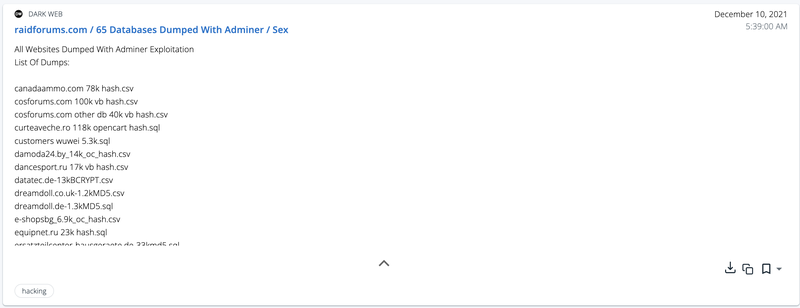
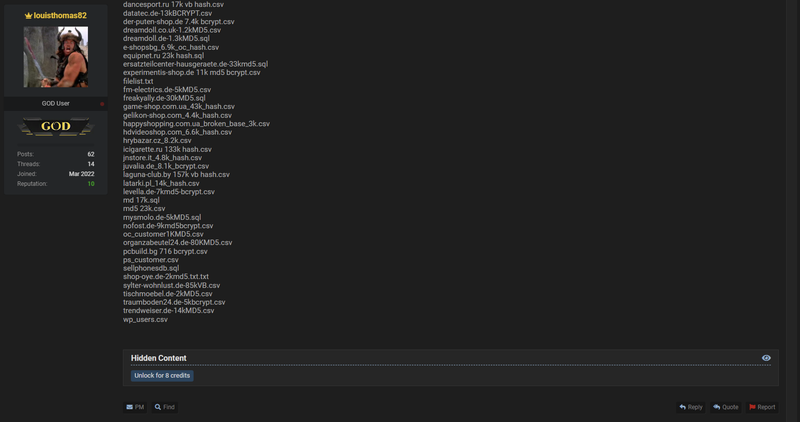
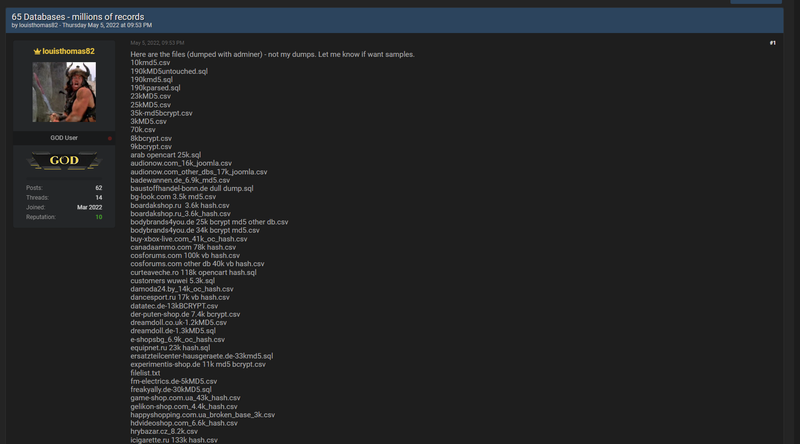
On May 5, 2022, a reputed threat actor "louisthomas82" from the BreachForums posted a combo list package. From the combo list package, ZeroFox collectively parsed the packages which were non-identifiable and titled as "65_DBs. The combolist was also circulated in Raid Forums on December 10, 2021, by the threat actor "Sex".The alert you received was from the acquisition and ingestion of what is known as a "combolilst" that was being shared on a Dark Web forum. A combo list is a list of allegedly compromised login credentials containing email addresses and their associated passwords. Combolists are often generated by threat actors from a variety of sources to be used in various onward malicious actions. The login credentials in these lists often come from a threat actor compiling data from previous breaches or exposures to take advantage of user’s who re-use their password on multiple websites or have not changed their password since it was exposed. ZeroFox emphasizes that threat actors often misrepresent the authenticity of some email and password combinations and in some cases completely make up the email and password combinations on these lists. From the package published in BreachForums, ZeroFox extracted 432,405 email addresses and hashed passwords.
Recommendations
- If not already enabled, turn on the compromised credentials rule for all relevant entities and ensure relevant emails are entered for those entities, or reach out to [email protected] for assistance
- If one of your entities receives an alert, ZeroFox recommends immediate password changes for the affected account
- Enable 2-factor authentication for all of your organizational accounts to help mitigate phishing and credential stuffing attacks
Tags: data breach, all industries, global