
Threat Intelligence Bulletin: 09/16/2022 - 09/22/2022
|by Alpha Team
NFT Drainer Claims to Bypass Cryptocurrency Wallet Update
Product Serial: F-2022-09-21a
TLP:CLEAR
In this flash report, ZeroFox Intelligence shares details about an advertisement for an NFT drainer targeting the latest version of MetaMask.
Standing Intelligence Requirements


For the most up-to-date list of ZeroFox Threat Research’s Intelligence Requirements, please visit:
https://cloud.zerofox.com/intelligence/advisories/14956
Link to Download
View the full report here.
Scope Note
ZeroFox Intelligence is derived from a variety of sources, including—but not limited to—curated open-source accesses, vetted social media, proprietary data sources, and direct access to threat actors and groups through covert communication channels. Information relied upon to complete any report cannot always be independently verified. As such, ZeroFox applies rigorous analytic standards and tradecraft in accordance with best practices and includes caveat language and source citations to clearly identify the veracity of our Intelligence reporting and substantiate our assessments and recommendations. All sources used in this particular Intelligence product were identified prior to 11:00 AM (EDT) on September 21, 2022; per cyber hygiene best practices, caution is advised when clicking on any third-party links.
Executive Summary
A credible dark web actor is advertising an updated NFT drainer aimed at the latest version of MetaMask, indicating a burgeoning market for more sophisticated attack vectors aimed at the NFT user base. In early September 2022, well-regarded threat actor “jezabeth” announced a new NFT drainer capable of draining ERC-20, ERC-1155, ERC-721, and Ethereum (ETH) tokens on popular Russian language dark web forum exploit[.]in; the actor is selling this drainer for 8 ETH, which is valued at about USD 10,790.
Key Findings
- A credible dark web actor is advertising an updated non-fungible token (NFT) drainer aimed at the latest version of MetaMask, indicating a burgeoning market for more sophisticated attack vectors aimed at the NFT user base.
- Threat actors’ shift to more sophisticated exploits tracks with the increase in general awareness and popularity of NFTs, which provide a lucrative target base.
The Underground Economist: Volume 2, Issue 17
Welcome back to The Underground Economist, Volume 2, Issue 17, an intelligence focused blog series illuminating Dark Web findings in digestible tidbits from our ZeroFox Dark Ops intelligence team. The Dark Ops team scours the Dark Web, extending visibility and engagement into places traditional security teams can’t reach to share meaningful and insightful intelligence on the trends and tactics threat actors are leveraging across the Dark Web and criminal underground. Here’s the latest for the week of September 16, 2022.
Standing Intelligence Requirements

For the most up-to-date list of ZeroFox Threat Research’s Intelligence Requirements, please visit:
https://cloud.zerofox.com/intelligence/advisories/14956
Link to Download
View the full piece here.
Uber Breach
Product Serial: F-2022-09-16a
TLP:CLEAR
In this flash report, ZeroFox Intelligence shares details on the Uber breach that have been made public by the alleged attacker.
Standing Intelligence Requirements
For the most up-to-date list of ZeroFox Threat Research’s Intelligence Requirements, please visit:
https://cloud.zerofox.com/intelligence/advisories/14956
Link to Download
View the full report here.
Scope Note
ZeroFox Intelligence is derived from a variety of sources, including—but not limited to—curated open-source accesses, vetted social media, proprietary data sources, and direct access to threat actors and groups through covert communication channels. Information relied upon to complete any report cannot always be independently verified. As such, ZeroFox applies rigorous analytic standards and tradecraft in accordance with best practices and includes caveat language and source citations to clearly identify the veracity of our Intelligence reporting and substantiate our assessments and recommendations. All sources used in this particular Intelligence product were identified prior to 11:00 AM (EDT) on September 16, 2022; per cyber hygiene best practices, caution is advised when clicking on any third-party links.
Executive Summary
Uber notified the public of an ongoing cybersecurity incident late on September 15, 2022, via Twitter. While Uber itself has not provided much detail, the alleged attacker appeared to share details and screenshots with those who reached out through Telegram. For the duration of their access, the attacker posted messages to internal messaging systems and online services announcing the breach. Later, several images began circulating online as proof of their access.
Key Findings
- Initial access to a breach disclosed by Uber on September 15, 2022, was gained through social engineering.
- Administrative credentials stored in a network-accessible script allowed the additional discovery of even more sensitive credentials.
- While the depth and breadth of the breach is yet to be determined, screenshots posted on social media indicate that the attacker may have had access to over 1 Petabyte of data.
Breach Disclosure: VampireFreaks
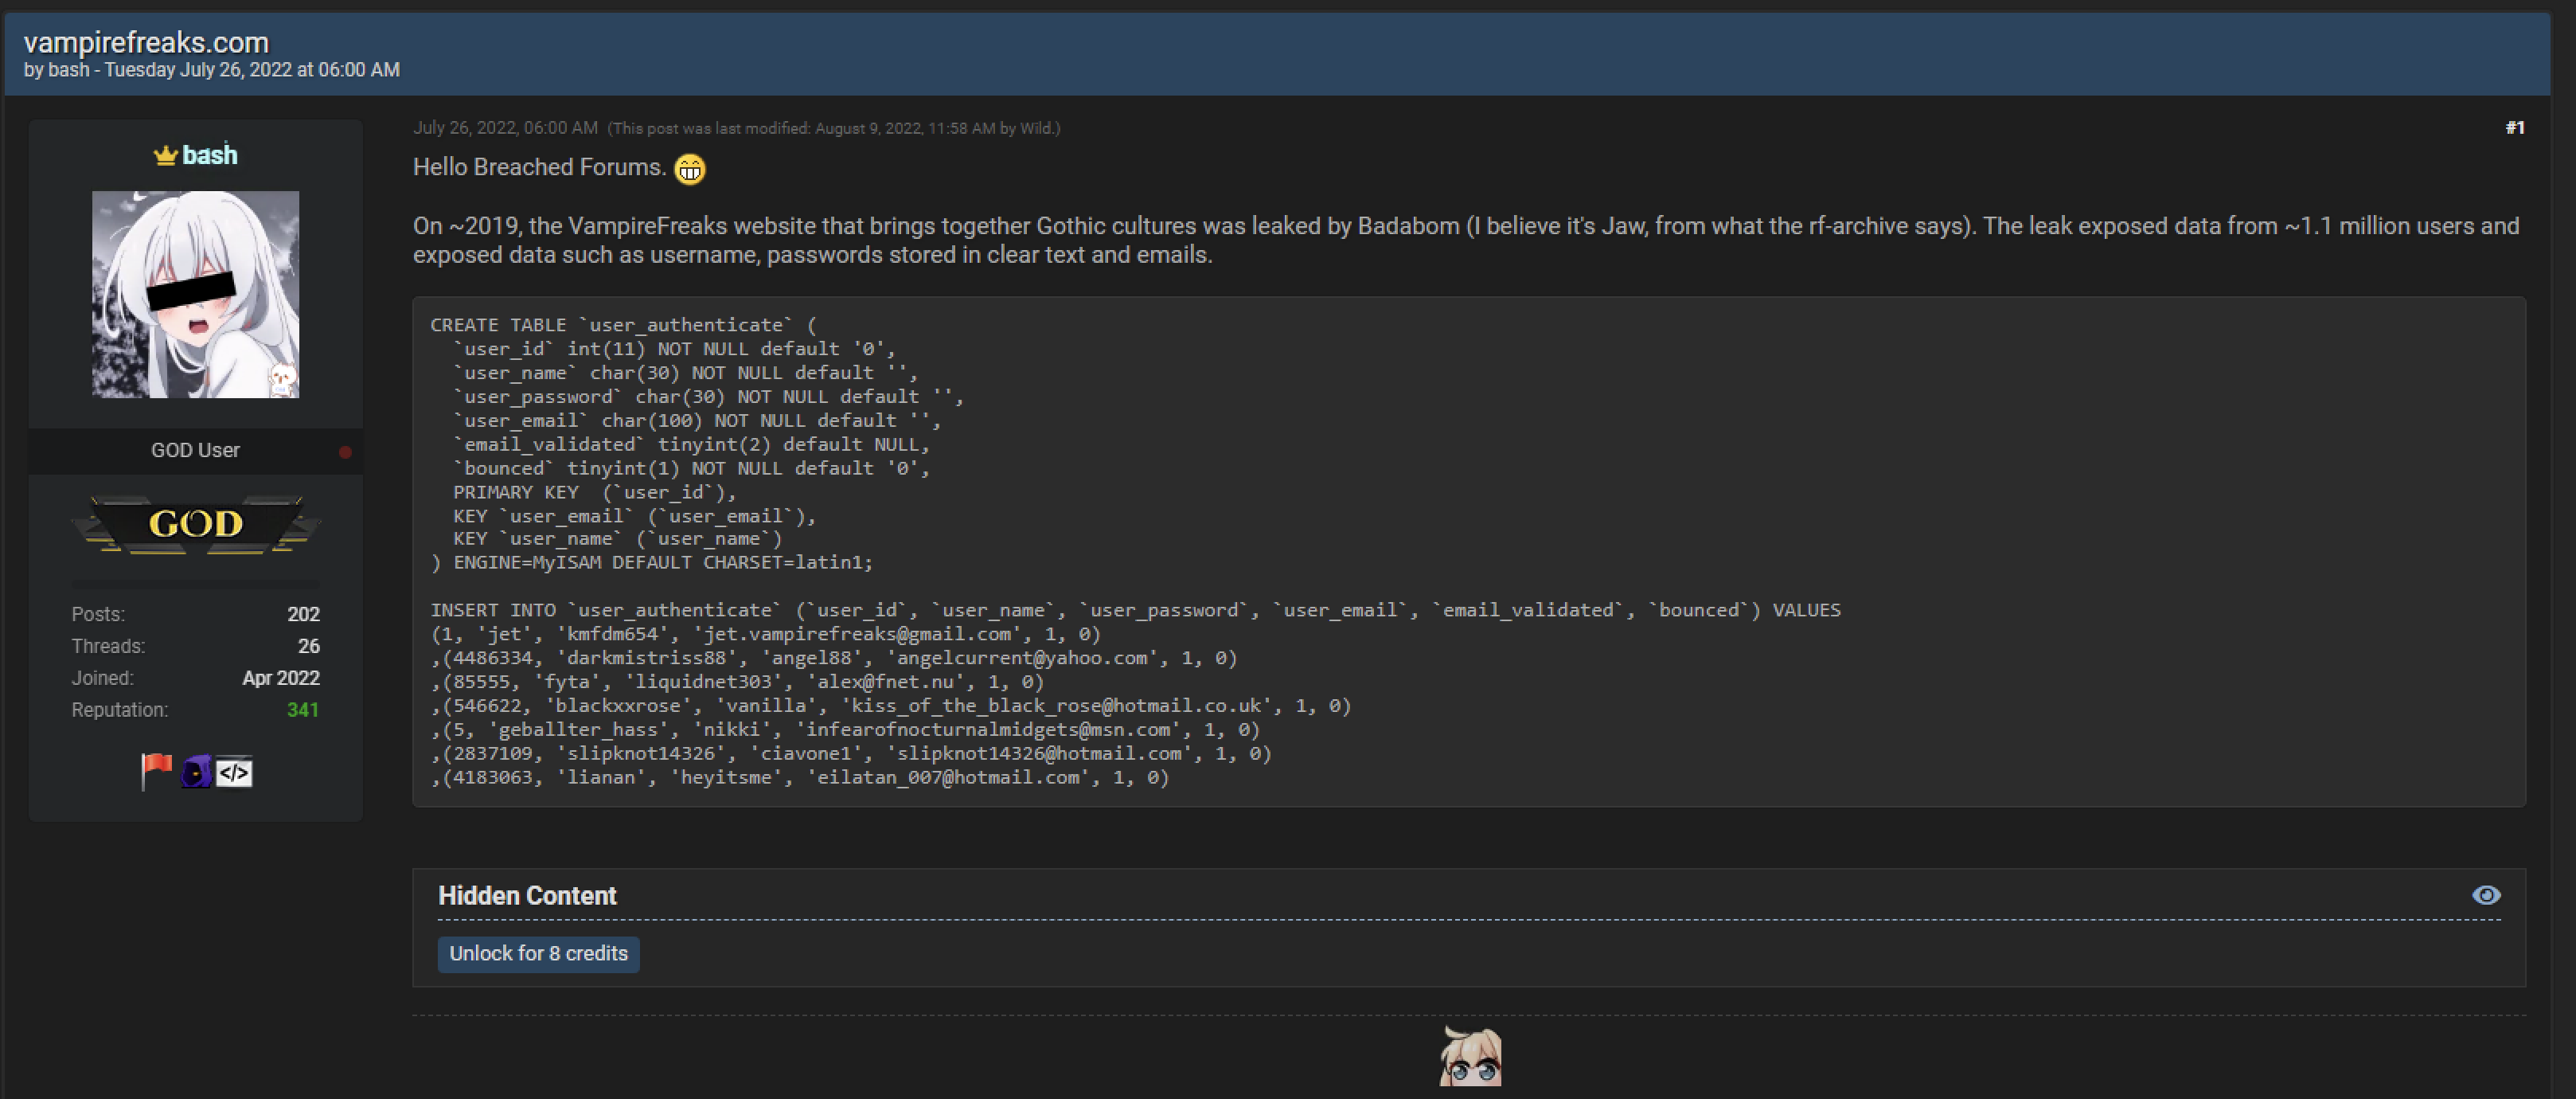
On July 26, 2022, a reputed threat actor "bash" from the BreachForums posted a data breach package targeting VampireFreaks, an online clothing store operating from Pennsylvania, United states. From the package published in BreachForums, ZeroFox extracted 1,048,618 email addresses, usernames and plain-text passwords.
Standing Intelligence Requirements
For the most up to date list of ZeroFox Threat Research’s Intelligence Requirements, please visit:
https://cloud.zerofox.com/intelligence/advisories/14956
Details
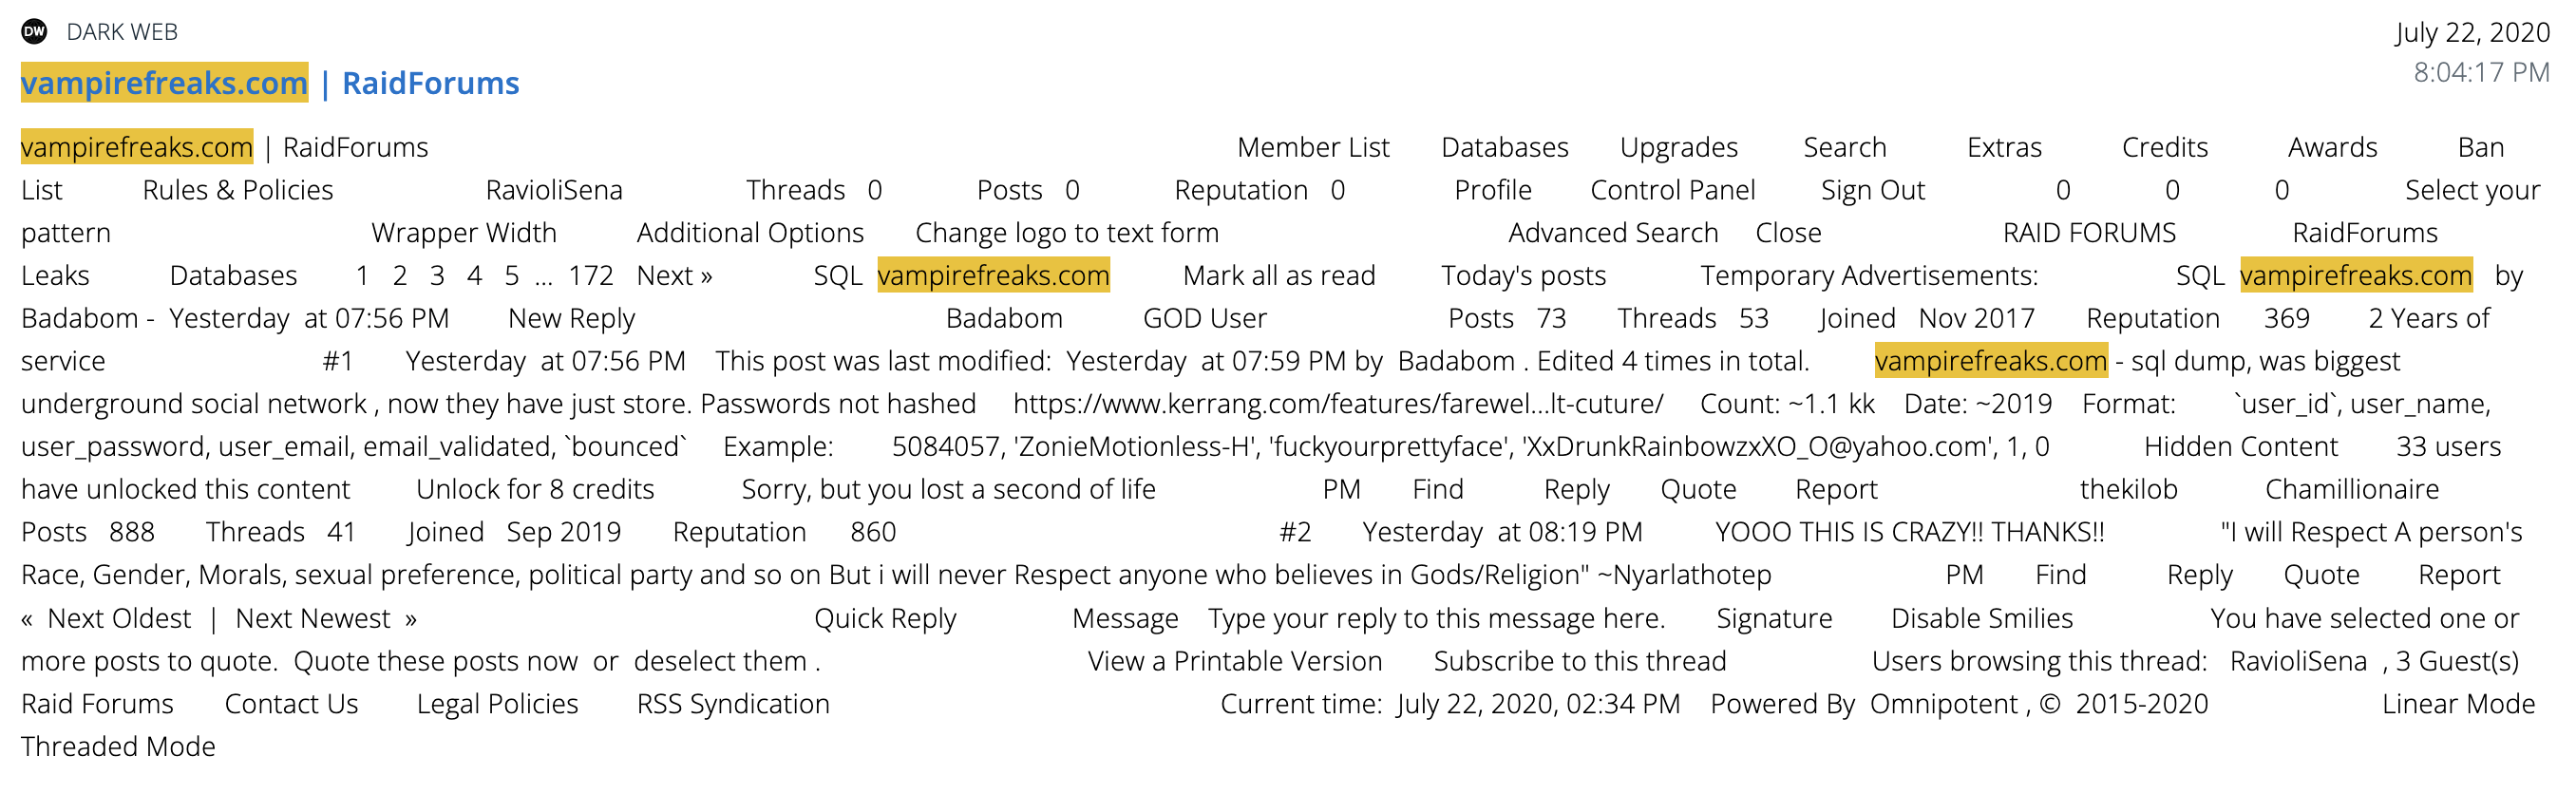
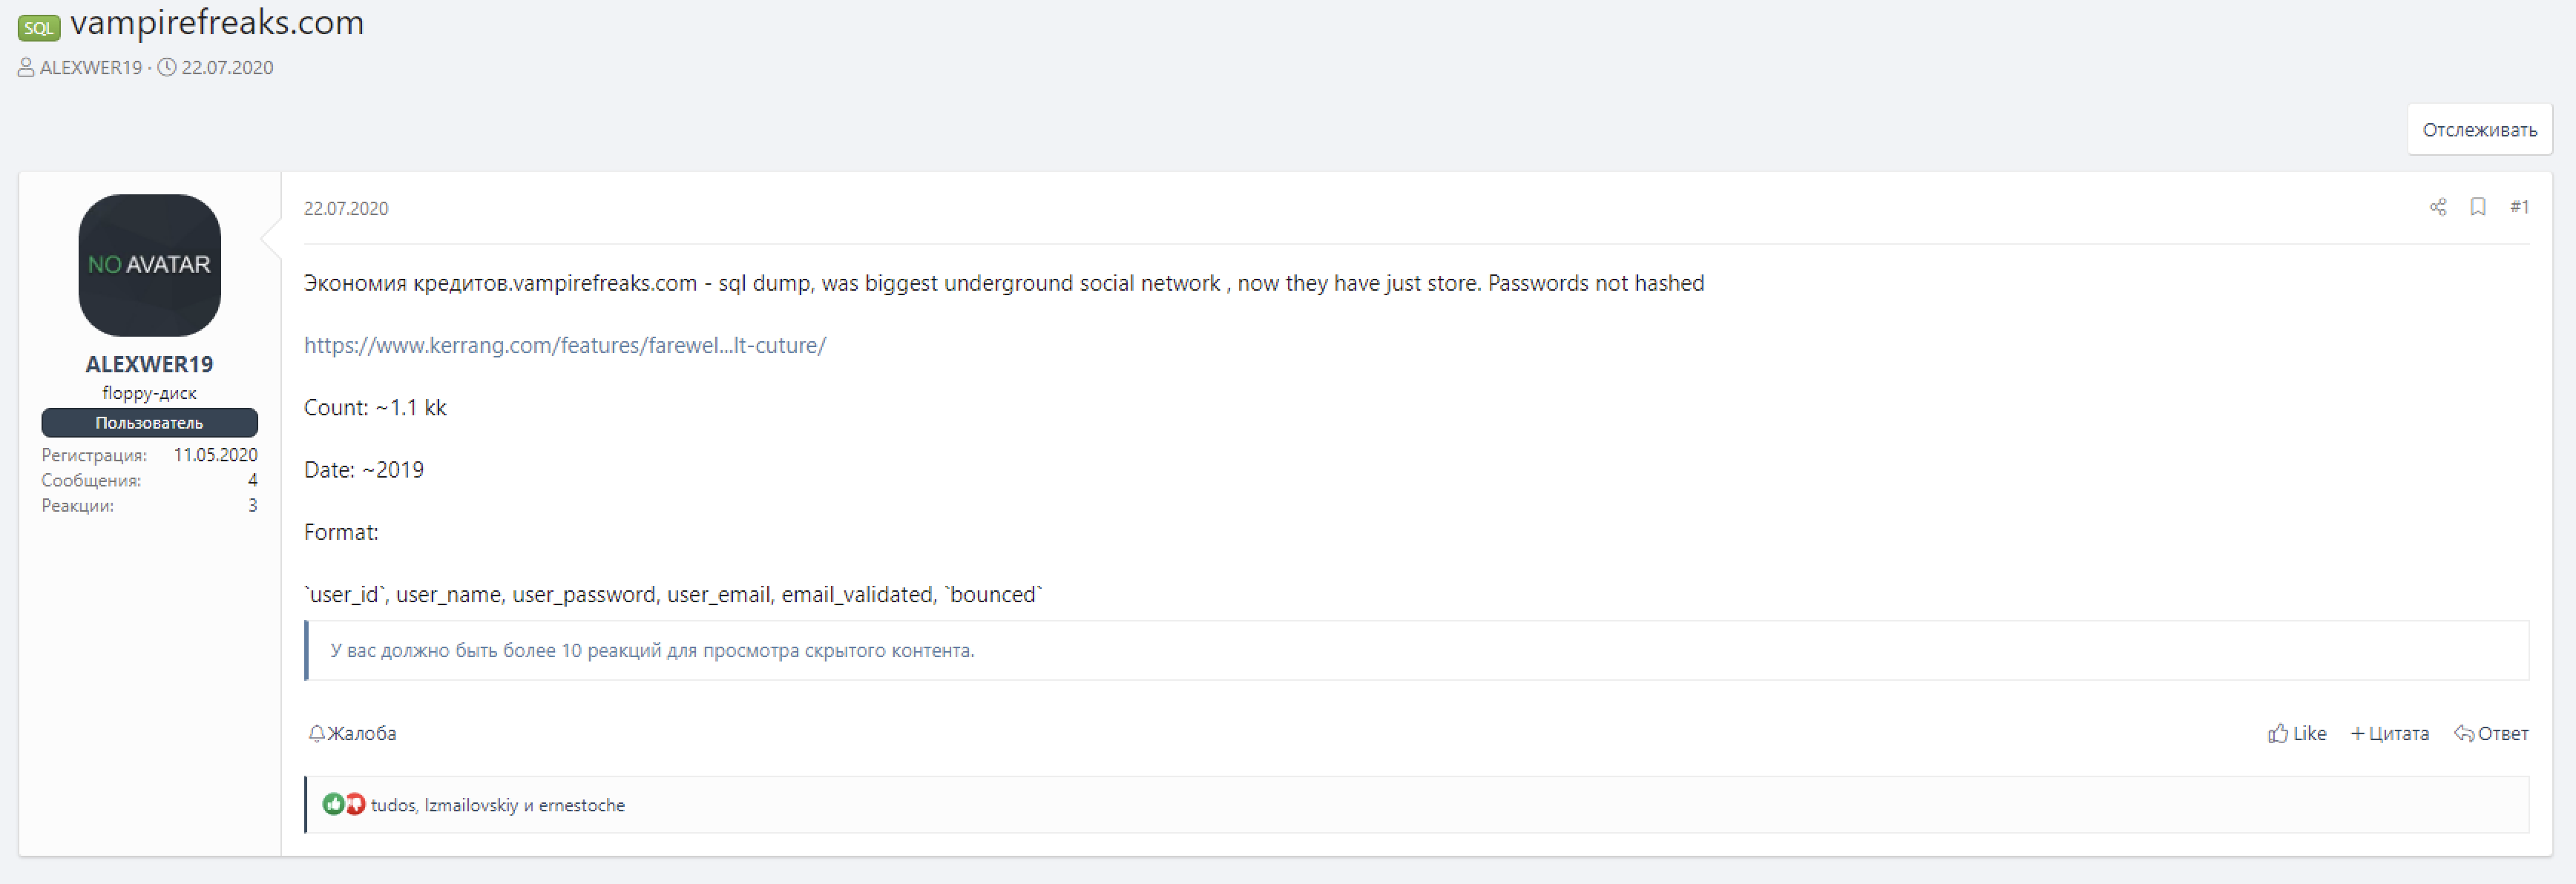
On July 26, 2022, a reputed threat actor "bash" from the BreachForums posted a data breach package targeting VampireFreaks (vampirefreaks[.]com), an online clothing store operating from Pennsylvania, United states. The threat actor noted that the data dump is from the year 2019 which includes the database of 1.1 million users with username, passwords stored in clear text and emails. The data dump was also circulated in the deep web forums like Raid Forums on July 22, 2020 and in the Russian language forum XSS on July 22, 2020 by the threat actor "ALEXWER19". From the package published in BreachForums, ZeroFox extracted 1,048,618 email addresses, usernames and plain-text passwords.
Recommendations
- If not already enabled, turn on the compromised credentials rule for all relevant entities and ensure relevant emails are entered for those entities, or reach out to [email protected] for assistance
- If one of your entities receives an alert, ZeroFox recommends immediate password changes for the affected account
- Enable 2-factor authentication for all of your organizational accounts to help mitigate phishing and credential stuffing attacks
Breach Disclosure: WiredBucks
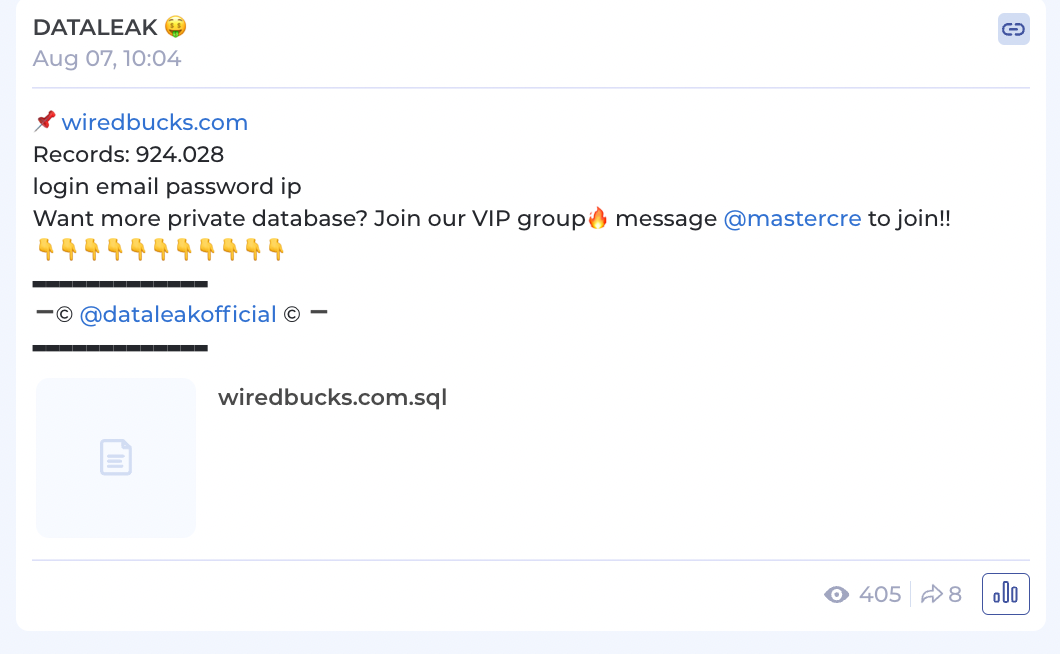
On August 7, 2022, the Telegram Channel "Dataleak" posted a data breach package targeting the WiredBucks, a U.S.-based organization that provides rewards to the influencer in the form of gift cards and cash. From the package published in the Telegram channel, ZeroFox extracted 946,249 email addresses and usernames.
Standing Intelligence Requirements
For the most up to date list of ZeroFox Threat Research’s Intelligence Requirements, please visit:
https://cloud.zerofox.com/intelligence/advisories/14956
Details
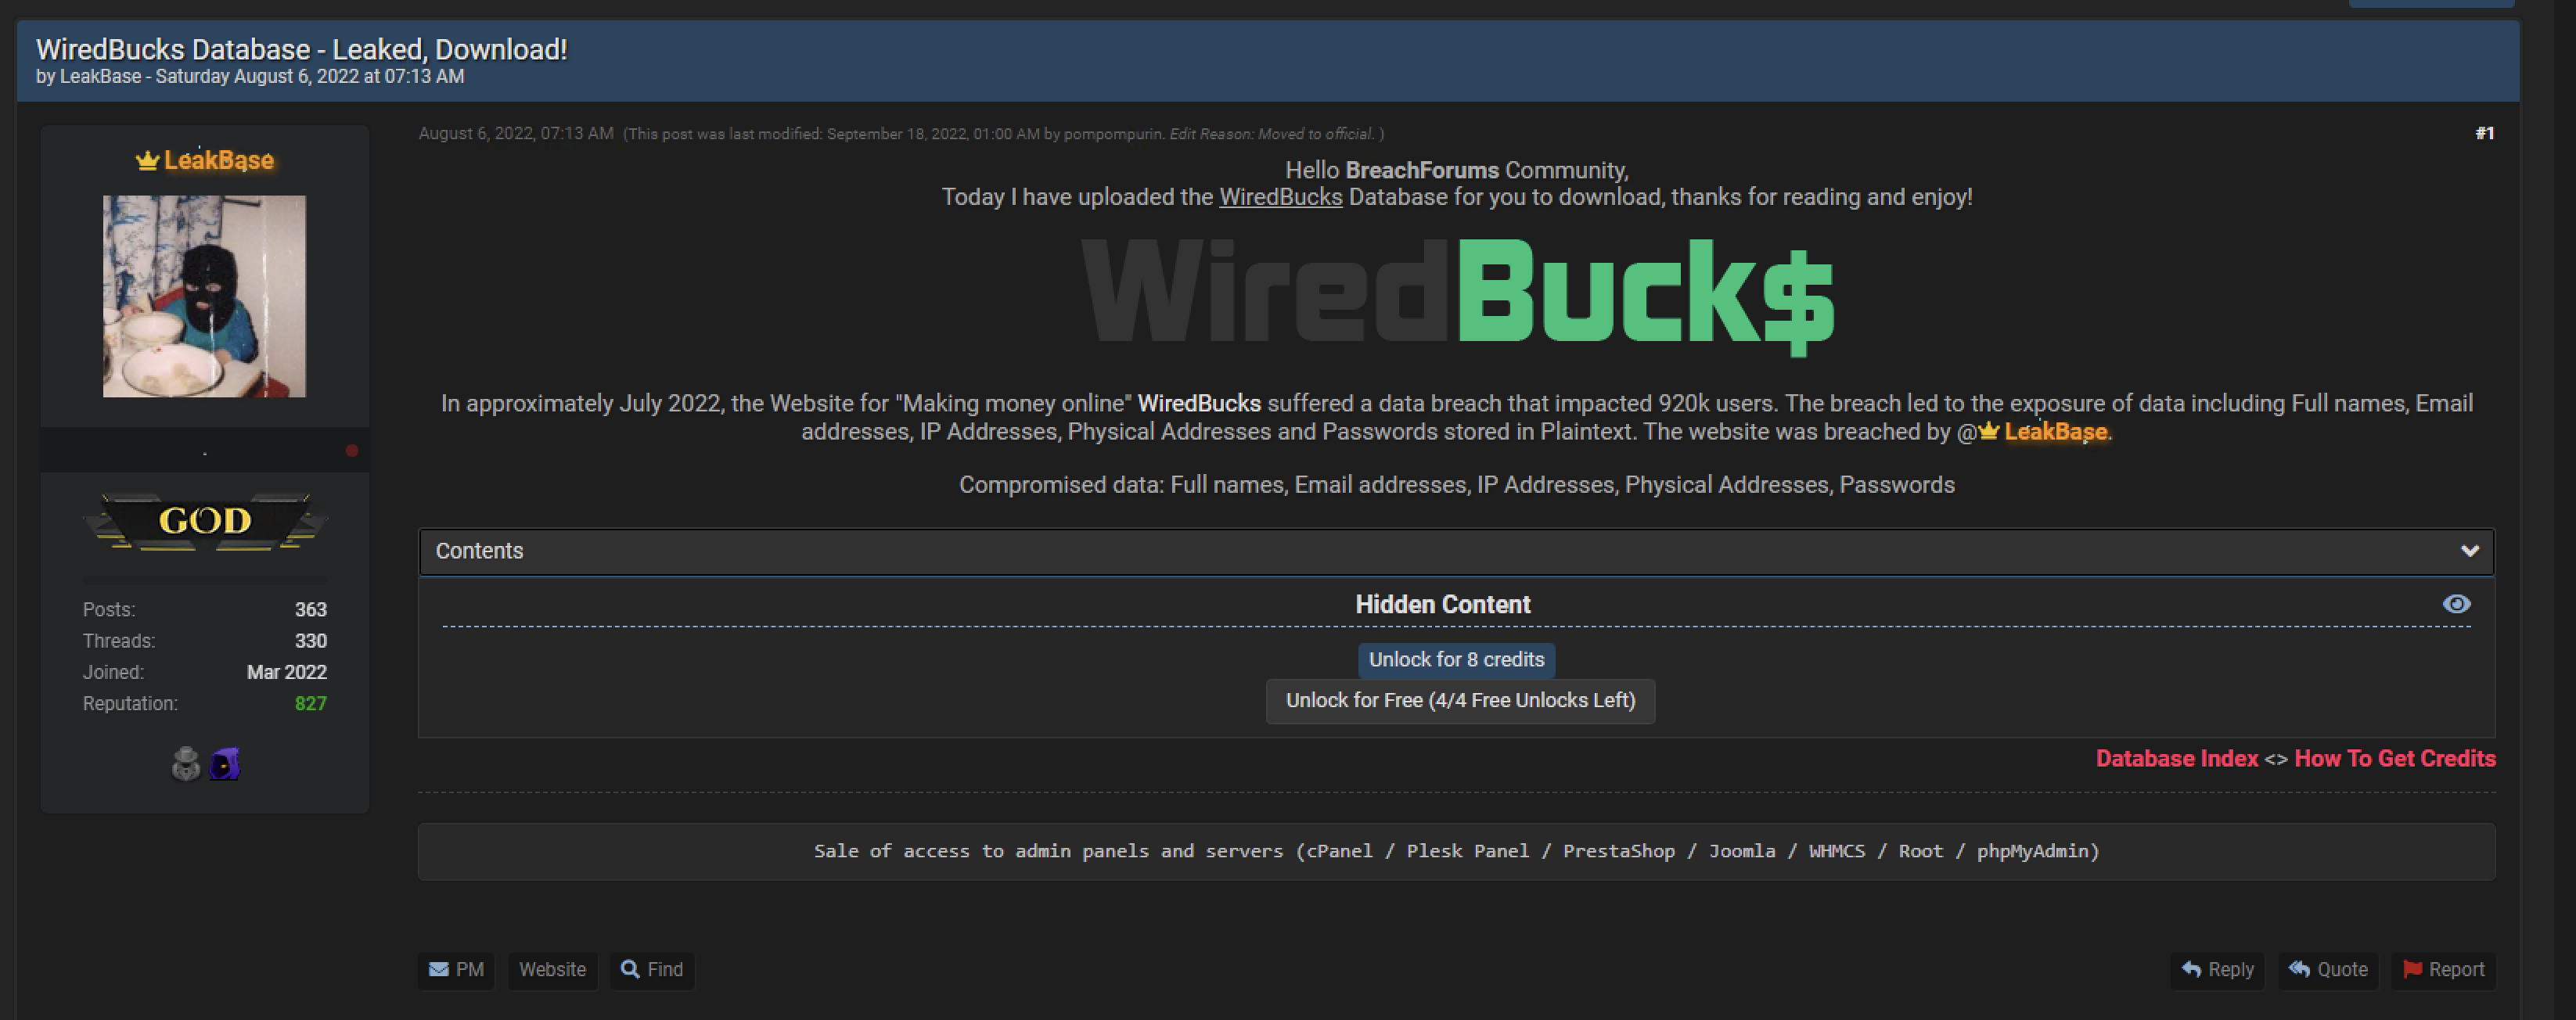
On August 7, 2022, the Telegram Channel "Dataleak" posted a data breach package targeting the WiredBucks (wiredbucks[.]com), a U.S.-based organization that provides rewards to the influencer in the form of gift cards and cash. The threat actor noted that the data dump includes user information with login email, password and IP address. The data dump was also posted in the deep web forum BreachForums on August 6, 2022 by the threat actor "LeakBase". From the package published in the Telegram channel, ZeroFox extracted 946,249 email addresses and usernames. Of these, an assessed 916,955 records were successfully linked to plain-text passwords. Other notable data fields observed in this package include: ip, fullname, payment_method, payment_address, and date_registered.
Recommendations
- If not already enabled, turn on the compromised credentials rule for all relevant entities and ensure relevant emails are entered for those entities, or reach out to [email protected] for assistance
- If one of your entities receives an alert, ZeroFox recommends immediate password changes for the affected account
- Enable 2-factor authentication for all of your organizational accounts to help mitigate phishing and credential stuffing attacks
Breach Disclosure: Juvalia
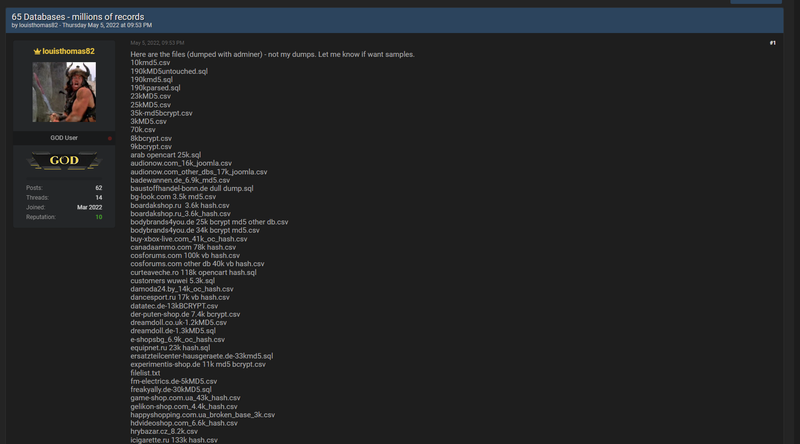
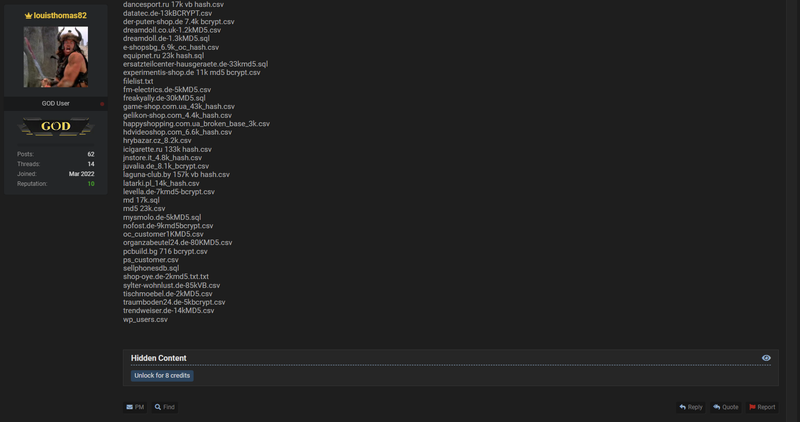
On May 5, 2022, a reputed threat actor "louisthomas82" from the BreachForums posted a data breach package targeting Juvalia, a Germany-based online store sells special jewelry and watches from wide section of brands. From the package published on BreachForums, ZeroFox extracted 8,107 email addresses and hashed passwords.
Standing Intelligence Requirements
For the most up to date list of ZeroFox Threat Research’s Intelligence Requirements, please visit:
https://cloud.zerofox.com/intelligence/advisories/14956
Details
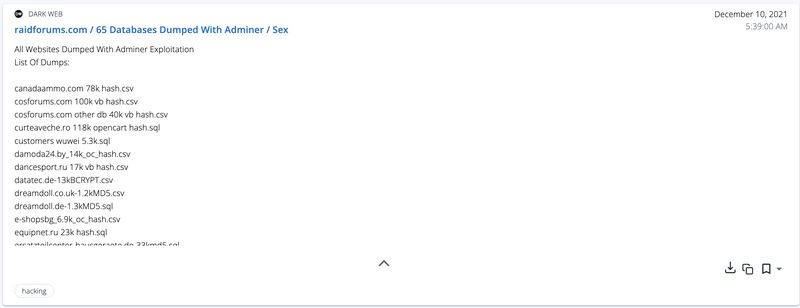
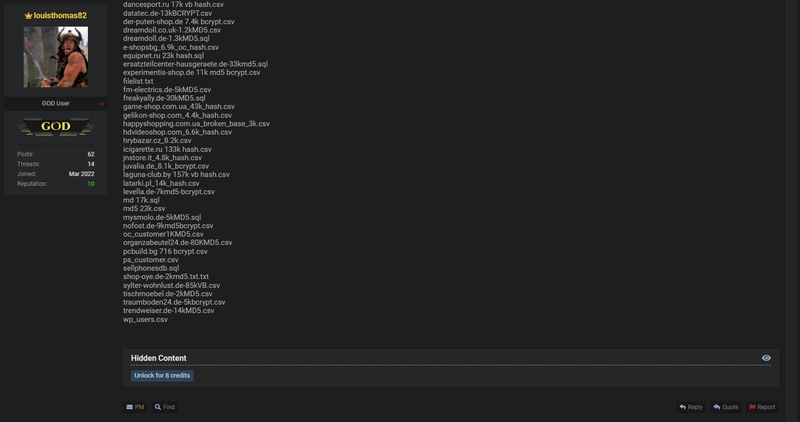
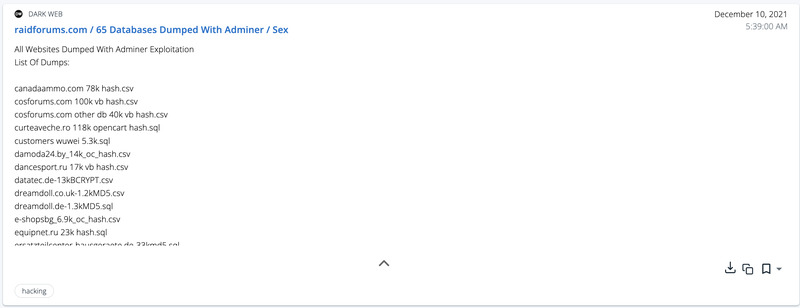
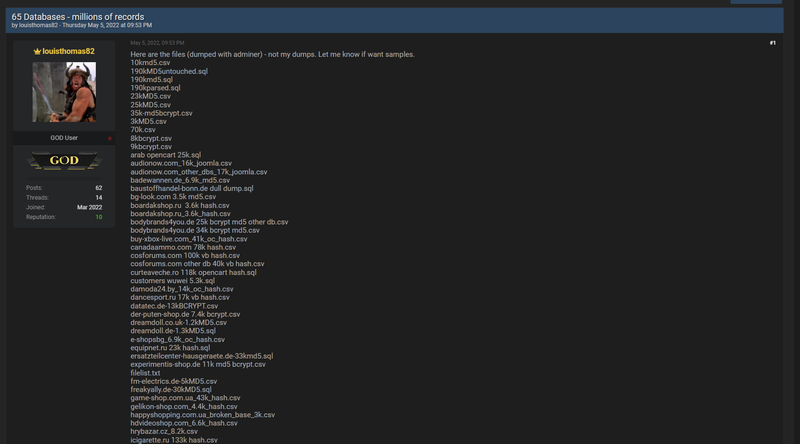
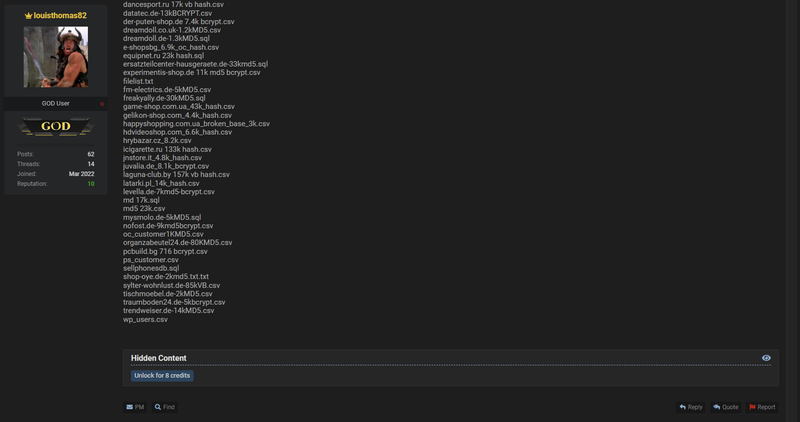
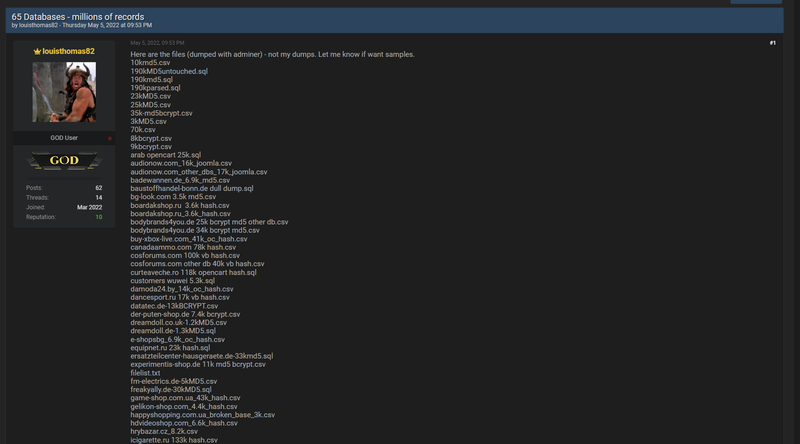
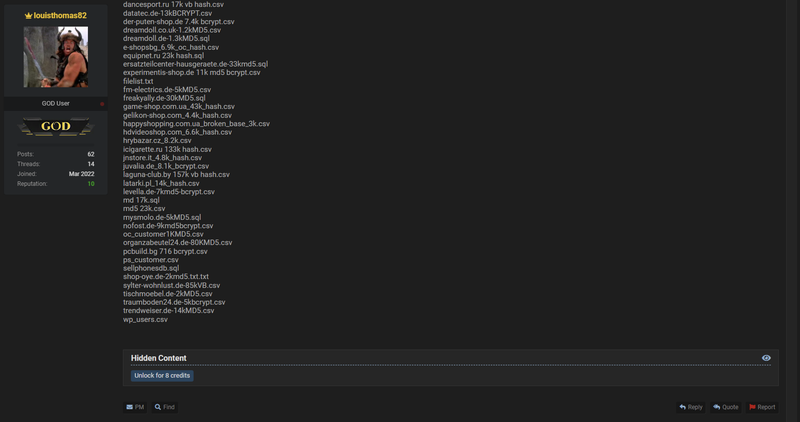
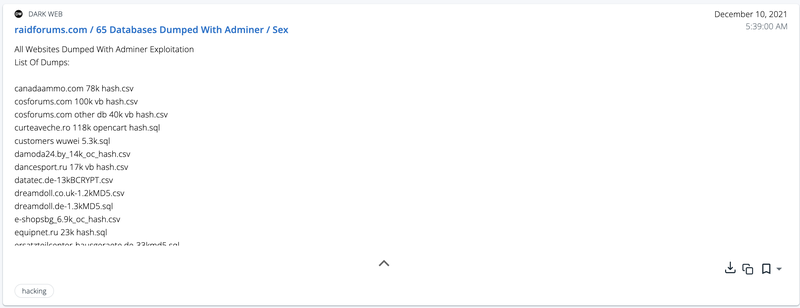
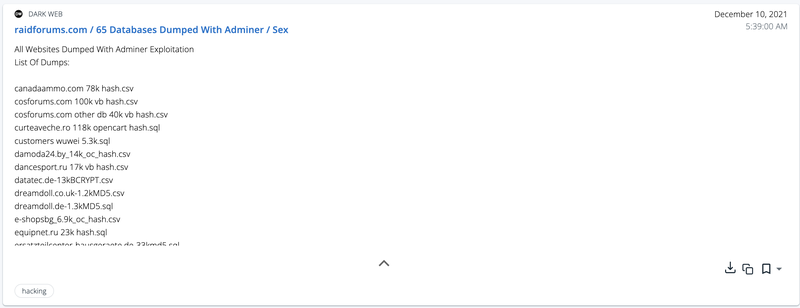
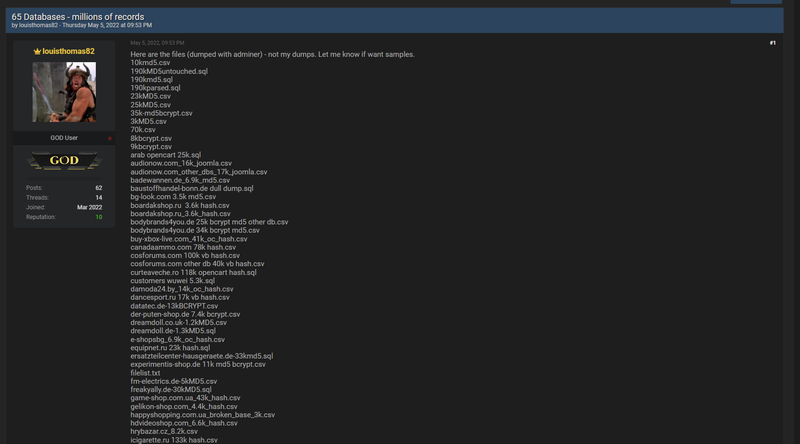
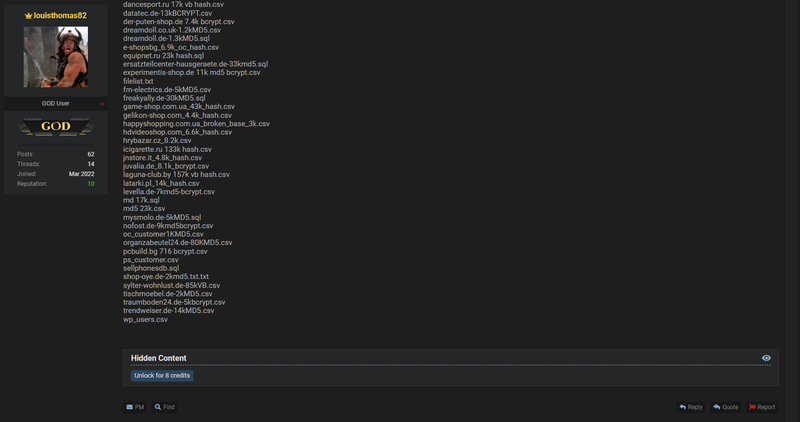
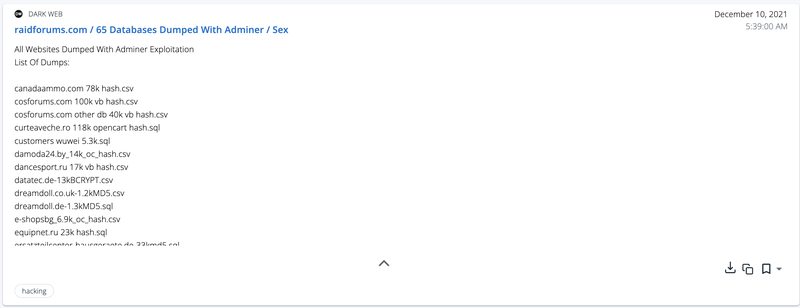
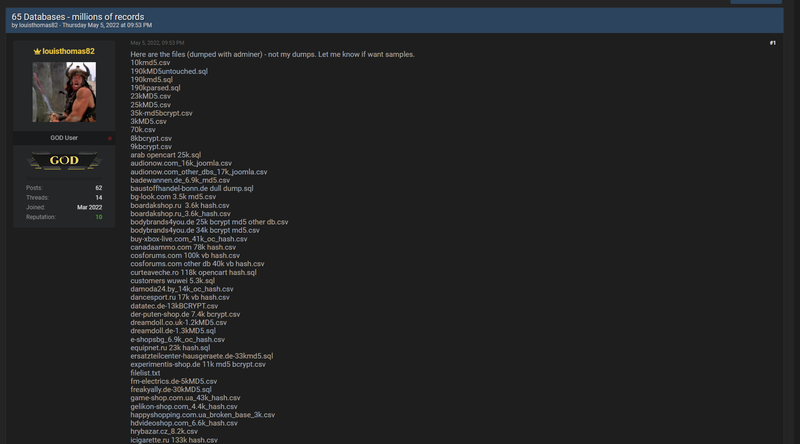
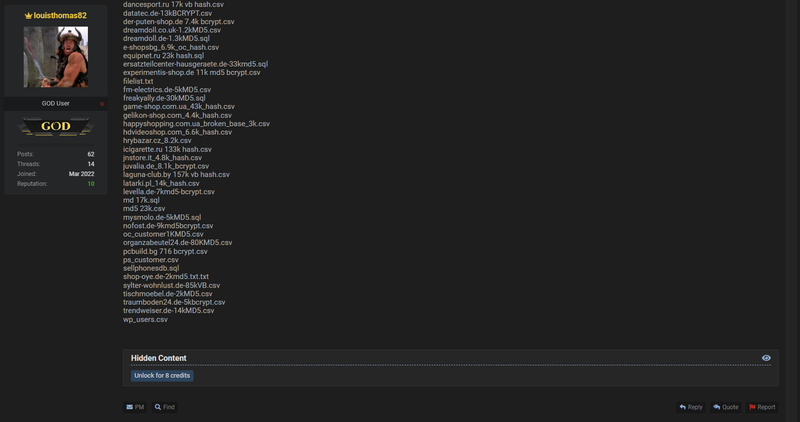
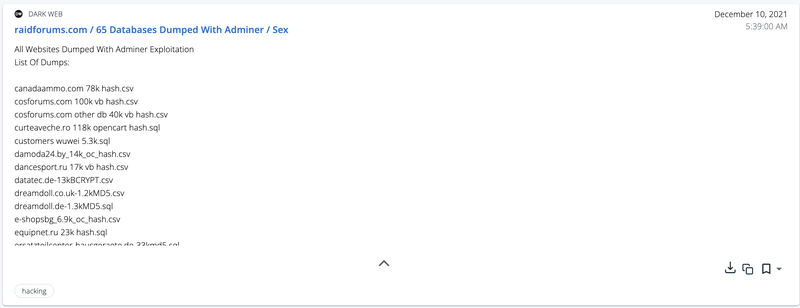
On May 5, 2022, a reputed threat actor "louisthomas82" from the BreachForums posted a data breach package targeting Juvalia (juvalia.de), a Germany-based online store sells special jewelry and watches from wide section of brands. The threat actor noted that the data breach package includes 65 databases with millions of records. The database for Juvalia is a part of that 65 databases. The data dump was also circulated in Raid Forums on December 10, 2021 by the threat actor "Sex". From the package published on BreachForums, ZeroFox extracted 8,107 email addresses and hashed passwords.
Recommendations
- If not already enabled, turn on the compromised credentials rule for all relevant entities and ensure relevant emails are entered for those entities, or reach out to [email protected] for assistance
- If one of your entities receives an alert, ZeroFox recommends immediate password changes for the affected account
- Enable 2-factor authentication for all of your organizational accounts to help mitigate phishing and credential stuffing attacks
Breach Disclosure: JN Store
On May 5, 2022, a reputed threat actor "louisthomas82" from the BreachForums posted a data breach package targeting JN Store, an Italy-based online store that sells nail reconstruction, health and beauty products. From the package published in BreachForums, ZeroFox extracted 4,797 email addresses and hashed passwords.
Standing Intelligence Requirements
For the most up to date list of ZeroFox Threat Research’s Intelligence Requirements, please visit:
https://cloud.zerofox.com/intelligence/advisories/14956
Details
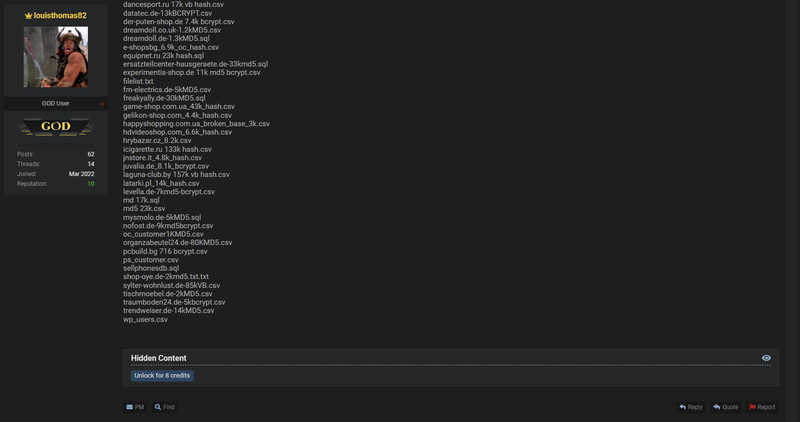
On May 5, 2022, a reputed threat actor "louisthomas82" from the BreachForums posted a data breach package targeting JN Store (jnstore[.]it), an Italy-based online store that sells nail reconstruction, health and beauty products. The threat actor noted that the data breach package includes 65 databases with millions of records. The database for JN Store is a part of that 65 databases. The data dump was also circulated in Raid Forums on December 10, 2021 by the threat actor "Sex". From the package published in BreachForums, ZeroFox extracted 4,797 email addresses and hashed passwords.
Recommendations
- If not already enabled, turn on the compromised credentials rule for all relevant entities and ensure relevant emails are entered for those entities, or reach out to [email protected] for assistance
- If one of your entities receives an alert, ZeroFox recommends immediate password changes for the affected account
- Enable 2-factor authentication for all of your organizational accounts to help mitigate phishing and credential stuffing attacks
Breach Disclosure: Hry Bazar
On May 5, 2022, a reputed threat actor "louisthomas82" from the BreachForums posted a data breach package targeting Hry Bazar, a Czechia-based online store sells bazaar games and accessories for different game consoles. From the package published in BreachForums, ZeroFox extracted 8,115 email addresses and hashed passwords.
Standing Intelligence Requirements
For the most up to date list of ZeroFox Threat Research’s Intelligence Requirements, please visit:
https://cloud.zerofox.com/intelligence/advisories/14956
Details
On May 5, 2022, a reputed threat actor "louisthomas82" from the BreachForums posted a data breach package targeting Hry Bazar (hrybazar[.]cz), a Czechia-based online store sells bazaar games and accessories for different game consoles. The threat actor noted that the data breach package includes 65 databases with millions of records. The database for Hry Bazar is a part of that 65 databases. The data dump was also circulated in Raid Forums on December 10, 2021 by the threat actor "Sex". From the package published in BreachForums, ZeroFox extracted 8,115 email addresses and hashed passwords.
Recommendations
- If not already enabled, turn on the compromised credentials rule for all relevant entities and ensure relevant emails are entered for those entities, or reach out to [email protected] for assistance
- If one of your entities receives an alert, ZeroFox recommends immediate password changes for the affected account
- Enable 2-factor authentication for all of your organizational accounts to help mitigate phishing and credential stuffing attacks
Breach Disclosure: 65 DBs
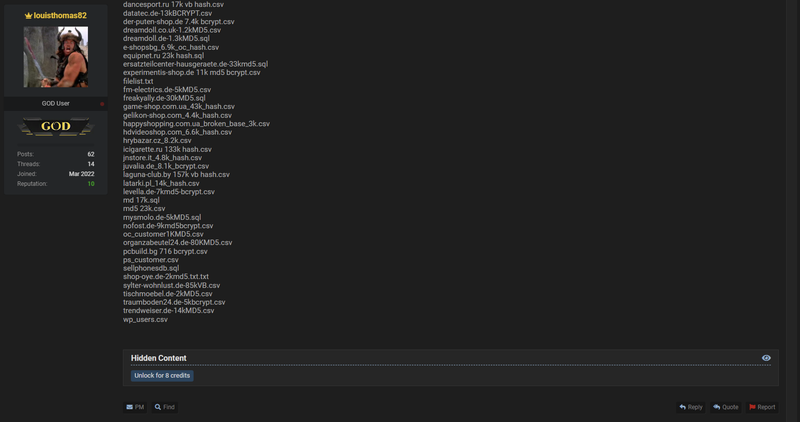
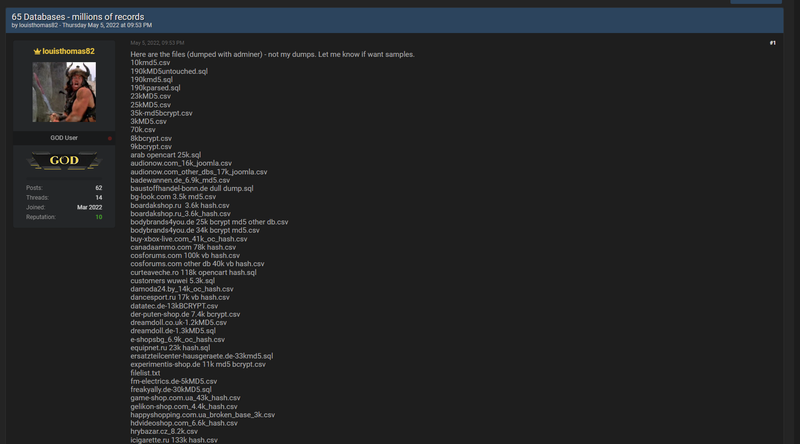
On May 5, 2022, a reputed threat actor "louisthomas82" from the BreachForums posted a combo list package. From the combo list package, ZeroFox collectively parsed the packages which were non-identifiable and titled as 65_DBs. ZeroFox extracted 432,405 email addresses and hashed passwords from the package.
Standing Intelligence Requirements
For the most up to date list of ZeroFox Threat Research’s Intelligence Requirements, please visit:
https://cloud.zerofox.com/intelligence/advisories/14956
Details
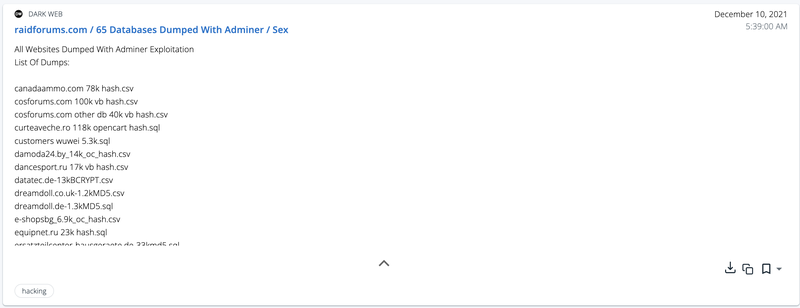
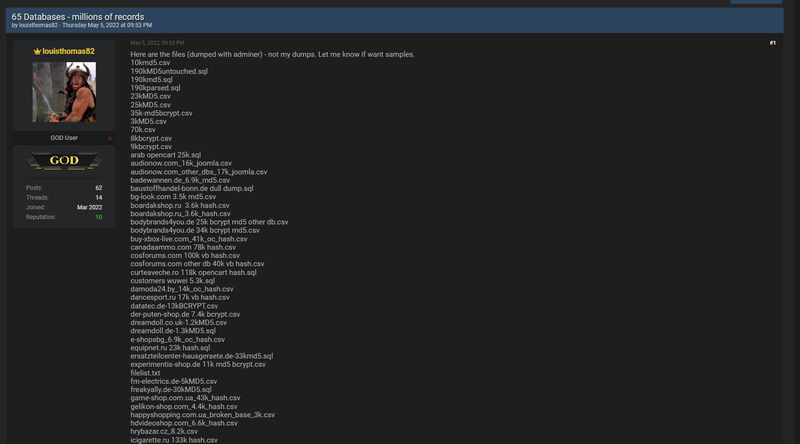
On May 5, 2022, a reputed threat actor "louisthomas82" from the BreachForums posted a combo list package. From the combo list package, ZeroFox collectively parsed the packages which were non-identifiable and titled as "65_DBs. The combolist was also circulated in Raid Forums on December 10, 2021, by the threat actor "Sex".The alert you received was from the acquisition and ingestion of what is known as a "combolilst" that was being shared on a Dark Web forum. A combo list is a list of allegedly compromised login credentials containing email addresses and their associated passwords. Combolists are often generated by threat actors from a variety of sources to be used in various onward malicious actions. The login credentials in these lists often come from a threat actor compiling data from previous breaches or exposures to take advantage of user’s who re-use their password on multiple websites or have not changed their password since it was exposed. ZeroFox emphasizes that threat actors often misrepresent the authenticity of some email and password combinations and in some cases completely make up the email and password combinations on these lists. From the package published in BreachForums, ZeroFox extracted 432,405 email addresses and hashed passwords.
Recommendations
- If not already enabled, turn on the compromised credentials rule for all relevant entities and ensure relevant emails are entered for those entities, or reach out to [email protected] for assistance
- If one of your entities receives an alert, ZeroFox recommends immediate password changes for the affected account
- Enable 2-factor authentication for all of your organizational accounts to help mitigate phishing and credential stuffing attacks
Breach Disclosure: Höhenrainer Delikatessen
On May 5, 2022, a reputed threat actor "louisthomas82" from the BreachForums posted a data breach package targeting Höhenrainer Delikatessen, a Germany-based online poultry related product selling website specialized in sausage. From this package, ZeroFox extracted 7,434 email addresses and hashed passwords.
Standing Intelligence Requirements
For the most up to date list of ZeroFox Threat Research’s Intelligence Requirements, please visit:
https://cloud.zerofox.com/intelligence/advisories/14956
Details
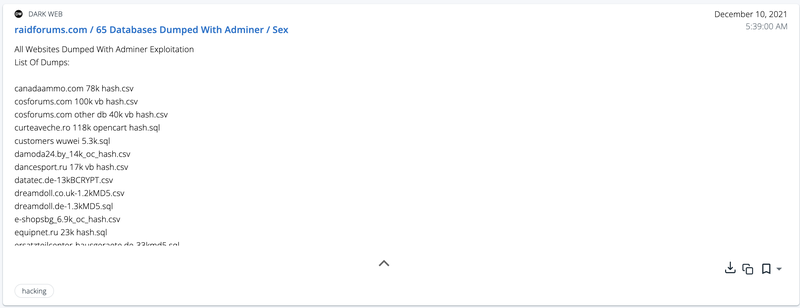
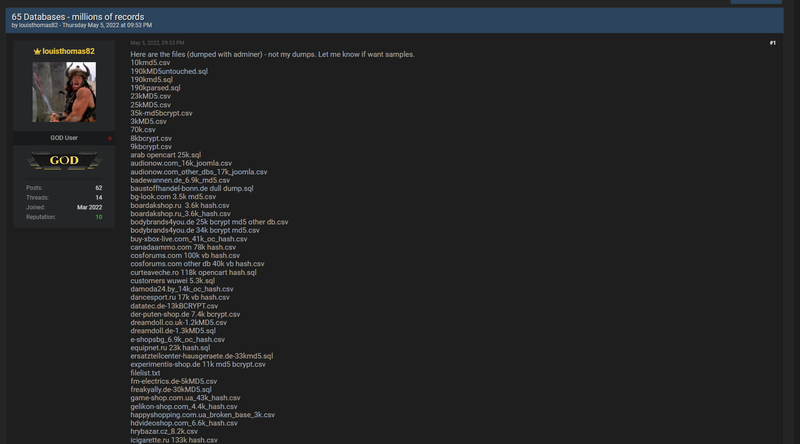
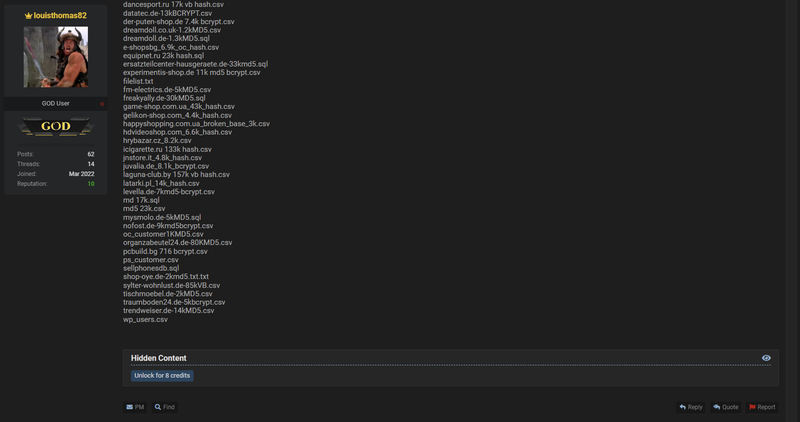
On May 5, 2022, a reputed threat actor "louisthomas82" from the BreachForums posted a data breach package targeting Höhenrainer Delikatessen (der-puten-shop[.]de), a Germany-based online poultry related product selling website specialized in sausage. The threat actor noted that the data breach package includes 65 Databases with millions of records. The database for Höhenrainer Delikatessen is a part of that 65 databases. The data dump was also circulated in Raid Forums on December 10, 2021 by the threat actor "Sex". From this package, ZeroFox extracted 7,434 email addresses and hashed passwords.
Recommendations
- If not already enabled, turn on the compromised credentials rule for all relevant entities and ensure relevant emails are entered for those entities, or reach out to [email protected] for assistance
- If one of your entities receives an alert, ZeroFox recommends immediate password changes for the affected account
- Enable 2-factor authentication for all of your organizational accounts to help mitigate phishing and credential stuffing attacks
Breach Disclosure: Buy Xbox Live
On May 5, 2022, a reputed threat actor "louisthomas82" from the BreachForums posted a data breach package targeting Buy Xbox Live, a website selling video games and prepaid cards of Xbox online operating from Spain. From the package published in BreachForums, ZeroFox extracted 41,227 email addresses and hashed passwords.
Standing Intelligence Requirements
For the most up to date list of ZeroFox Threat Research’s Intelligence Requirements, please visit:
https://cloud.zerofox.com/intelligence/advisories/14956
Details
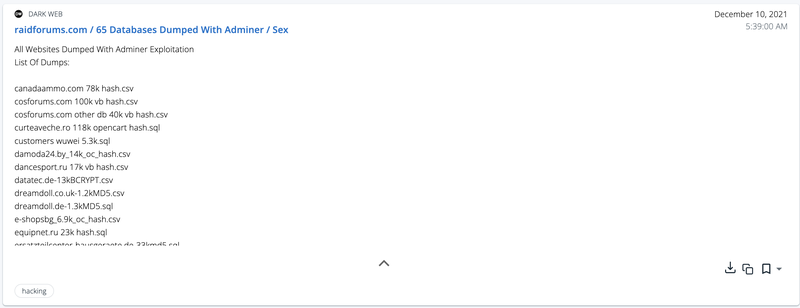
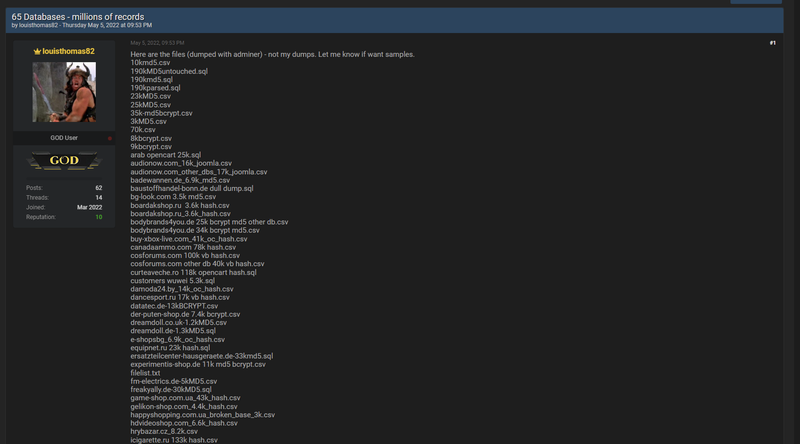
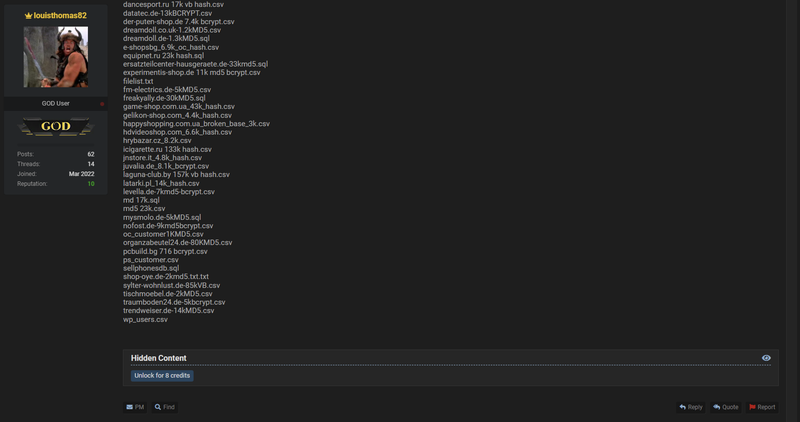
On May 5, 2022, a reputed threat actor "louisthomas82" from the BreachForums posted a data breach package targeting Buy Xbox Live (buy-xbox-live[.]com), a website selling video games and prepaid cards of Xbox online operating from Spain. The threat actor noted that the data breach package includes 65 Databases with millions of records. The database for Buy Xbox Live is a part of that 65 databases. The data dump was also circulated in Raid Forums on December 10, 2021 by the threat actor "Sex". From the package published in BreachForums, ZeroFox extracted 41,227 email addresses and hashed passwords.
Recommendations
- If not already enabled, turn on the compromised credentials rule for all relevant entities and ensure relevant emails are entered for those entities, or reach out to [email protected] for assistance
- If one of your entities receives an alert, ZeroFox recommends immediate password changes for the affected account
- Enable 2-factor authentication for all of your organizational accounts to help mitigate phishing and credential stuffing attacks
Breach Disclosure: dataTec
On May 5, 2022, a reputed threat actor "louisthomas82" from the BreachForums posted a data breach package targeting dataTec, a Germany-based company that manufactures and retails the electrical and electronics equipments. From the package published on BreachForums, ZeroFox extracted 14,218 email addresses and hashed passwords.
Standing Intelligence Requirements
For the most up to date list of ZeroFox Threat Research’s Intelligence Requirements, please visit:
https://cloud.zerofox.com/intelligence/advisories/14956
Details
On May 5, 2022, a reputed threat actor "louisthomas82" from the BreachForums posted a data breach package targeting dataTec (datatec.de), a Germany-based company that manufactures and retails the electrical and electronics equipments. The threat actor noted that the data breach package includes 65 Databases with millions of records. The database for dataTec is a part of that 65 databases. The data dump was also circulated in Raid Forums on December 10, 2021 by the threat actor "Sex". From the package published on BreachForums, ZeroFox extracted 14,218 email addresses and hashed passwords.


Recommendations
- If not already enabled, turn on the compromised credentials rule for all relevant entities and ensure relevant emails are entered for those entities, or reach out to [email protected] for assistance
- If one of your entities receives an alert, ZeroFox recommends immediate password changes for the affected account
- Enable 2-factor authentication for all of your organizational accounts to help mitigate phishing and credential stuffing attacks
Breach Disclosure: Go Ninja
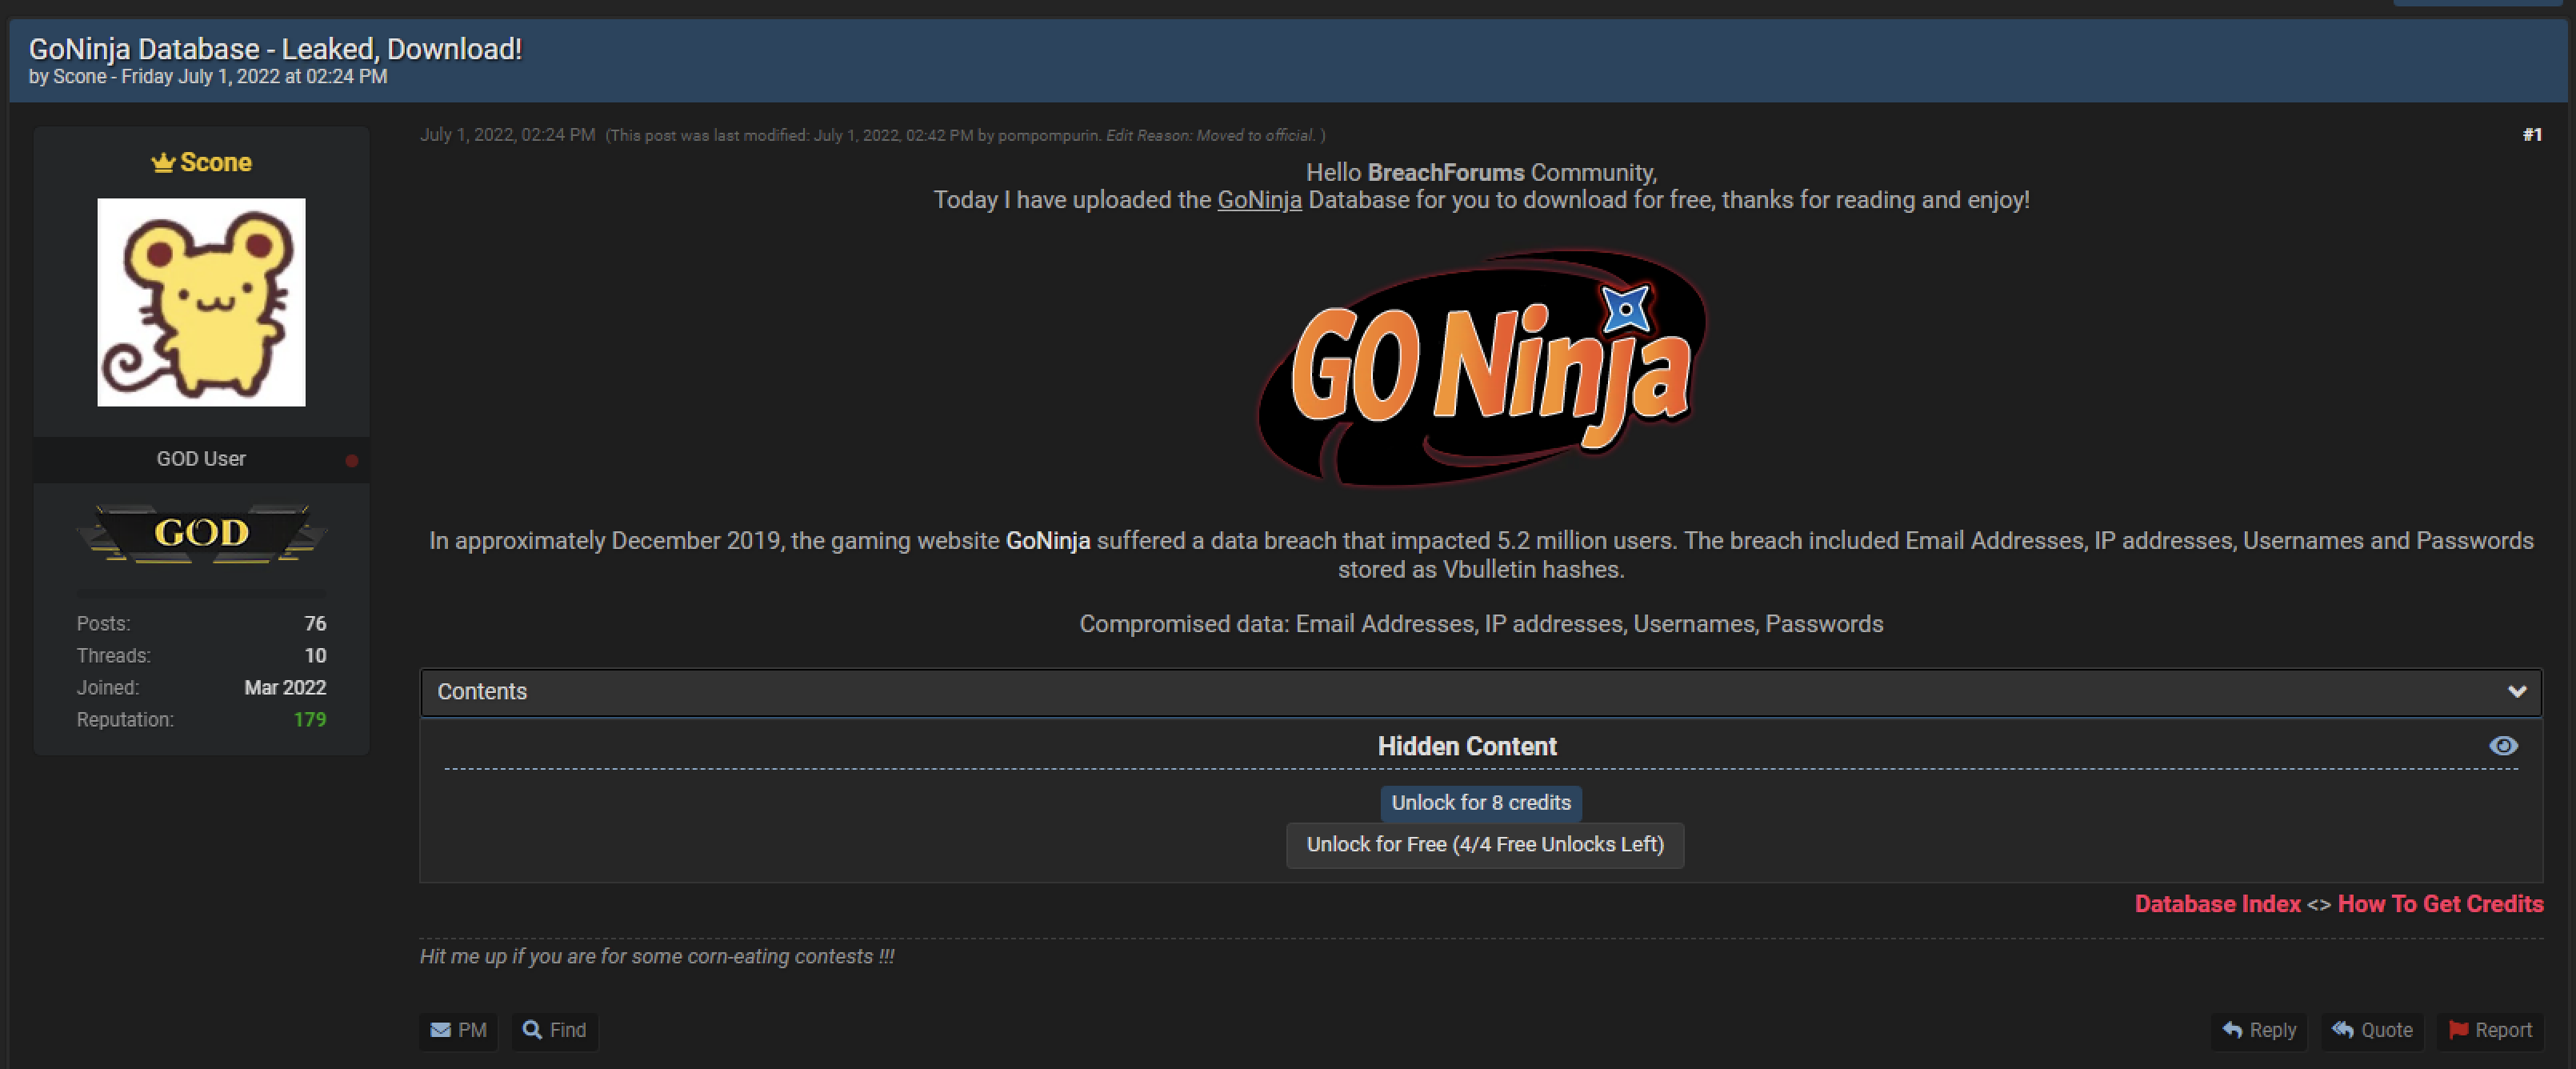
On July 1, 2022, a reputed threat actor "Scone" from the BreachForums posted a data breach package targeting Go Ninja, a Germany-based online gaming website. From the package posted on BreachForums, ZeroFox extracted 4,999,903 usernames, email addresses and hashed passwords.
Standing Intelligence Requirements
For the most up to date list of ZeroFox Threat Research’s Intelligence Requirements, please visit:
https://cloud.zerofox.com/intelligence/advisories/14956
Details
On July 1, 2022, a reputed threat actor "Scone" from the BreachForums posted a data breach package targeting Go Ninja (goninja.de), a Germany-based online gaming website. The threat actor noted that the data dump is from the year 2019 which impacted 5.2 million users. From the package posted on BreachForums, ZeroFox extracted 4,999,903 usernames, email addresses and hashed passwords. Other notable data fields observed in this package include: regip, regdate, lastloginip, lastlogintime, salt, and secques.
Recommendations
- If not already enabled, turn on the compromised credentials rule for all relevant entities and ensure relevant emails are entered for those entities, or reach out to [email protected] for assistance
- If one of your entities receives an alert, ZeroFox recommends immediate password changes for the affected account
- Enable 2-factor authentication for all of your organizational accounts to help mitigate phishing and credential stuffing attacks
Breach Disclosure: experimentis
On May 5, 2022, a reputed threat actor "louisthomas82" from the BreachForums posted a data breach package targeting experimentis, a Germany-based online store that sells products related to physics toys, science gifts & gadgets, kinetic art. From the package posted on BreachForums, ZeroFox extracted 17,812 email addresses.
Standing Intelligence Requirements
For the most up to date list of ZeroFox Threat Research’s Intelligence Requirements, please visit:
https://cloud.zerofox.com/intelligence/advisories/14956
Details
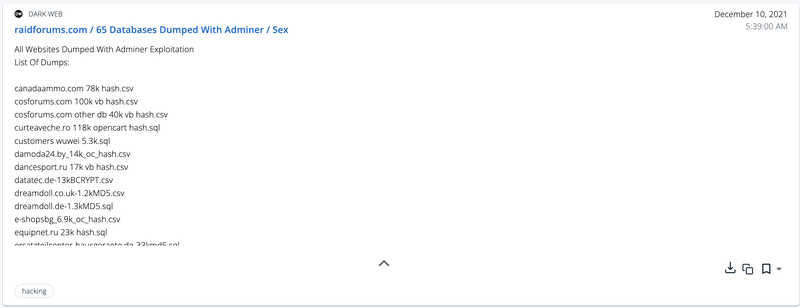
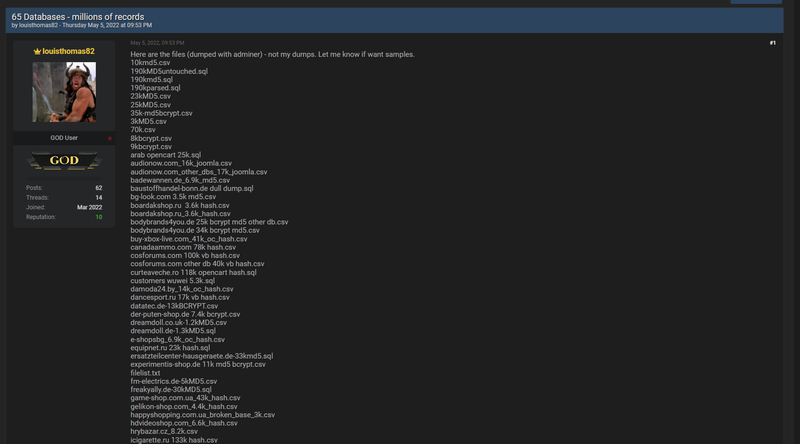
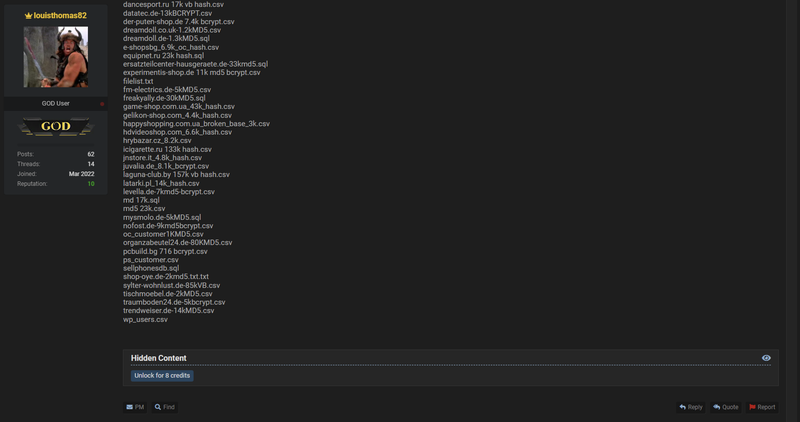
On May 5, 2022, a reputed threat actor "louisthomas82" from the BreachForums posted a data breach package targeting experimentis (experimentis-shop[.]de), a Germany-based online store that sells products related to physics toys, science gifts & gadgets, kinetic art. The threat actor noted that the data breach package includes 65 Databases with millions of records. The database for experimentis is a part of that 65 databases. The data dump was also circulated in Raid Forums on December 10, 2021 by the threat actor "Sex". From the package posted on BreachForums, ZeroFox extracted 17,812 email addresses. Of this total, an assessed 17,809 records contained hashed passwords.
Recommendations
- If not already enabled, turn on the compromised credentials rule for all relevant entities and ensure relevant emails are entered for those entities, or reach out to [email protected] for assistance
- If one of your entities receives an alert, ZeroFox recommends immediate password changes for the affected account
- Enable 2-factor authentication for all of your organizational accounts to help mitigate phishing and credential stuffing attacks
Breach Disclosure: DreamDoll
On May 5, 2022, a reputed threat actor "louisthomas82" from the BreachForums posted a data breach package targeting DreamDoll, a U.K.-based online store for sex dolls & real dolls. From the package posted on BreachForums, ZeroFox extracted 1,230 email addresses and hashed passwords.
Standing Intelligence Requirements
For the most up to date list of ZeroFox Threat Research’s Intelligence Requirements, please visit:
https://cloud.zerofox.com/intelligence/advisories/14956
Details
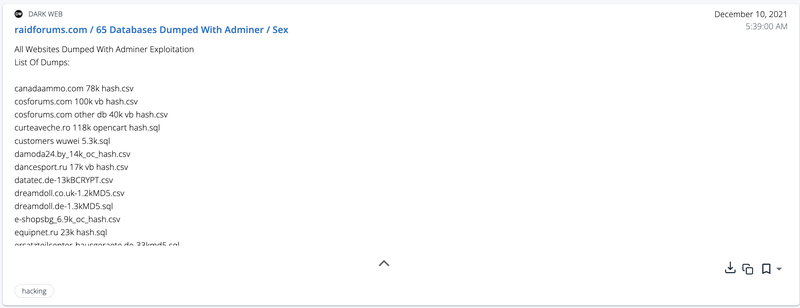
On May 5, 2022, a reputed threat actor "louisthomas82" from the BreachForums posted a data breach package targeting DreamDoll (dreamdoll.co.uk), a U.K.-based online store for sex dolls & real dolls. The threat actor noted that the data breach package includes 65 Databases with millions of records. The database for DreamDoll is a part of that 65 databases. The data dump was also circulated in Raid Forums on December 10, 2021 by the threat actor "Sex". From the package posted on BreachForums, ZeroFox extracted 1,230 email addresses and hashed passwords.
Recommendations
- If not already enabled, turn on the compromised credentials rule for all relevant entities and ensure relevant emails are entered for those entities, or reach out to [email protected] for assistance
- If one of your entities receives an alert, ZeroFox recommends immediate password changes for the affected account
- Enable 2-factor authentication for all of your organizational accounts to help mitigate phishing and credential stuffing attacks
Breach Disclosure: Fm-electrics
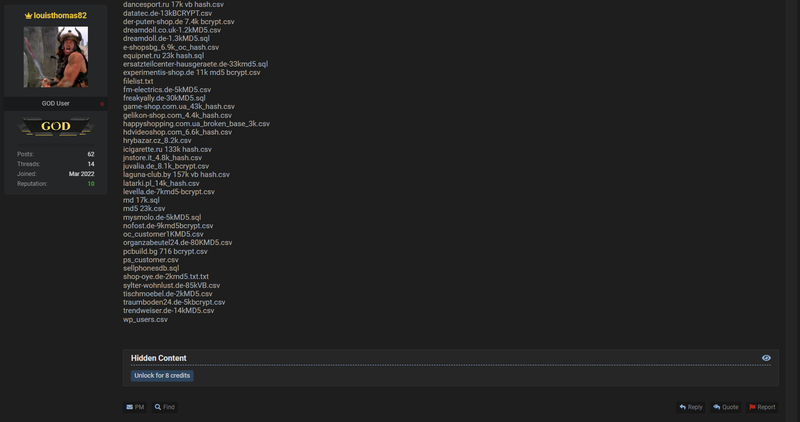
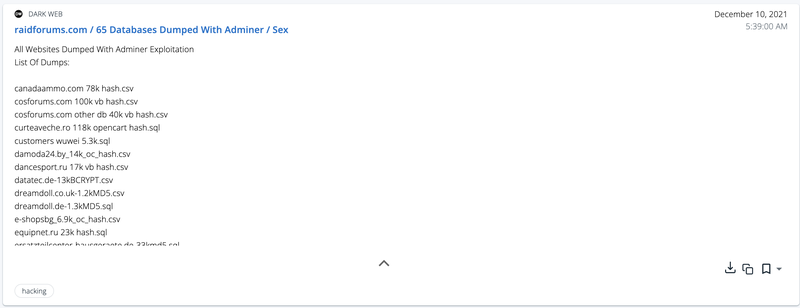
On May 5, 2022, a reputed threat actor "louisthomas82" from the BreachForums posted a data breach package targeting Fm-electrics, a Germany-based online store for electrical equipments and accessories. From this package published in BreachForums, ZeroFox extracted 4,644 email addresses and hashed passwords.
Standing Intelligence Requirements
For the most up to date list of ZeroFox Threat Research’s Intelligence Requirements, please visit:
https://cloud.zerofox.com/intelligence/advisories/14956
Details
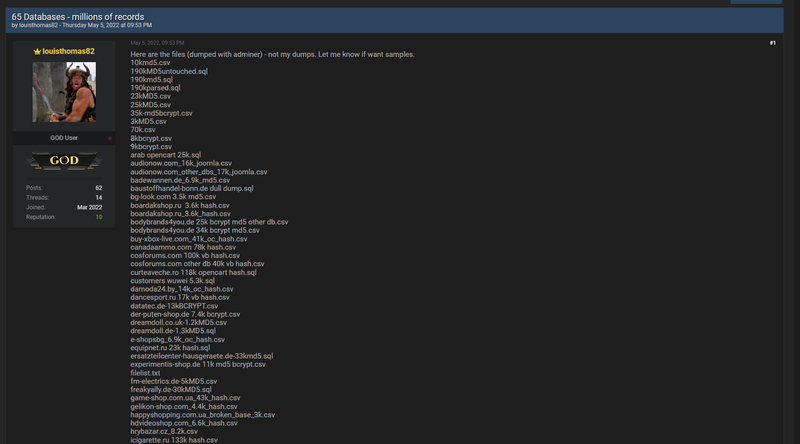
On May 5, 2022, a reputed threat actor "louisthomas82" from the BreachForums posted a data breach package targeting Fm-electrics (fm-electrics.de), a Germany-based online store for electrical equipments and accessories. The threat actor noted that the data breach package includes 65 Databases with millions of records. The database for Fm-electrics is a part of that 65 databases. The data dump was also circulated in Raid Forums on December 10, 2021 by the threat actor "Sex". From this package published in BreachForums, ZeroFox extracted 4,644 email addresses and hashed passwords.
Recommendations
- If not already enabled, turn on the compromised credentials rule for all relevant entities and ensure relevant emails are entered for those entities, or reach out to [email protected] for assistance
- If one of your entities receives an alert, ZeroFox recommends immediate password changes for the affected account
- Enable 2-factor authentication for all of your organizational accounts to help mitigate phishing and credential stuffing attacks
Breach Disclosure: Freaky Ally
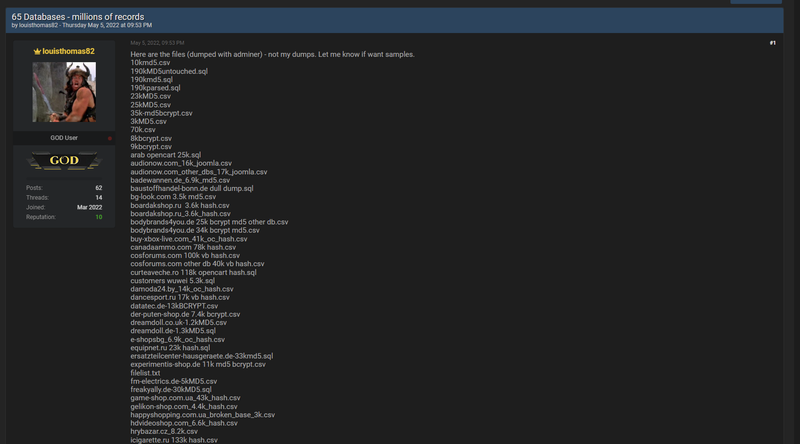
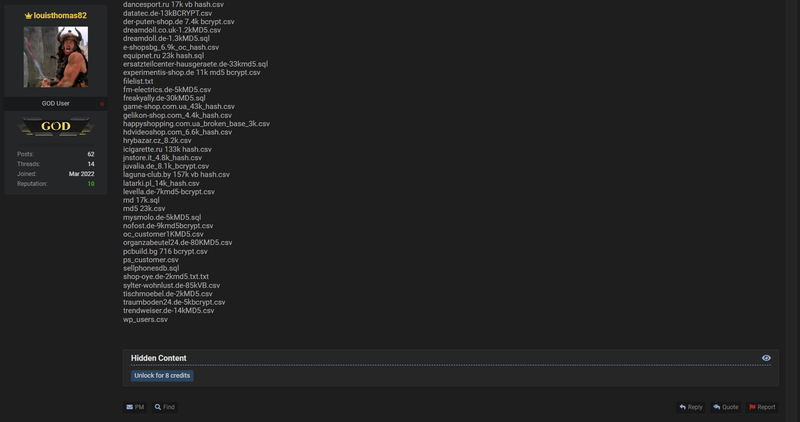
On May 5, 2022, a reputed threat actor "louisthomas82" from the BreachForums posted a data breach package targeting Freaky Ally, a Germany-based online Vape store. From this package published on BreachForums, ZeroFox extracted 26,857 email addresses.
Standing Intelligence Requirements
For the most up to date list of ZeroFox Threat Research’s Intelligence Requirements, please visit:
https://cloud.zerofox.com/intelligence/advisories/14956
Details
On May 5, 2022, a reputed threat actor "louisthomas82" from the BreachForums posted a data breach package targeting Freaky Ally (freakyally[.]de), a Germany-based online Vape store. The threat actor noted that the data breach package includes 65 Databases with millions of records. The database for Freaky Ally is a part of that 65 databases. The data dump was also circulated in Raid Forums on December 10, 2021 by the threat actor "Sex". From this package published on BreachForums, ZeroFox extracted 26,857 email addresses. Of this total, an assessed 26,119 records contained hashed passwords.
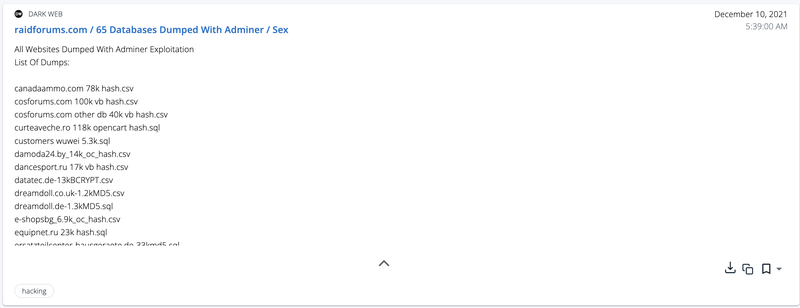
Recommendations
- If not already enabled, turn on the compromised credentials rule for all relevant entities and ensure relevant emails are entered for those entities, or reach out to [email protected] for assistance
- If one of your entities receives an alert, ZeroFox recommends immediate password changes for the affected account
- Enable 2-factor authentication for all of your organizational accounts to help mitigate phishing and credential stuffing attacks
Breach Disclosure: Game Shop
On May 5, 2022, a reputed threat actor "louisthomas82" from the BreachForums posted a data breach package targeting Game Shop, a Ukraine-based online store for game consoles and accessories. From this package published on BreachForums, ZeroFox extracted 42,684 email addresses and hashed passwords.
Standing Intelligence Requirements
For the most up to date list of ZeroFox Threat Research’s Intelligence Requirements, please visit:
https://cloud.zerofox.com/intelligence/advisories/14956
Details
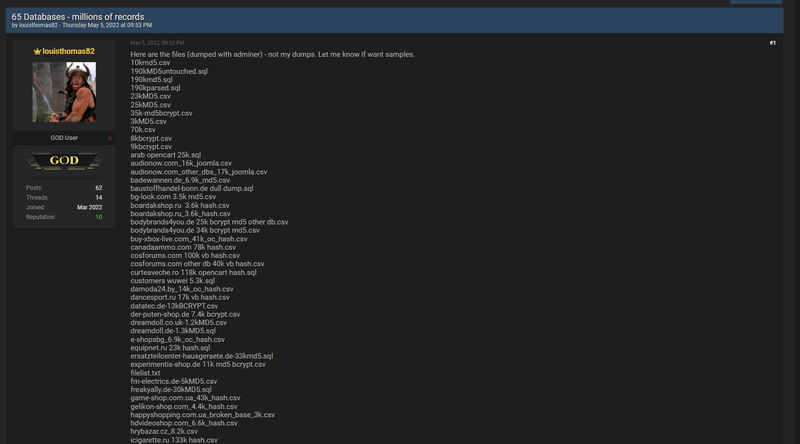
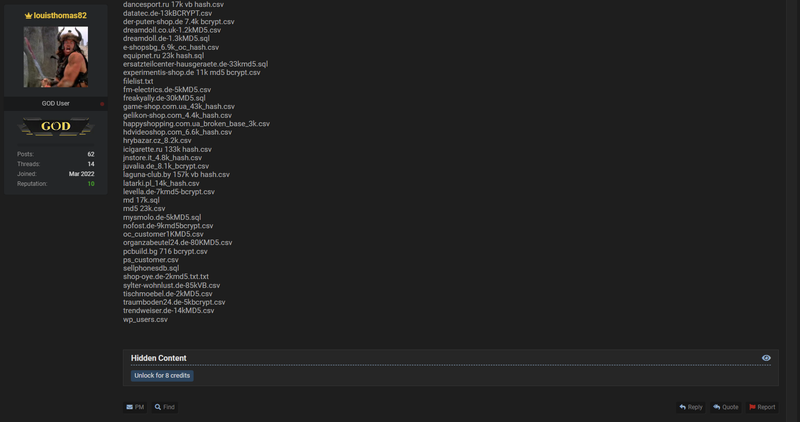
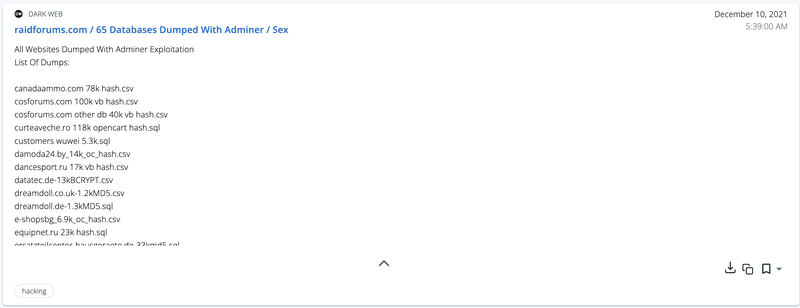
On May 5, 2022, a reputed threat actor "louisthomas82" from the BreachForums posted a data breach package targeting Game Shop (game-shop[.]com[.]ua), a Ukraine-based online store for game consoles and accessories. The threat actor noted that the data breach package includes 65 Databases with millions of records. The database for Game Shop is a part of that 65 databases. The data dump was also circulated in Raid Forums on December 10, 2021, by the threat actor "Sex". From this package published on BreachForums, ZeroFox extracted 42,684 email addresses and hashed passwords.
Recommendations
- If not already enabled, turn on the compromised credentials rule for all relevant entities and ensure relevant emails are entered for those entities, or reach out to [email protected] for assistance
- If one of your entities receives an alert, ZeroFox recommends immediate password changes for the affected account
- Enable 2-factor authentication for all of your organizational accounts to help mitigate phishing and credential stuffing attacks
Breach Disclosure: Gelikon
On May 5, 2022, a reputed threat actor "louisthomas82" from the BreachForums posted a data breach package targeting Gelikon, a Germany-based online store for books, movies, audiobooks, and press. From this package published on BreachForums, ZeroFox extracted 4,395 email addresses and hashed passwords.
Standing Intelligence Requirements
For the most up to date list of ZeroFox Threat Research’s Intelligence Requirements, please visit:
https://cloud.zerofox.com/intelligence/advisories/14956
Details
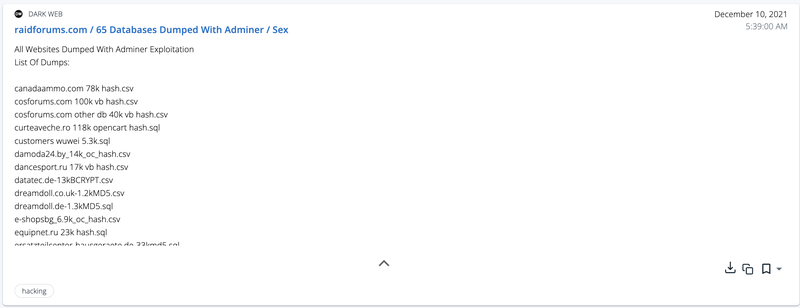
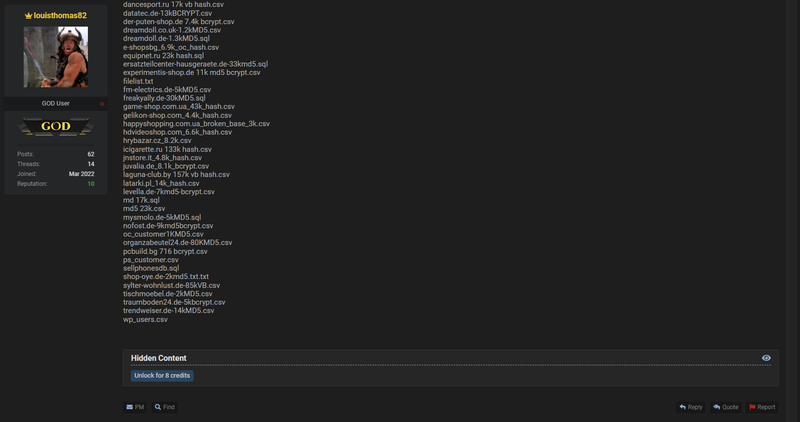
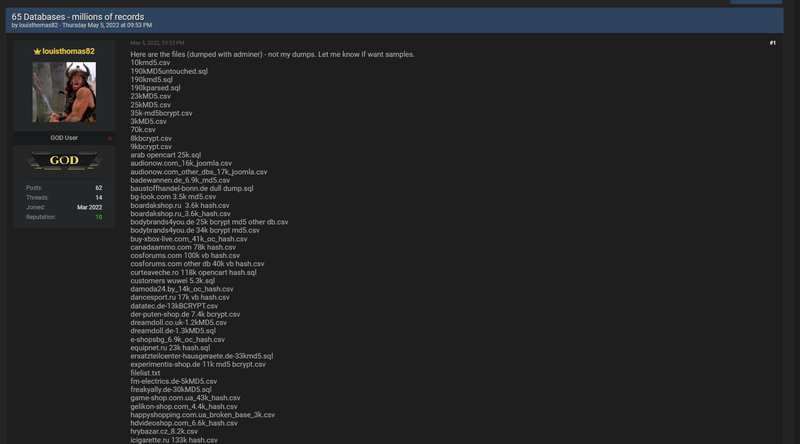
On May 5, 2022, a reputed threat actor "louisthomas82" from the BreachForums posted a data breach package targeting Gelikon (gelikon-shop[.]com), a Germany-based online store for books, movies, audiobooks, and press. The threat actor noted that the data breach package includes 65 Databases with millions of records. The database for Gelikon is a part of that 65 database. The data dump was also circulated in Raid Forums on December 10, 2021, by the threat actor "Sex". From this package published on BreachForums, ZeroFox extracted 4,395 email addresses and hashed passwords.
Recommendations
- If not already enabled, turn on the compromised credentials rule for all relevant entities and ensure relevant emails are entered for those entities, or reach out to [email protected] for assistance
- If one of your entities receives an alert, ZeroFox recommends immediate password changes for the affected account
- Enable 2-factor authentication for all of your organizational accounts to help mitigate phishing and credential stuffing attacks
Breach Disclosure: HAPPYShopping
On May 5, 2022, a reputed threat actor "louisthomas82" from the BreachForums posted a data breach package targeting HAPPYShopping, an Ukraine-based online store for fashion and lifestyle. From this package published on BreachForums, ZeroFox extracted 1,047 email addresses. Of this total, an assessed 27 records contained hashed passwords.
Standing Intelligence Requirements
For the most up to date list of ZeroFox Threat Research’s Intelligence Requirements, please visit:
https://cloud.zerofox.com/intelligence/advisories/14956
Details
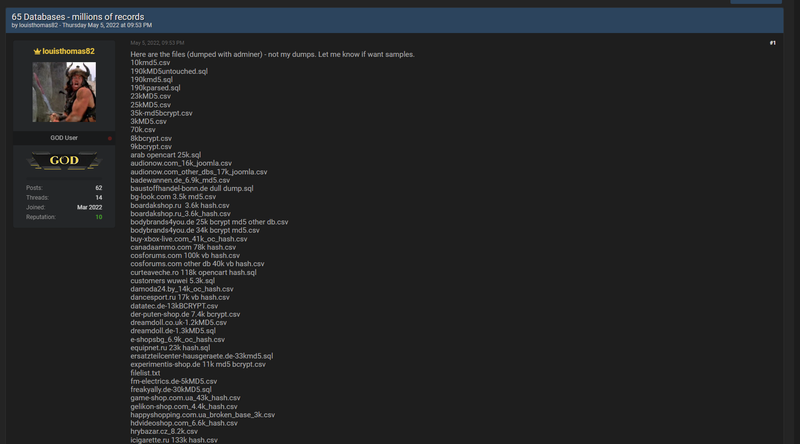
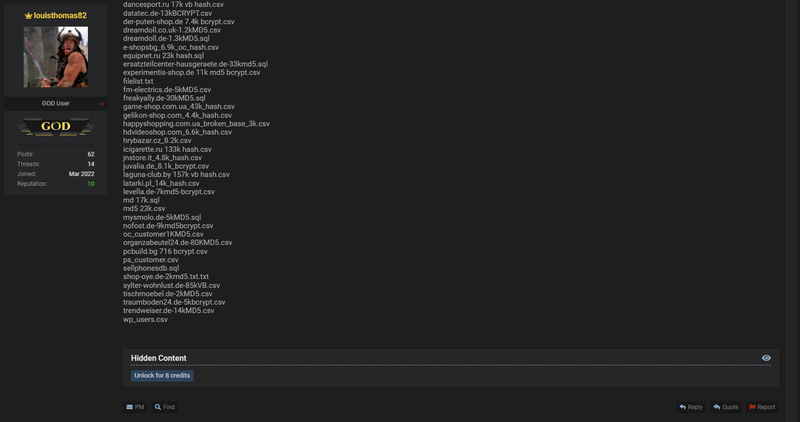
On May 5, 2022, a reputed threat actor "louisthomas82" from the BreachForums posted a data breach package targeting HAPPYShopping (happyshopping[.]com[.]ua), an Ukraine-based online store for fashion and lifestyle. The threat actor noted that the data breach package includes 65 Databases with millions of records. The database for HAPPYShopping is a part of that 65 databases. The data dump was also circulated in Raid Forums on December 10, 2021 by the threat actor "Sex". From this package published on BreachForums, ZeroFox extracted 1,047 email addresses. Of this total, an assessed 27 records contained hashed passwords.
Recommendations
- If not already enabled, turn on the compromised credentials rule for all relevant entities and ensure relevant emails are entered for those entities, or reach out to [email protected] for assistance
- If one of your entities receives an alert, ZeroFox recommends immediate password changes for the affected account
- Enable 2-factor authentication for all of your organizational accounts to help mitigate phishing and credential stuffing attacks
Breach Disclosure: MDS
On May 5, 2022, a reputed threat actor "louisthomas82" from the BreachForums posted a data breach package targeting MDS, a spare parts store for household appliances and electronic components operating from Germany. From this package published on BreachForums, ZeroFox extracted 33,407 usernames and email addresses. Of this total, an assessed 33,335 records contained hashed passwords.
Standing Intelligence Requirements
For the most up to date list of ZeroFox Threat Research’s Intelligence Requirements, please visit:
https://cloud.zerofox.com/intelligence/advisories/14956
Details
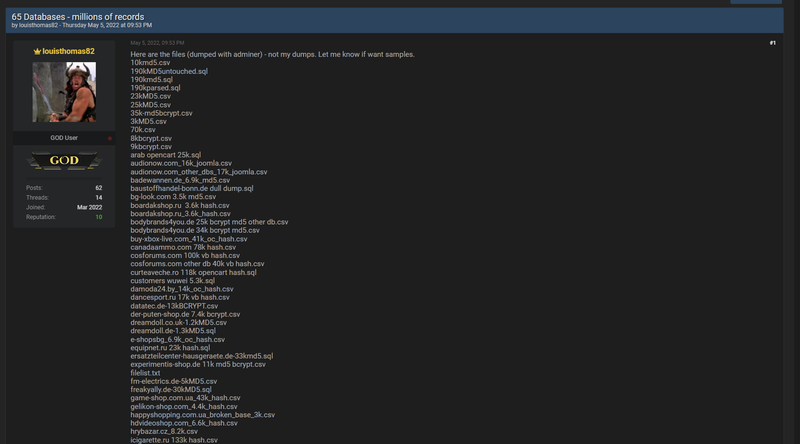
On May 5, 2022, a reputed threat actor "louisthomas82" from the BreachForums posted a data breach package targeting MDS (ersatzteilcenter-hausgeraete.de), a spare parts store for household appliances and electronic components operating from Germany. The threat actor noted that the data breach package includes 65 Databases with millions of records. The database for MDS is a part of that 65 databases. The data dump was also circulated in Raid Forums on December 10, 2021 by the threat actor "Sex". From this package published on BreachForums, ZeroFox extracted 33,407 usernames and email addresses. Of this total, an assessed 33,335 records contained hashed passwords.
Recommendations
- If not already enabled, turn on the compromised credentials rule for all relevant entities and ensure relevant emails are entered for those entities, or reach out to [email protected] for assistance
- If one of your entities receives an alert, ZeroFox recommends immediate password changes for the affected account
- Enable 2-factor authentication for all of your organizational accounts to help mitigate phishing and credential stuffing attacks
Breach Disclosure: EquipNet
On May 5, 2022, a reputed threat actor "louisthomas82" from the BreachForums posted a data breach package targeting EquipNet, an online store for industrial equipment operating from Russia. From this package published on BreachForums, ZeroFox extracted 25,200 email addresses. Of this total, an assessed 22,965 records contained hashed passwords.
Standing Intelligence Requirements
For the most up to date list of ZeroFox Threat Research’s Intelligence Requirements, please visit:
https://cloud.zerofox.com/intelligence/advisories/14956
Details
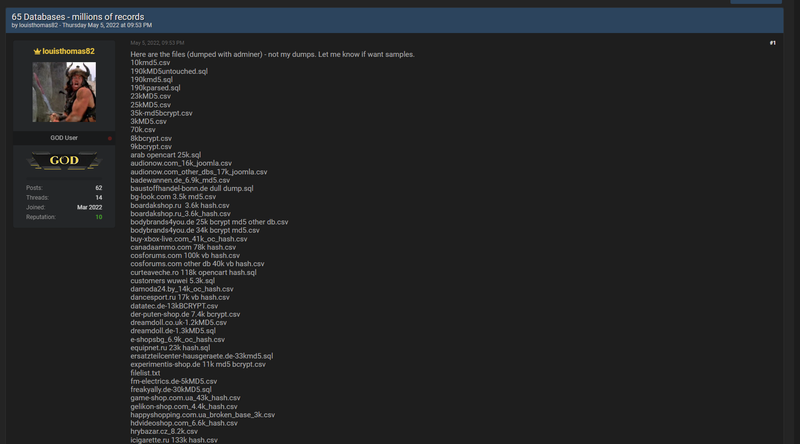
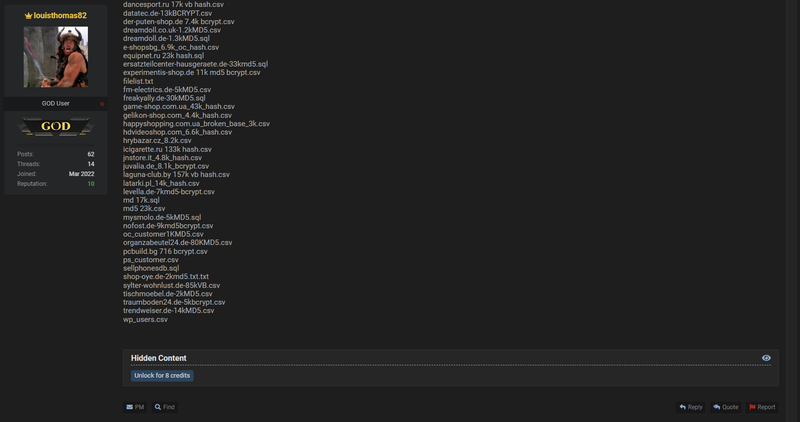
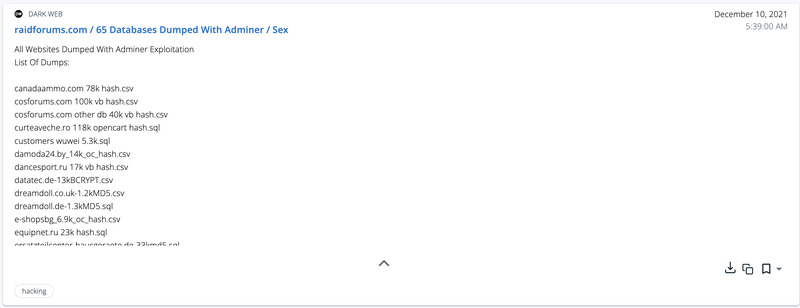
On May 5, 2022, a reputed threat actor "louisthomas82" from the BreachForums posted a data breach package targeting EquipNet (equipnet[.]ru), an online store for industrial equipment operating from Russia. The threat actor noted that the data breach package includes 65 Databases with millions of records. The database for EquipNet is a part of that 65 databases. The data dump was also circulated in Raid Forums on December 10, 2021, by the threat actor "Sex". From this package published on BreachForums, ZeroFox extracted 25,200 email addresses. Of this total, an assessed 22,965 records contained hashed passwords.
Recommendations
- If not already enabled, turn on the compromised credentials rule for all relevant entities and ensure relevant emails are entered for those entities, or reach out to [email protected] for assistance
- If one of your entities receives an alert, ZeroFox recommends immediate password changes for the affected account
- Enable 2-factor authentication for all of your organizational accounts to help mitigate phishing and credential stuffing attacks
Breach Disclosure: PC Build
On May 5, 2022, a reputed threat actor "louisthomas82" from the BreachForums posted a data breach package targeting PC Build, a Bulgaria-based online store for computers and its accessories. From this package published in BreachForums, ZeroFox extracted 722 email addresses and hashed passwords.
Standing Intelligence Requirements
For the most up to date list of ZeroFox Threat Research’s Intelligence Requirements, please visit:
https://cloud.zerofox.com/intelligence/advisories/14956
Details
On May 5, 2022, a reputed threat actor "louisthomas82" from the BreachForums posted a data breach package targeting PC Build (pcbuild[.]bg), a Bulgaria-based online store for computers and its accessories. The threat actor noted that the data breach package includes 65 Databases with millions of records. The database for PC Build is a part of that 65 databases. The data dump was also circulated in Raid Forums on December 10, 2021, by the threat actor "Sex". From this package published in BreachForums, ZeroFox extracted 722 email addresses and hashed passwords.


Recommendations
- If not already enabled, turn on the compromised credentials rule for all relevant entities and ensure relevant emails are entered for those entities, or reach out to [email protected] for assistance
- If one of your entities receives an alert, ZeroFox recommends immediate password changes for the affected account
- Enable 2-factor authentication for all of your organizational accounts to help mitigate phishing and credential stuffing attacks
Breach Disclosure: Trendweiser
On May 5, 2022, a reputed threat actor "louisthomas82" from the BreachForums posted a data breach package targeting Trendweiser, an online store for Italian designer shoes and fashion items. From this package published in BreachForums, ZeroFox extracted 13,974 email addresses and hashed passwords.
Standing Intelligence Requirements
For the most up to date list of ZeroFox Threat Research’s Intelligence Requirements, please visit:
https://cloud.zerofox.com/intelligence/advisories/14956
Details
On May 5, 2022, a reputed threat actor "louisthomas82" from the BreachForums posted a data breach package targeting Trendweiser (trendweiser[.]de), an online store for Italian designer shoes and fashion items. The threat actor noted that the data breach package includes 65 Databases with millions of records. The database for Trendweiser is a part of that 65 databases. The data dump was also circulated in Raid Forums on December 10, 2021, by the threat actor "Sex". From this package published in BreachForums, ZeroFox extracted 13,974 email addresses and hashed passwords.
Recommendations
- If not already enabled, turn on the compromised credentials rule for all relevant entities and ensure relevant emails are entered for those entities, or reach out to [email protected] for assistance
- If one of your entities receives an alert, ZeroFox recommends immediate password changes for the affected account
- Enable 2-factor authentication for all of your organizational accounts to help mitigate phishing and credential stuffing attacks
Breach Disclosure: Traumboden24
On May 5, 2022, a reputed threat actor "louisthomas82" from the BreachForums posted a data breach package targeting Tischmoebel, an online wooden furniture store operating from Germany. From this package published in BreachForums, ZeroFox extracted 1,952 email addresses and hashed passwords.
Standing Intelligence Requirements
For the most up to date list of ZeroFox Threat Research’s Intelligence Requirements, please visit:
https://cloud.zerofox.com/intelligence/advisories/14956
Details
On May 5, 2022, a reputed threat actor "louisthomas82" from the BreachForums posted a data breach package targeting Tischmoebel (tischmoebel[.]de), an online wooden furniture store operating from Germany. The threat actor noted that the data breach package includes 65 Databases with millions of records. The database for Tischmoebel is a part of that 65 database. The data dump was also circulated in Raid Forums on December 10, 2021 by the threat actor "Sex". From this package published in BreachForums, ZeroFox extracted 1,952 email addresses and hashed passwords.
Recommendations
- If not already enabled, turn on the compromised credentials rule for all relevant entities and ensure relevant emails are entered for those entities, or reach out to [email protected] for assistance
- If one of your entities receives an alert, ZeroFox recommends immediate password changes for the affected account
- Enable 2-factor authentication for all of your organizational accounts to help mitigate phishing and credential stuffing attacks
Breach Disclosure: Tischmoebel
On May 5, 2022, a reputed threat actor "louisthomas82" from the BreachForums posted a data breach package targeting Tischmoebel, an online wooden furniture store operating from Germany. From this package published in BreachForums, ZeroFox extracted 1,952 email addresses and hashed passwords.
Standing Intelligence Requirements
For the most up to date list of ZeroFox Threat Research’s Intelligence Requirements, please visit:
https://cloud.zerofox.com/intelligence/advisories/14956
Details
On May 5, 2022, a reputed threat actor "louisthomas82" from the BreachForums posted a data breach package targeting Tischmoebel (tischmoebel[.]de), an online wooden furniture store operating from Germany. The threat actor noted that the data breach package includes 65 Databases with millions of records. The database for Tischmoebel is a part of that 65 database. The data dump was also circulated in Raid Forums on December 10, 2021 by the threat actor "Sex". From this package published in BreachForums, ZeroFox extracted 1,952 email addresses and hashed passwords.
Recommendations
- If not already enabled, turn on the compromised credentials rule for all relevant entities and ensure relevant emails are entered for those entities, or reach out to [email protected] for assistance
- If one of your entities receives an alert, ZeroFox recommends immediate password changes for the affected account
- Enable 2-factor authentication for all of your organizational accounts to help mitigate phishing and credential stuffing attacks
Breach Disclosure: Sylter WohnLust
On May 5, 2022, a reputed threat actor "louisthomas82" from the BreachForums posted a data breach package targeting Sylter WohnLust, an online store for home accessories & decoration items operating from Germany. From this package published in BreachForums, ZeroFox extracted 84,891 email addresses and hashed passwords.
Standing Intelligence Requirements
For the most up to date list of ZeroFox Threat Research’s Intelligence Requirements, please visit:
https://cloud.zerofox.com/intelligence/advisories/14956
Details
On May 5, 2022, a reputed threat actor "louisthomas82" from the BreachForums posted a data breach package targeting Sylter WohnLust (sylter-wohnlust[.]de), an online store for home accessories & decoration items operating from Germany. The threat actor noted that the data breach package includes 65 Databases with millions of records. The database for Sylter WohnLust is a part of that 65 databases. The data dump was also circulated in Raid Forums on December 10, 2021, by the threat actor "Sex". From this package published in BreachForums, ZeroFox extracted 84,891 email addresses and hashed passwords.


Recommendations
- If not already enabled, turn on the compromised credentials rule for all relevant entities and ensure relevant emails are entered for those entities, or reach out to [email protected] for assistance
- If one of your entities receives an alert, ZeroFox recommends immediate password changes for the affected account
- Enable 2-factor authentication for all of your organizational accounts to help mitigate phishing and credential stuffing attacks
Breach Disclosure: Dancesport
On May 5, 2022, a reputed threat actor "louisthomas82" from the BreachForums posted a data breach package targeting Dancesport, a Russia-based website which post information related to ballroom dancing sport. From the package posted on BreachForums, ZeroFox extracted 17,163 usernames, email addresses, and hashed passwords.
Standing Intelligence Requirements
For the most up to date list of ZeroFox Threat Research’s Intelligence Requirements, please visit:
https://cloud.zerofox.com/intelligence/advisories/14956
Details
On May 5, 2022, a reputed threat actor "louisthomas82" from the BreachForums posted a data breach package targeting Dancesport (dancesport[.]ru), a Russia-based website which post information related to ballroom dancing sport. The threat actor noted that the data breach package includes 65 Databases with millions of records. The database for Dancesport is a part of that 65 databases. The data dump was also circulated in Raid Forums on December 10, 2021 by the threat actor "Sex". From the package posted on BreachForums, ZeroFox extracted 17,163 usernames, email addresses, and hashed passwords.
Recommendations
- If not already enabled, turn on the compromised credentials rule for all relevant entities and ensure relevant emails are entered for those entities, or reach out to [email protected] for assistance
- If one of your entities receives an alert, ZeroFox recommends immediate password changes for the affected account
- Enable 2-factor authentication for all of your organizational accounts to help mitigate phishing and credential stuffing attacks
Breach Disclosure: Laguna Club Belarus
On May 5, 2022, a reputed threat actor "louisthomas82" from the BreachForums posted a data breach package targeting Laguna Club Belarus, a Belarus-based discussion forum for friendly communication, discussion, and mutual assistance upon operating Renault Laguna cars. From the package published in BreachForums, ZeroFox extracted 157,945 email addresses and hashed passwords.
Standing Intelligence Requirements
For the most up to date list of ZeroFox Threat Research’s Intelligence Requirements, please visit:
https://cloud.zerofox.com/intelligence/advisories/14956
Details
On May 5, 2022, a reputed threat actor "louisthomas82" from the BreachForums posted a data breach package targeting Laguna Club Belarus (laguna-club[.]by), a Belarus-based discussion forum for friendly communication, discussion, and mutual assistance upon operating Renault Laguna cars. The threat actor noted that the data breach package includes 65 databases with millions of records. The database for Laguna Club Belarus is a part of that 65 databases. The data dump was also circulated in Raid Forums on December 10, 2021, by the threat actor "Sex". From the package published in BreachForums, ZeroFox extracted 157,945 email addresses and hashed passwords.
Recommendations
- If not already enabled, turn on the compromised credentials rule for all relevant entities and ensure relevant emails are entered for those entities, or reach out to [email protected] for assistance
- If one of your entities receives an alert, ZeroFox recommends immediate password changes for the affected account
- Enable 2-factor authentication for all of your organizational accounts to help mitigate phishing and credential stuffing attacks
Breach Disclosure: Levella
On May 5, 2022, a reputed threat actor "louisthomas82" from the BreachForums posted a data breach package targeting Levella, a Germany-based automobile and lifestyle store. From the package published in BreachForums, ZeroFox extracted 7,096 email addresses and hashed passwords.
Standing Intelligence Requirements
For the most up to date list of ZeroFox Threat Research’s Intelligence Requirements, please visit:
https://cloud.zerofox.com/intelligence/advisories/14956
Details
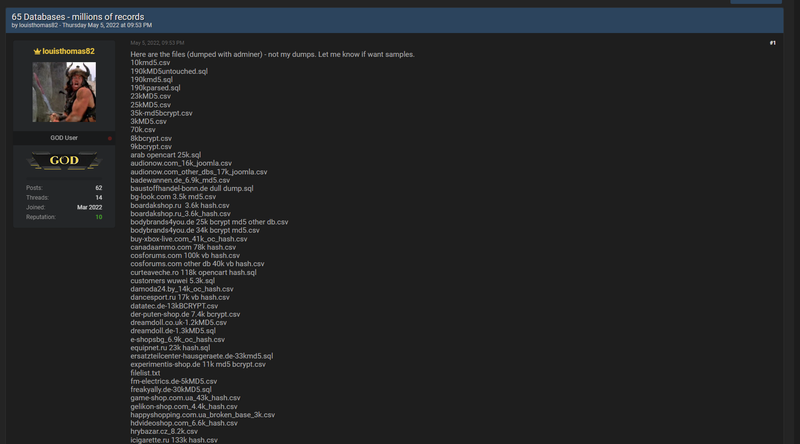
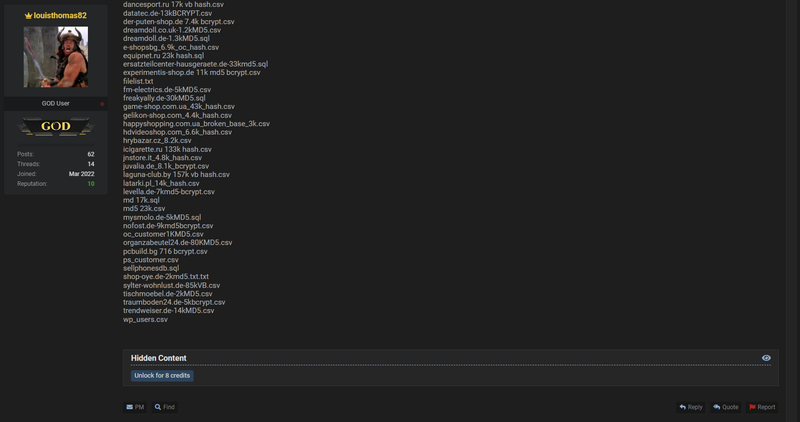
On May 5, 2022, a reputed threat actor "louisthomas82" from the BreachForums posted a data breach package targeting Levella (levella[.]de), a Germany-based automobile and lifestyle store. The threat actor noted that the data breach package includes 65 databases with millions of records. The database for Levella is a part of that 65 databases. The data dump was also circulated in Raid Forums on December 10, 2021 by the threat actor "Sex". From the package published in BreachForums, ZeroFox extracted 7,096 email addresses and hashed passwords.
Recommendations
- If not already enabled, turn on the compromised credentials rule for all relevant entities and ensure relevant emails are entered for those entities, or reach out to [email protected] for assistance
- If one of your entities receives an alert, ZeroFox recommends immediate password changes for the affected account
- Enable 2-factor authentication for all of your organizational accounts to help mitigate phishing and credential stuffing attacks
Breach Disclosure: Latarki
On May 5, 2022, a reputed threat actor "louisthomas82" from the BreachForums posted a data breach package targeting Latarki, an online store for LED lights operating from Wrocław, Poland. From the package published in BreachForums, ZeroFox extracted 14,814 email addresses and hashed passwords.
Standing Intelligence Requirements
For the most up to date list of ZeroFox Threat Research’s Intelligence Requirements, please visit:
https://cloud.zerofox.com/intelligence/advisories/14956
Details
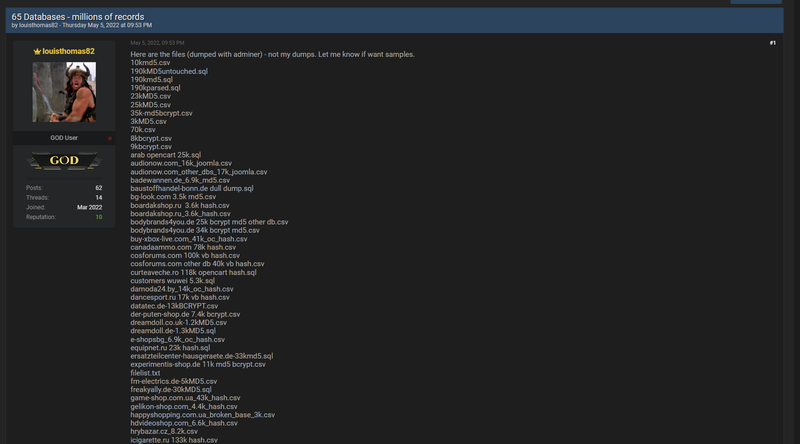
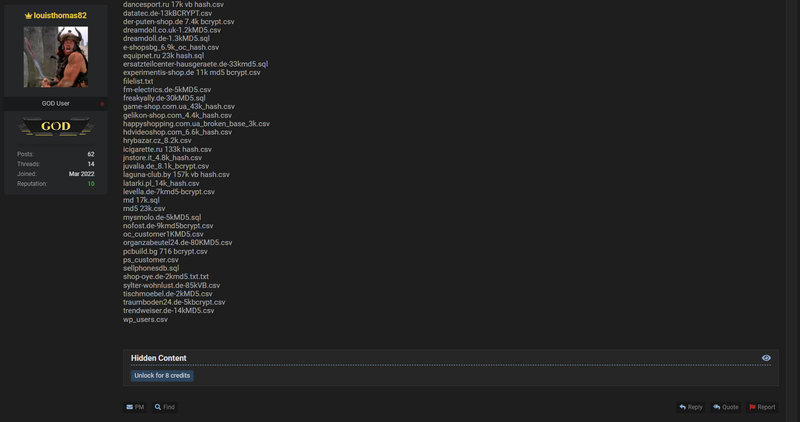
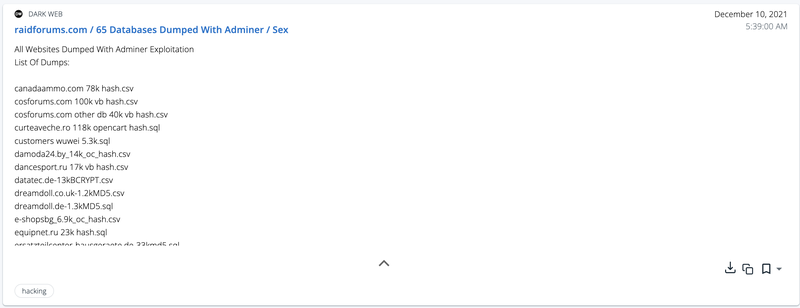
On May 5, 2022, a reputed threat actor "louisthomas82" from the BreachForums posted a data breach package targeting Latarki (latarki[.]pl), an online store for LED lights operating from Wrocław, Poland. The threat actor noted that the data breach package includes 65 databases with millions of records. The database for Latarki is a part of that 65 databases. The data dump was also circulated in Raid Forums on December 10, 2021, by the threat actor "Sex". From the package published in BreachForums, ZeroFox extracted 14,814 email addresses and hashed passwords.
Recommendations
- If not already enabled, turn on the compromised credentials rule for all relevant entities and ensure relevant emails are entered for those entities, or reach out to [email protected] for assistance
- If one of your entities receives an alert, ZeroFox recommends immediate password changes for the affected account
- Enable 2-factor authentication for all of your organizational accounts to help mitigate phishing and credential stuffing attacks
Breach Disclosure: HDVideoshop
On May 5, 2022, a reputed threat actor "louisthomas82" from the BreachForums posted a data breach package targeting HDVideoshop, an online and offline store for the camera, video equipment, and accessories operating from Germany. From the package published in BreachForums, ZeroFox extracted 6,605 email addresses and hashed passwords.
Standing Intelligence Requirements
For the most up to date list of ZeroFox Threat Research’s Intelligence Requirements, please visit:
https://cloud.zerofox.com/intelligence/advisories/14956
Details
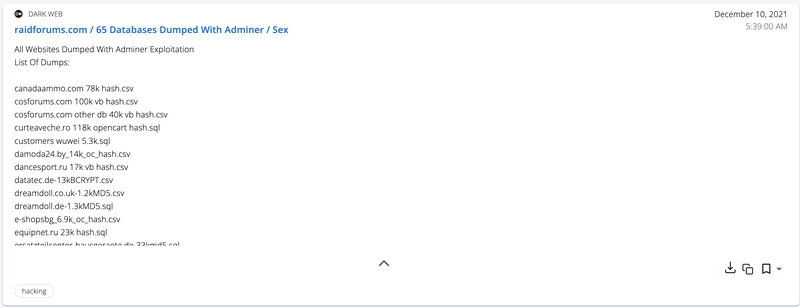
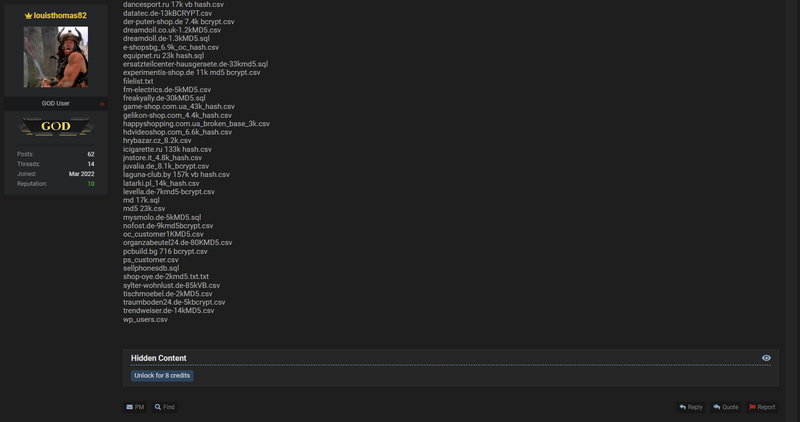
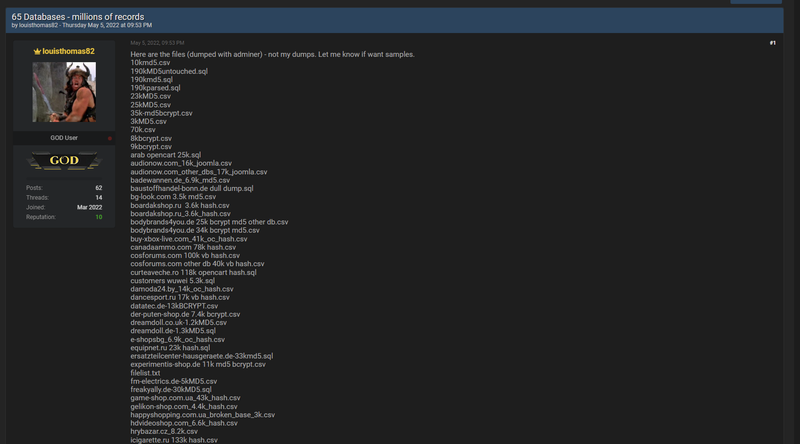
On May 5, 2022, a reputed threat actor "louisthomas82" from the BreachForums posted a data breach package targeting HDVideoshop (hdvideoshop.com), an online and offline store for the camera, video equipment, and accessories operating from Germany. The threat actor noted that the data breach package includes 65 databases with millions of records. The database for HDVideoshop is a part of that 65 databases. The data dump was also circulated in Raid Forums on December 10, 2021, by the threat actor "Sex". From the package published in BreachForums, ZeroFox extracted 6,605 email addresses and hashed passwords.
Recommendations
- If not already enabled, turn on the compromised credentials rule for all relevant entities and ensure relevant emails are entered for those entities, or reach out to [email protected] for assistance
- If one of your entities receives an alert, ZeroFox recommends immediate password changes for the affected account
- Enable 2-factor authentication for all of your organizational accounts to help mitigate phishing and credential stuffing attacks
Breach Disclosure: Wu-Wei Liefer GmbH
On May 5, 2022, a reputed threat actor "louisthomas82" from the BreachForums posted a data breach package targeting Wu-Wei Liefer GmbH, a Germany-based online store for products mostly related to healthcare. From this package published in BreachForums, ZeroFox extracted 5,331 email addresses and hashed passwords.
Standing Intelligence Requirements
For the most up to date list of ZeroFox Threat Research’s Intelligence Requirements, please visit:
https://cloud.zerofox.com/intelligence/advisories/14956
Details
On May 5, 2022, a reputed threat actor "louisthomas82" from the BreachForums posted a data breach package targeting Wu-Wei Liefer GmbH (wuwei-shop[.]de), a Germany-based online store for products mostly related to healthcare. The threat actor noted that the data breach package includes 65 databases with millions of records. The database for Wu-Wei Liefer GmbH is a part of that 65 databases. The data dump was also circulated in Raid Forums on December 10, 2021, by the threat actor "Sex". From this package published in BreachForums, ZeroFox extracted 5,331 email addresses and hashed passwords.
Recommendations
- If not already enabled, turn on the compromised credentials rule for all relevant entities and ensure relevant emails are entered for those entities, or reach out to [email protected] for assistance
- If one of your entities receives an alert, ZeroFox recommends immediate password changes for the affected account
- Enable 2-factor authentication for all of your organizational accounts to help mitigate phishing and credential stuffing attacks
Breach Disclosure: SellPhones
On May 5, 2022, a reputed threat actor "louisthomas82" from the BreachForums posted a data breach package targeting SellPhones, a U.K-based online and offline store for selling used phones. From this package published in BreachForums, ZeroFox extracted 15,203 email addresses and hashed passwords.
Standing Intelligence Requirements
For the most up to date list of ZeroFox Threat Research’s Intelligence Requirements, please visit:
https://cloud.zerofox.com/intelligence/advisories/14956
Details
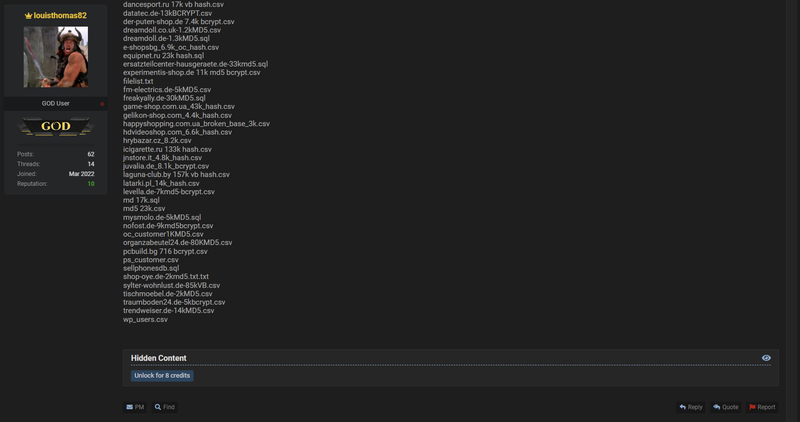
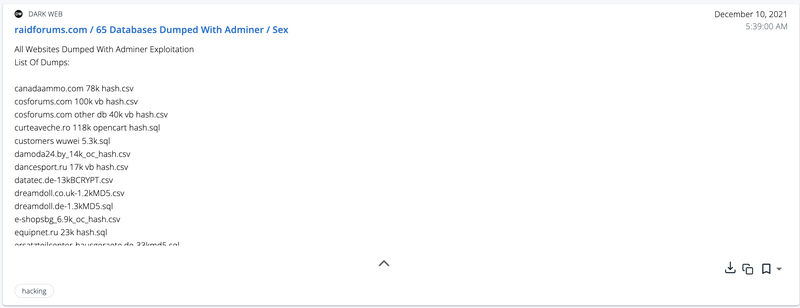
On May 5, 2022, a reputed threat actor "louisthomas82" from the BreachForums posted a data breach package targeting SellPhones (sellphones[.]co[.]uk), a U.K-based online and offline store for selling used phones. SellPhones.co.uk is a trading name of GSMNET Ltd. The threat actor noted that the data breach package includes 65 databases with millions of records. The database for SellPhones is a part of that 65 databases. The data dump was also circulated in Raid Forums on December 10, 2021, by the threat actor "Sex". From this package published in BreachForums, ZeroFox extracted 15,203 email addresses and hashed passwords.
Recommendations
- If not already enabled, turn on the compromised credentials rule for all relevant entities and ensure relevant emails are entered for those entities, or reach out to [email protected] for assistance
- If one of your entities receives an alert, ZeroFox recommends immediate password changes for the affected account
- Enable 2-factor authentication for all of your organizational accounts to help mitigate phishing and credential stuffing attacks
Breach Disclosure: Organzabeutel24
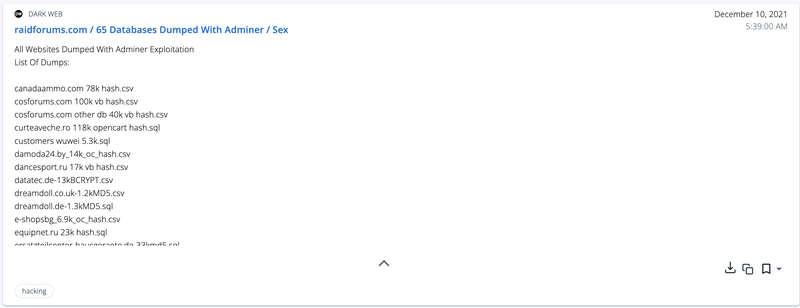
On May 5, 2022, a reputed threat actor "louisthomas82" from the BreachForums posted a data breach package targeting Organzabeutel24, a Germany-based online store for Organza material gift bags. From this package published in BreachForums, ZeroFox extracted 79,303 email addresses and hashed passwords.
Standing Intelligence Requirements
For the most up to date list of ZeroFox Threat Research’s Intelligence Requirements, please visit:
https://cloud.zerofox.com/intelligence/advisories/14956
Details
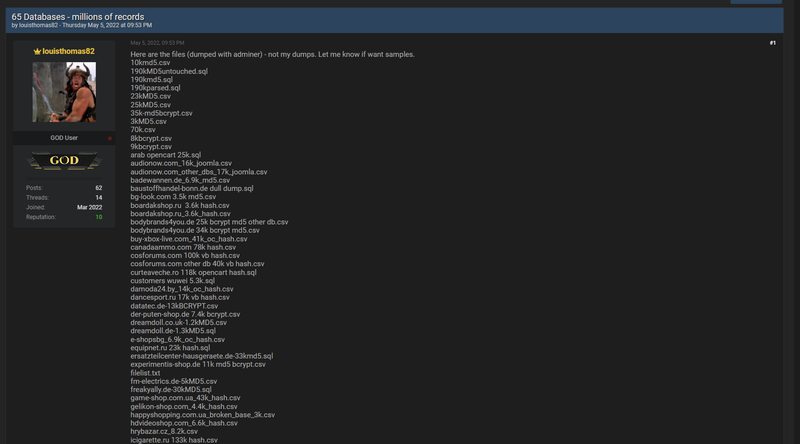
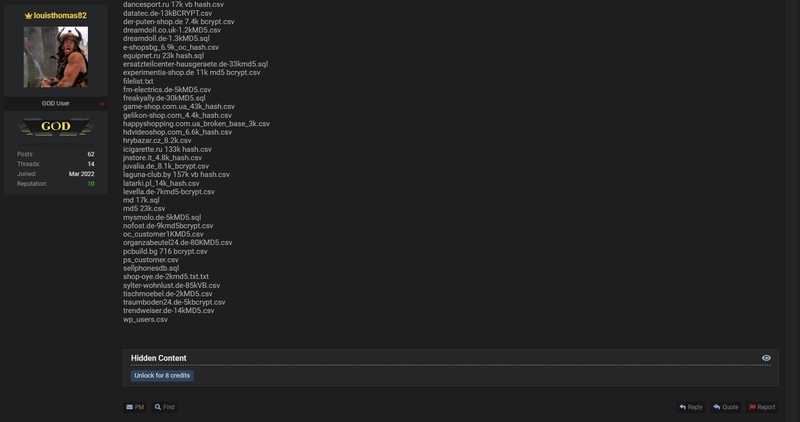
On May 5, 2022, a reputed threat actor "louisthomas82" from the BreachForums posted a data breach package targeting Organzabeutel24 (organzabeutel24[.]de), a Germany-based online store for Organza material gift bags. The threat actor noted that the data breach package includes 65 databases with millions of records. The database for Organzabeutel24 is a part of that 65 databases. The data dump was also circulated in Raid Forums on December 10, 2021, by the threat actor "Sex". From this package published in BreachForums, ZeroFox extracted 79,303 email addresses and hashed passwords.
Recommendations
- If not already enabled, turn on the compromised credentials rule for all relevant entities and ensure relevant emails are entered for those entities, or reach out to [email protected] for assistance
- If one of your entities receives an alert, ZeroFox recommends immediate password changes for the affected account
- Enable 2-factor authentication for all of your organizational accounts to help mitigate phishing and credential stuffing attacks
Breach Disclosure: Shop Open Your Eyes(OYE)
On May 5, 2022, a reputed threat actor "louisthomas82" from the BreachForums posted a data breach package targeting Shop Open Your Eyes(OYE), an online electronics gadgets store operating from London, United Kingdom. From this package published in BreachForums, ZeroFox extracted 2,087 email addresses.
Standing Intelligence Requirements
For the most up to date list of ZeroFox Threat Research’s Intelligence Requirements, please visit:
https://cloud.zerofox.com/intelligence/advisories/14956
Details
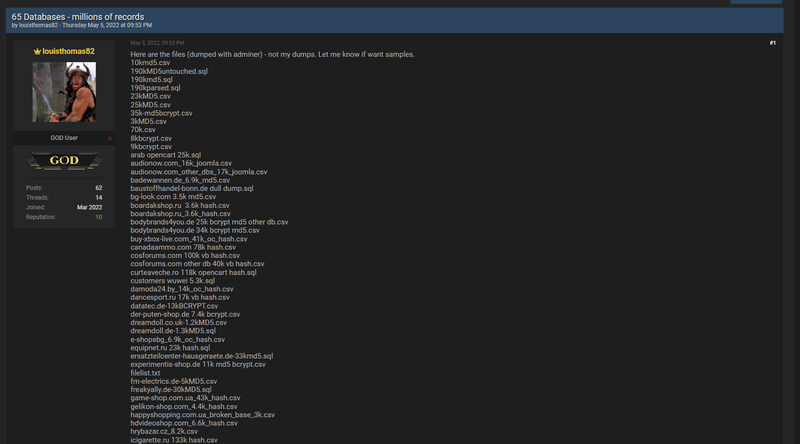
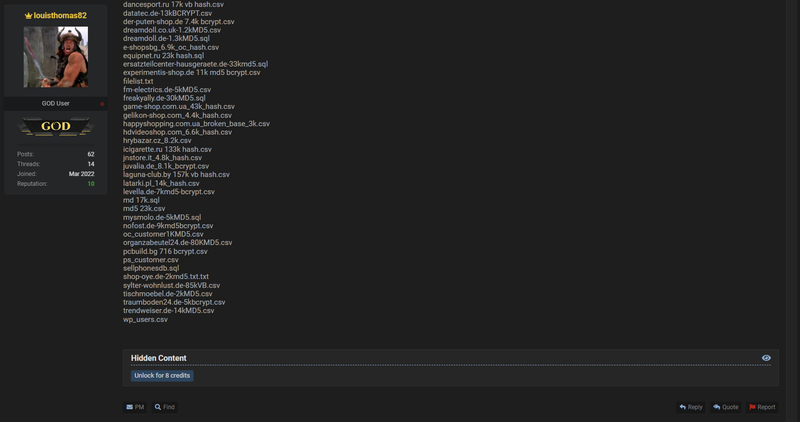
On May 5, 2022, a reputed threat actor "louisthomas82" from the BreachForums posted a data breach package targeting Shop Open Your Eyes(OYE) (shop-oye[.]de), an online electronics gadgets store operating from London, United Kingdom. The threat actor noted that the data breach package includes 65 databases with millions of records. The database for Shop Open Your Eyes(OYE) is a part of that 65 databases. The data dump was also circulated in Raid Forums on December 10, 2021 by the threat actor "Sex". From this package published in BreachForums, ZeroFox extracted 2,087 email addresses. Of this total, an assessed 1,979 records contained hashed passwords.
Recommendations
- If not already enabled, turn on the compromised credentials rule for all relevant entities and ensure relevant emails are entered for those entities, or reach out to [email protected] for assistance
- If one of your entities receives an alert, ZeroFox recommends immediate password changes for the affected account
- Enable 2-factor authentication for all of your organizational accounts to help mitigate phishing and credential stuffing attacks
Breach Disclosure: Nofost
On May 5, 2022, a reputed threat actor "louisthomas82" from the BreachForums posted a data breach package targeting Nofost, an online store for Laptop, Personal Computer, Tablets, and accessories operating from Germany. From this package published in BreachForums, ZeroFox extracted 8,981 email addresses and hashed passwords.
Standing Intelligence Requirements
For the most up to date list of ZeroFox Threat Research’s Intelligence Requirements, please visit:
https://cloud.zerofox.com/intelligence/advisories/14956
Details
On May 5, 2022, a reputed threat actor "louisthomas82" from the BreachForums posted a data breach package targeting Nofost (nofost[.]de), an online store for Laptop, Personal Computer, Tablets, and accessories operating from Germany. The threat actor noted that the data breach package includes 65 databases with millions of records. The database for Nofost is a part of that 65 databases. The data dump was also circulated in Raid Forums on December 10, 2021, by the threat actor "Sex". From this package published in BreachForums, ZeroFox extracted 8,981 email addresses and hashed passwords.
Recommendations
- If not already enabled, turn on the compromised credentials rule for all relevant entities and ensure relevant emails are entered for those entities, or reach out to [email protected] for assistance
- If one of your entities receives an alert, ZeroFox recommends immediate password changes for the affected account
- Enable 2-factor authentication for all of your organizational accounts to help mitigate phishing and credential stuffing attacks
Breaking News: 2022-09-16 - 2022-09-22
Uber hacked, internal systems breached and vulnerability reports stolen
Uber suffered a cyberattack with a hacker gaining access to vulnerability reports and sharing screenshots of the company's internal systems, email dashboard, and Slack server. The screenshots shared by the hacker appears to indicate full access to many critical Uber IT systems, including the company's security software and Windows domain.
See the full report here: https://www.bleepingcomputer.com/news/security/uber-hacked-internal-systems-breached-and-vulnerability-reports-stolen/
Hackers trojanize PuTTY SSH client to backdoor media company
North Korean hackers (UNC4034 / "Temp.Hermit" / "Labyrinth Chollima") are reportedly using trojanized versions of the PuTTY SSH client to deploy backdoors on targets' devices as part of a fake Amazon job assessment.
See the full report here: https://www.bleepingcomputer.com/news/security/hackers-trojanize-putty-ssh-client-to-backdoor-media-company/
Hive ransomware claims cyberattack on Bell Canada subsidiary
The Hive ransomware gang claimed responsibility for an attack that hit the systems of Bell Canada subsidiary Bell Technical Solutions (BTS). While the Canadian telecommunications company didn't reveal when its network was breached, Hive claims that it encrypted BTS' systems on August 20, 2022. BTS is currently investigating the incident with the help of law enforcement officials. The compromised servers contained operational company and employee information and no customer financial data was apparently accessed during the incident.
See the full report here: https://www.bleepingcomputer.com/news/security/hive-ransomware-claims-cyberattack-on-bell-canada-subsidiary/
Akamai stopped new record-breaking DDoS attack in Europe
The cybersecurity and cloud services company Akamai stopped an unprecedented distributed denial-of-service (DDoS) attack on September 12 that broke the previous record that Akamai recorded in July 2022. The attack involved “garbage” traffic sent to the target network peaking at 704.8 Mpps, roughly 7% higher than the July attack. Both the threat actor and the target (an unnamed customer in Eastern Europe) are reportedly the same as those of the July attack.
See the full report here: https://www.bleepingcomputer.com/news/security/akamai-stopped-new-record-breaking-ddos-attack-in-europe/
Microsoft Edge’s News Feed ads abused for tech support scams
An ongoing malvertising campaign is injecting ads in the Microsoft Edge News Feed to redirect potential victims to websites pushing tech support scams.
See the full report here: https://www.bleepingcomputer.com/news/security/microsoft-edge-s-news-feed-ads-abused-for-tech-support-scams/
New malware bundle self-spreads through YouTube gaming videos
A new malware bundle uses victims' YouTube channels to upload malicious video tutorials advertising fake cheats and cracks for popular video games to spread the malicious package further. The self-spreading malware bundle has been promoted in YouTube videos targeting fans playing FIFA, Final Fantasy, Forza Horizon, Lego Star Wars, and Spider-Man.
See the full report here: https://www.bleepingcomputer.com/news/security/new-malware-bundle-self-spreads-through-youtube-gaming-videos/
Russian hackers use new info stealer malware against Ukrainian orgs
A Russian state-backed threat group Gamaredon (also known as Primitive Bear, Shuckworm, IronTiden, and Callisto) is targeting Ukrainian entities with new info-stealing malware in an ongoing espionage campaign. Organizations can use disclosed indicators of compromise (IoCs) to defend their organizations from espionage campaigns Gamaredon may deploy.
See the full report here: https://www.bleepingcomputer.com/news/security/russian-hackers-use-new-info-stealer-malware-against-ukrainian-orgs/
Webworm hackers modify old malware in new attacks to evade attribution
The Chinese “Webworm” hacking group is experimenting with customizing old malware in new attacks, likely to evade attribution and reduce operations costs. The threat actors are currently testing various modified Remote Access Trojans (RATs) against IT service providers in Asia, likely to determine their effectiveness. Using older RATs that are in wide circulation and deployed by various random hackers helps Webworm disguise their operations and blend with the activities of others.
See the full report here: https://www.bleepingcomputer.com/news/security/webworm-hackers-modify-old-malware-in-new-attacks-to-evade-attribution/
LastPass says hackers had internal access for four days
Password management software provider LastPass said that the attacker behind the August security breach had internal access to the company's systems for four days until they were detected and evicted. Although the threat actor was able to access the Development environment, the system design and controls prevented the threat actor from accessing any customer data or encrypted password vaults, the company stated.
See the full report here: https://www.bleepingcomputer.com/news/security/lastpass-says-hackers-had-internal-access-for-four-days/
Google, Microsoft can get your passwords via web browser's spellcheck
Extended spellcheck features (like Enhanced Spellcheck or Microsoft Editor) in Google Chrome and Microsoft Edge web browsers transmit form data, including personally identifiable information (PII) and in some cases, passwords, to Google and Microsoft respectively.
See the full report here: https://www.bleepingcomputer.com/news/security/google-microsoft-can-get-your-passwords-via-web-browsers-spellcheck/
GTA 6 source code and videos leaked after Rockstar Games hack
Grand Theft Auto 6 gameplay videos and source code have been leaked after a hacker allegedly breached Rockstar Game's Slack server and Confluence wiki. The threat actor reportedly said that they are accepting offers over $10,000 for the GTA V source code and assets but are not selling the GTA 6 source code at this time. The threat actor claims to be the same hacker behind the recent Uber cyberattack.
See the full report here: https://www.bleepingcomputer.com/news/security/gta-6-source-code-and-videos-leaked-after-rockstar-games-hack/
TeamTNT hijacking servers to run Bitcoin encryption solvers
Security researchers have observed evidence that indicates that the TeamTNT group is back in action, after the group suspended operations in November 2021. Among other attacks, the group seems to be using the computational power of hijacked servers to run Bitcoin encryption solvers.
See the full report here: https://www.bleepingcomputer.com/news/security/teamtnt-hijacking-servers-to-run-bitcoin-encryption-solvers/
New York ambulance service discloses data breach after ransomware attack
Empress EMS (Emergency Medical Services), a New York-based emergency response and ambulance service provider, has disclosed a data breach that exposed customer information. According to the notification, the company suffered a ransomware attack on July 14, 2022.
See the full report here: https://www.bleepingcomputer.com/news/security/new-york-ambulance-service-discloses-data-breach-after-ransomware-attack/
CISA orders agencies to patch vulnerability used in Stuxnet attacks
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has added half a dozen vulnerabilities to its catalog of Known Exploited Vulnerabilities and is ordering federal agencies to follow vendor’s instructions to fix them.
See the full report here: https://www.bleepingcomputer.com/news/security/cisa-orders-agencies-to-patch-vulnerability-used-in-stuxnet-attacks/
Hacker sells stolen Starbucks data of 219,000 Singapore customers
The Singapore division of Starbucks has admitted that it suffered a data breach incident impacting over 219,000 of its customers. The first hint came on September 10, when a threat actor offered to sell a database containing sensitive details of 219,675 Starbucks customers on a popular hacking forum.
See the full report here: https://www.bleepingcomputer.com/news/security/hacker-sells-stolen-starbucks-data-of-219-000-singapore-customers/
Bitdefender releases free decryptor for LockerGoga ransomware
Bitdefender says the decryptor was developed in cooperation with law enforcement agencies, including Europol, the NoMoreRansom Project, the Zürich Public Prosecutor's Office, and the Zürich Cantonal Police.
See the full report here: https://www.bleepingcomputer.com/news/security/bitdefender-releases-free-decryptor-for-lockergoga-ransomware/
Emotet botnet now pushes Quantum and BlackCat ransomware
Quantum and BlackCat ransomware gangs are using the Emotet malware to deploy their payloads. The botnet is being used to install a Cobalt Strike beacon on infected systems as a second-stage payload, allowing attackers to move laterally and deploy ransomware payloads across the victim's network. From November 2021 to June 2022, Emotet was an exclusive Conti ransomware tool.
See the full report here: https://www.bleepingcomputer.com/news/security/emotet-botnet-now-pushes-quantum-and-blackcat-ransomware/
Piracy Advertising Researchers Fall Victim to Ransomware Attacks
More than 10% of all ads on pirate streaming sites are linked to malware. The problem is so bad that the researchers fell prey to multiple ransomware attacks.
See the full report here: https://torrentfreak.com/piracy-advertising-researchers-fall-victim-to-ransomware-attacks/
VMware, Microsoft warn of widespread Chromeloader malware attacks
VMware and Microsoft are warning of an ongoing, widespread Chromeloader malware campaign that has evolved into a more dangerous threat, seen dropping malicious browser extensions, node-WebKit malware, and even ransomware in some cases
See the full report here: https://www.bleepingcomputer.com/news/security/vmware-microsoft-warn-of-widespread-chromeloader-malware-attacks/
Lubbock Heart & Surgical Hospital Reports Data Breach
Lubbock Heart & Surgical Hospital filed official notice of a data breach with the U.S. Department of Health and Human Services Office for Civil Rights following a data security incident that disrupted the hospital’s computer network.
See the full report here: https://www.jdsupra.com/legalnews/lubbock-heart-surgical-hospital-reports-6782813/
Hacking group focused on Central America dumps 10 gigabytes of military emails, files
A hacking group that has primarily focused on Central American targets released roughly 10 gigabytes of emails and other materials from military and police agencies in Chile, Mexico, El Salvador, Colombia and Peru.
See the full report here: https://www.cyberscoop.com/central-american-hacking-group-releases-emails/
Ransomware Attack on Medical Records Company
Almost one million protected health information (PHI) records from as many as 28 healthcare providers in New York and surrounding areas appear to have been stolen from a medical records company that services these providers.
See the full report here: https://www.darkdaily.com/2022/09/19/nearly-one-million-patient-records-of-hospitals-health-clinics-medical-laboratories-and-other-providers-stolen-in-ransomware-attack-on-medical-records-company/
M.C. Dean, Inc. Reports Data Breach After Unauthorized Party Had Access to the Company’s Computer System
M.C. Dean confirmed that the company experienced a data breach after an unauthorized party gained access to sensitive consumer data contained on M.C. Dean’s network. The company’s data breach letter does not mention the types of information leaked.
See the full report here: https://www.jdsupra.com/legalnews/m-c-dean-inc-reports-data-breach-after-1236681/
Ameriprise Financial, Inc. Confirms the Company’s Fourth Data Breach of 2022
Ameriprise Financial, Inc. filed official notice of a data breach with the Massachusetts Office of Consumer Affairs and Business Regulation after the company confirmed that sensitive information in its possession was subject to unauthorized access. The breach resulted in the names, Social Security numbers and financial account numbers belonging to some clients being compromised
See the full report here: https://www.jdsupra.com/legalnews/ameriprise-financial-inc-confirms-the-3334468/
Bosnia and Herzegovina investigating alleged ransomware attack on parliament
Prosecutors in Bosnia and Herzegovina are investigating a wide-ranging cyberattack that has crippled the operations of the country’s parliament. Several lawmakers were reportedly told to not even turn on their computers, barring them from access to their email accounts and official documents.
See the full report here: https://therecord.media/bosnia-and-herzegovina-investigating-alleged-ransomware-attack-on-parliament/
Uber links breach to Lapsus$ group, blames contractor for hack
Uber stated it believes the hacker behind last week's breach is affiliated with the Lapsus$ extortion group. The company also disclosed that the attacker used the stolen credentials of an Uber EXT contractor in an MFA fatigue attack where the contractor was flooded with two-factor authentication (2FA) login requests until one of them was accepted. Uber reportedly found no evidence that the threat actor could access production systems that store sensitive user information, including personal and financial data.
See the full report here: https://www.bleepingcomputer.com/news/security/uber-links-breach-to-lapsus-group-blames-contractor-for-hack/
Revolut hack exposes data of 50,000 users, fuels new phishing wave
Financial technology company Revolut has suffered a cyberattack that gave an unauthorized third party access to personal information of over fifty thousand clients. The likely exposed information includes email addresses, names, postal addresses, phone numbers, and limited payment card data, and more. There’s already an ongoing SMS phishing campaign attempting to trick Revolut account holders with messages that their existing card has been frozen to prevent fraud.
See the full report here: https://www.bleepingcomputer.com/news/security/revolut-hack-exposes-data-of-50-000-users-fuels-new-phishing-wave/
Microsoft 365 phishing attacks impersonate U.S. govt agencies
A phishing campaign targeting U.S. government contractors uses high-quality lures and documents and takes victims to phishing pages that are clones of legitimate federal agency portals (including the Department of Transportation and the Department of Commerce). People should examine all details like the sending address and the landing URL to guard themselves from falling victims to such attacks.
See the full report here: https://www.bleepingcomputer.com/news/security/microsoft-365-phishing-attacks-impersonate-us-govt-agencies/
American Airlines discloses data breach after employee email compromise
American Airlines has notified customers of a recent data breach after attackers compromised employee email accounts and gained access to sensitive personal information. Personal information exposed in the attack may have included employees' and customers' names, dates of birth, mailing addresses, phone numbers, email addresses, driver's license numbers, passport numbers, and certain medical information. The company is yet to disclose the number of affected customers and how many email accounts were breached in the incident.
See the full report here: https://www.bleepingcomputer.com/news/security/american-airlines-discloses-data-breach-after-employee-email-compromise/
Hackers take over CoinDCX Twitter account, promote fake XRP ads
The official Twitter account of India-based crypto exchange CoinDCX has been hacked and used by the exploiters to post fake Ripple (XRP) promos partnered with phishing links in an attempt to scam the exchange’s followers.
See the full report here: https://cointelegraph.com/news/hackers-take-over-coindcx-twitter-account-promote-fake-xrp-ads
MMO For Kids Shuts Down Temporarily After Hacker Fills It With Swearwords
Kid-friendly PC MMO Wizard101 found itself thrust into the spotlight after a series of bizarre and expletive-filled in-game messages began popping up for players. And fans believe an angry developer is to blame.
See the full report here: https://kotaku.com/wizard101-mmo-kids-hacker-swears-nasty-messages-1849559612
Arbitrum Saved From Major ETH Loss by White Hat Hacker
An exploitable bug was found in the bridge between Ethereum and Arbitrum Nitro.This vulnerability would have allowed an attacker to steal all incoming ether deposits from users attempting to bridge their assets between Ethereum layer-1 and layer-2 protocols to Arbitrum.
See the full report here: https://blockworks.co/arbitrum-saved-from-major-eth-loss-by-white-hat-hacker/
Texas Nonprofit Election Fraud Group Sued In Federal Court For Hacking And Defamation
US-based nonprofit is being sued in federal court for allegedly hacking and committing defamation against Michigan election software company, Konnech Inc., claiming that the company has ties to the Chinese Communist Party and was responsible for voter fraud in the 2020 election cycle.
See the full report here: https://www.reformaustin.org/elections/texas-nonprofit-election-fraud-group-sued-in-federal-court-for-hacking-and-defamation/
Mobile phone hackers wield “Violence-as-a-service” for money, revenge
A new phenomenon known as violence-as-a-service has become the acceptable way to settle scores in the SIM swapper community. Doxing or defacing websites just doesn’t send enough of a message. So they are throwing Molotov cocktails or slashing tires in the real world instead.
See the full report here: https://therecord.media/mobile-phone-hackers-wield-violence-as-a-service-for-money-revenge/
Philadelphia 76ers coach Doc Rivers reportedly hacked on Twitter
The Twitter account of Philadelphia 76ers coach Doc Rivers was hacked and the Sixers organization had to work overnight to regain access.
See the full report here: https://www.cbssports.com/nba/news/sixers-coach-doc-rivers-reportedly-hacked-on-twitter-adult-content-had-a-lot-of-likes/
New Malware Spreading Disguised as Legitimate Zoom Application
Researchers have spotted numerous fake Zoom sites being created, with the purpose of infecting people with malware disguised as Zoom’s legitimate application, using this site as a vehicle for spreading malware.
See the full report here: https://cybersecuritynews.com/zoom-users-beware/
IHG hack: Vindictive couple deleted hotel chain data for fun
Hackers said they carried out a destructive cyber-attack against Holiday Inn owner Intercontinental Hotels Group "for fun". Describing themselves as a couple from Vietnam, they say they first tried a ransomware attack, then deleted large amounts of data when they were foiled.
See the full report here: https://www.bbc.com/news/technology-62937678
2K Games says hacked help desk targeted players with malware
American video game publisher 2K has confirmed that its help desk platform was hacked and used to target customers with fake support tickets pushing malware via embedded links. The company warns people to not open any emails or click on any links that they receive from the 2K Games support account. The company said it would issue a notice to let players know when it will be safe to start interacting with its support staff again.
See the full report here: https://www.bleepingcomputer.com/news/security/2k-games-says-hacked-help-desk-targeted-players-with-malware/
MFA Fatigue: Hackers’ new favorite tactic in high-profile breaches
A component of social-engineering attacks that is becoming more popular among hackers with the rise of multi-factor authentication is MFA Fatigue. In these attacks, a threat actor runs a script that attempts to log in with stolen credentials over and over, causing what feels like an endless stream of MFA push requests to be sent to the account's owner's mobile device. The goal is to break down the target's cybersecurity posture and inflict a sense of "fatigue" regarding these MFA prompts.
See the full report here: https://www.bleepingcomputer.com/news/security/mfa-fatigue-hackers-new-favorite-tactic-in-high-profile-breaches/
Imperva mitigated long-lasting, 25.3 billion request DDoS attack
Internet security company Imperva has announced its DDoS (distributed denial of service) mitigation solution has broken a new record, defending against a single attack that sent over 25.3 billion to the target (a Chinese telecommunications service provider). The DDoS attack was launched by a massive botnet spread across 180 countries, with most IP addresses located in the U.S., Brazil, and Indonesia.
See the full report here: https://www.bleepingcomputer.com/news/security/imperva-mitigated-long-lasting-253-billion-request-ddos-attack/
Hive ransomware claims attack on New York Racing Association
The Hive ransomware operation claimed responsibility for an attack on the New York Racing Association (NYRA), which impacted IT operations and website availability and compromised member data. The threat actors may have exfiltrated Social Security numbers (SSNs), driver's license identification numbers, health records, and health insurance information.
See the full report here: https://www.bleepingcomputer.com/news/security/hive-ransomware-claims-attack-on-new-york-racing-association/
Hackers steal $162 million from Wintermute crypto market maker
Digital assets trading firm Wintermute lost $162.2 million in DeFi operations after a hack. Wintermute provides liquidity to over 50 cryptocurrency exchanges and trading platforms, including Binance, Coinbase, Kraken, and Bitfinex. The company CEO has clarified that Wintermute’s CeFi (centralized finance) and OTC (over-the-counter) operations have not been impacted by the security breach.
See the full report here: https://www.bleepingcomputer.com/news/security/hackers-steal-162-million-from-wintermute-crypto-market-maker/
Hackers publish sensitive data on political assassination plots in Albania, Kosovo
Iranian cybercriminals published sensitive information from the authorities, including documents on alleged plots to kill Albanian and Kosovo politicians, while the prosecutor in Tirana has banned media from publishing any of the data.
See the full report here: https://www.euractiv.com/section/politics/short_news/hackers-publish-sensitive-data-on-political-assassination-plots-in-albania-kosovo/
Atlassian Confluence Vulnerability Abused For Cryptocurrency Mining, Other Malware
CVE-2022-26134, an unauthenticated remote code execution (RCE) vulnerability with a critical rating of 9.8, is being abused for malicious cryptocurrency mining. Confluence has released a security advisory detailing the fixes necessary for all affected products.
See the full report here: https://confluence.atlassian.com/doc/confluence-security-advisory-2022-06-02-1130377146.html
Malwarebytes mistakenly blocks Google, YouTube for malware
According to a large number of reports from people, their browsers were prevented from accessing Google sites after Malwarebytes flagged and blocked them as malicious. The issue has been fixed.
See the full report here: https://www.bleepingcomputer.com/news/technology/malwarebytes-mistakenly-blocks-google-youtube-for-malware/
Pay-per-install services provide access to thousands of compromised computers
Pay-per-install services are used in the cybercrime underground to monetize the installation of malware on computers. Cybercriminals who have the capability to build a network of infected computers then sell access to those computers.
See the full report here: https://www.techrepublic.com/article/pay-per-install-services/
Sophisticated Hermit Mobile Spyware Heralds Wave of Government Surveillance
A recently discovered, powerful mobile reconnaissance malware dubbed Hermit is being touted by an Italian developer as a "lawful intercept" tool.
See the full report here: https://www.darkreading.com/application-security/sophisticated-hermit-mobile-spyware-government-surveillance
Iranian State Actors Conduct Cyber Operations Against the Government of Albania
The Federal Bureau of Investigation (FBI) and the Cybersecurity and Infrastructure Security Agency (CISA) have released a joint cybersecurity advisory to provide information on recent cyber operations against the Government of Albania in July and September.
See the full report here: https://www.cisa.gov/uscert/ncas/alerts/aa22-264a
A former threat actor has returned with new attacks targeting encryption keys, the cloud, and containers
Three assaults that mirrored those committed by TeamTNT, a threat actor that targets online resources like Kubernetes clusters, Redis servers, and Docker APIs in the cloud, were found by researchers.
See the full report here: https://www.thetechoutlook.com/news/technology/security/a-former-threat-actor-has-returned-with-new-attacks-targeting-encryption-keys-the-cloud-and-containers/
Microsoft Learns a Lesson From Cybercrime Sting
Having failed to completely demolish a massive cybercriminal network that was poised to disrupt US election technology two years ago, Microsoft Corp. is looking to apply lessons from the experience to help fend off future attacks.
See the full report here: https://www.bloomberg.com/news/newsletters/2022-09-21/microsoft-reveals-how-trickbot-cybercrime-sting-fell-short
‘Anonymous’ hackers knock Iran state websites offline amid nationwide protests
Anonymous has said it was behind cyber attacks that knocked Iranian government websites offline, claiming that it was part of the hacking collective’s support for protests against the death of Mahsa Amini.
See the full report here: https://www.independent.co.uk/tech/anonymous-iran-hack-protests-cyber-attack-amini-b2172302.html
The Gang Behind LA's School District Hack Is Demanding Ransom Two Weeks Later
The ransomware gang that hacked the Los Angeles Unified School District—paralyzing the computer systems of the second-largest school district in the country—is demanding a ransom two weeks after the attack.
See the full report here: https://gizmodo.com/vice-society-lausd-hack-demands-ransom-1849565148
Bayern Munich patches vulnerability after fan-hacker blows whistle
Martins, 24, an expert in information security, alerted Bayern when he spotted weaknesses in their official website portal. Personal data could have been exposed by the problem.
See the full report here: https://www.the-sun.com/sport/6273932/bayern-munich-hacker-gets-thomas-muller-website/
Hampton Public Library website hacked, redirects to adult retail store
The Hampton Public Library, USA, is making some big changes after someone hacked the website, redirecting people to an adult retail store website.
See the full report here: https://www.13newsnow.com/article/news/local/mycity/hampton/hampton-public-library-creates-new-website-hacker-took-control-sending-people-adult-retail-store/291-620b252f-2b7b-4f93-b70d-7d6cd7f86e5b
LockBit ransomware builder leaked online by “angry developer”
The LockBit ransomware operation has suffered a breach, with an allegedly disgruntled developer leaking the builder for the gang's newest encryptor (LockBit 3.0). The leaked builder allows anyone to quickly build the executables required to launch their own operation, including an encryptor, decryptor, and specialized tools to launch the decryptor in certain ways.
See the full report here: https://www.bleepingcomputer.com/news/security/lockbit-ransomware-builder-leaked-online-by-angry-developer-/
Unpatched 15-year old Python bug allows code execution in 350k projects
A vulnerability in Python (CVE-2007-4559, disclosed in 2007) likely affects more than 350,000 open-source repositories and can lead to code execution. The security issue never received a patch, with the only mitigation provided being a documentation update warning developers about the risk. There are no reports about the bug being used in attacks.
See the full report here: https://www.bleepingcomputer.com/news/security/unpatched-15-year-old-python-bug-allows-code-execution-in-350k-projects/
Okta: Credential stuffing accounts for 34% of all login attempts
The identity and access management firm Okta reports that it has recorded over 10 billion credential stuffing events on its platform in the first 90 days of 2022. The worst cases are South East Asia and the United States, where credential stuffing traffic consistently dwarfed normal login attempts throughout Q1 2022.
See the full report here: https://www.bleepingcomputer.com/news/security/okta-credential-stuffing-accounts-for-34-percent-of-all-login-attempts/
Domain shadowing becoming more popular among cybercriminals
Threat analysts have discovered that domain shadowing might be more prevalent than previously thought, uncovering 12,197 cases between April and June 2022. Domain shadowing is a subcategory of DNS hijacking, where threat actors compromise the DNS of a legitimate domain to host their own subdomains for use in malicious activity but do not modify the legitimate DNS entries that already exist.
See the full report here: https://www.bleepingcomputer.com/news/security/domain-shadowing-becoming-more-popular-among-cybercriminals/
Twitter failed to log you out of all devices after password resets
Twitter logged out some users after addressing a bug where some Twitter accounts remained logged on some mobile devices after voluntary password resets. There are some potential privacy risks for Twitter users who were affected by this bug, including having their accounts accessed by others who got their hands on devices that remained logged in without the user's knowledge. Twitter reached out to those who might have been impacted and logged them out of their accounts on all active sessions across all devices.
See the full report here: https://www.bleepingcomputer.com/news/security/twitter-failed-to-log-you-out-of-all-devices-after-password-resets/
Over 39,000 Unauthenticated Redis Instances Found Exposed on the Internet
An attacker targeted thousands of unauthenticated Redis servers exposed on the internet in an attempt to install a cryptocurrency miner. This was via a lesser-known technique designed to trick the servers into writing data to arbitrary files – a case of unauthorized access first documented in 2018. Users are advised to enable client authentication, configure Redis to run only on internal-facing network interfaces, prevent the abuse of CONFIG command by renaming it to something unguessable, and configure firewalls to accept Redis connections only from trusted hosts.
See the full report here: https://thehackernews.com/2022/09/over-39000-unauthenticated-redis.html
U.S. Adds 2 More Chinese Telecom Firms to National Security Threat List
The U.S. Federal Communications Commission (FCC) has added Pacific Network Corp, along with its subsidiary ComNet (USA) LLC, and China Unicom (Americas) Operations Limited to the list of communications equipment and services deemed a threat to national security. The agency said the companies are subject to the Chinese government's exploitation, influence, and control, and could be forced to comply with requests for intercepting and misrouting communications.
See the full report here: https://thehackernews.com/2022/09/us-adds-2-more-chinese-telecom-firms-to.html
LinkedIn Smart Links abused in evasive email phishing attacks
Phishing actors are abusing LinkedIn’s Smart Link feature to bypass email security products and successfully redirect targeted users to phishing pages that steal payment information. Smart Link is a feature reserved for LinkedIn Sales Navigator and Enterprise users, allowing them to send a pack of up to 15 documents using a single trackable link.
See the full report here: https://www.bleepingcomputer.com/news/security/linkedin-smart-links-abused-in-evasive-email-phishing-attacks/
Hackers Likely Accessed Emails of Serbia’s Cadastre Staff, BIRN Reveals
Serbia’s cadaster system, RGZ, was infected by at least three malicious programs. At least one of them entered the server via the RGZ mail server, from where it tried to spread.
See the full report here: https://balkaninsight.com/2022/09/21/hackers-likely-accessed-emails-of-serbias-cadastre-staff-birn-reveals/
Customers’ personal data stolen as Optus suffers massive cyber-attack
Australian telecommunications company Optus has suffered a massive cyber-attack, with the personal information of customers stolen, including names, dates of birth, addresses, and contact details.
See the full report here: https://www.theguardian.com/business/2022/sep/22/customers-personal-data-stolen-as-optus-suffers-massive-cyber-attack
Tags: all industries, global